
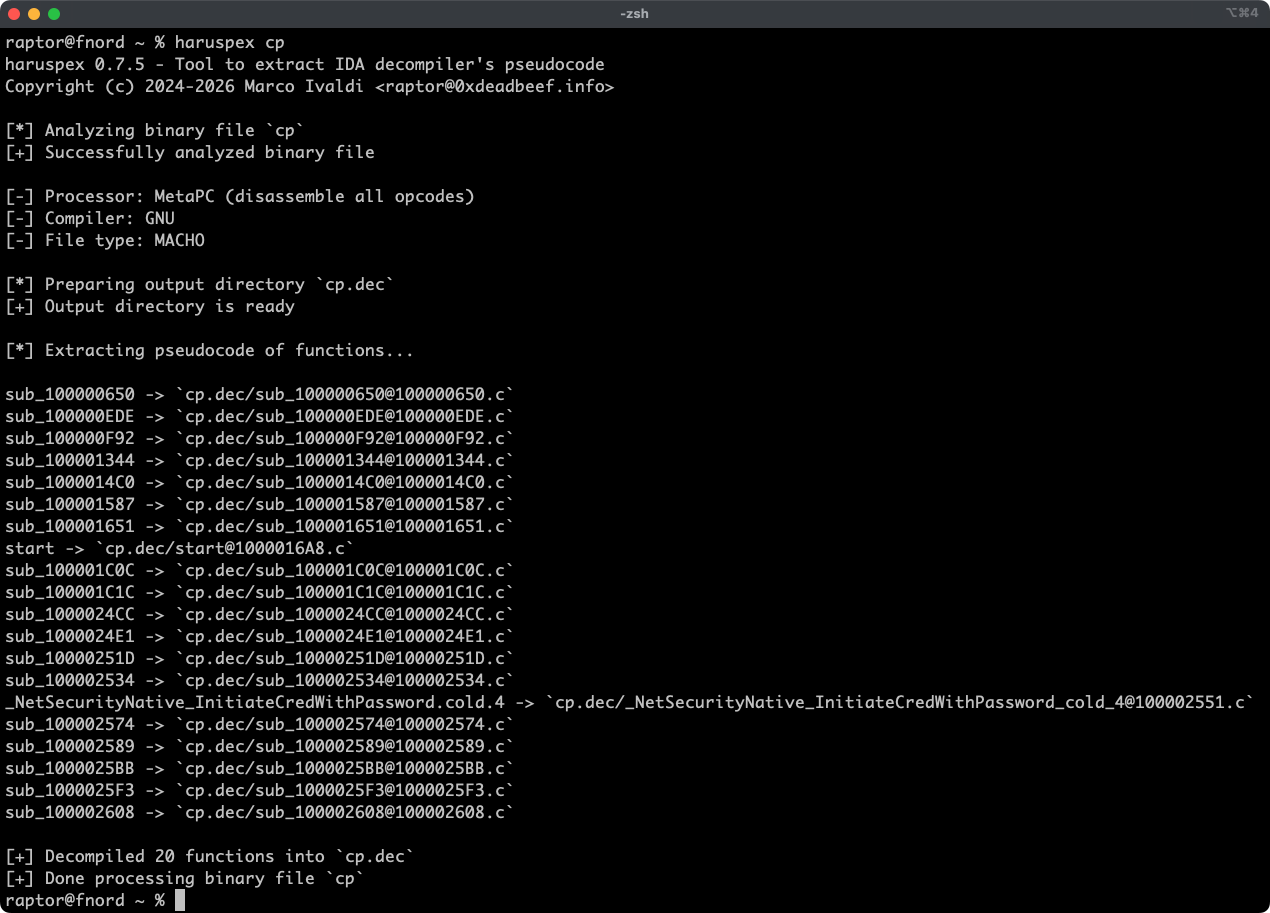
haruspex
 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
binary-analysisreverse-engineeringstatic-code-analysis+1
1354 days ago
0xdea/haruspexVulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 0xdea/ghidra-scripts
Curated Ghidra scripts to automate reverse engineering and vulnerability analysis: locate insecure functions, extract decompiler pseudocode, fix…
 limingxi6/cve-2020-9373-netgear-r6400
解决网络安全漏洞
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
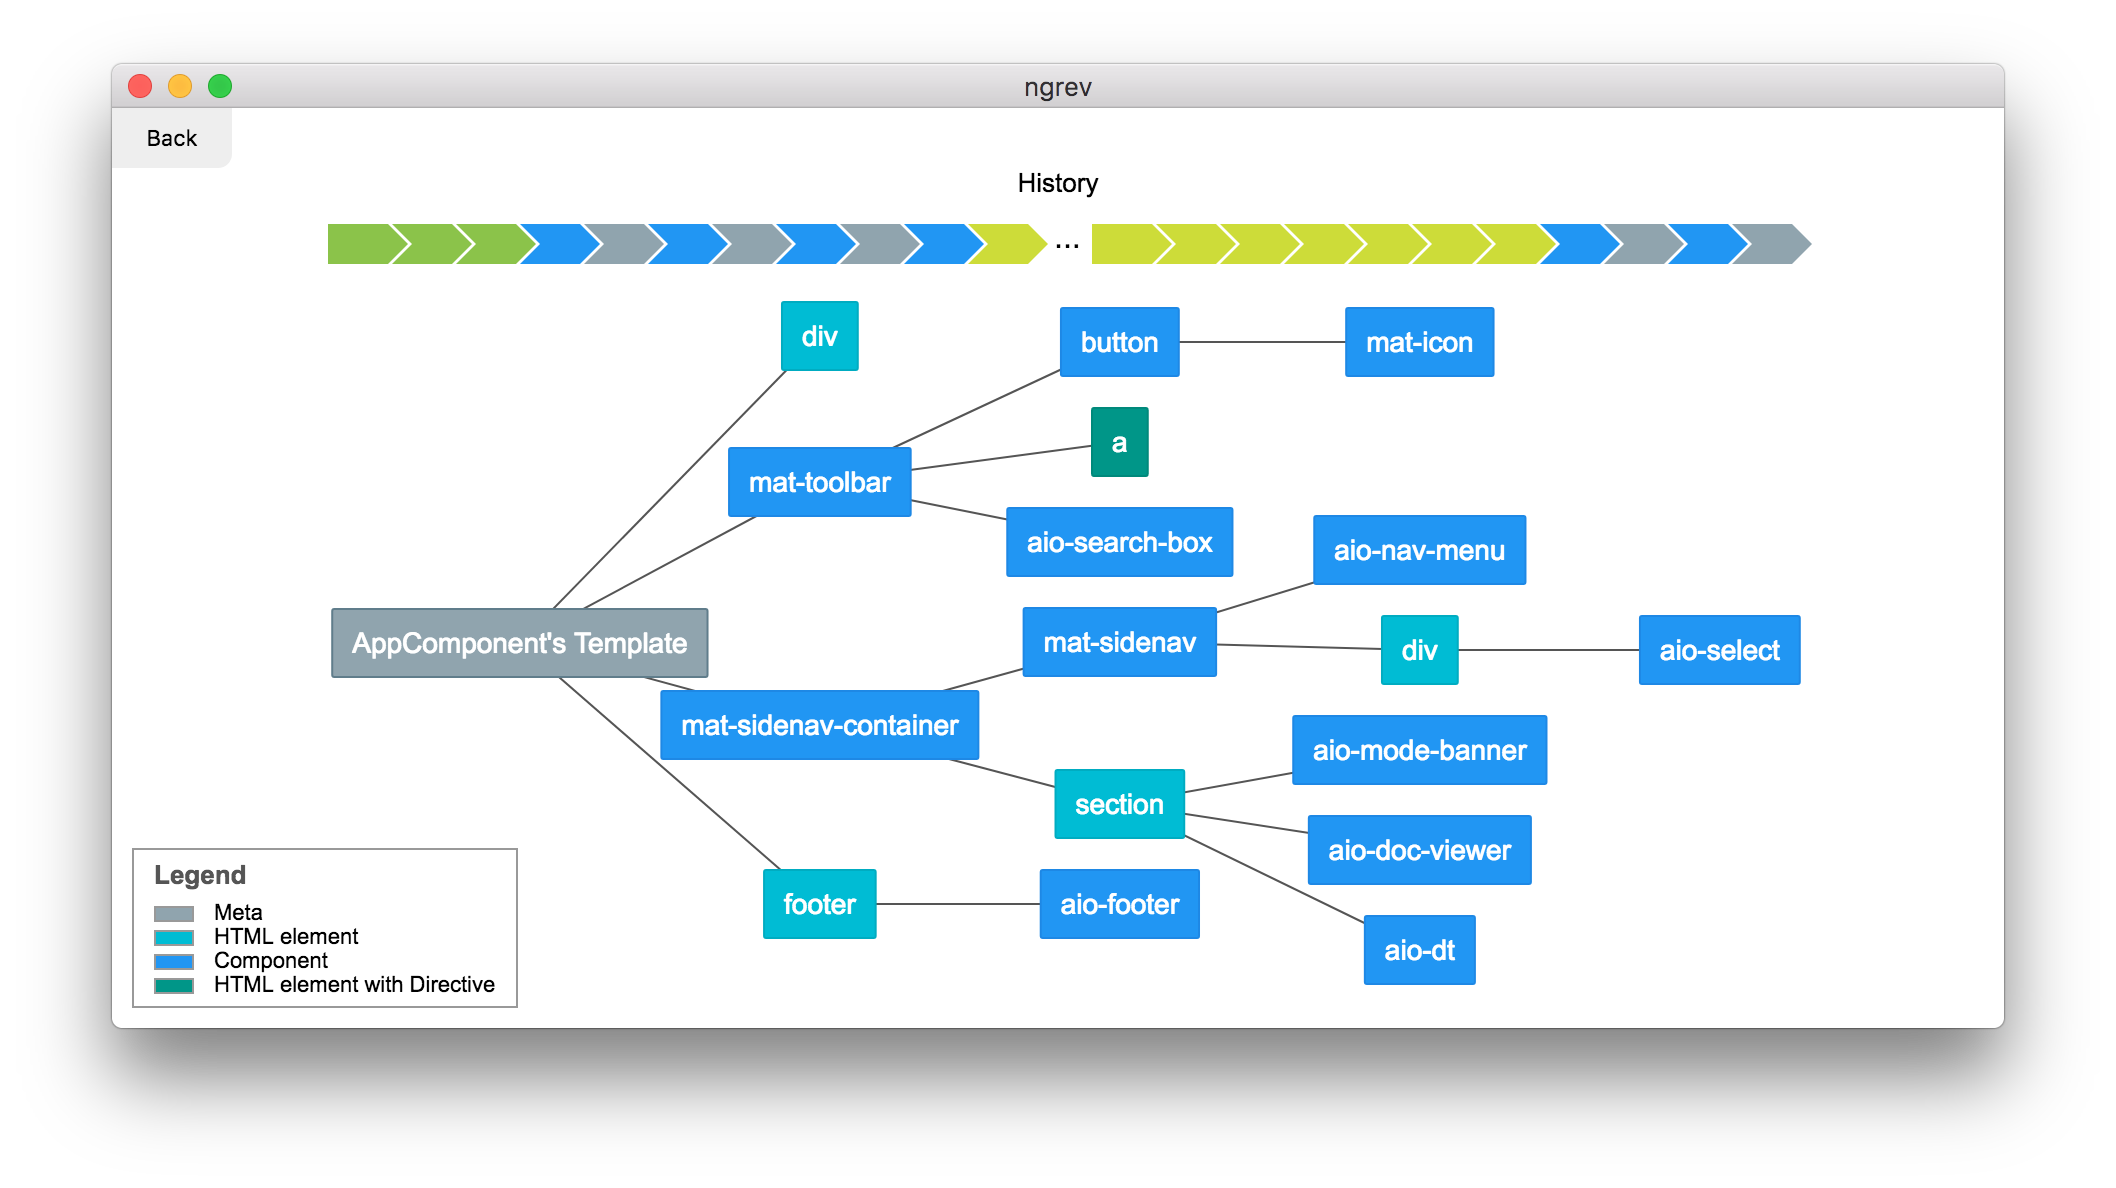 mgechev/ngrev
Tool for reverse engineering of Angular applications
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.