Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
63 results
seclab-taskflow-agent preview

seclab-taskflow-agent

GitHubgithubsecuritylab/seclab-taskflow-agent

MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…

ai-assisted-reversingai-securitycode-analysis+9
284

14 days ago
VulnHunter preview

VulnHunter

GitHubnealbridges/vulnhunter

Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…

ai-assisted-reversingai-securitycode-analysis+9
7902 days ago
Deserializer preview

Deserializer

GitHubjoshuaprovoste/deserializer

AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…

ai-securitycode-analysisexploitation+6
222h 47m ago
JavaSecLab preview

JavaSecLab

GitHubwhgojp/javaseclab

Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…

code-analysisctfdevsecops+6
8864 months ago
CVE-2025-23134_fixes_code preview

CVE-2025-23134_fixes_code

GitHubthrilokh-q123/cve-2025-23134_fixes_code

The ASN1_STRING_set() function takes an `int` length, make sure the argument is not inadvertently truncated when it is called from asn1_ex_c2i().

code-analysiscryptographydefensive-tools+2
11 month ago
o1js-scan preview

o1js-scan

GitHubauditinfra-io/o1js-scan

Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits

code-analysiscryptographydefensive-tools+5
320 days ago
TriSuElla-AIDLCA-Framework preview

TriSuElla-AIDLCA-Framework

GitHubowasp/trisuella-aidlca-framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

ai-securitycloud-securitycode-analysis+7
31 month ago
kube-linter preview

kube-linter

GitHubstackrox/kube-linter

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

cloud-infrastructure-securitycloud-securityconfiguration-auditing+6
3.5k2 days ago
nullorigin preview

nullorigin

GitHubrakib-nyc/nullorigin

Research-only AI watermark robustness toolkit: local reverse proxy strips C2PA/EXIF/XMP, Unicode, image/audio stego, OOXML/PDF metadata, and scans…

adversarial-attackai-securityeducation+4
52 months ago
schrodingers-toctou preview

schrodingers-toctou

GitHubxoreaxeaxeax/schrodingers-toctou

Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…

binary-analysisdynamic-analysis-sandboxingeducation+3
1512 months ago
vbSparkle preview

vbSparkle

GitHubairbus-cert/vbsparkle

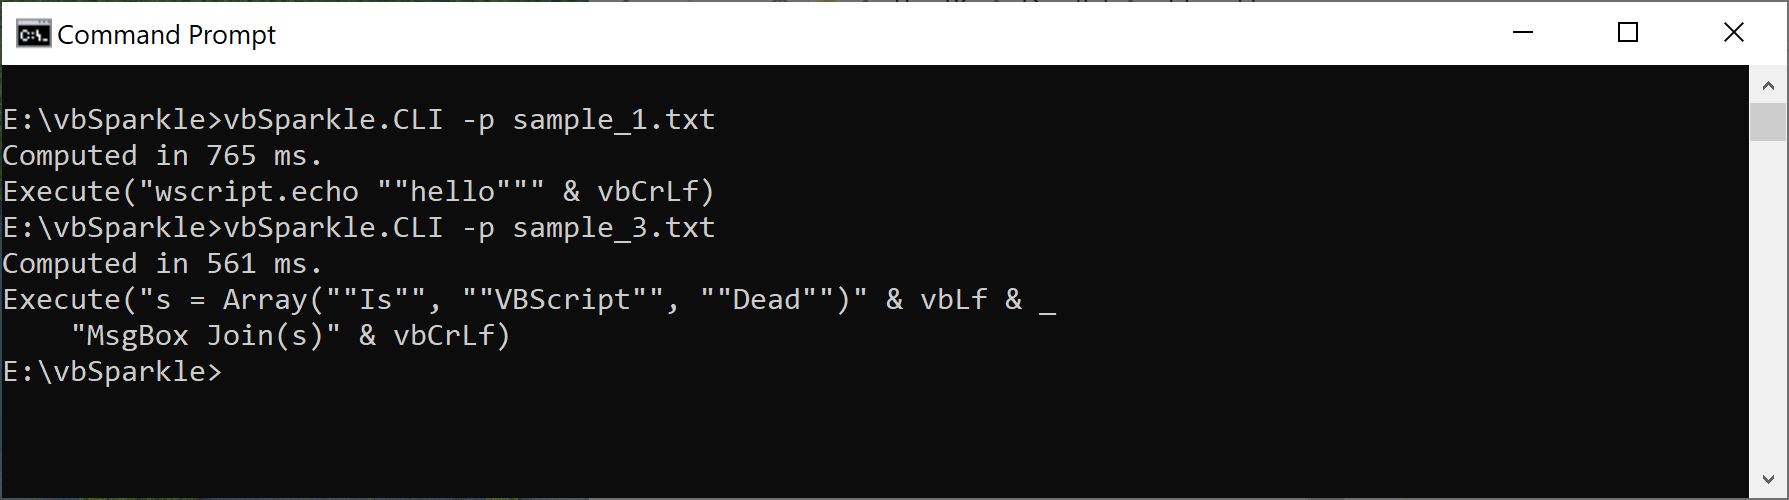
VBScript & VBA source-to-source deobfuscator with partial-evaluation

code-analysisdefensive-toolsmalware-analysis+2
814 years ago
UTopia preview

UTopia

GitHubsamsung/utopia

UT based automated fuzz driver generation

code-analysisfuzzingstatic-code-analysis+1
1701 year ago
ghidrecomp preview

ghidrecomp

GitHubclearbluejar/ghidrecomp

Python Command-Line Ghidra Decompiler

binary-analysisreverse-engineeringstatic-code-analysis+1
1609 months ago
jsluicepp preview

jsluicepp

GitHub0x999-x/jsluicepp

jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice

api-security-testinginformation-gatheringreconnaissance+3
3042 years ago
CVE-2026-56158-.NET-Framework-RCE-PoC-Exploit preview

CVE-2026-56158-.NET-Framework-RCE-PoC-Exploit

GitHubsam00/cve-2026-56158-.net-framework-rce-poc-exploit

Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…

exploitationpayload-developmentpayload-generation+4
12 months ago
JShunter preview

JShunter

GitHubcc1a2b/jshunter

jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…

api-securitydynamic-code-analysispenetration-testing+6
5441 month ago
CVE-2026-13158 preview

CVE-2026-13158

GitHubminhhk68/cve-2026-13158

Proof-of-concept exploit and technical advisory for an Admin+ arbitrary file upload to remote code execution vulnerability in Everest Toolkit…

exploitationpayload-developmentpenetration-testing+4
3 months ago
call_map preview

call_map

GitHubnccgroup/call_map

Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.

code-analysisreverse-engineeringstatic-code-analysis+1
299 years ago
Previous1234Next