
cryptoptic
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
code-analysisconfiguration-auditingcryptography+6
nationwide-group-oss/cryptopticCodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
 thrilokh-q123/cve-2025-23134_fixes_code
The ASN1_STRING_set() function takes an `int` length, make sure the argument is not inadvertently truncated when it is called from asn1_ex_c2i().
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows
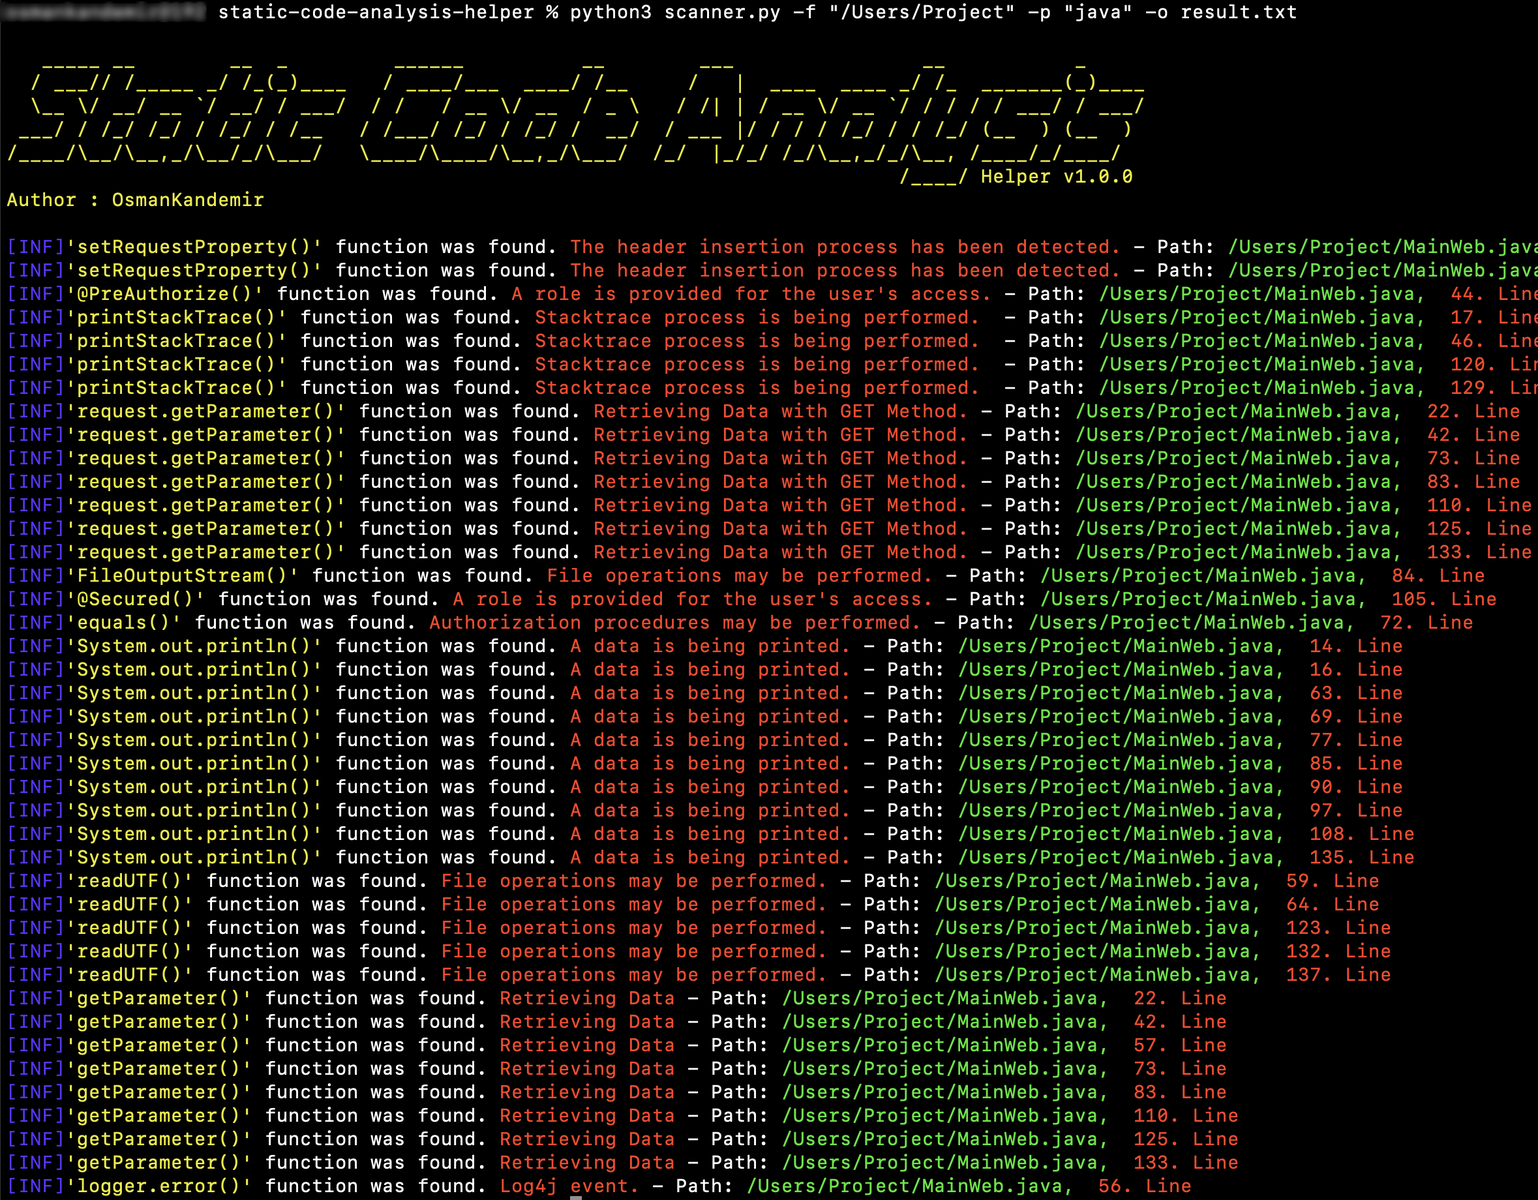 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 luiscastellanos-dev/cobol-shield
Security hardening toolkit for COBOL legacy systems — invisible Unicode detection, format boundary analysis, source transformation integrity


 samsung/utopia
UT based automated fuzz driver generation
 0x3c3e/slides
CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU
 trailofbits/multiplier
Indexes C/C++ build artifacts into a queryable whole-program database, exposing AST, token, and IR-level APIs for code auditing and vulnerability…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 robocoder/rips-scanner
RIPS - A static source code analyser for vulnerabilities in PHP scripts
 minhhk68/cve-2026-13158
Proof-of-concept exploit and technical advisory for an Admin+ arbitrary file upload to remote code execution vulnerability in Everest Toolkit…
 nccgroup/cq
Fast code security scanner designed for manual security code review by experts. Outputs line-referenced findings to text files for easy filtering and…
 nccgroup/glasgo
Go static analysis tool that checks for security issues using an AST.