

semgrep
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
api-securityapi-security-testingcode-analysis+9
16.8k3 days ago
semgrep/semgrepLightweight static analysis for many languages. Find bug variants with patterns that look like source code.
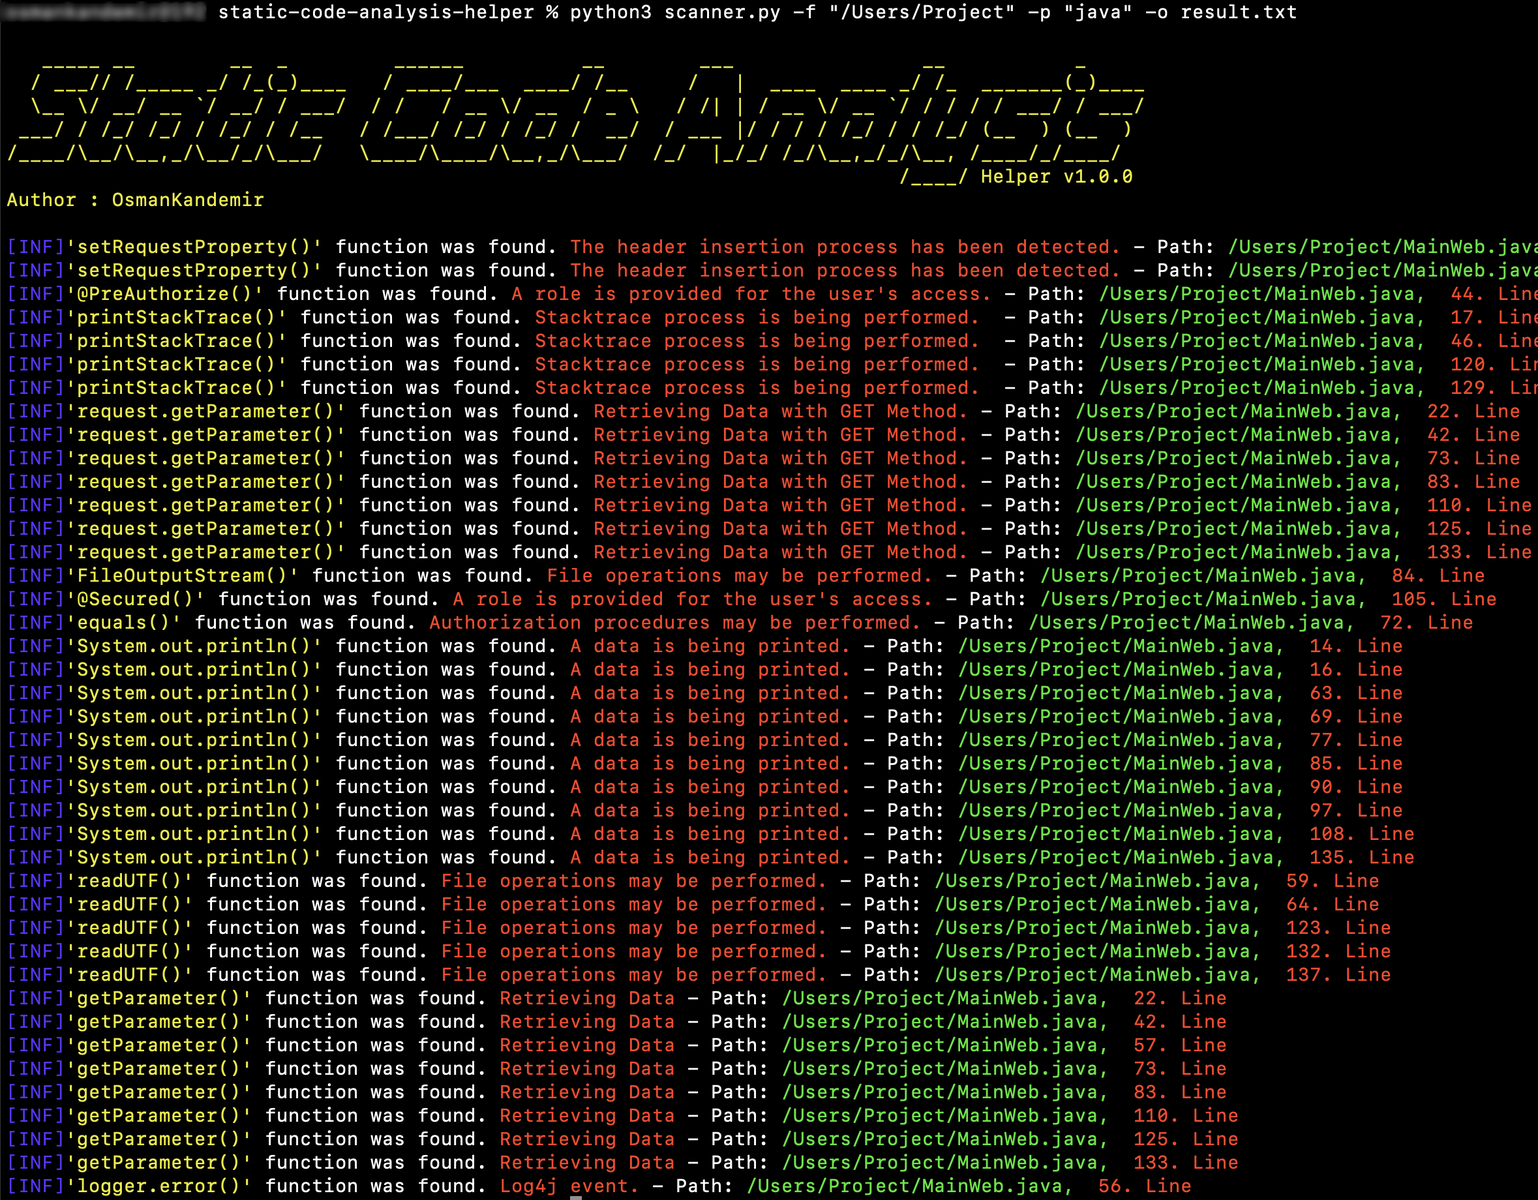 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 novoda/gradle-static-analysis-plugin
Easy setup of static analysis tools for Android and Java projects.
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 tai-e/cve-2021-44228
Utilize Tai-e to identify the Log4shell (a.k.a. CVE-2021-44228) Vulnerability
 noveogroup/android-check
Static code analysis plugin for Android project. (Checkstyle, PMD)
 yousif-iq/cve-2026-39259
CVE-2026-39259
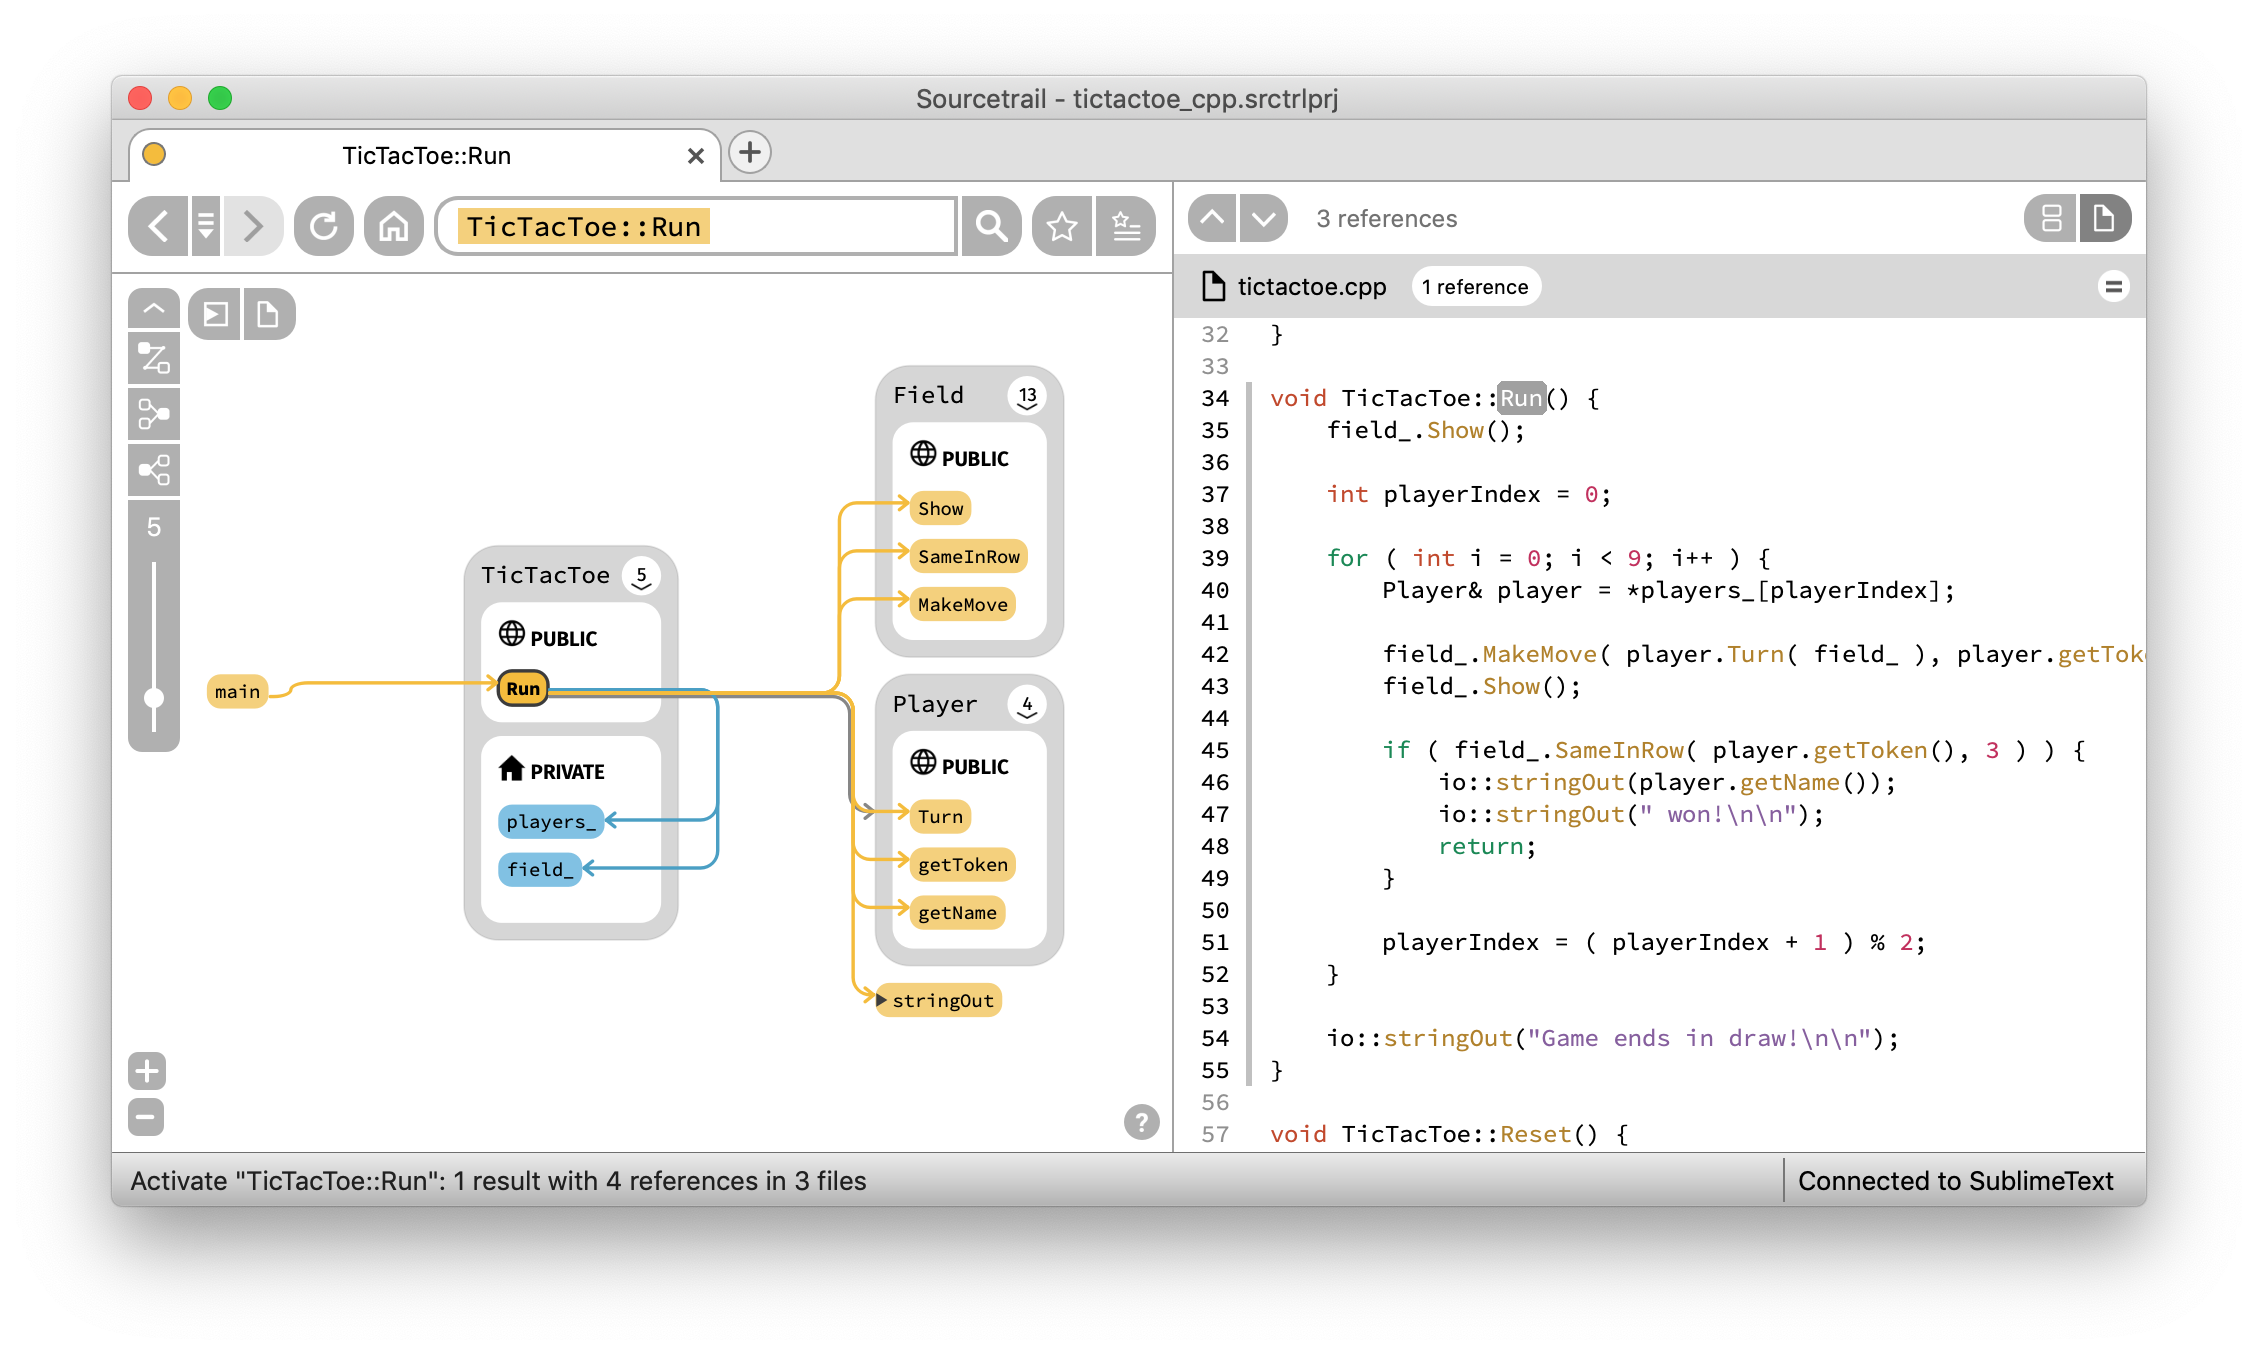 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer
 nightwatchcybersecurity/airflowscan
Checklist and tools for increasing security of Apache Airflow
 waleedadam360-web/syncshield
SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)