

njsscan
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
code-analysisdevsecopsstatic-analysis+3
457
ajinabraham/njsscanSemantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
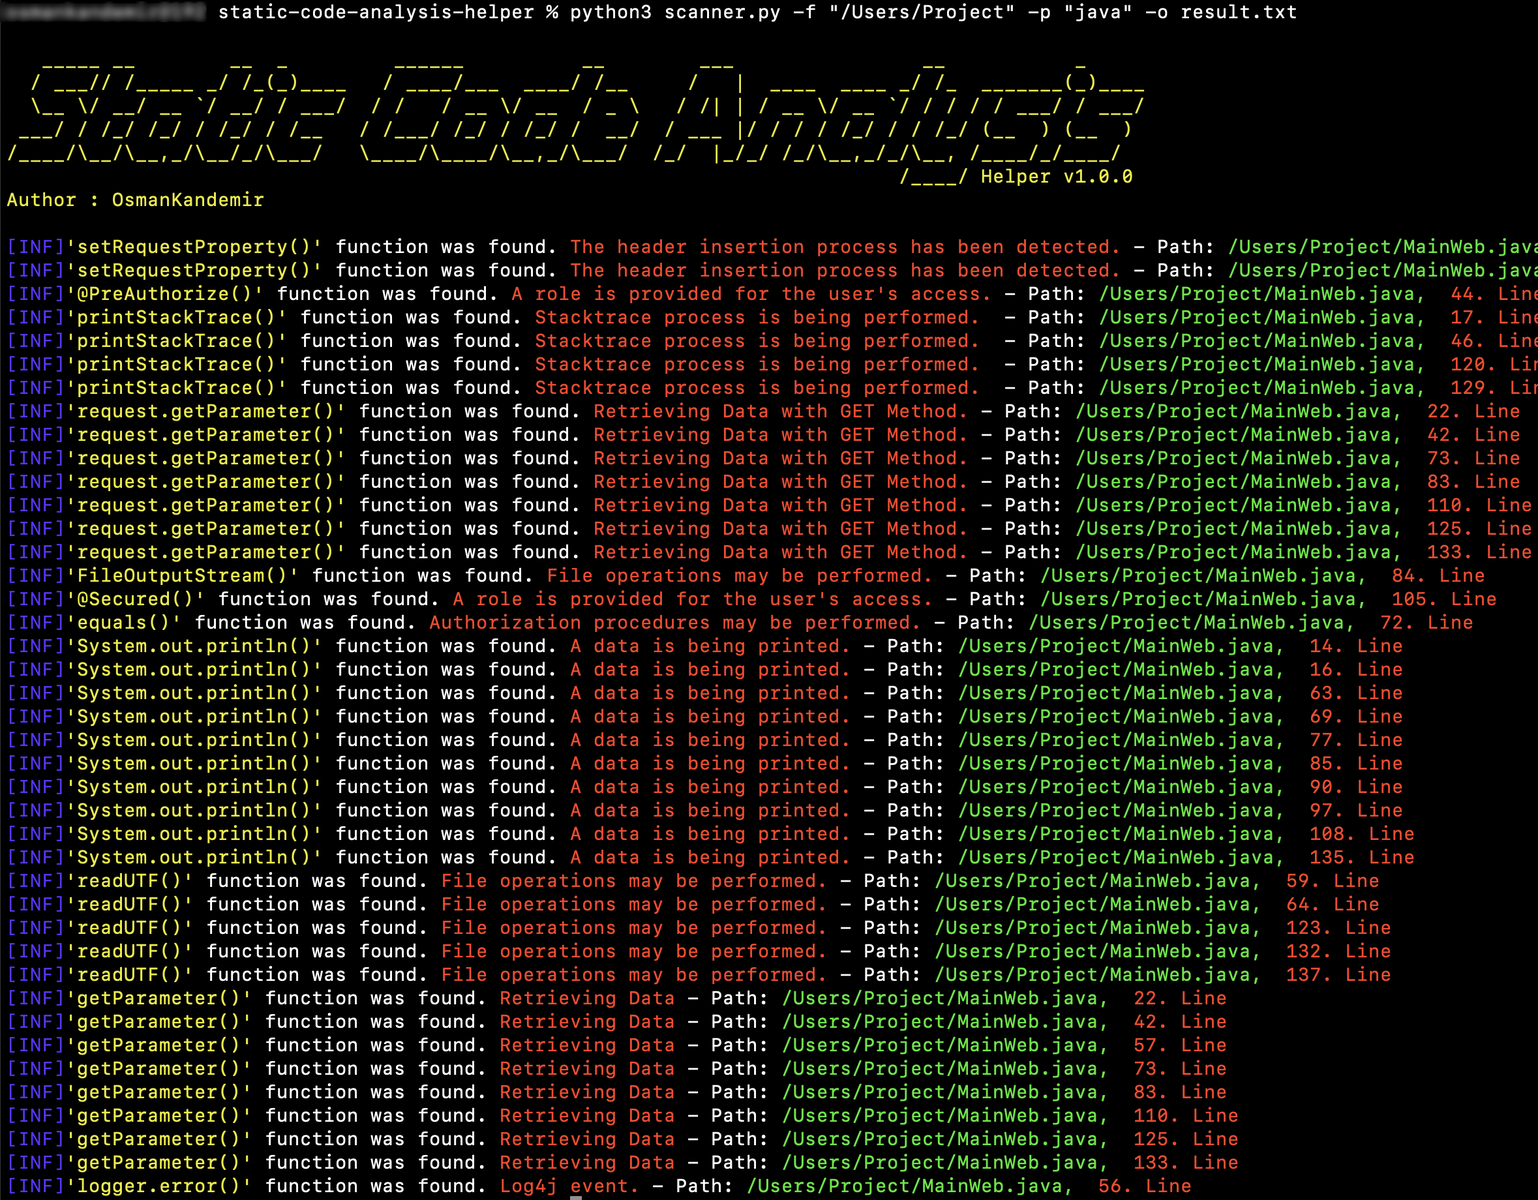 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
 sonarsource/sonarcloud-scan
A Bitbucket Pipe to trigger SonarCloud analysis
 luiscastellanos-dev/cobol-shield
Security hardening toolkit for COBOL legacy systems — invisible Unicode detection, format boundary analysis, source transformation integrity
 kira2040k/php_code_analysis
Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…
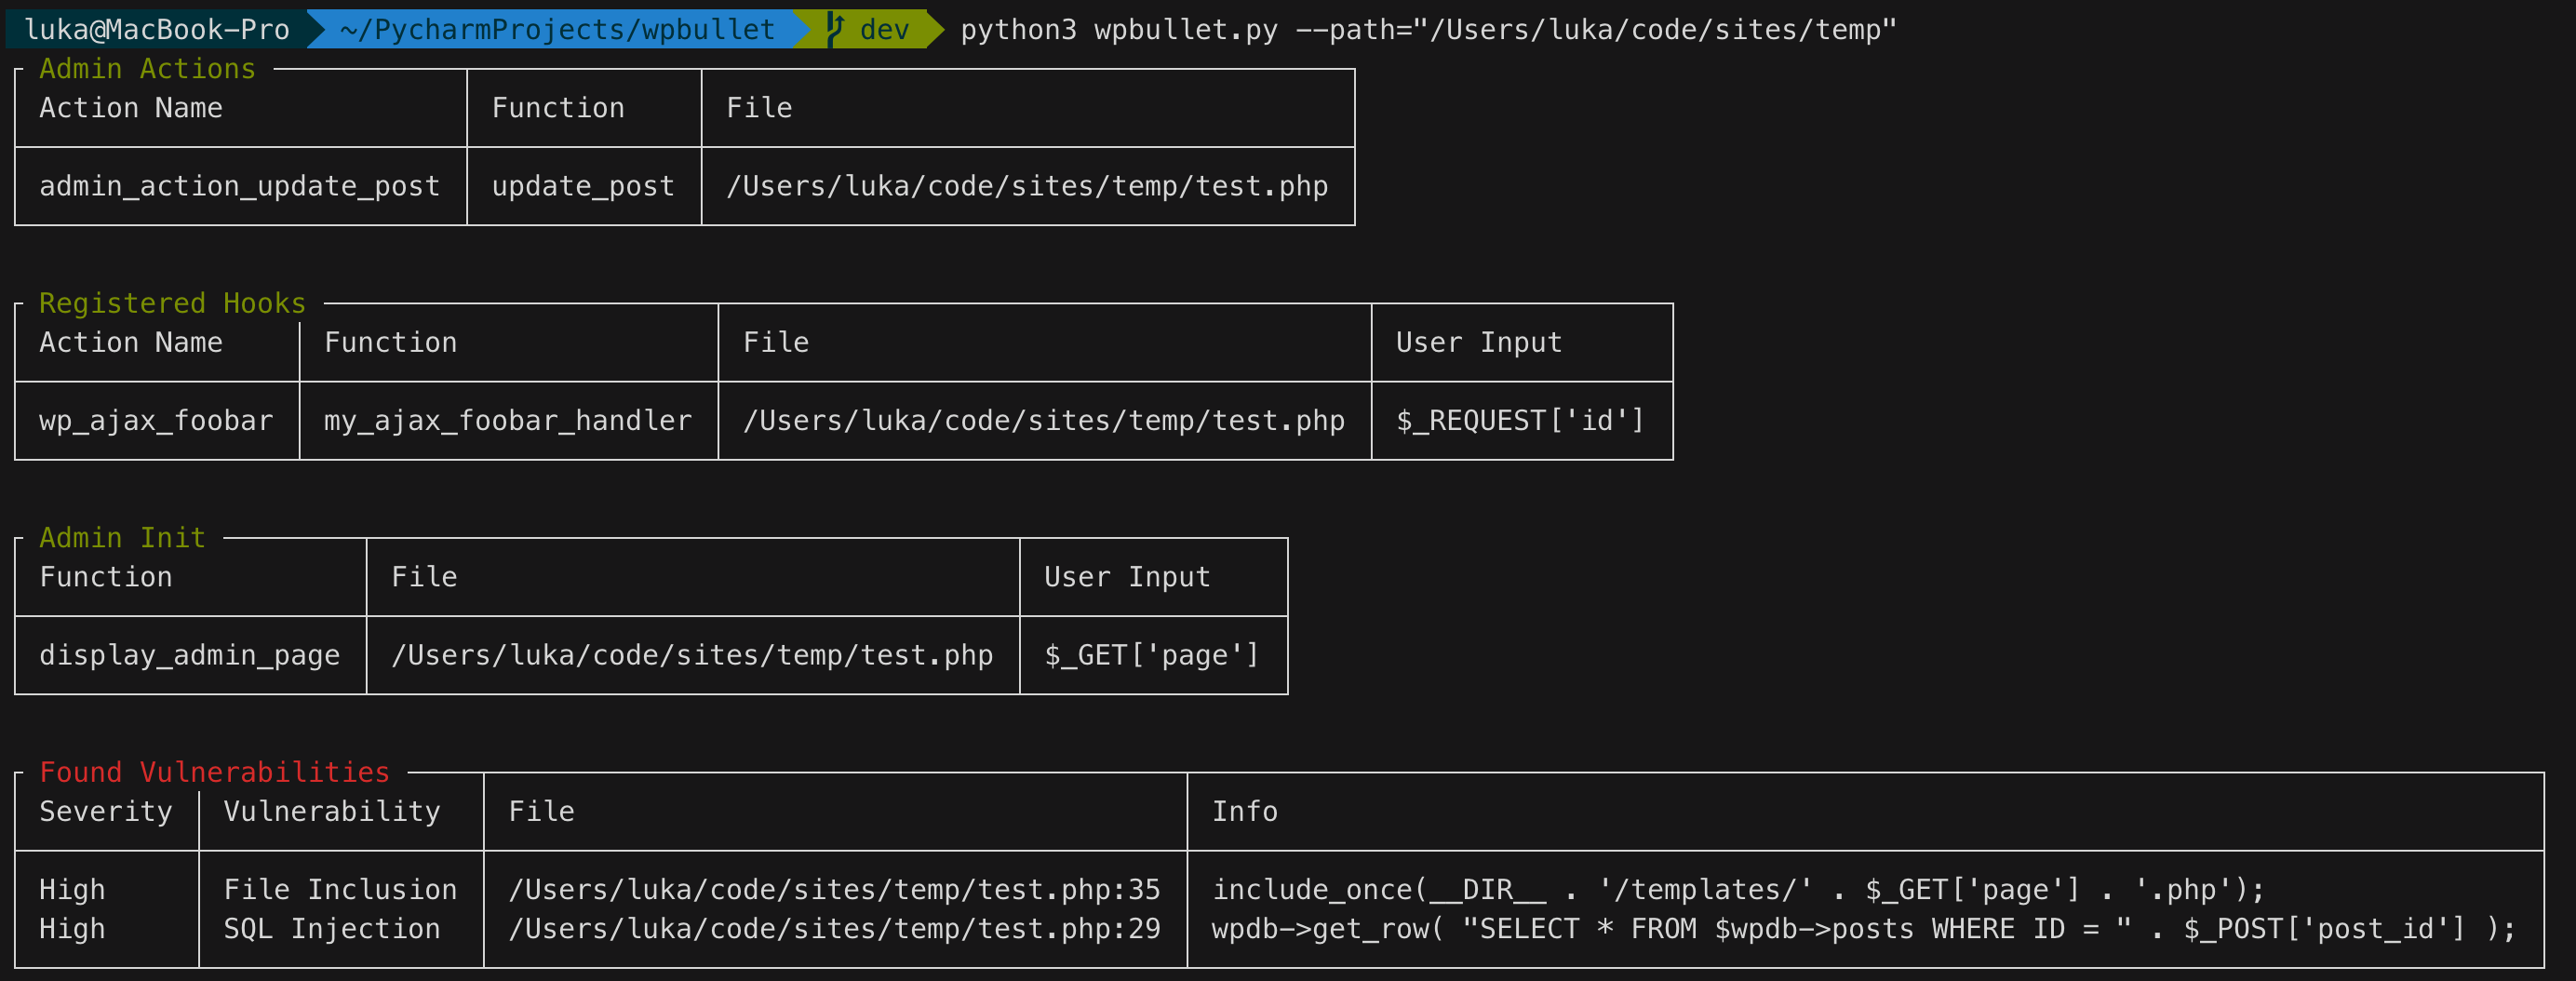 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 agrawalsmart7/scodescanner
Command-line static analysis scanner that detects critical vulnerabilities in PHP and YAML source code using custom semgrep rules, with Jira and…