

security-harness
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
ai-securitycode-analysisdevsecops+9
40
dmdhrumilmistry/security-harnessMulti-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
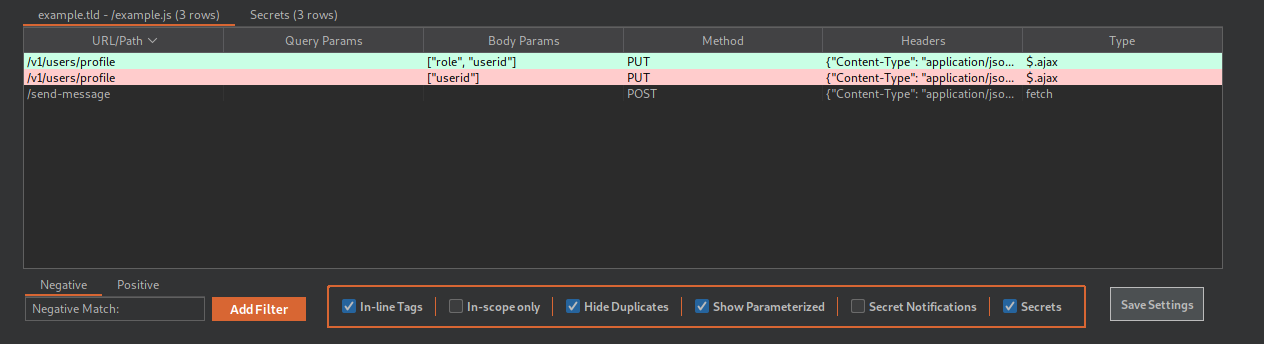 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
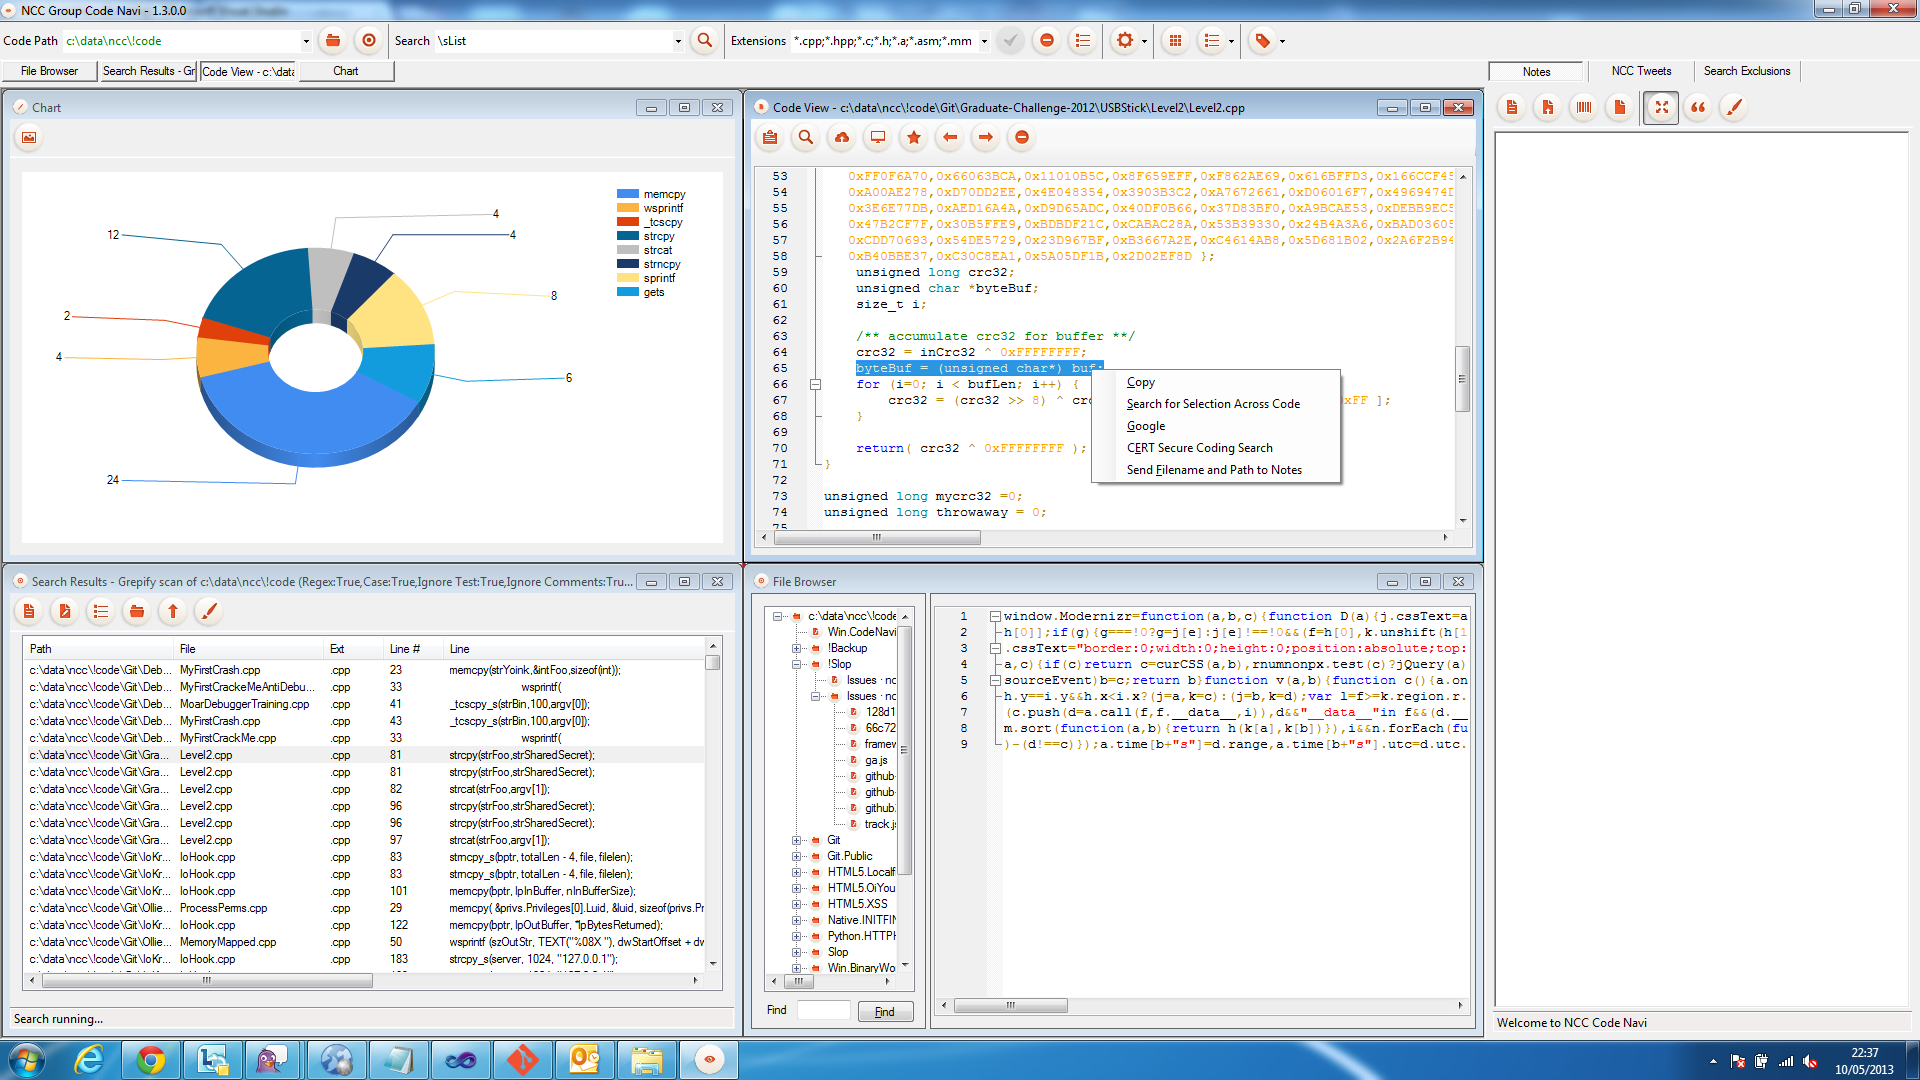 nccgroup/ncccodenavi
NCC Code Navigator