
static-analysis
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
code-analysiscurated-resourcesdevsecops+5
14.9k
analysis-tools-dev/static-analysisCurated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 rakib-nyc/nullorigin
Research-only AI watermark robustness toolkit: local reverse proxy strips C2PA/EXIF/XMP, Unicode, image/audio stego, OOXML/PDF metadata, and scans…
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
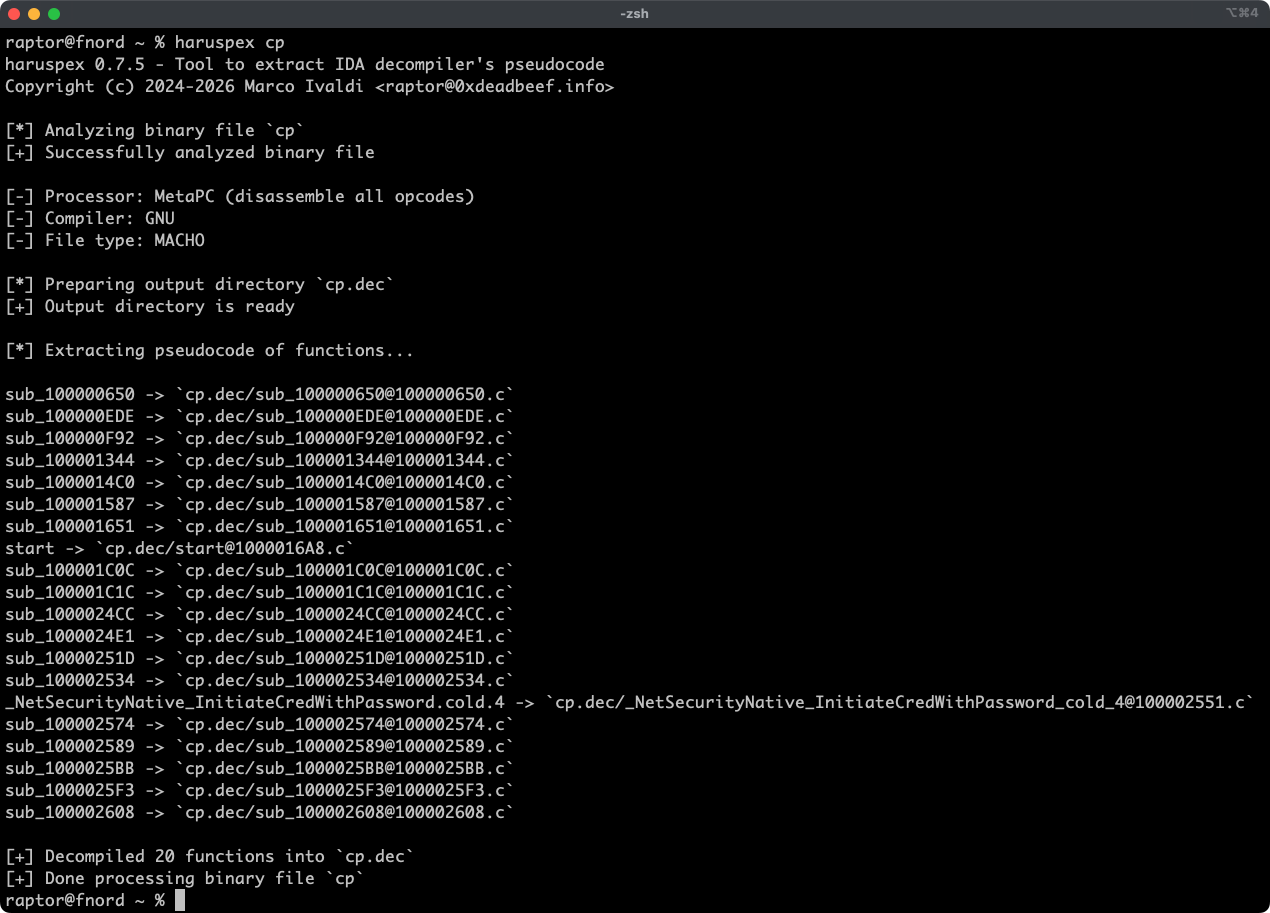 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
 reverseclabs/needle
The iOS Security Testing Framework
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
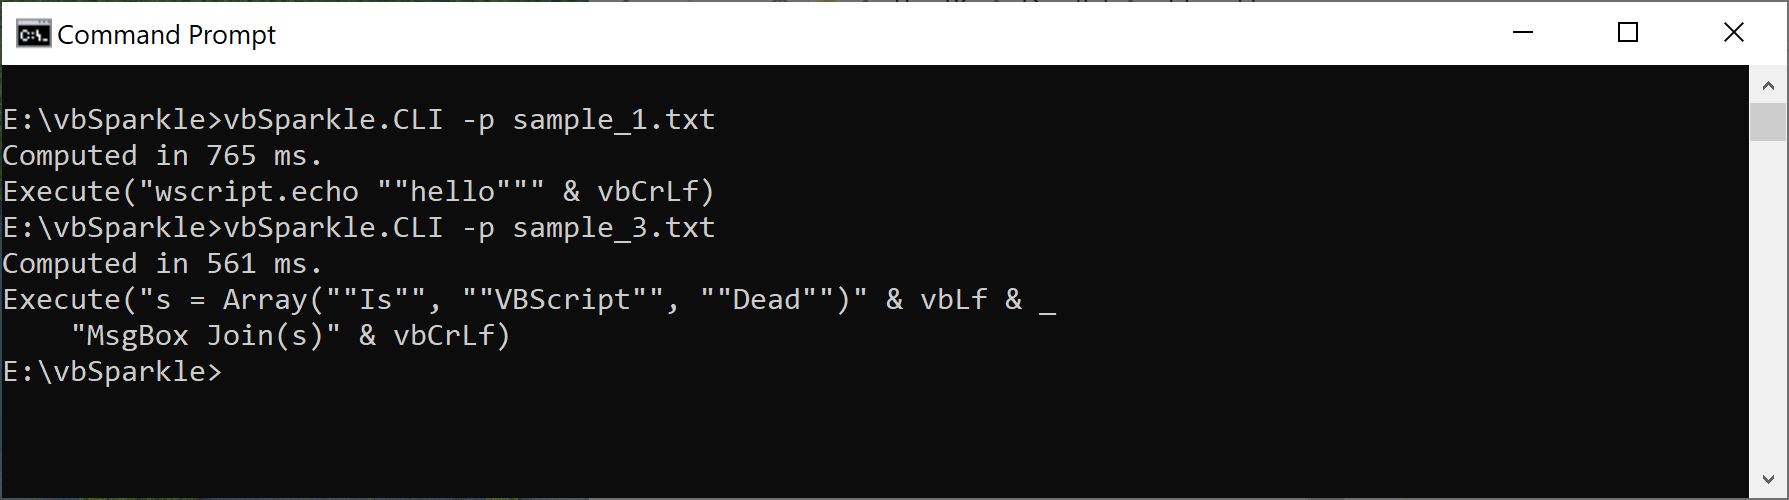 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 0xdea/ghidra-scripts
Curated Ghidra scripts to automate reverse engineering and vulnerability analysis: locate insecure functions, extract decompiler pseudocode, fix…