

njsscan
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
code-analysisdevsecopsstatic-analysis+3
454
ajinabraham/njsscanSemantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 silverplate3/my-cves
CVE's I found. technical writeups, expolitation examples and fuzzing sessions walkthroughs
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
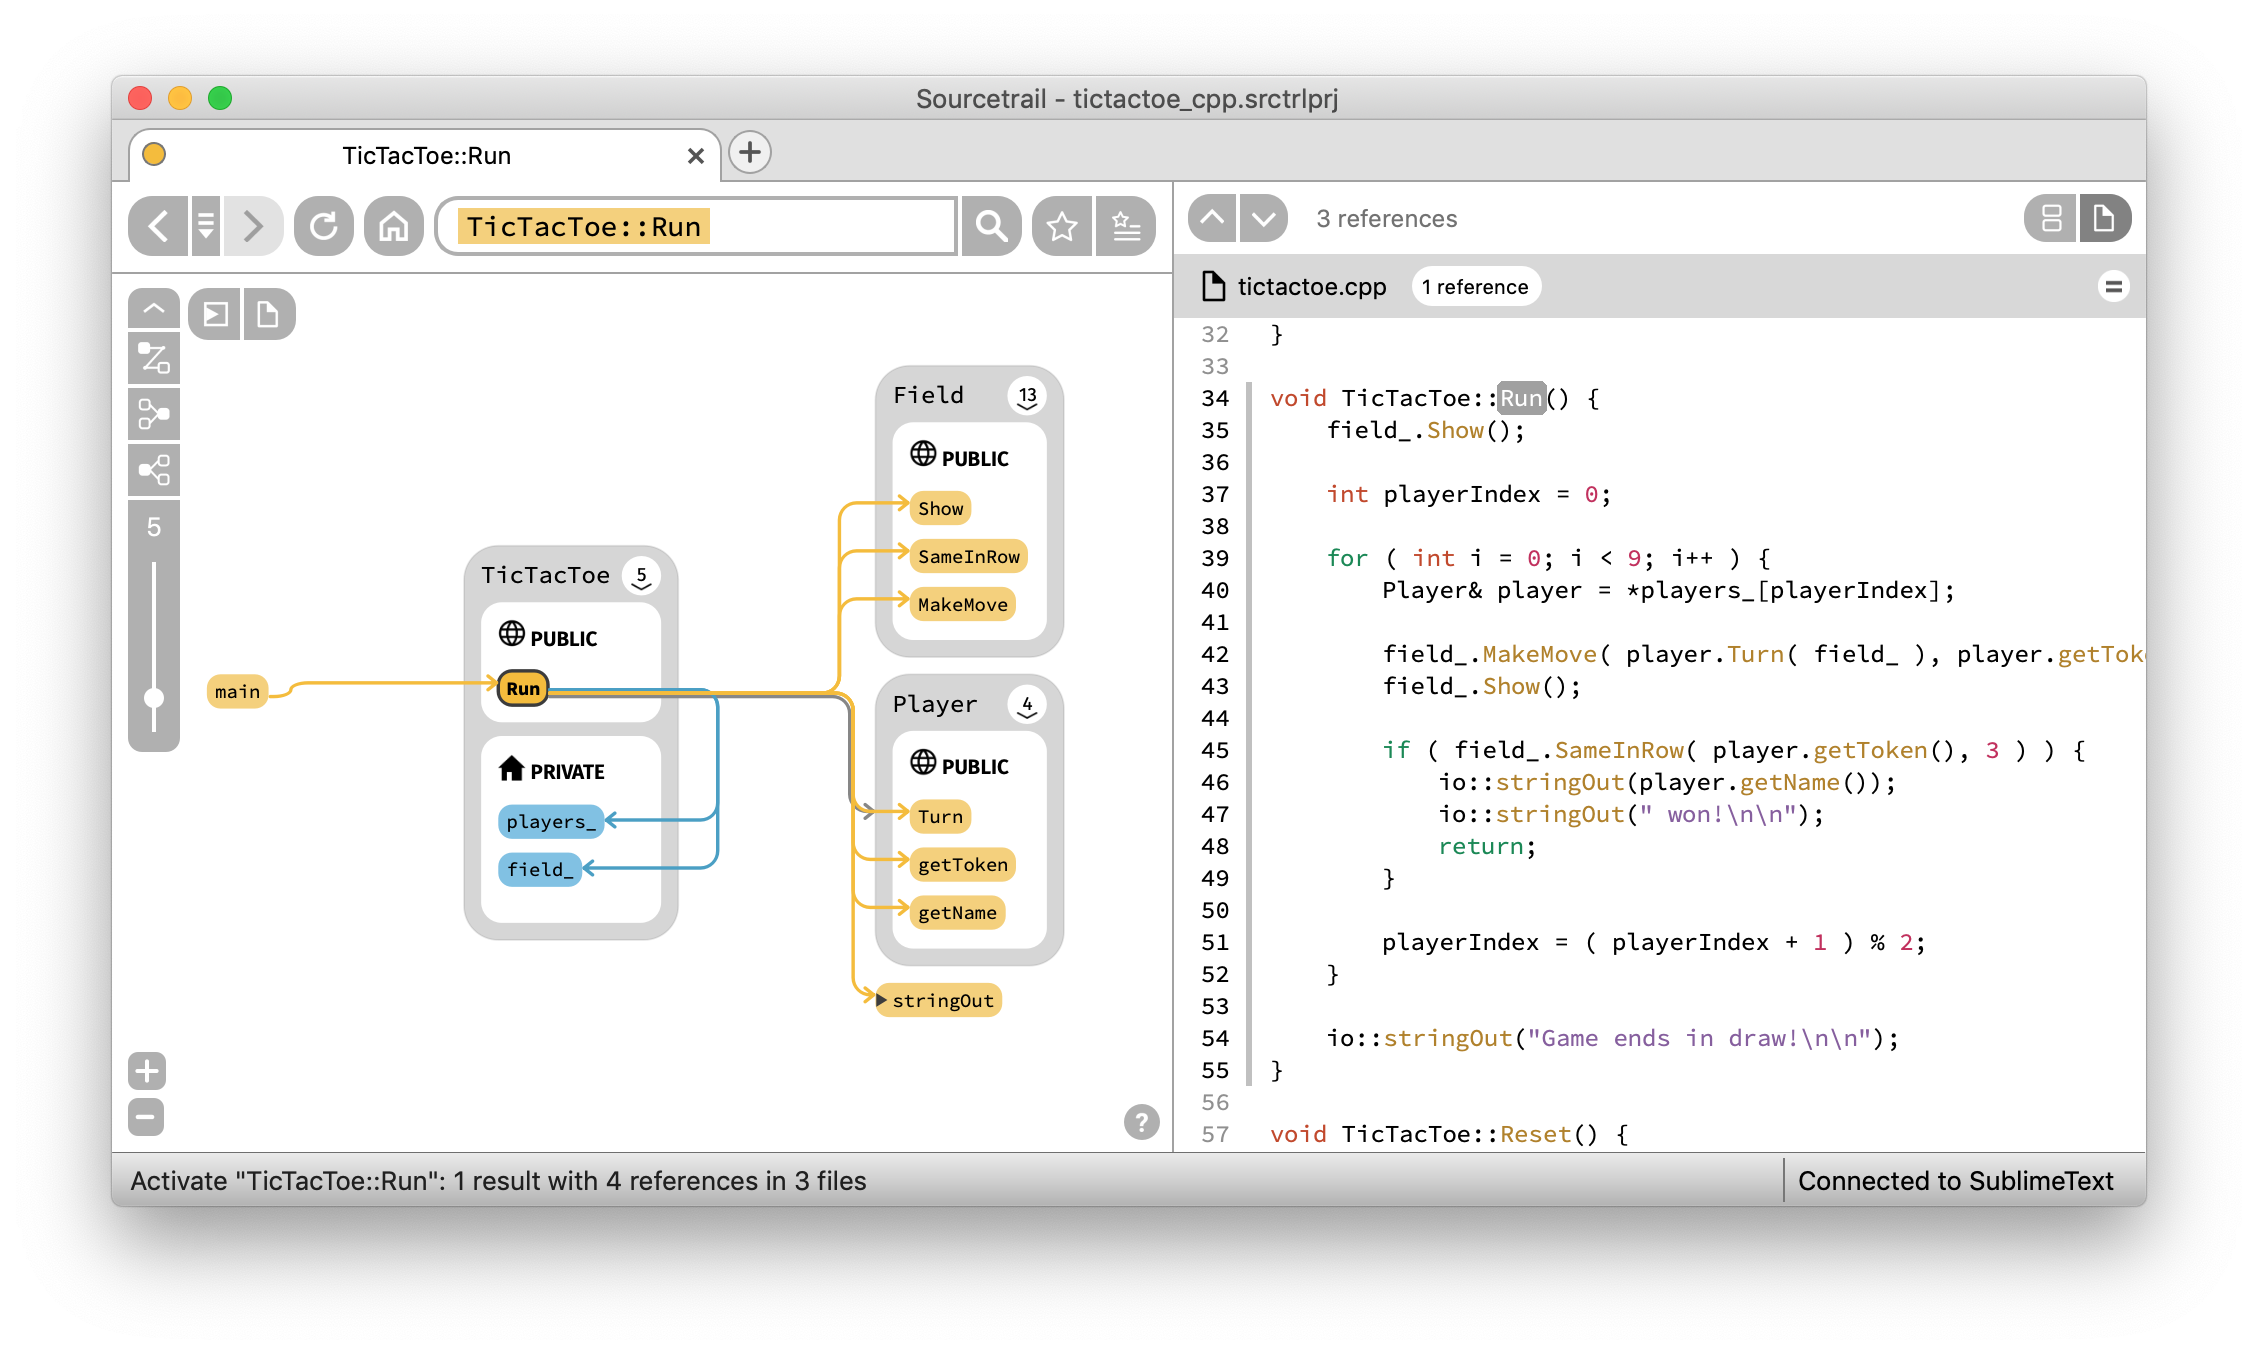 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer
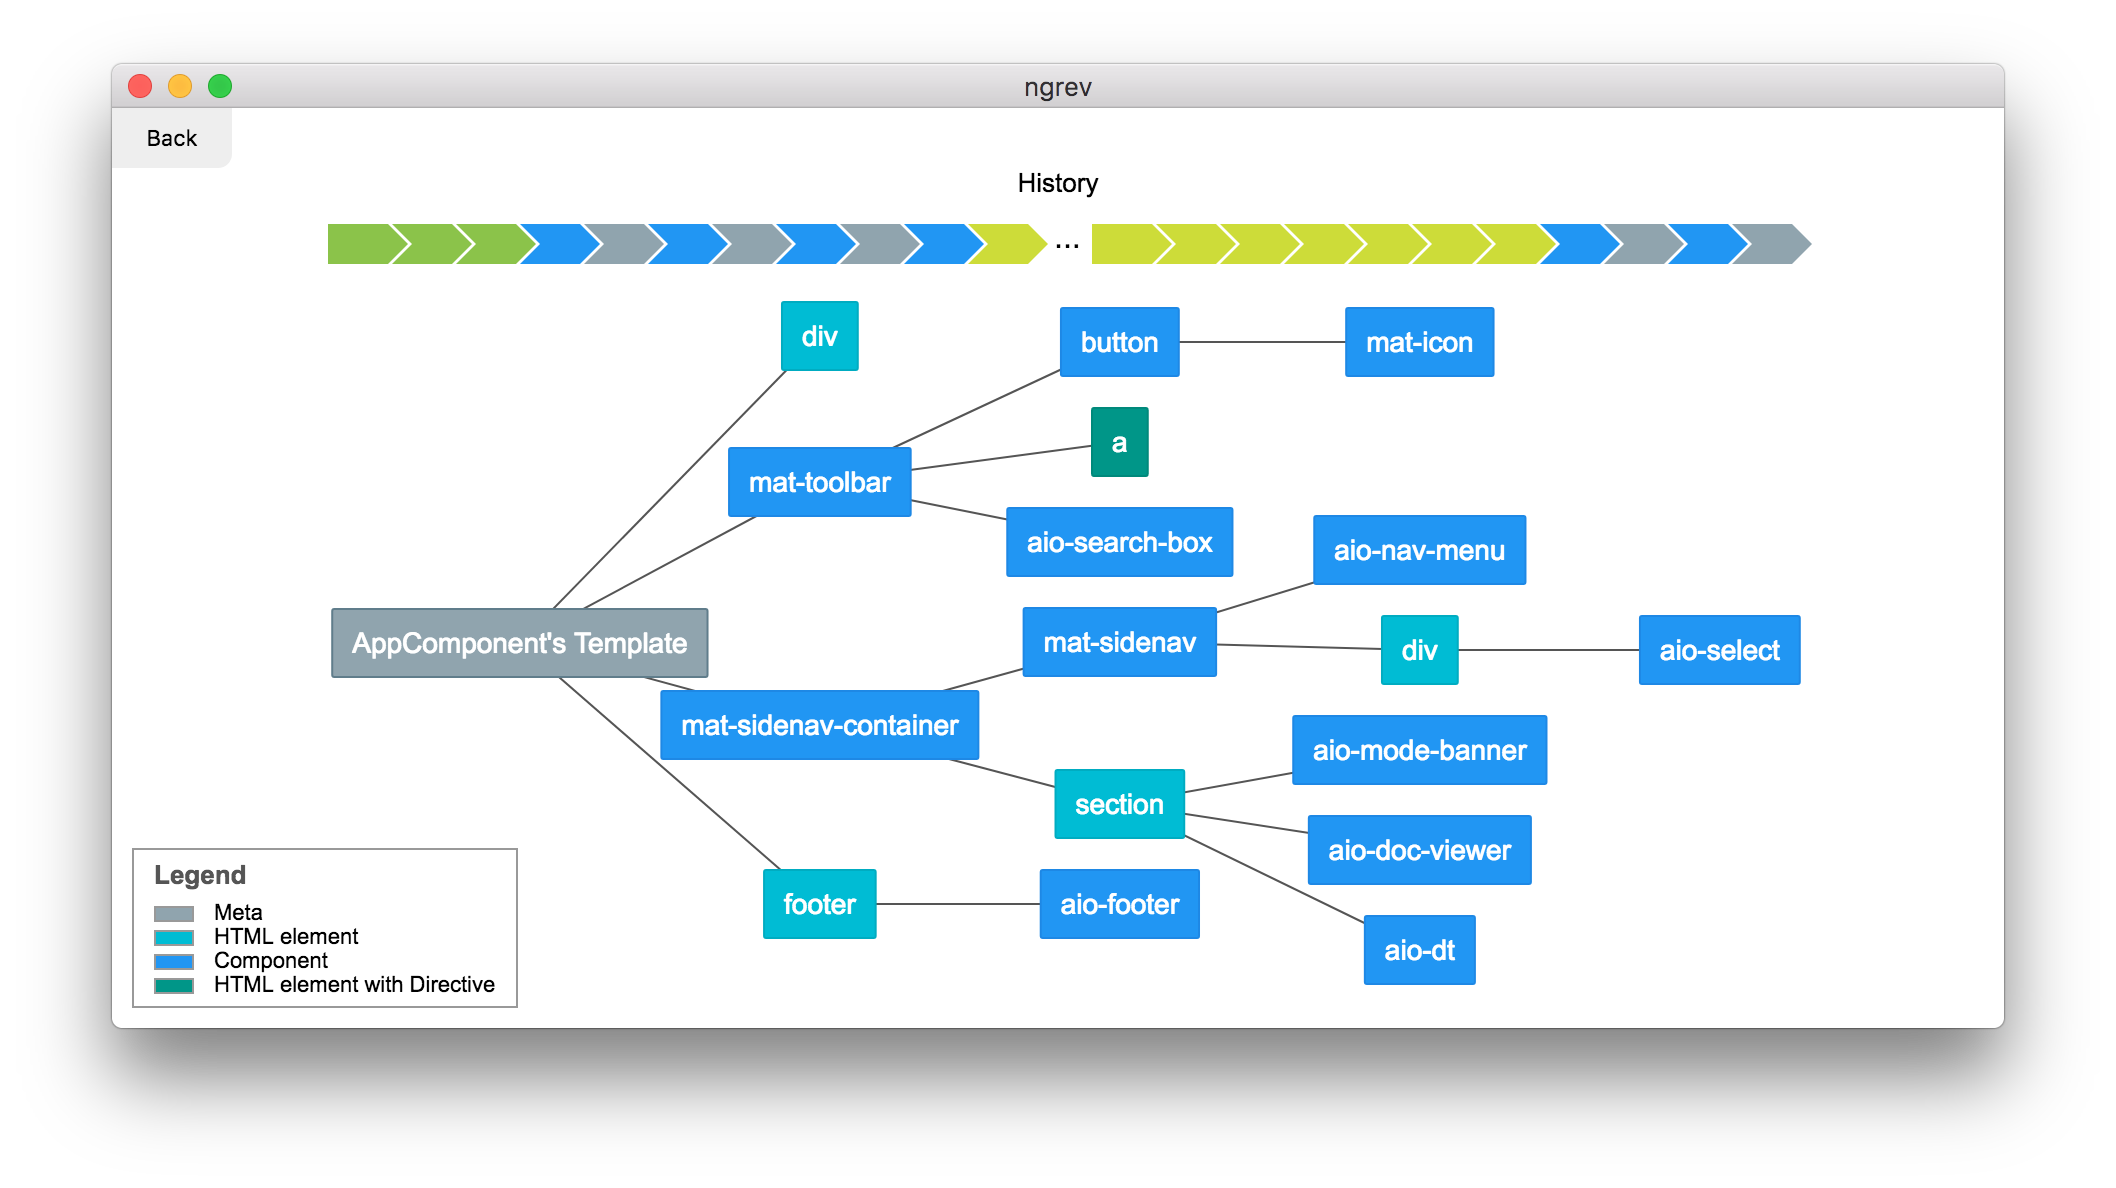 mgechev/ngrev
Tool for reverse engineering of Angular applications
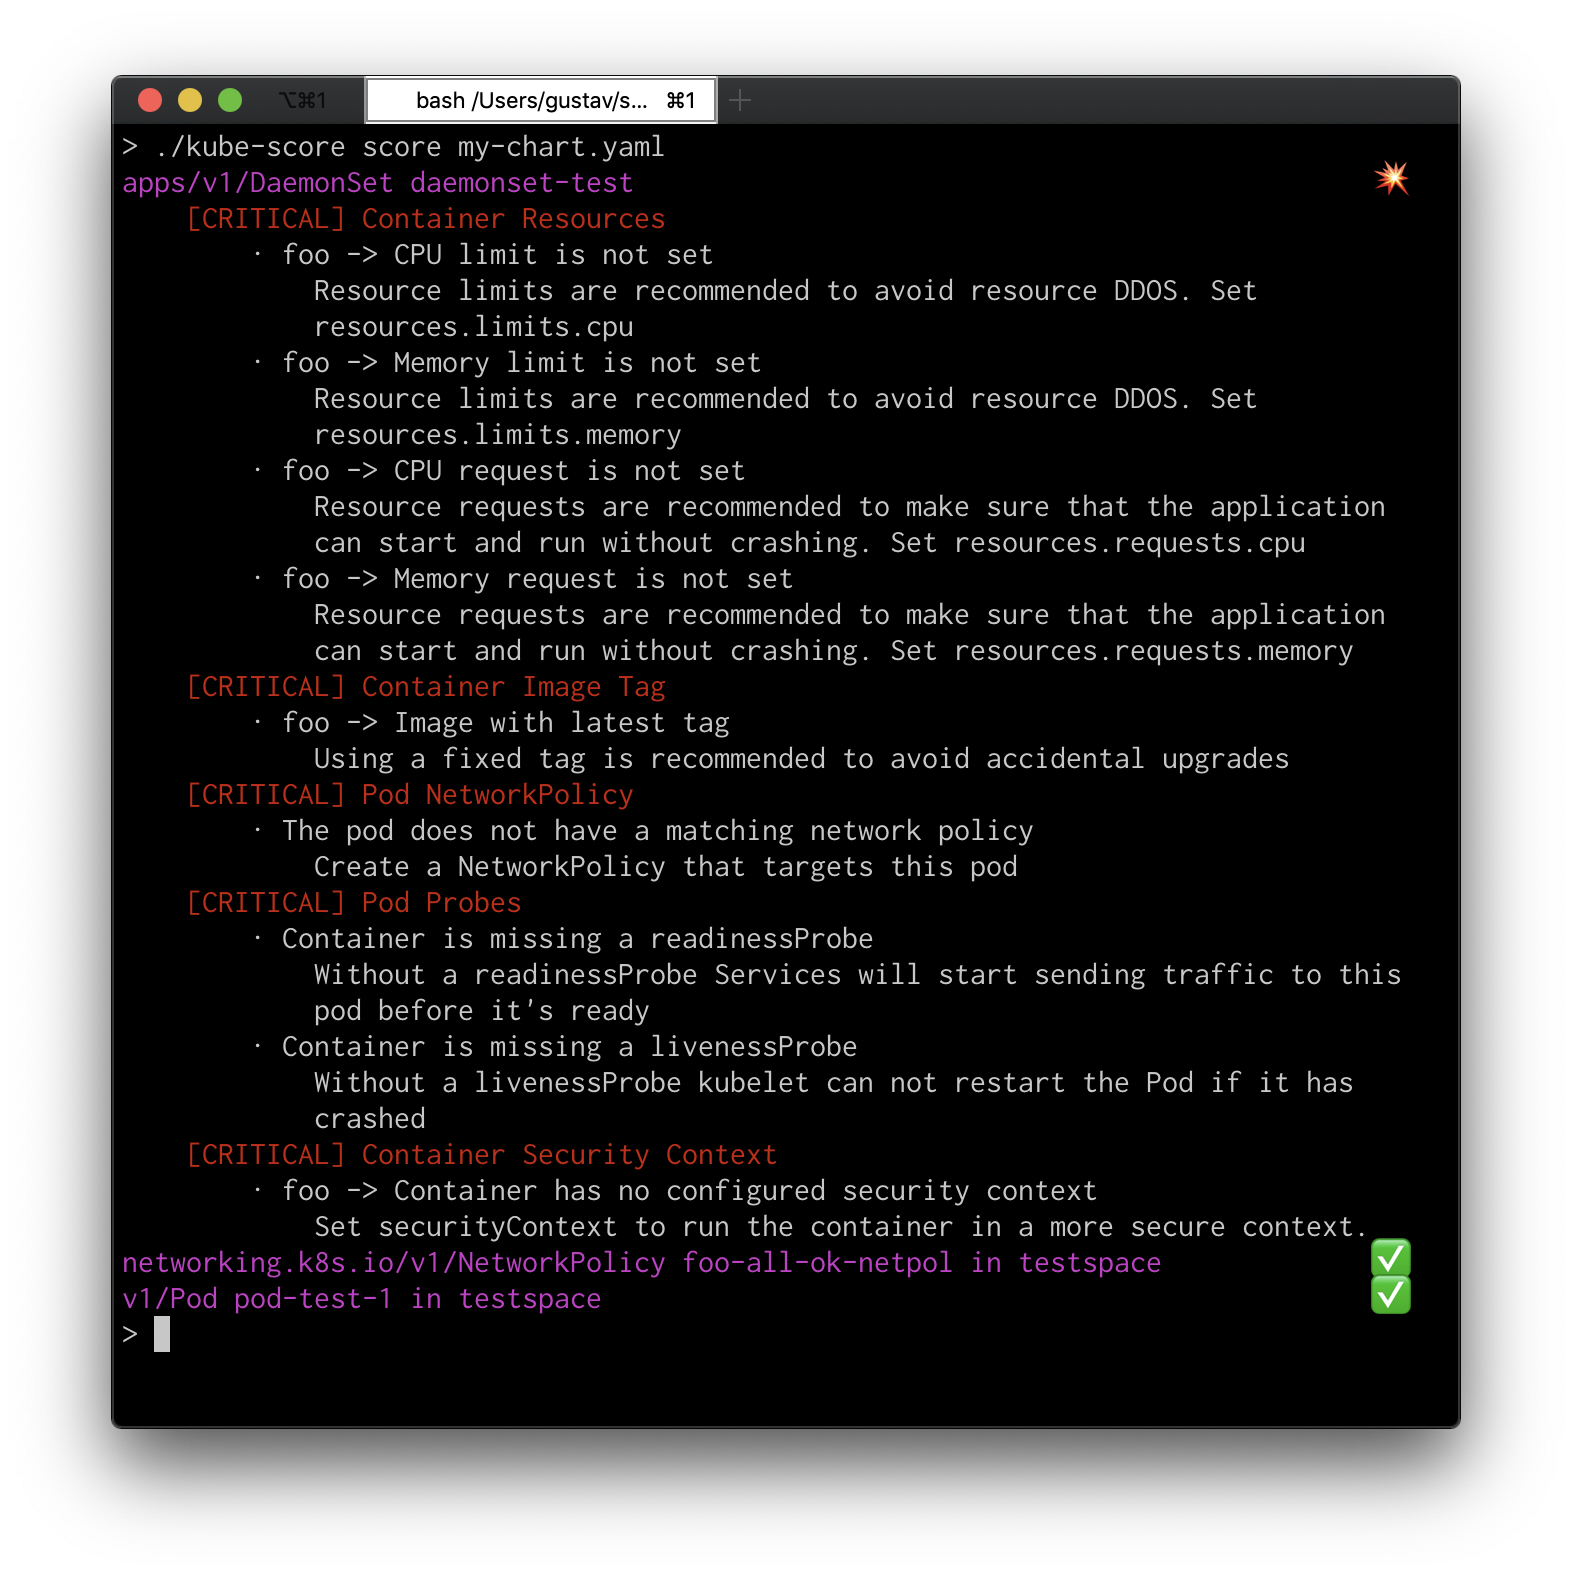 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
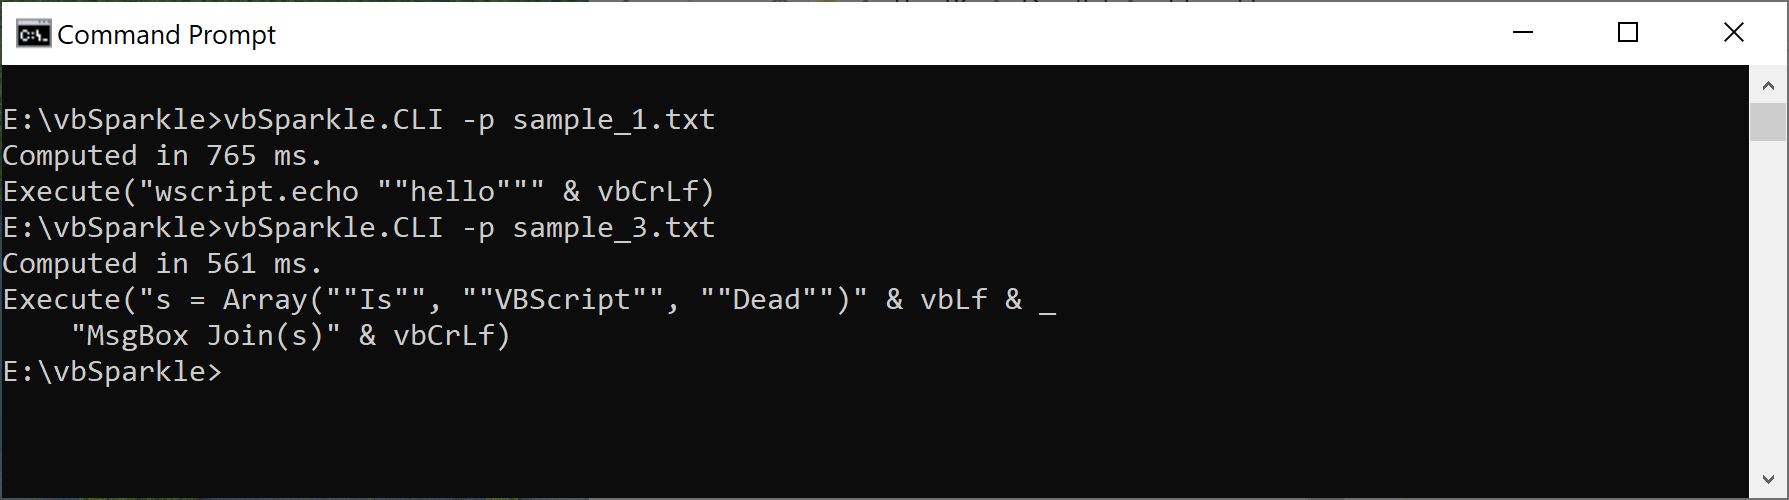 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 vusec/ghostrace
Proof-of-concept and static analysis toolkit for finding speculative race condition (SCUAF) gadgets in Linux kernel. Includes 1200+ gadget dataset.
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.