

security-harness
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
ai-securitycode-analysisdevsecops+9
40
dmdhrumilmistry/security-harnessMulti-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
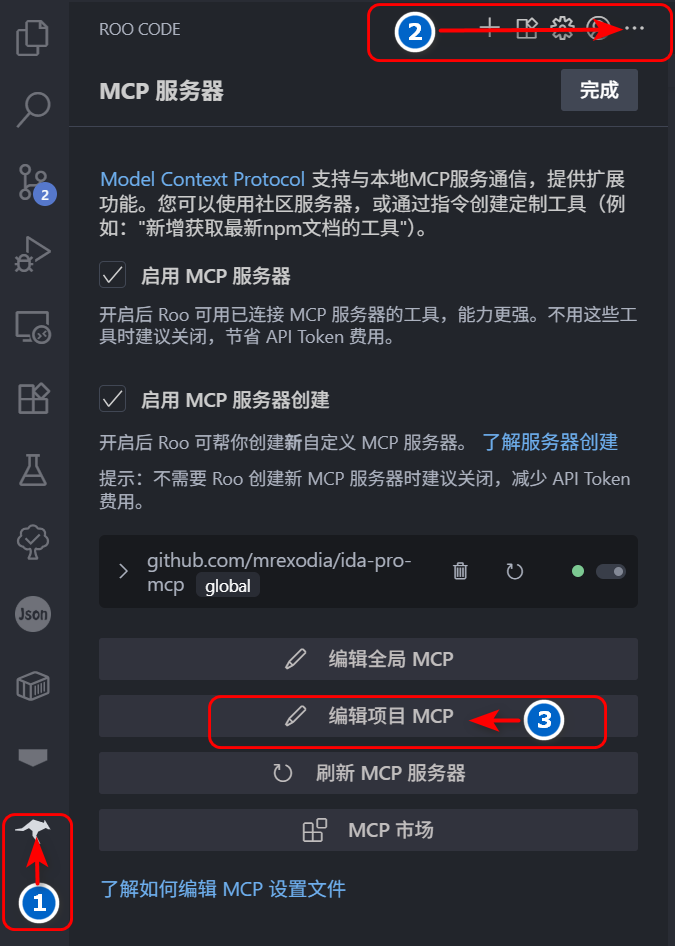 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 owasp/riskassessmentframework
The Secure Coding Framework
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 tenable/terrascan
Detect compliance and security violations across Infrastructure as Code to mitigate risk before provisioning cloud native infrastructure.
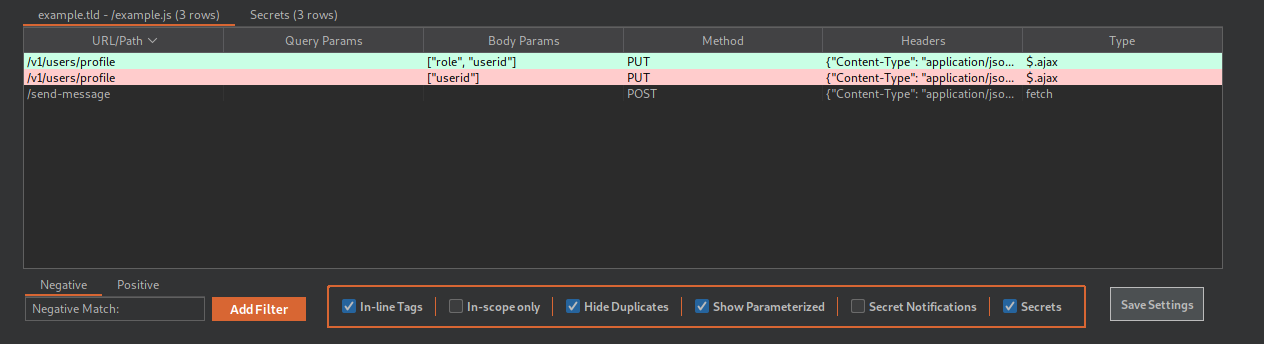 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 samsung/utopia
UT based automated fuzz driver generation