security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…

Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…

AI-powered bug bounty hunting toolkit that works with or without subscription.

Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…

Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…

Bandit is a tool designed to find common security issues in Python code.

RAM efficient terminal agent harness for coding, cybersecurity, and automation.

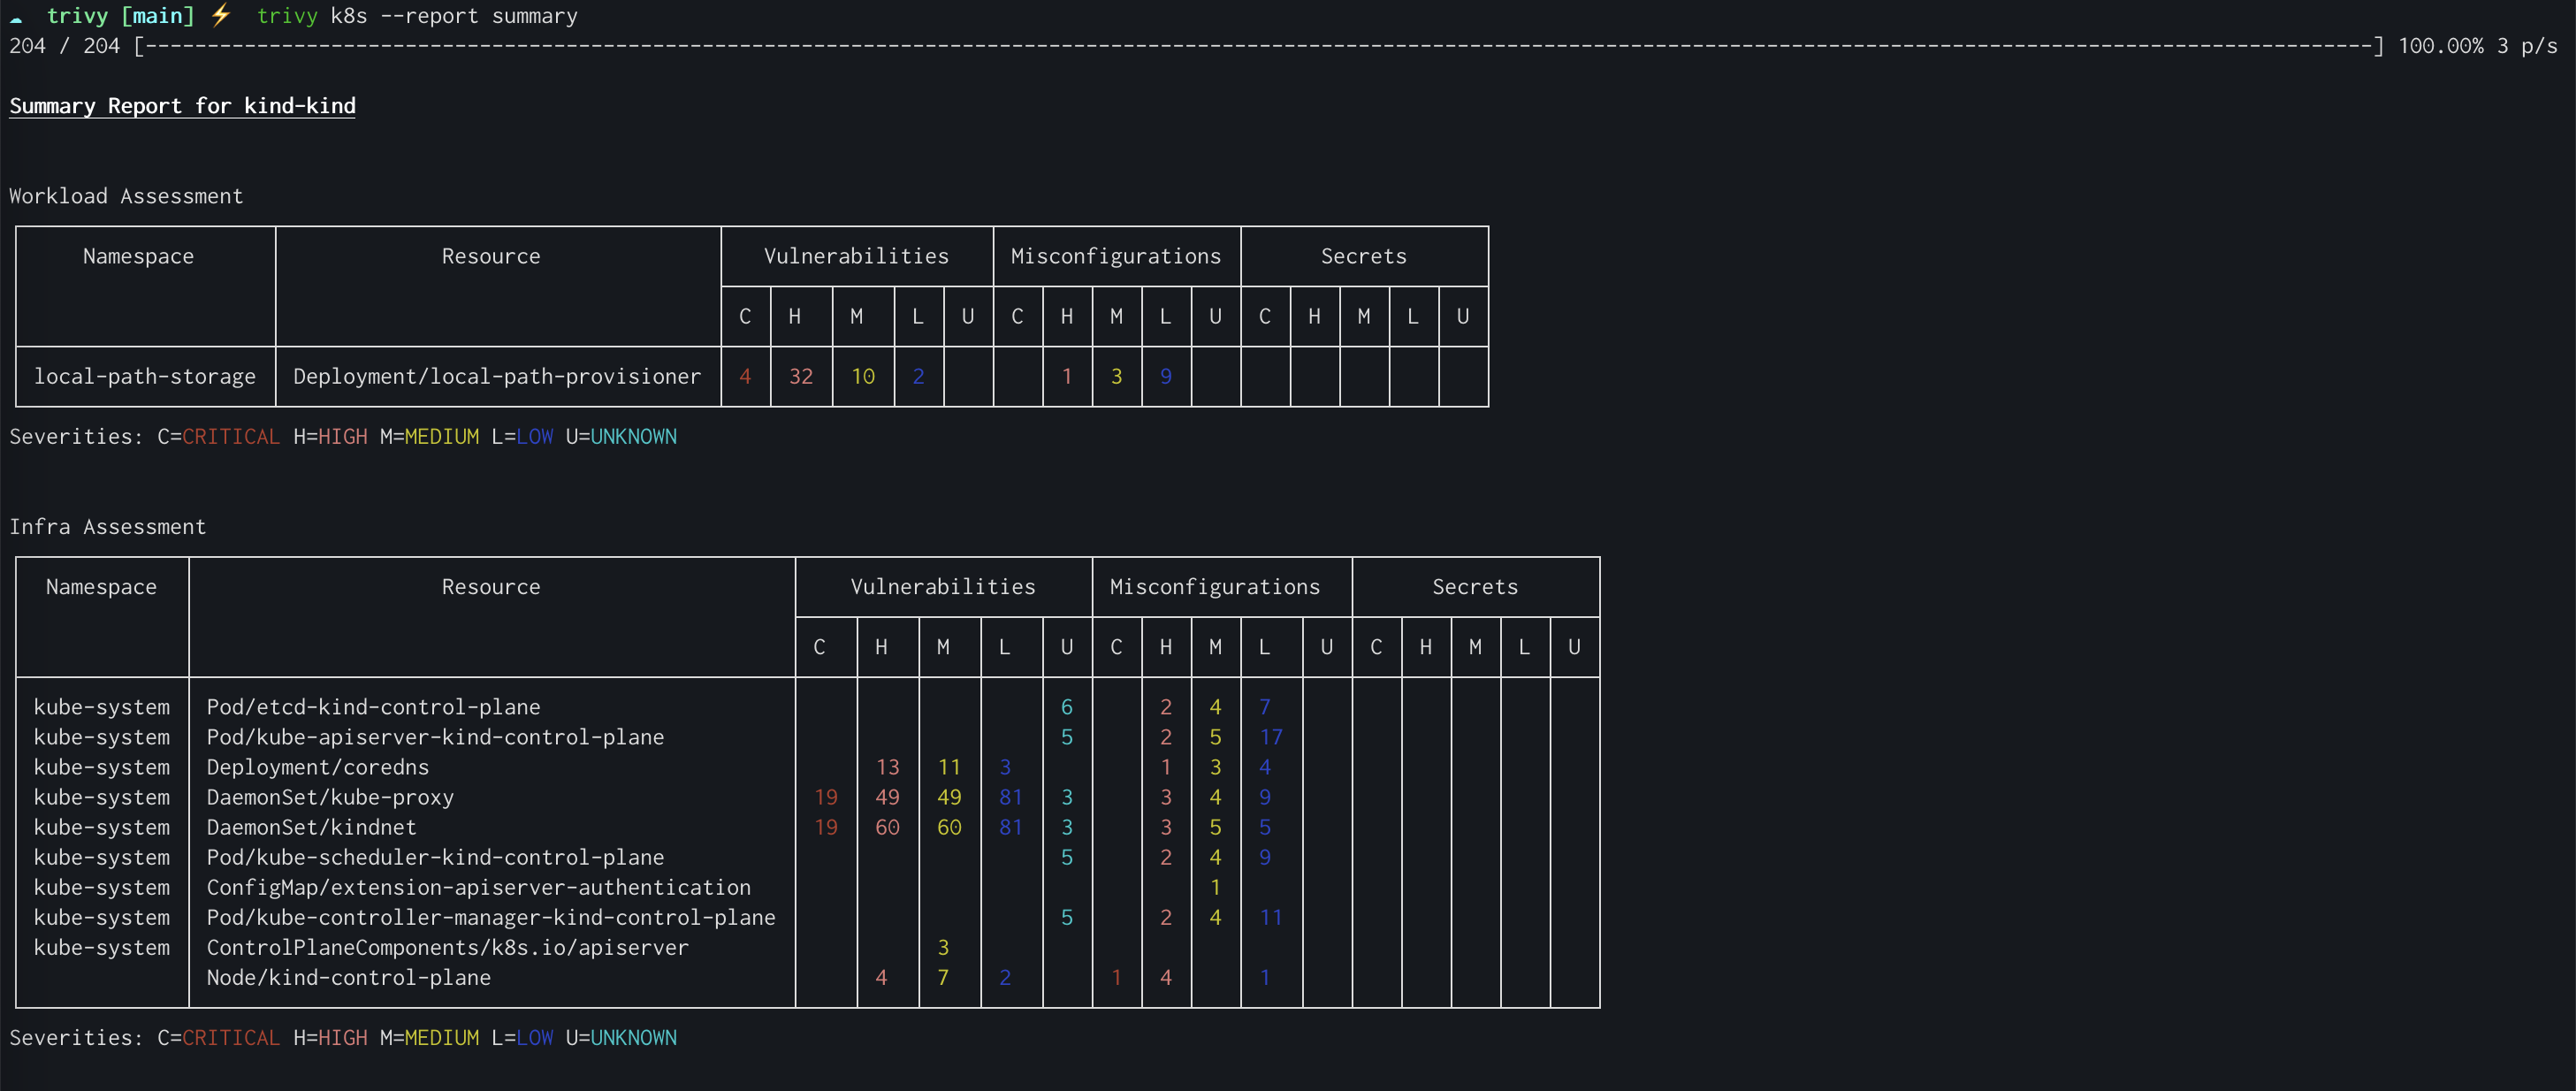
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more

find hardcoded strings from source code

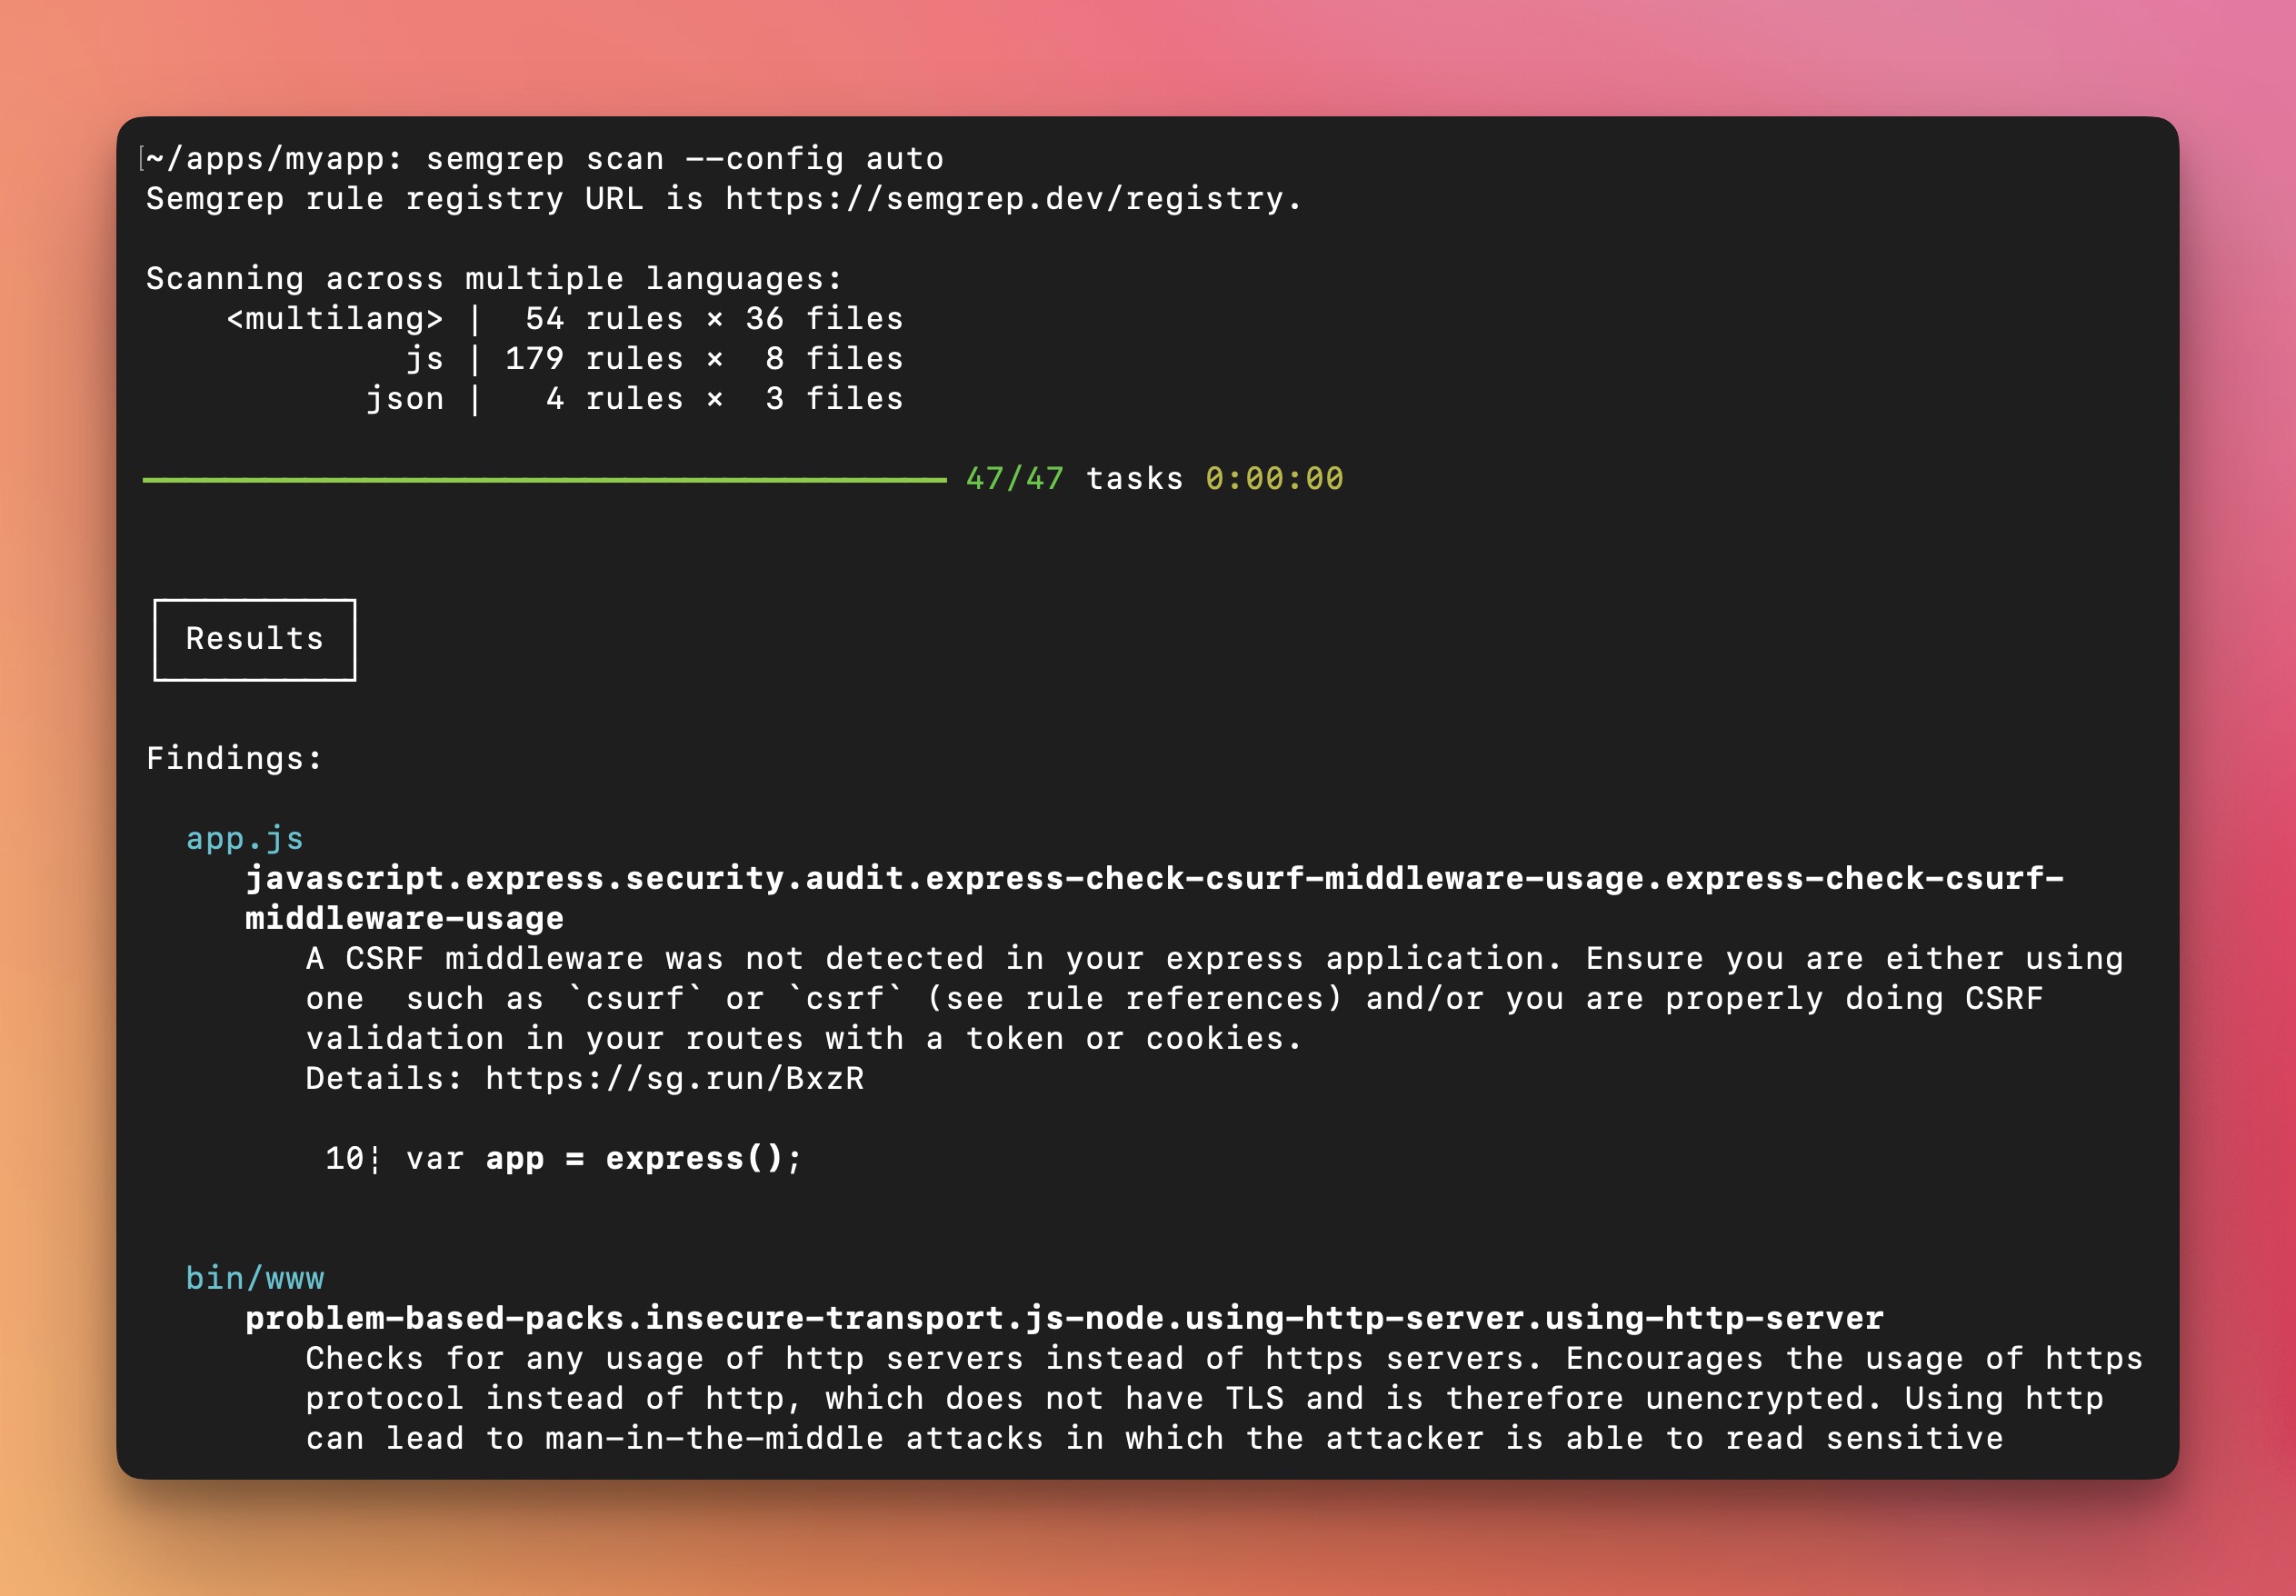
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…

Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits

Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…

Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…

Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…

Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.

OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…

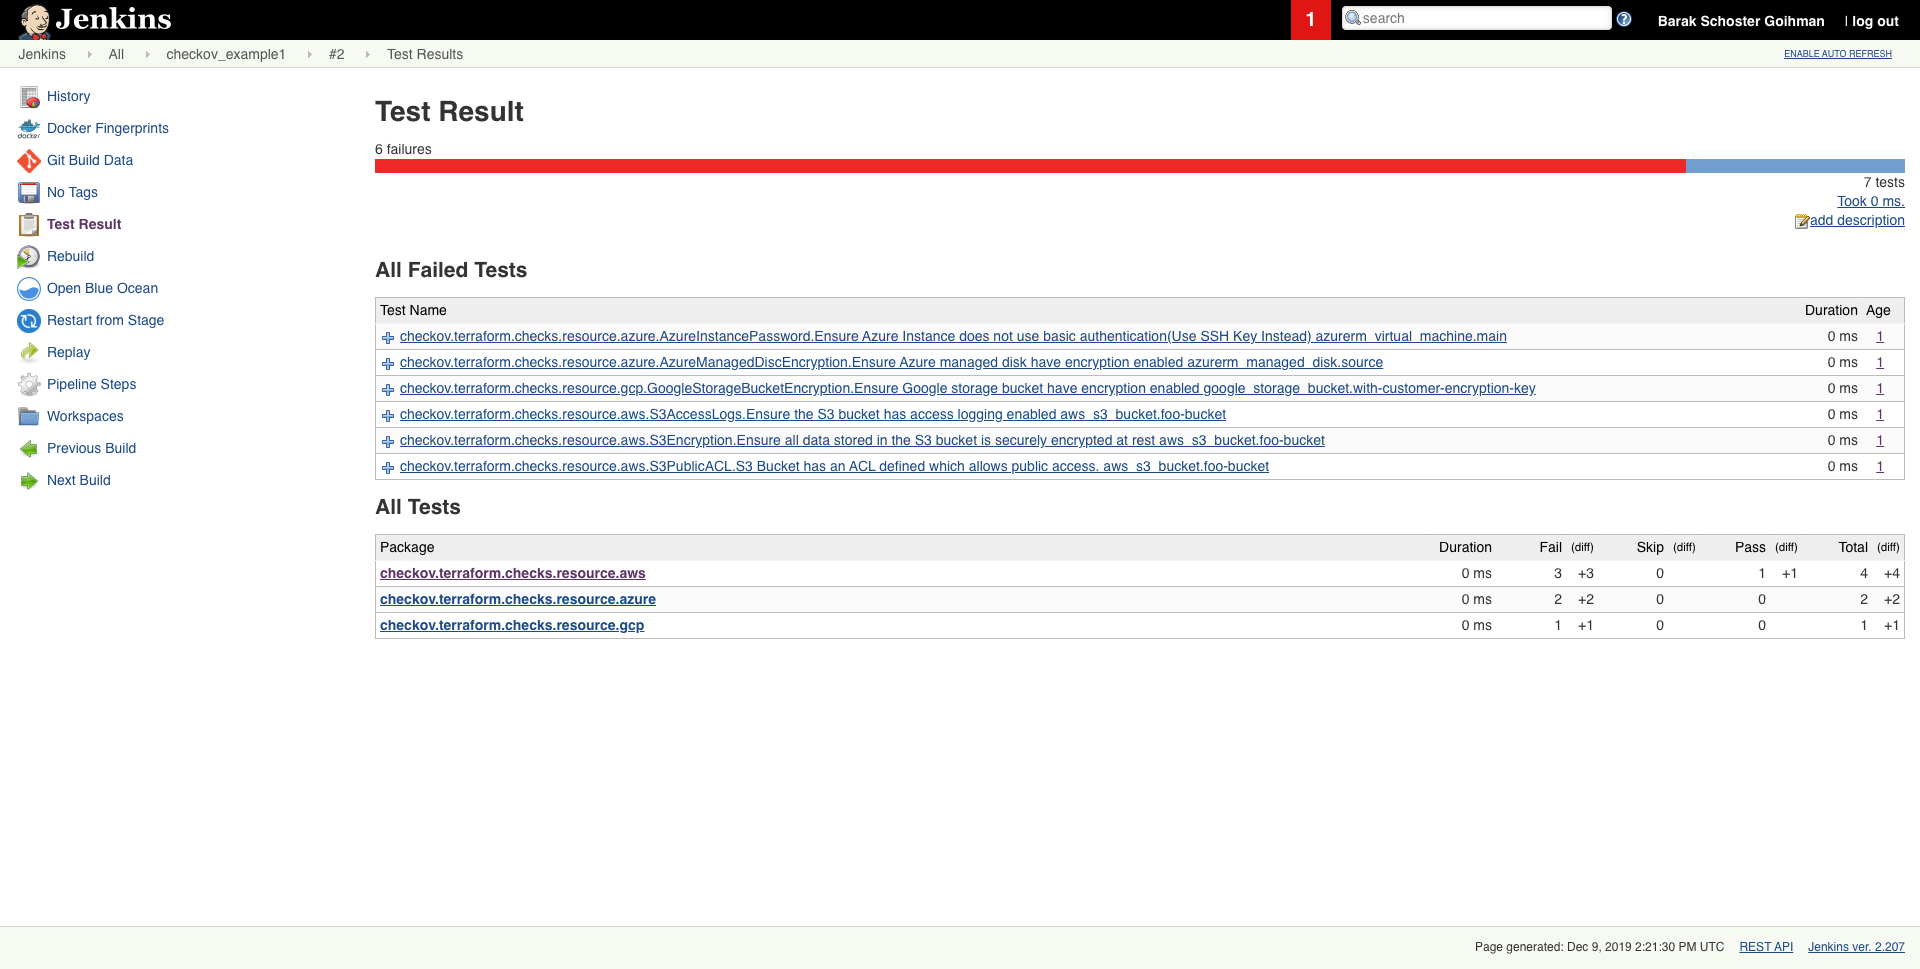
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…