
sudowp-dropzone-elementor
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
api-securitycode-analysismisconfiguration+3
sudo-wp/sudowp-dropzone-elementorSecure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 josue87/wp_hunter
Static analysis of wordpress plugins
 47cid/wp2shell-lab
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion
 aquasecurity/trivy-module-wordpress
Trivy example module for WordPress
 bytespulse-oe/wp2shell-hestia-scanner
Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…
 chpratik/cve-2026-9830
Threat intelligence report repository for CVE-2026-9830, an authentication bypass vulnerability in BookingPress Pro WordPress plugin, with detailed…
 svtagan/wp-cve-2026-87902
Read-only PHP diagnostic script that checks WordPress version, core checksums, extra PHP files, and known plugin paths for CVE-2026-87902 exposure…
 sudotom/rcno-reviews
Recencio Book Reviews - WordPress plugin for managing book reviews. Originally created by Kemory Grubb. Security-patched fork resolving…
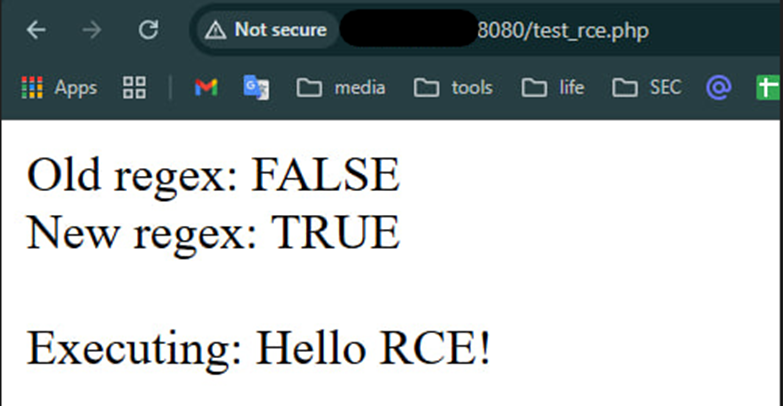 soltanali0/cve-2024-12877-exploit
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…