
class-dump
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
binary-analysisios-securityreverse-engineering+1
nygard/class-dumpGenerate Objective-C headers from Mach-O files.
 tylabs/qs_old
Command line tool for scanning streams within office documents plus xor db attack
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 spamscanner/spamscanner
Spam Scanner is a Node.js anti-spam, email filtering, and phishing prevention tool and service. Built for @ladjs, @forwardemail, @cabinjs, @breejs,…
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
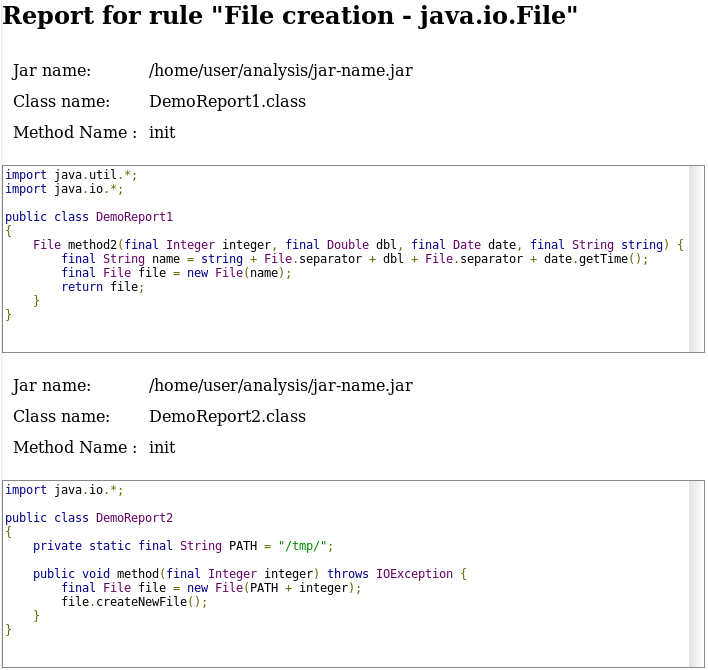 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules
 0x11dfe/file-unpumper
Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
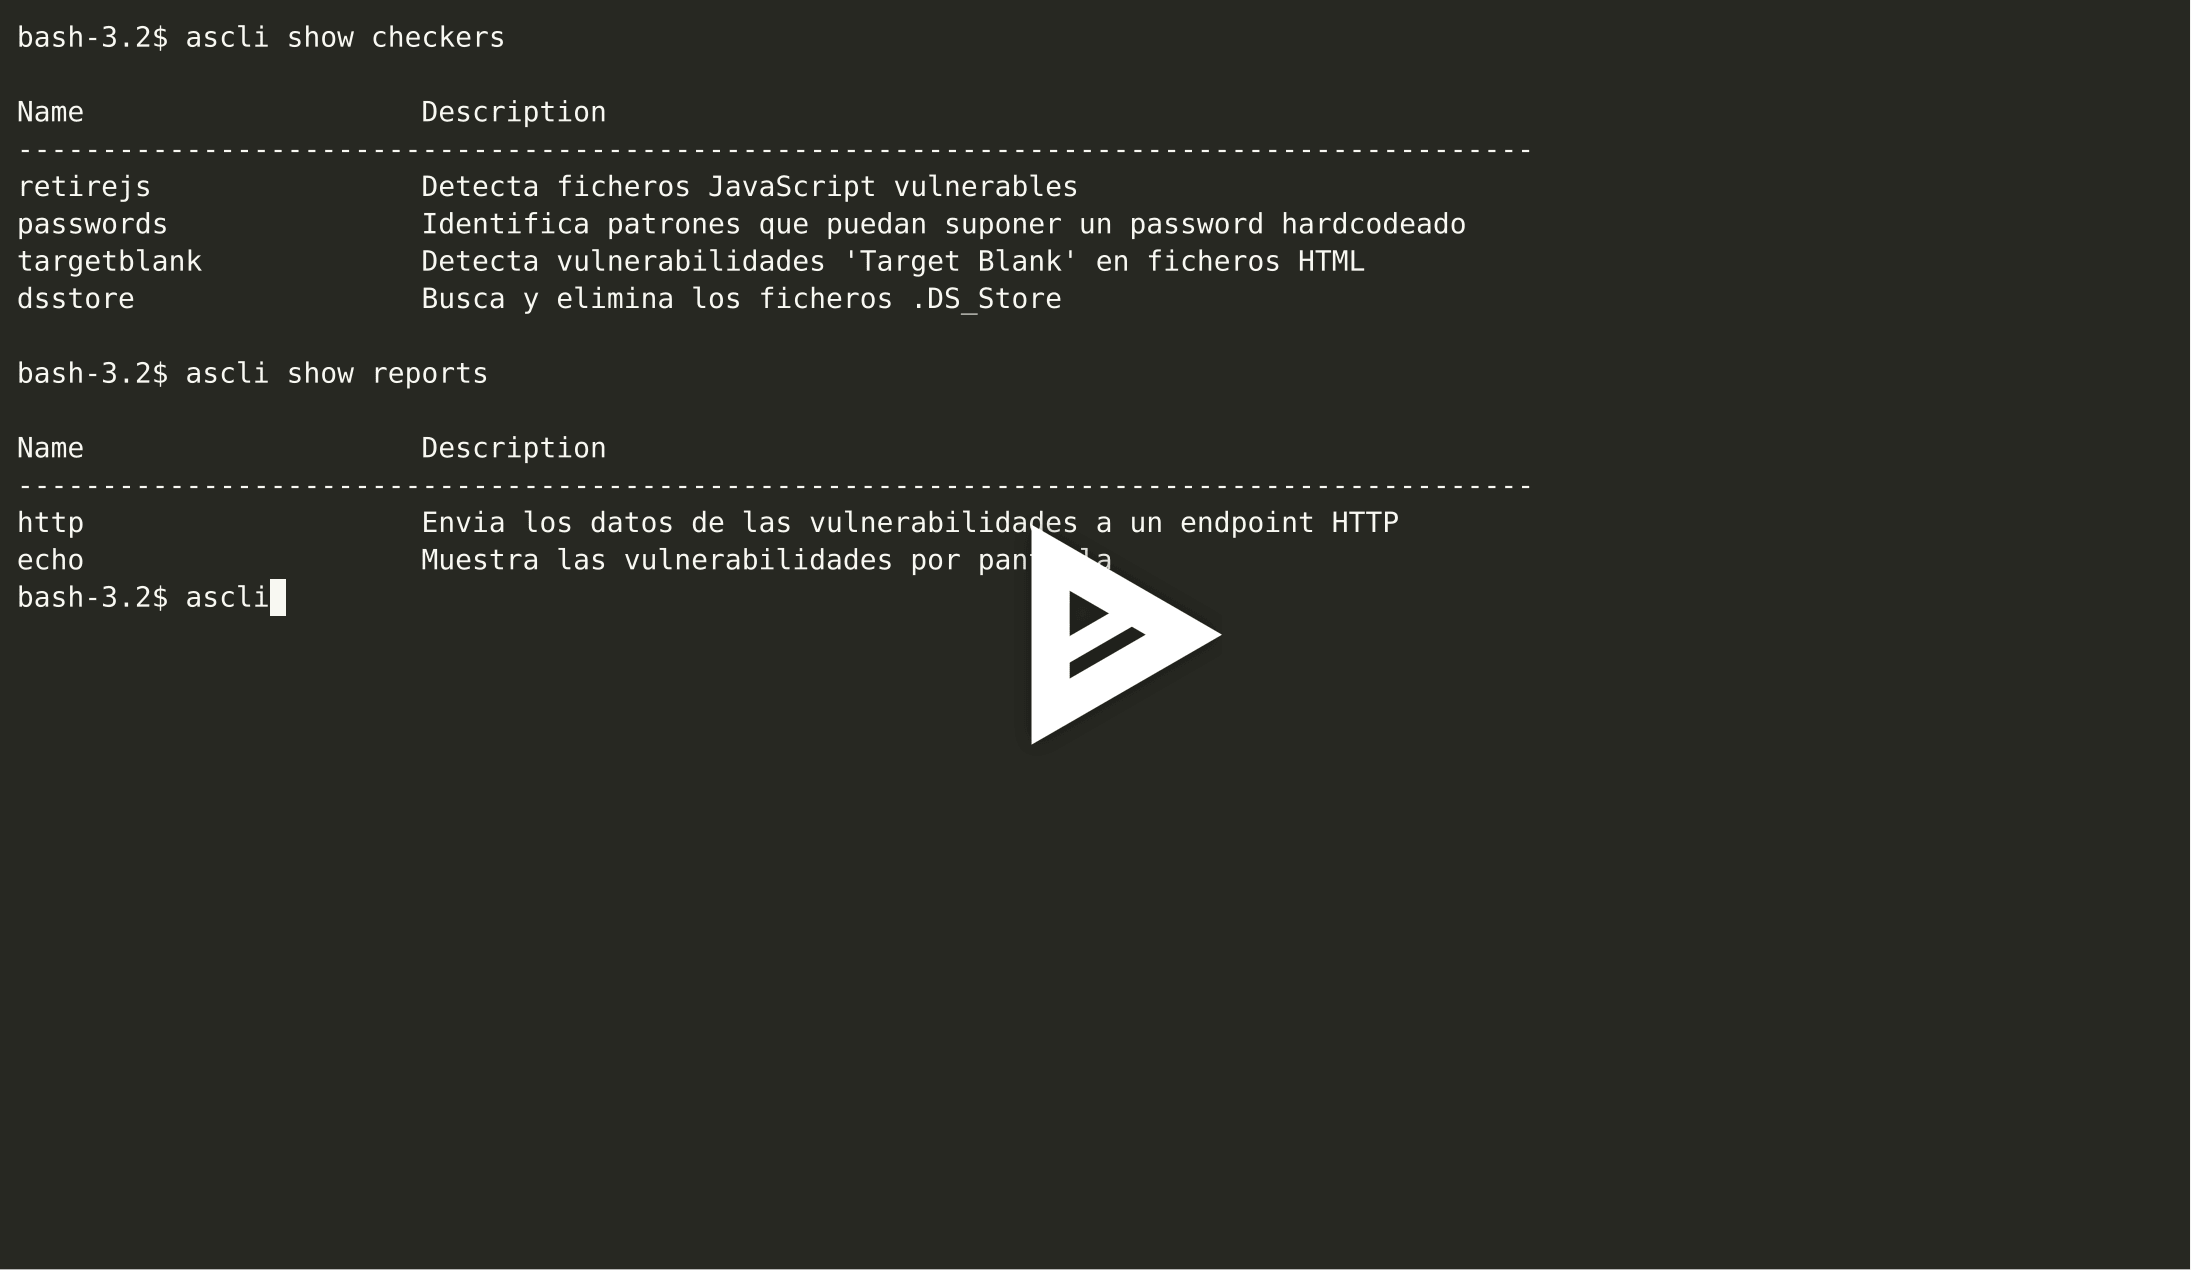 elevenpaths/atomshields-cli
CLI for AtomShields static analysis scanner. Install, uninstall, and run checkers and reports to detect vulnerabilities in source code projects.
 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 fauxrougee/smartscanner-source
Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 superandroidanalyzer/super
Secure, Unified, Powerful and Extensible Rust Android Analyzer
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework