
xfg_analyzer
 ea/xfg_analyzer
A Binary Ninja plugin that uses bruteforced XFG hashes to recover precise function prototypes
binary-analysisreverse-engineeringstatic-analysis
ea/xfg_analyzerA Binary Ninja plugin that uses bruteforced XFG hashes to recover precise function prototypes
 myrtus0x0/smoke_conf_extract
Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.
 synacktiv/pridelocker-analysis
This repository contains a IDA Python script to recover PrideLocker ESX encryptor strings and a YARA rule
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
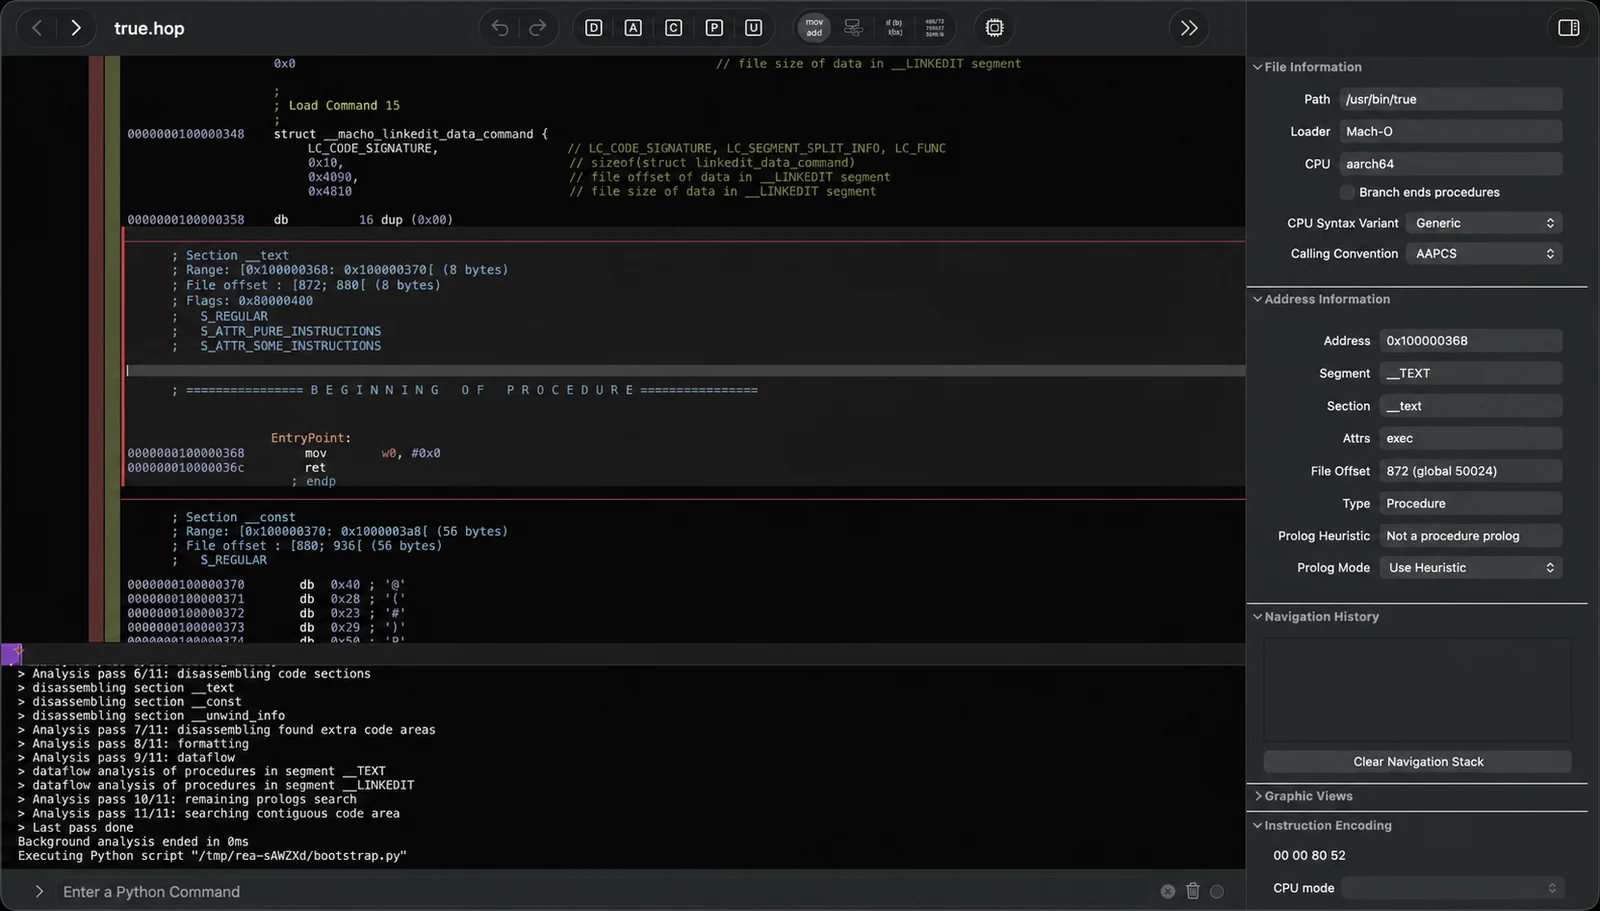 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
