

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.7k8 days ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
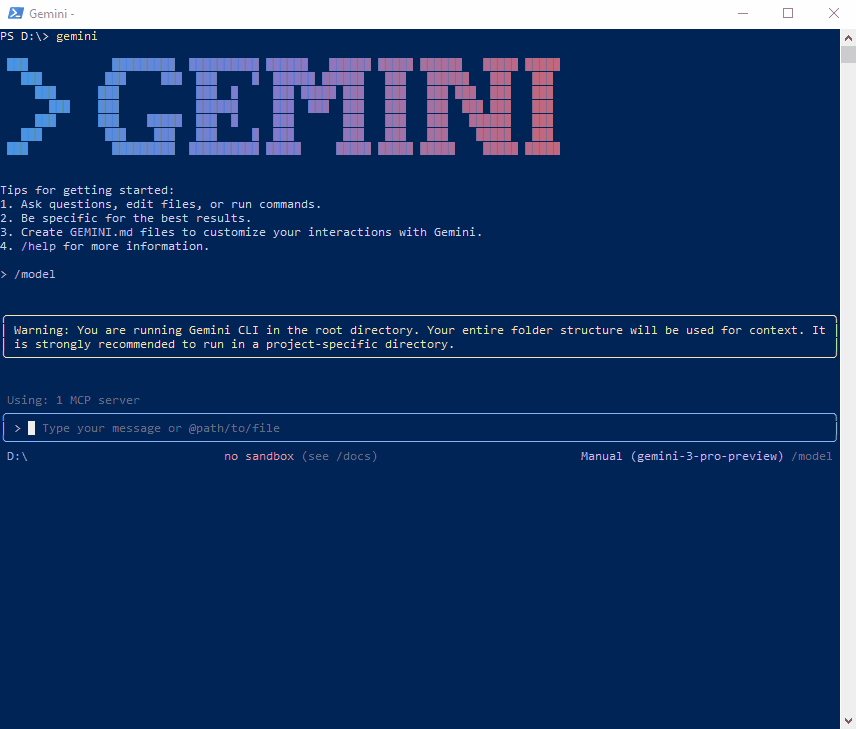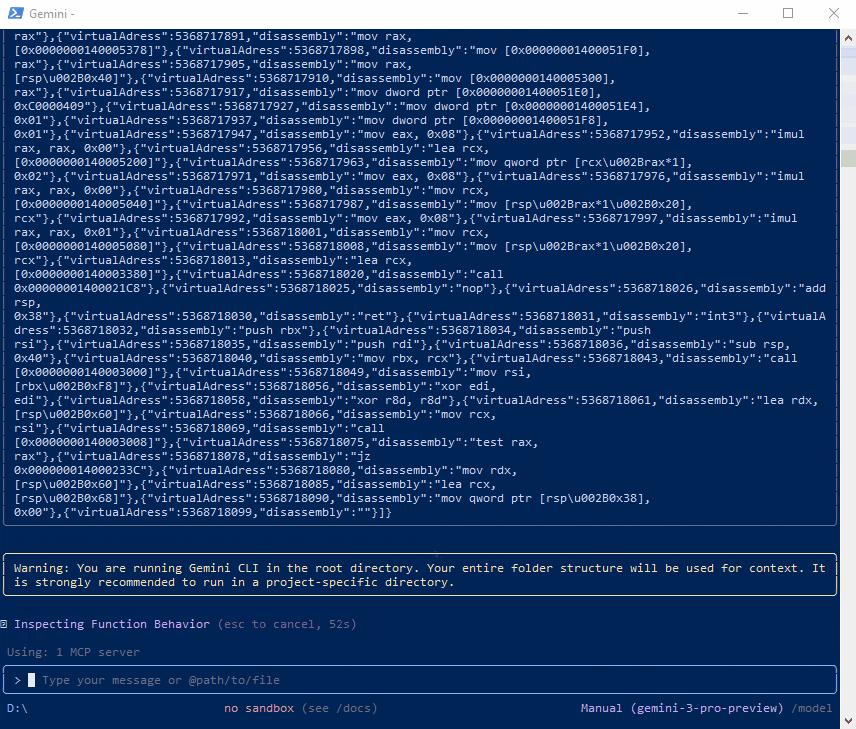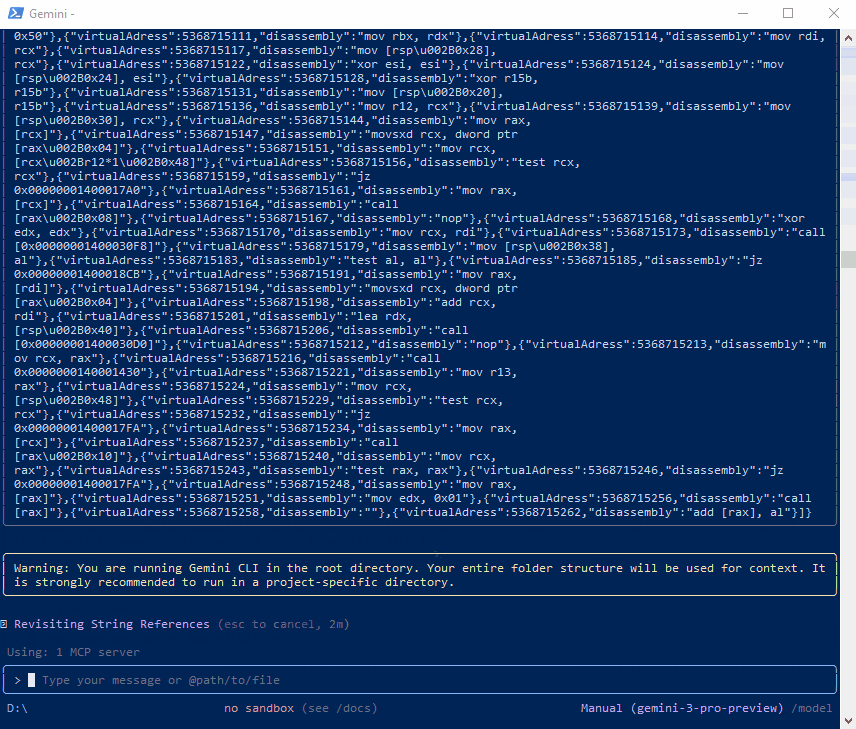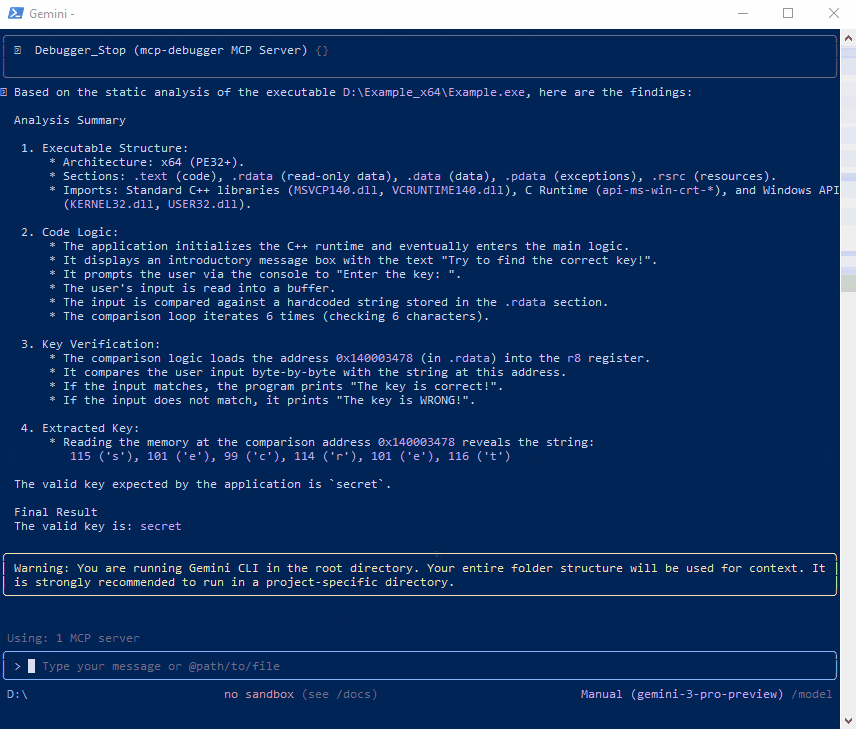 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
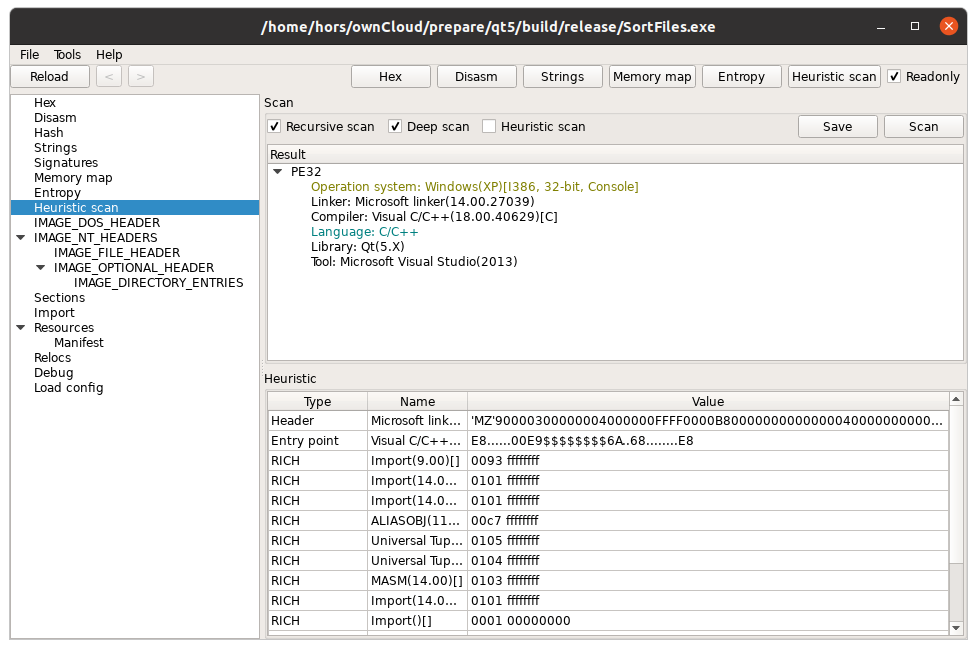 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
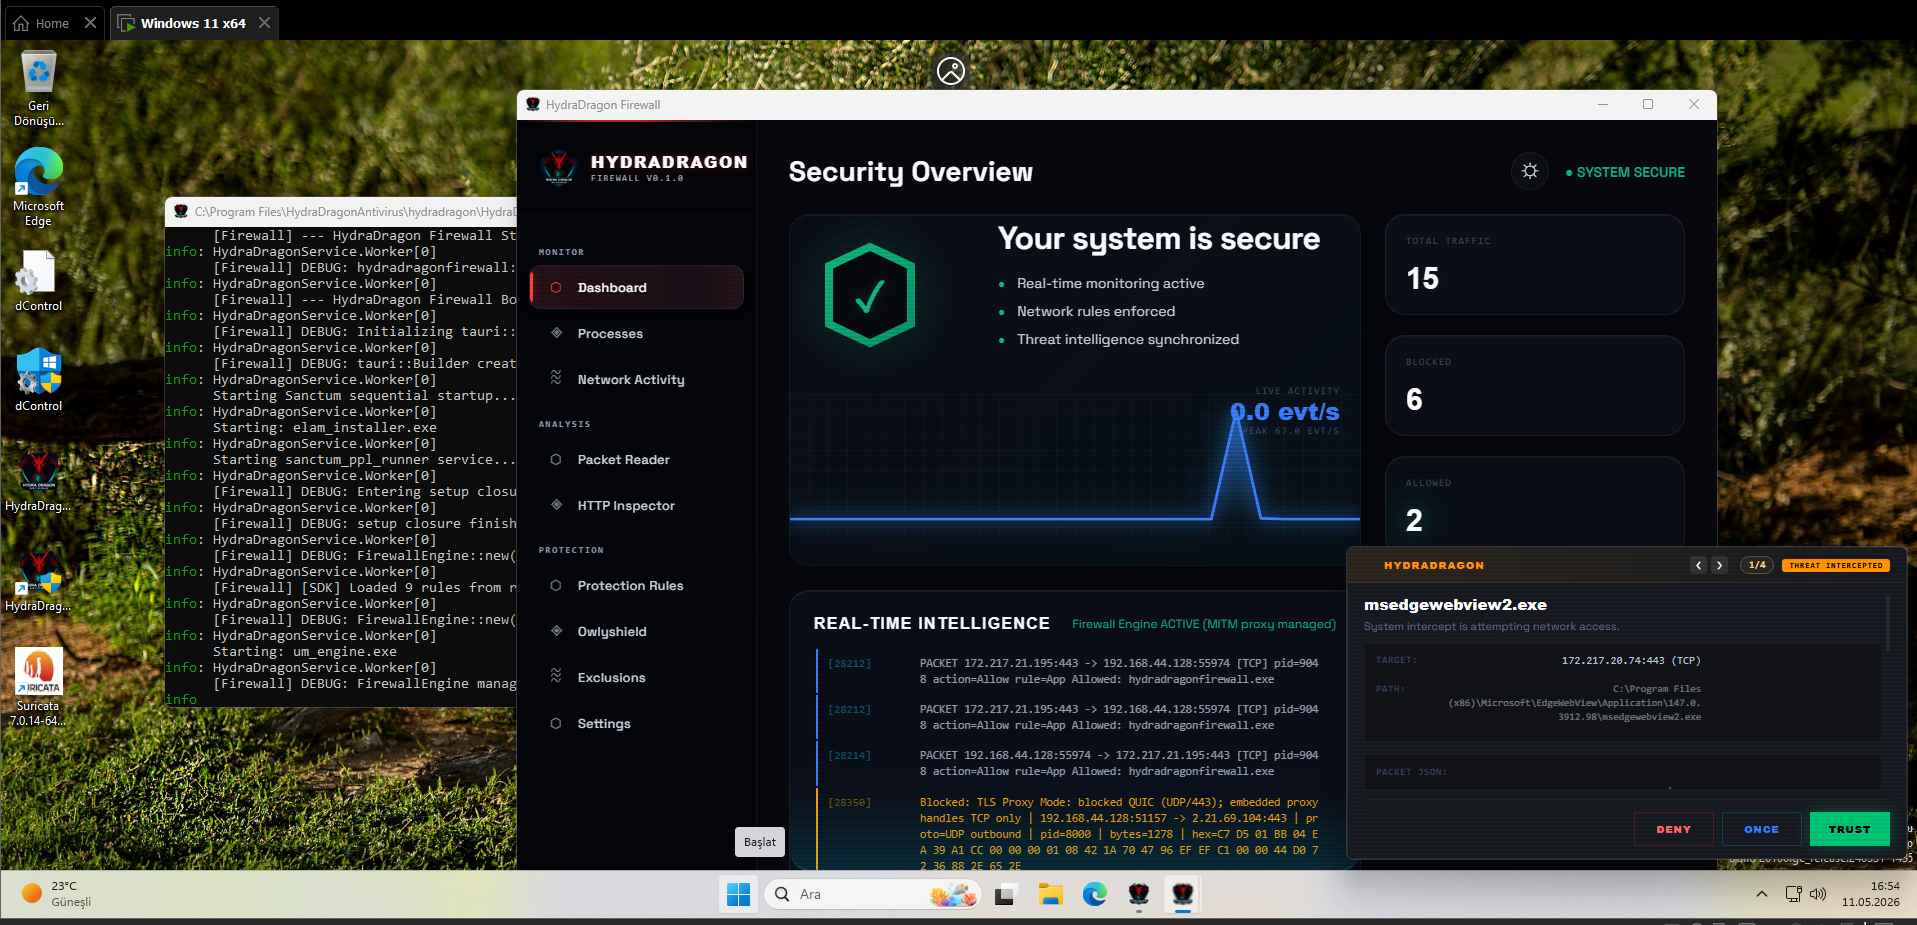 hydradragonantivirus/hydradragonantivirus
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
 lilify-jp/squre
🛡️ Open-source binary protection toolkit for Windows PE. Nanomite, VM protection, anti-debug, and more.
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
 sec-consult/msiscan
Scanning tool for identifying local privilege escalation issues in vulnerable MSI installers
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 santhreal/keyhog
Open-source secret scanner in Rust