
Archived
halogen
 target/halogen
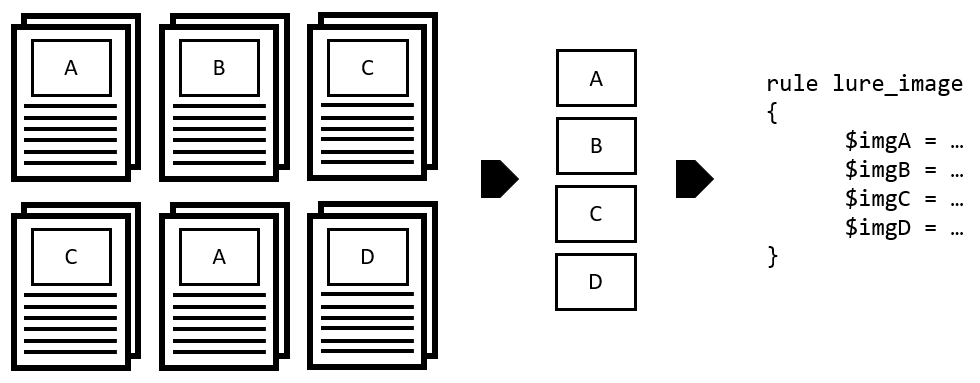
Automatically create YARA rules from malicious documents.
forensicsincident-responsemalware-analysis+2
210
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
 malpedia/malpedia-flossed
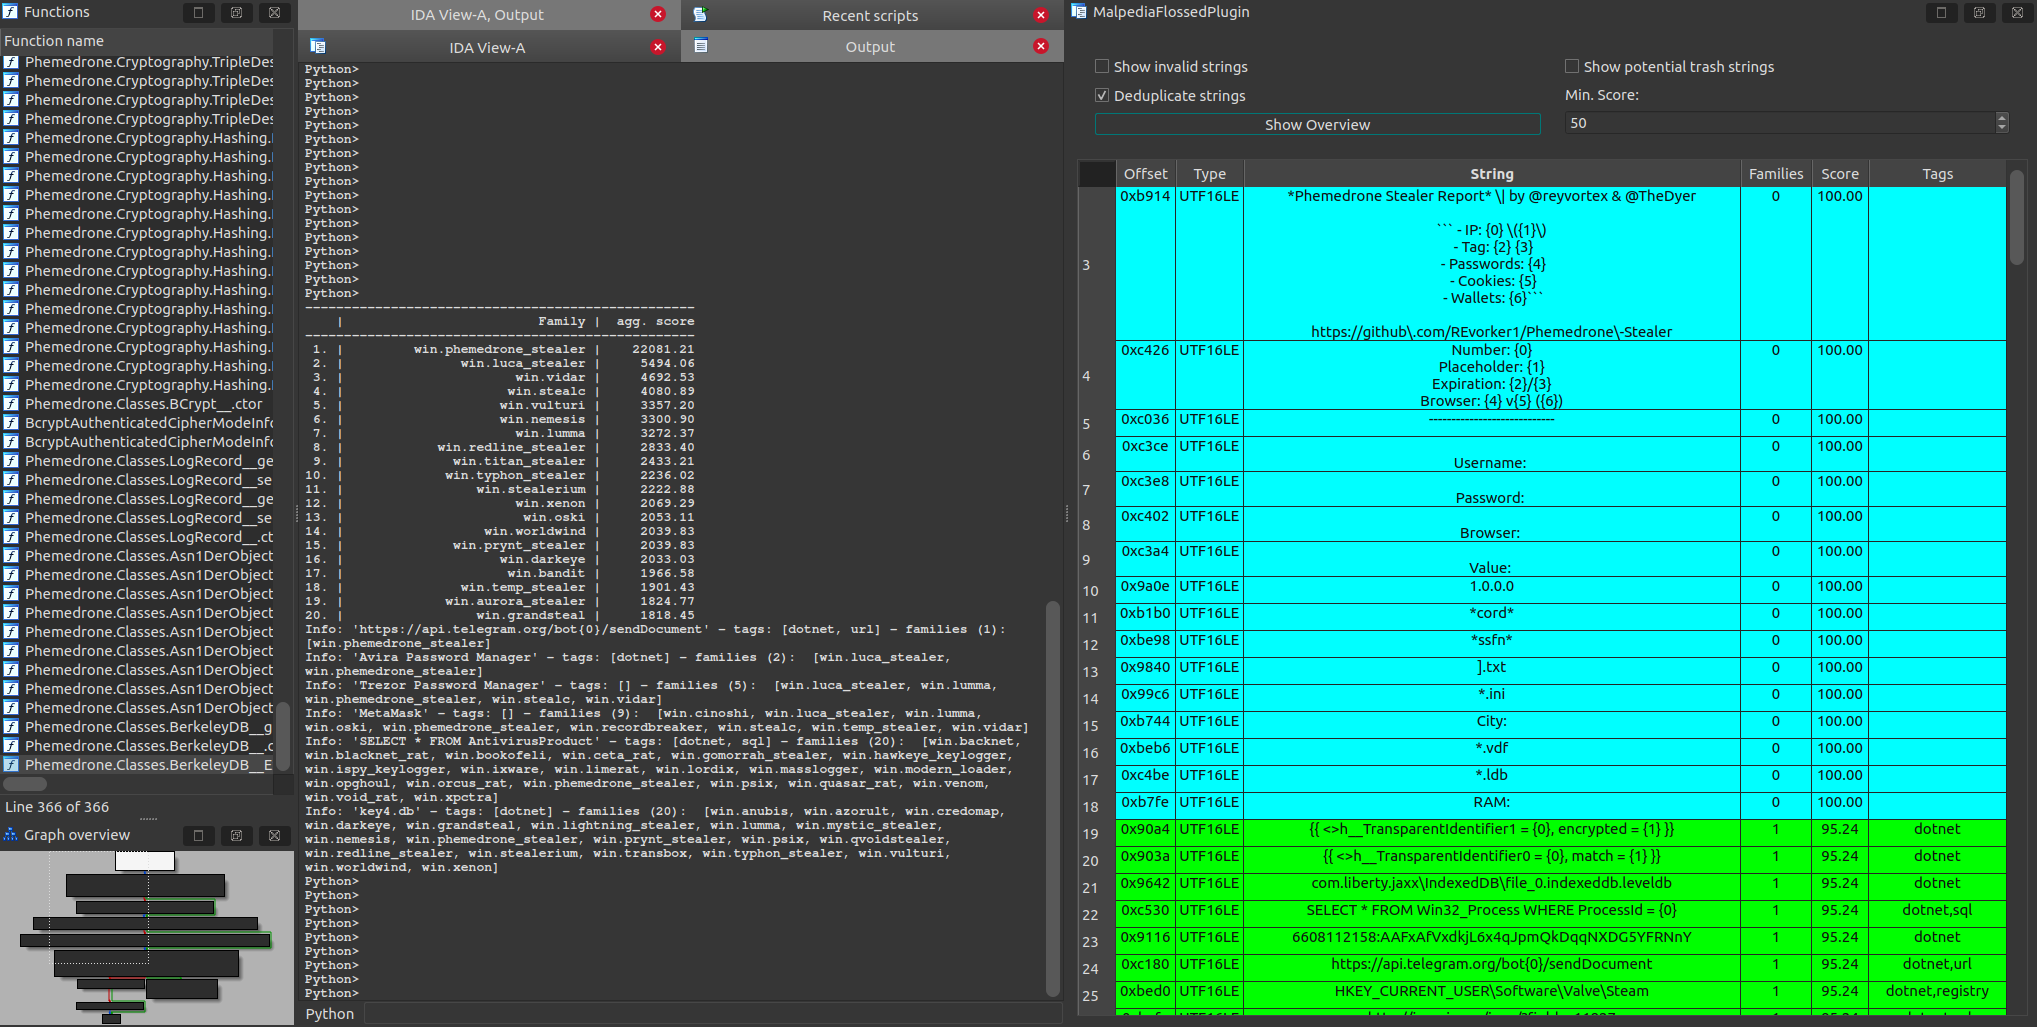
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
 notsosecure/android_application_analyzer
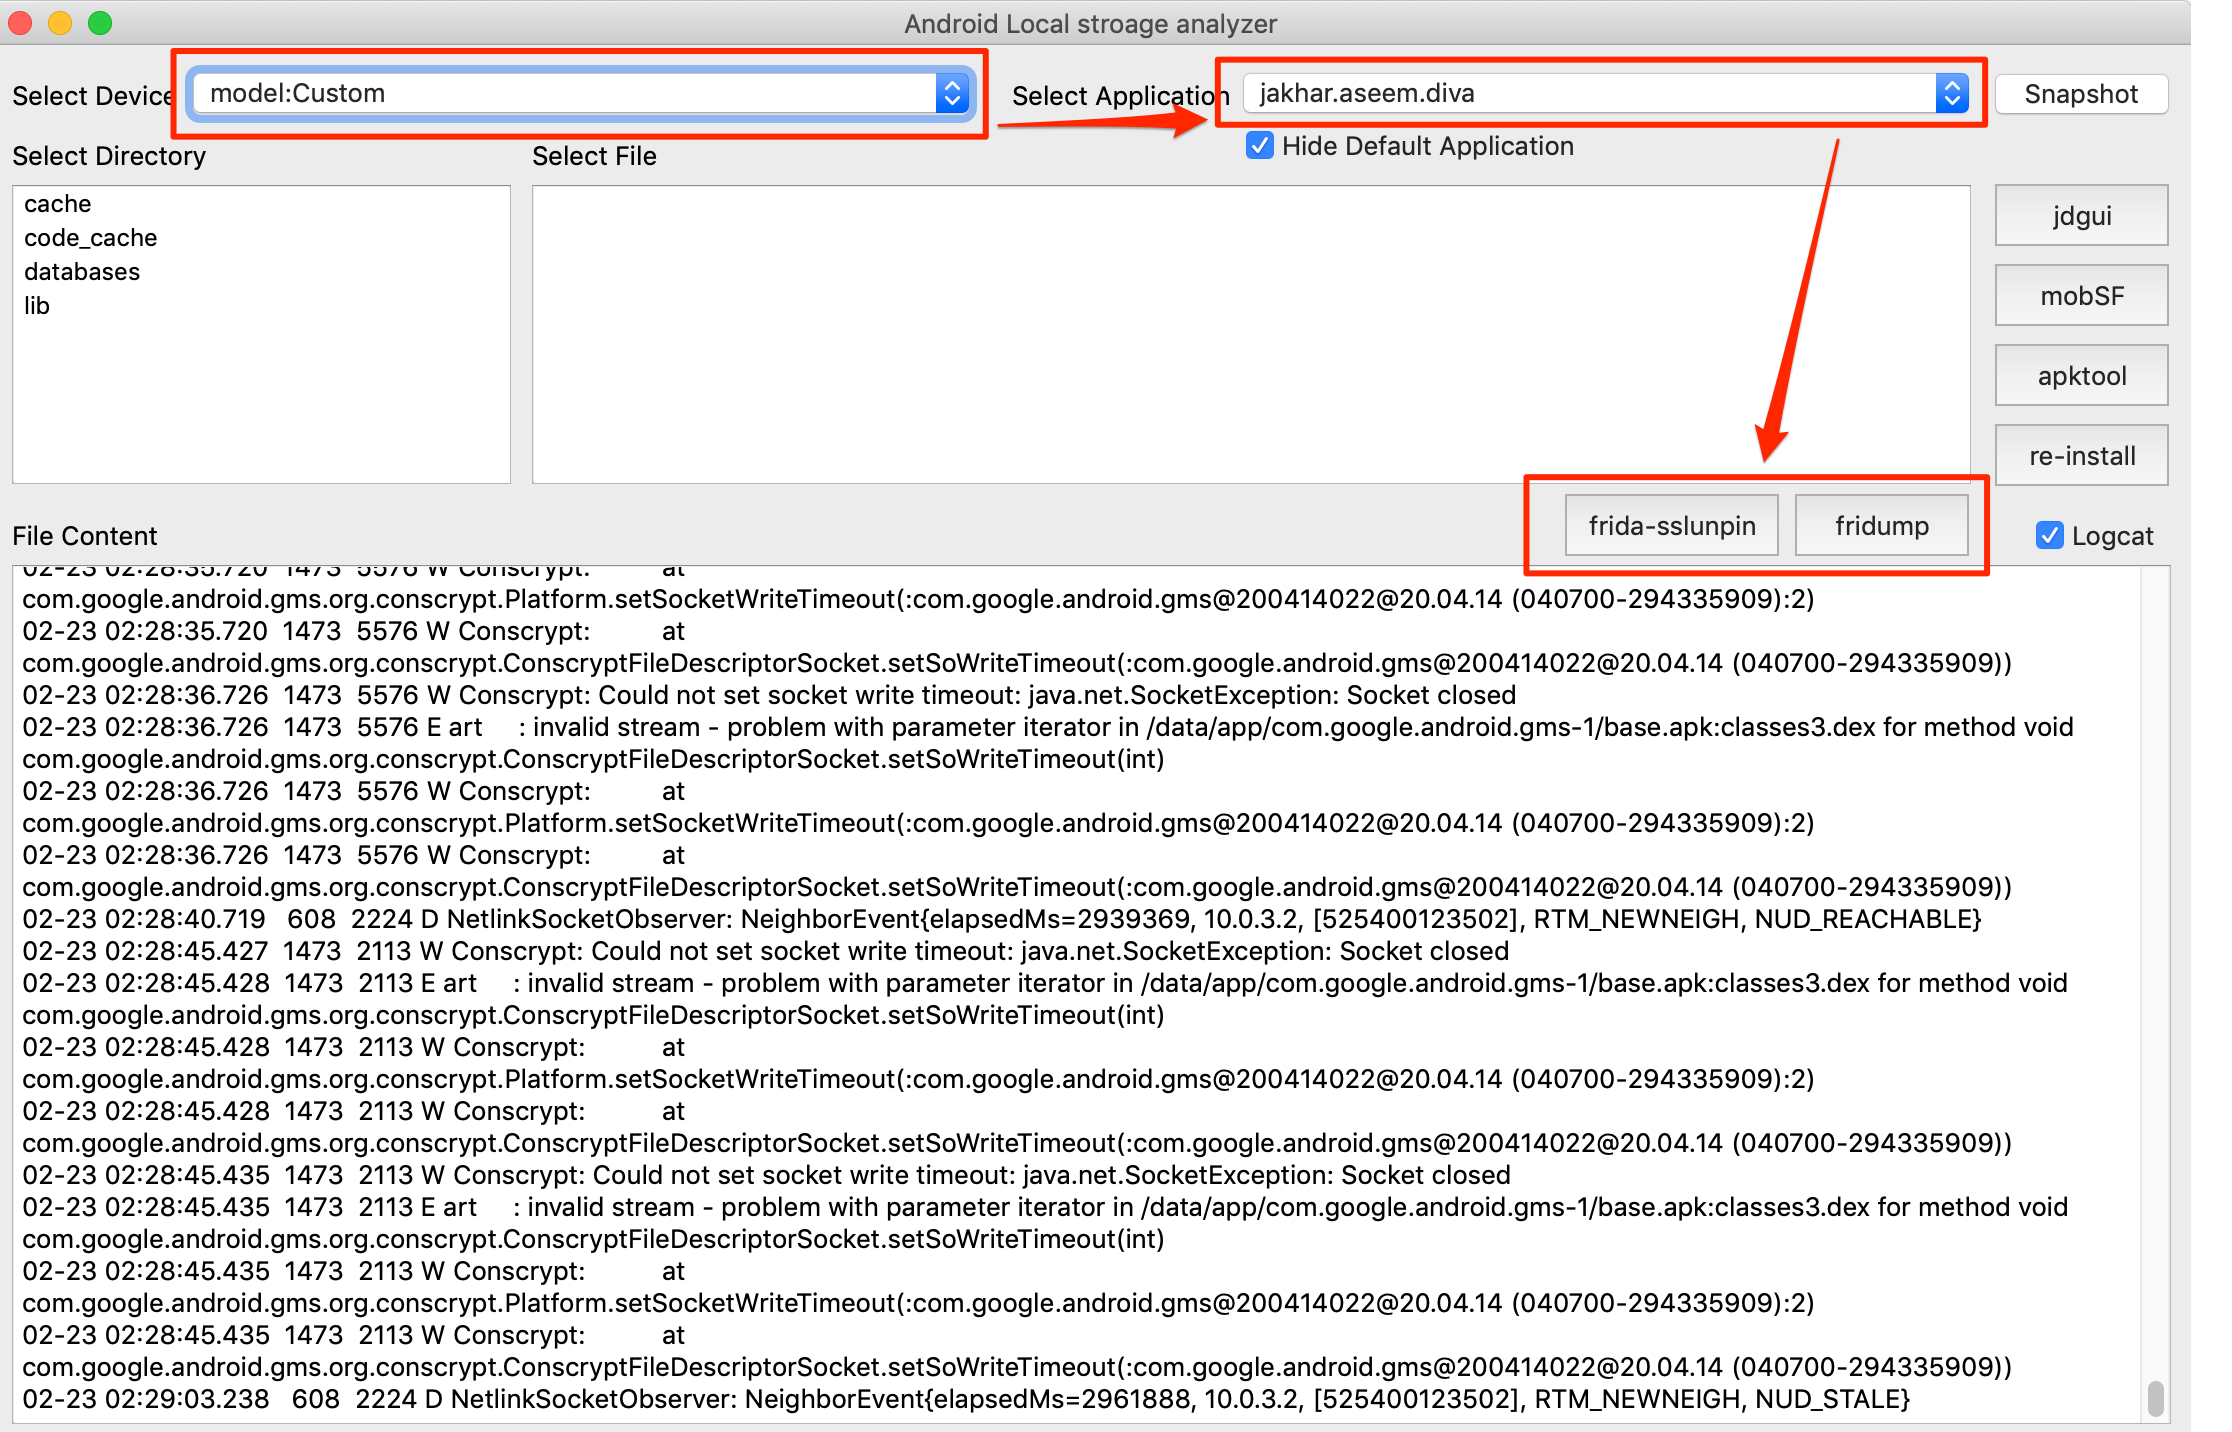
The tool is used to analyze the content of the android application in local storage.
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
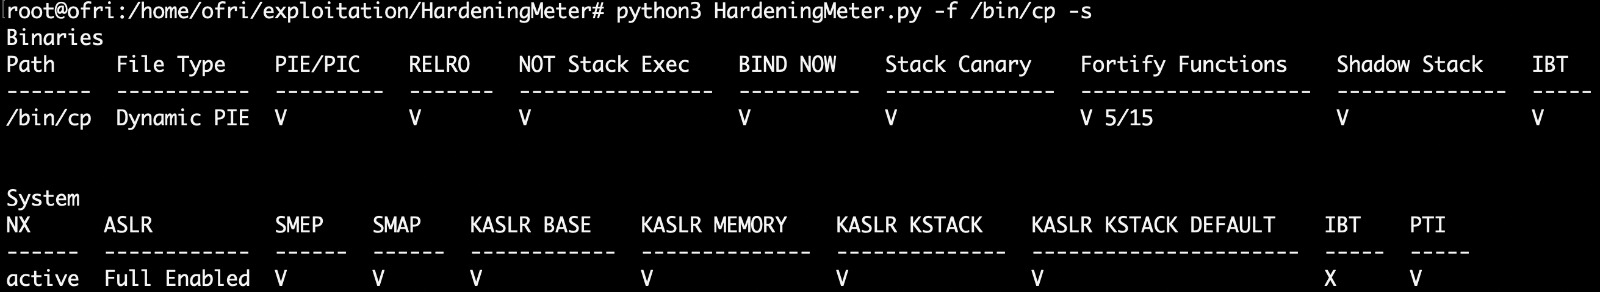 ofriouzan/hardeningmeter
HardeningMeter is an open-source Python tool carefully designed to comprehensively assess the security hardening of binaries and systems.
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 foxirain/linux-kernel-codex-harness-v2
Provenance-aware Linux kernel vulnerability research harness used in the investigation of CVE-2026-53075
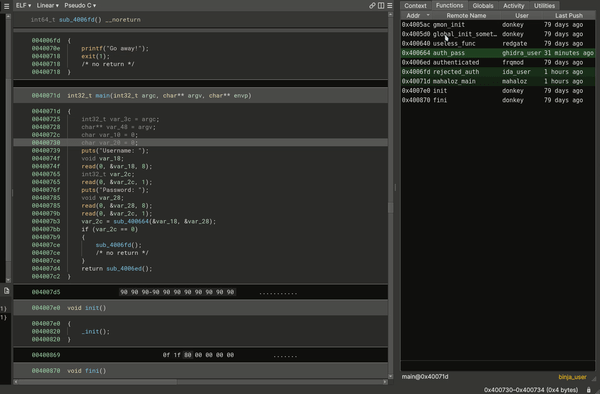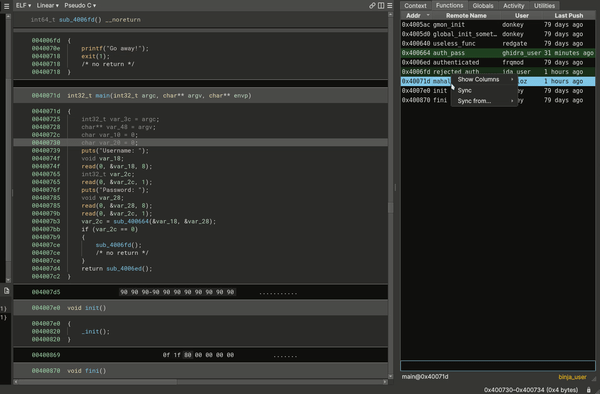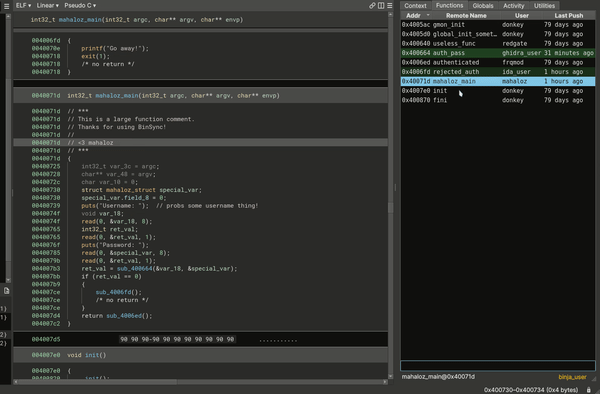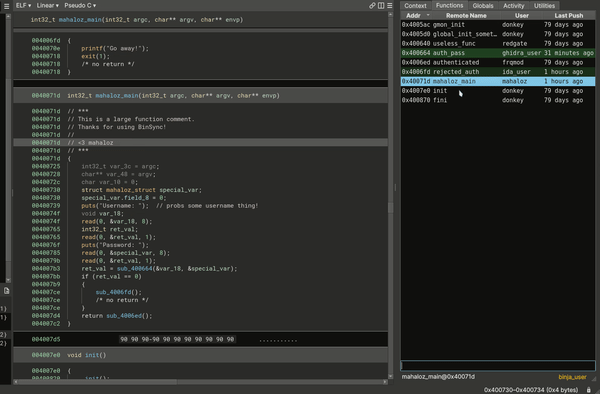 binsync/binsync
A reversing plugin for cross-decompiler collaboration, built on git.
 avito-tech/deepsecrets
Static analysis tool that scans source code for hardcoded secrets, API keys, and credentials using semantic understanding of code context.
 titanous/rocacheck
Go package that checks if RSA keys are vulnerable to ROCA / CVE-2017-15361
 raoufmaklouf/jsecret
Fast Go-based static scanner for detecting sensitive data (API keys, tokens, passwords) in JavaScript files and source code using regex patterns.
 bio/vue-template-compiler-patched
Patched Vue 2.7.16 template compiler with fixes for CVE‑2024‑6783 and CVE-2024-9506