

fsop-finder
 xf1les/fsop-finder
Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
binary-analysisbinary-exploitationexploitation+5
12
xf1les/fsop-finderBinary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
 111ddea/xstream_cve-2022-41966
Debug and proof-of-concept code for CVE-2022-41966, demonstrating exploitation of the XStream deserialization vulnerability in Java.
 bartimusprimed/cve-2021-1675-yara
YARA rules for detecting CVE-2021-1675 (PrintNightmare) exploitation attempts and related malware artifacts.
 nanopathi/external_libavc_aosp10_r33_cve-2021-0325
C-based vulnerability analysis and exploitation toolkit targeting AOSP libavc heap overflow (CVE-2021-0325) with static code analysis capabilities.
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
 shoucheng3/x-stream__xstream_cve-2013-7285_1-4-6
Java XML serialization library with a focus on the CVE-2013-7285 deserialization vulnerability, providing source code, binaries, and documentation…
 satheesh575555/external_v8_aosp10_r33_cve-2021-0396
Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.
 nidhihcl/external_expat_2.1.0_cve-2022-43680
C library for stream-oriented XML parsing with a focus on vulnerability analysis and exploitation of CVE-2022-43680, enabling fuzzing and…
 pazhanivel07/openjpeg-2.3.0_cve-2020-27824
CVE-2020-27824 exploit reproduction environment for OpenJPEG JPEG 2000 codec, enabling vulnerability analysis, fuzzing, and binary exploitation…
 forse01/cve-2019-5413-netbeans-nojson
Proof-of-concept exploit for CVE-2019-5413, a remote code execution vulnerability in Apache NetBeans. Demonstrates exploitation via crafted XML…
 bde574786/sequelize-1day-cve-2023-25813
Proof-of-concept and technical analysis of CVE-2023-25813, a SQL injection vulnerability in Sequelize ORM versions prior to 6.19.1, including…
 trinadh465/external_expat-2.1.0_cve-2022-25313
Repository dedicated to CVE-2022-25313, a vulnerability in Expat 2.1.0, providing analysis and potential exploitation code.
 epicosy/xstream-1
Java library for XML serialization and deserialization, with a focus on CVE-2020-26217 exploitation. Enables converting Java objects to XML and back,…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 ga1ois/blackhat-europe-2022
Select Bugs From Binary Where Pattern Like CVE-1337-Days
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
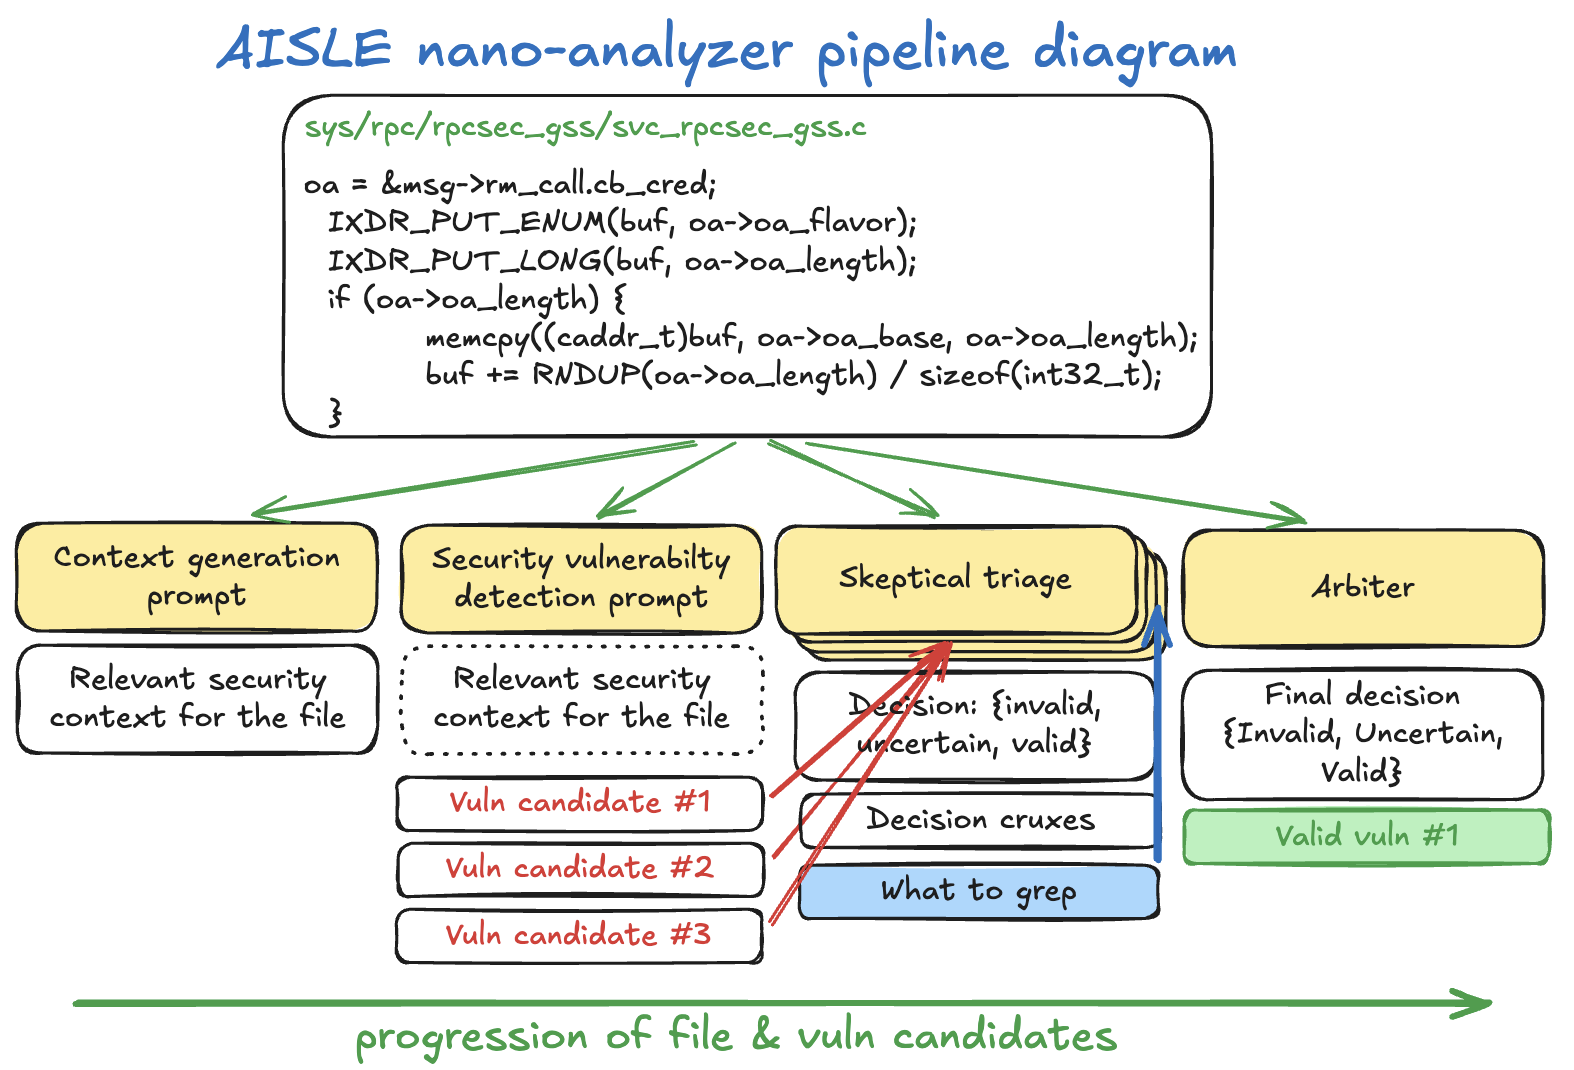 weareaisle/nano-analyzer
A minimal LLM-powered zero-day vulnerability scanner by AISLE.
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…