
np-audit
 koblers/np-audit
Static security analysis for npm packages. Detects obfuscated code, malicious patterns, and known vulnerabilities before installation.
code-analysismalware-analysissecret-detection+3
8
koblers/np-auditStatic security analysis for npm packages. Detects obfuscated code, malicious patterns, and known vulnerabilities before installation.

 divyanshukumar0014/shipproof
SOC 2 evidence that collects itself in GitLab CI: every merge emits a signed bundle, an OPA gate blocks releases with missing proof, and auditors get…
 adshao/flounder
Autonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.
 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
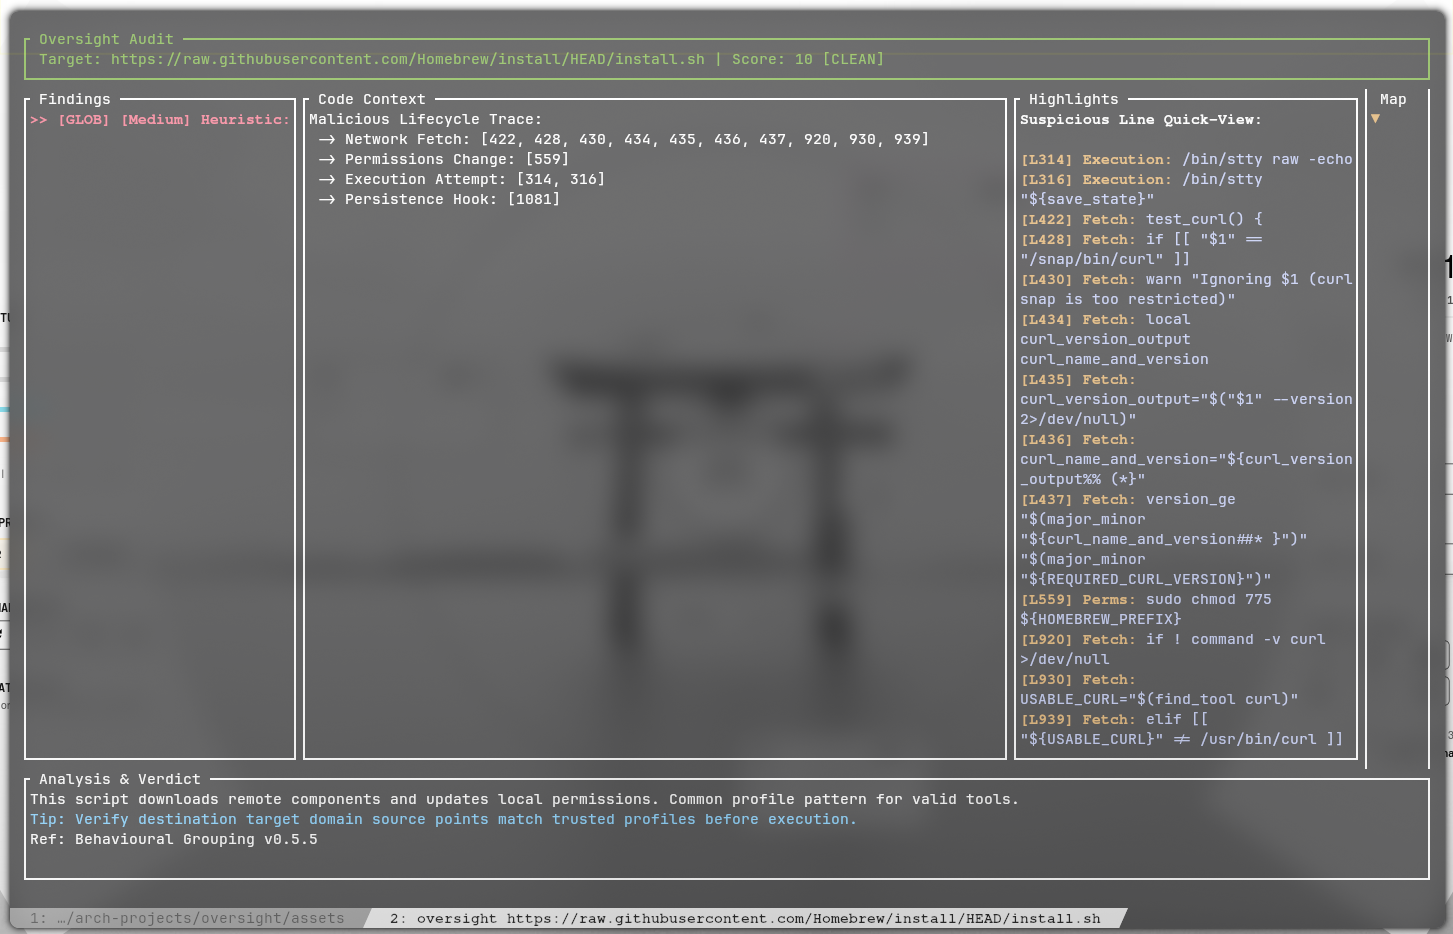 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings