
aura
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
code-analysiseducationmalware-analysis+4
sourcecode-ai/auraPython source code auditing and static analysis on a large scale
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
 shoucheng3/xwiki__xwiki-commons_cve-2023-31126_14-10-3
Java library providing technical commons for XWiki projects, with a focus on vulnerability analysis and static code inspection for security testing.
 vinsontang1/vultriage
The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection
 shoucheng3/codehaus-plexus__plexus-utils_cve-2017-1000487_3-0-15
Java utility library with a focus on a specific CVE vulnerability, providing code analysis and static analysis capabilities for security assessment.
 galoisinc/mate
Interactive program analysis suite using Code Property Graphs to hunt for bugs in C and C++ code, unifying application-specific and low-level…
 shoucheng3/x-stream__xstream_cve-2013-7285_1-4-6
Java XML serialization library with a focus on the CVE-2013-7285 deserialization vulnerability, providing source code, binaries, and documentation…
 thesp0nge/dawnscanner
Dawn is a static analysis security scanner for ruby written web applications. It supports Sinatra, Padrino and Ruby on Rails frameworks.
 trinadh465/external_expat-2.1.0_cve-2022-43680
Source code repository for Expat 2.1.0, a stream-oriented XML parser library, with focus on analyzing and addressing CVE-2022-43680.
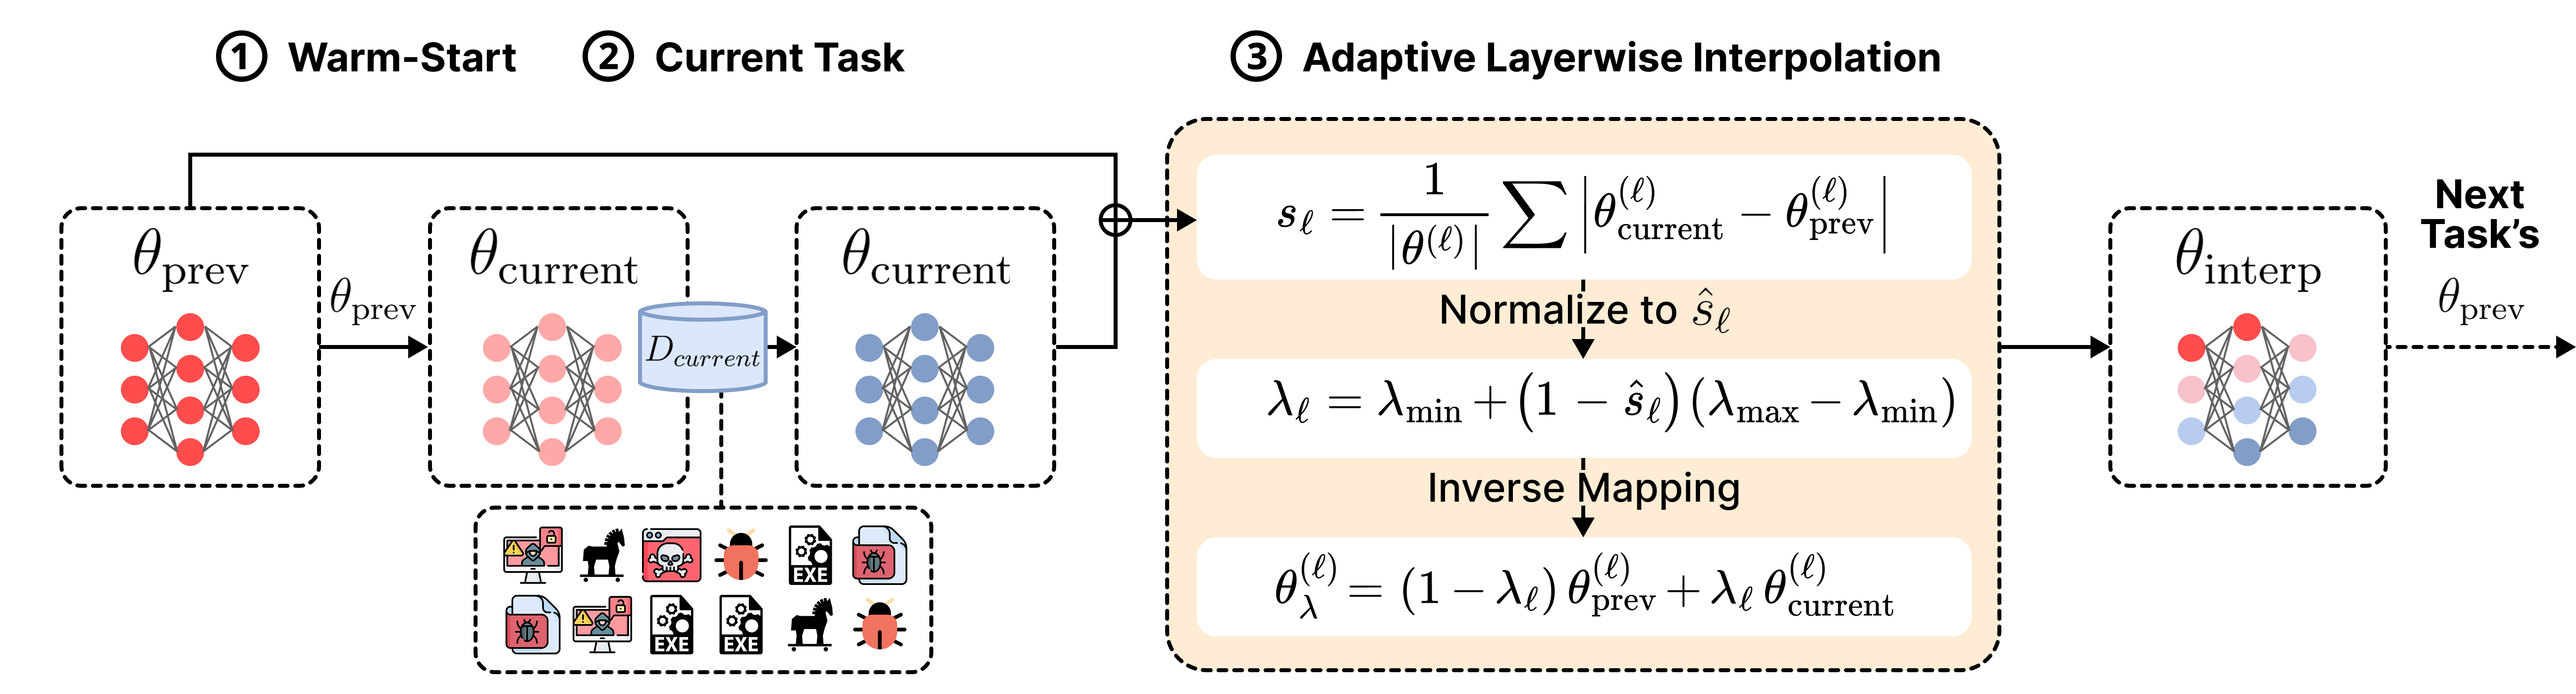 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
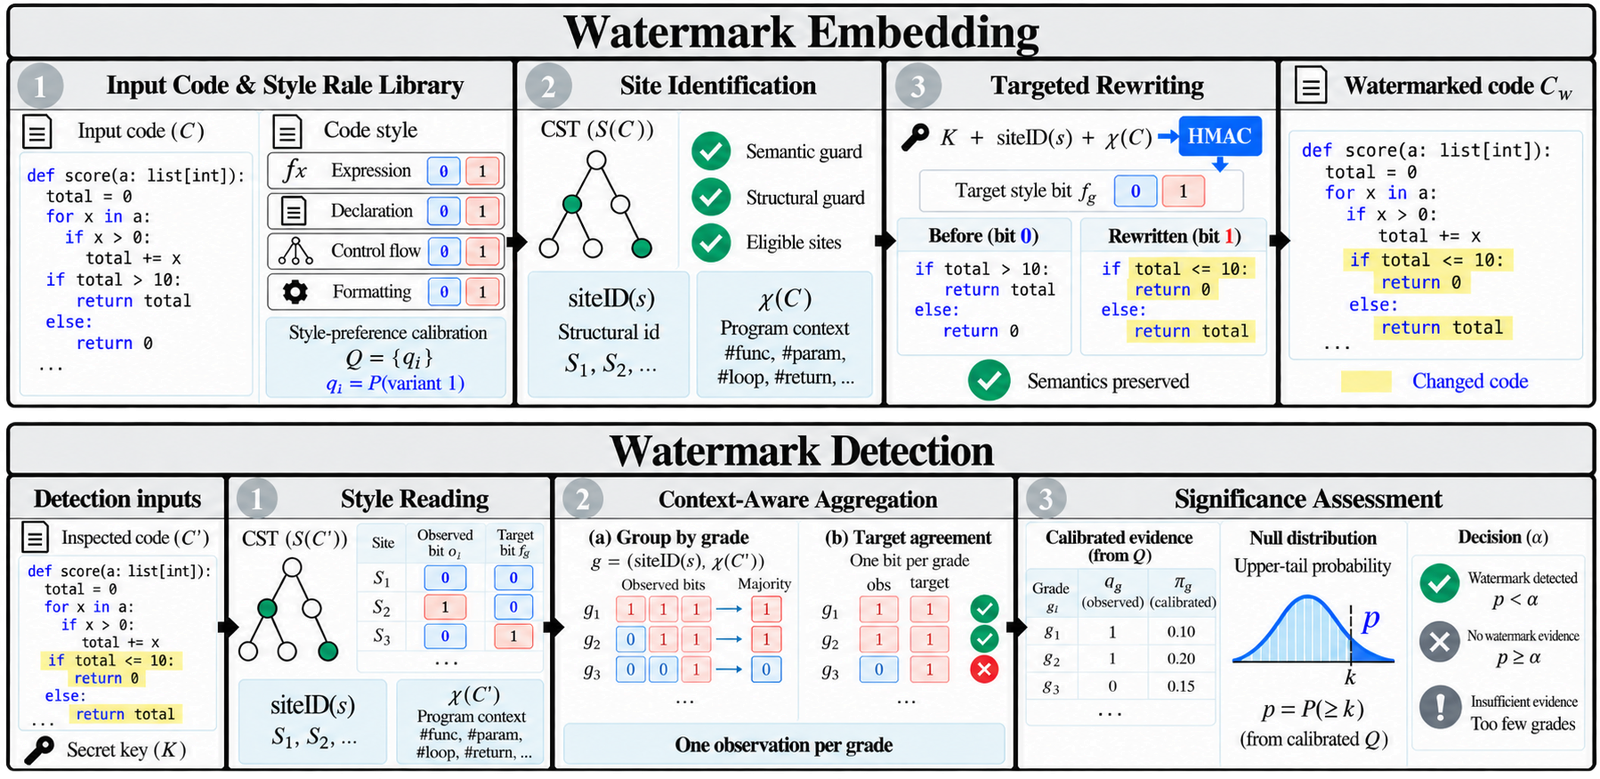 suhanmen/sew
Embeds and detects keyed, style-based watermarks in LLM-generated Python, Java, and C++ code via CST rewriting, preserving functional correctness and…
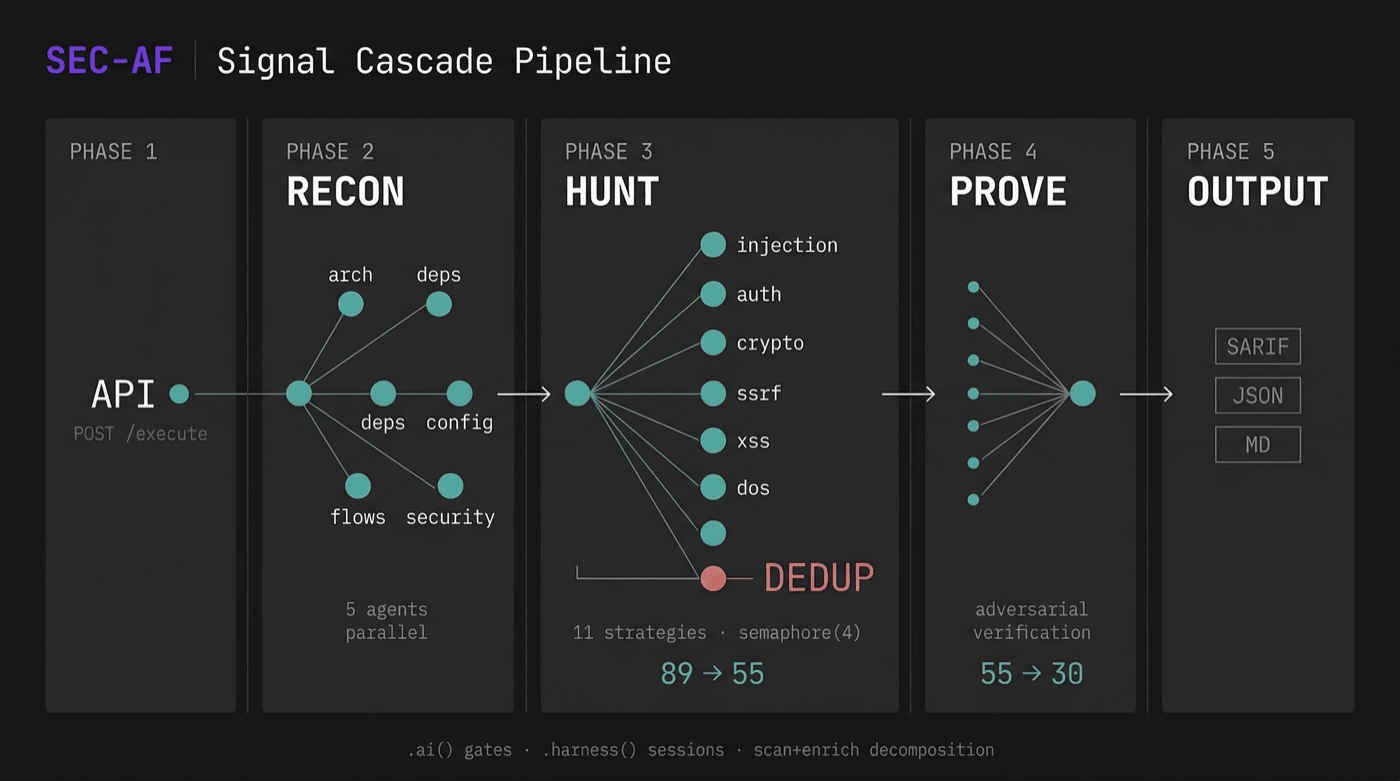 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 reb311ion/replica
Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
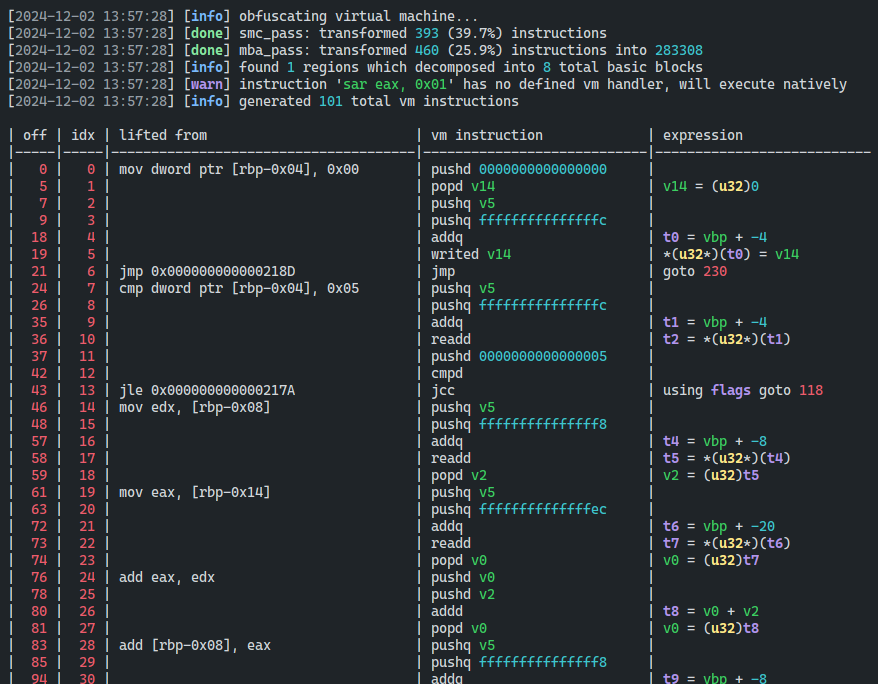 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…