android-reverse-engineering-skill

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux

Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…

Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection

Universal signature generation for any system function from all Windows Builds using Winbindex

Plugin for JADX to integrate MCP server

Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…

Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…

Ghidra is a software reverse engineering (SRE) framework

Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…

Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…

Static taint analysis platform for Android apps that detects vulnerabilities and compliance issues using customizable rule-based scanning and…

Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.

Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…

YARA-based scanner that detects obfuscated PHP malware and webshells using semantic pattern matching instead of file hashes, with a whitelist system…

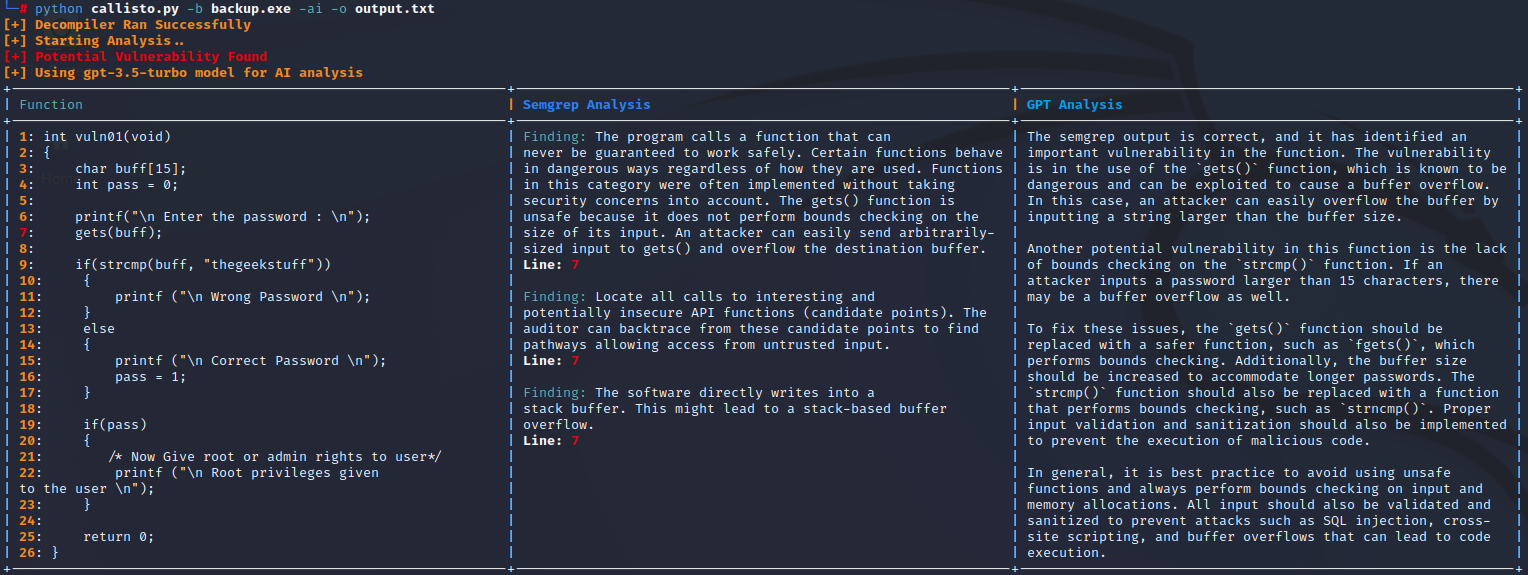
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…

Interactive program analysis suite using Code Property Graphs to hunt for bugs in C and C++ code, unifying application-specific and low-level…

Malware detection using learning and information retrieval for Android