cve-2015-1187-dir820l-firmware-reverse-engineering

Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…

Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…

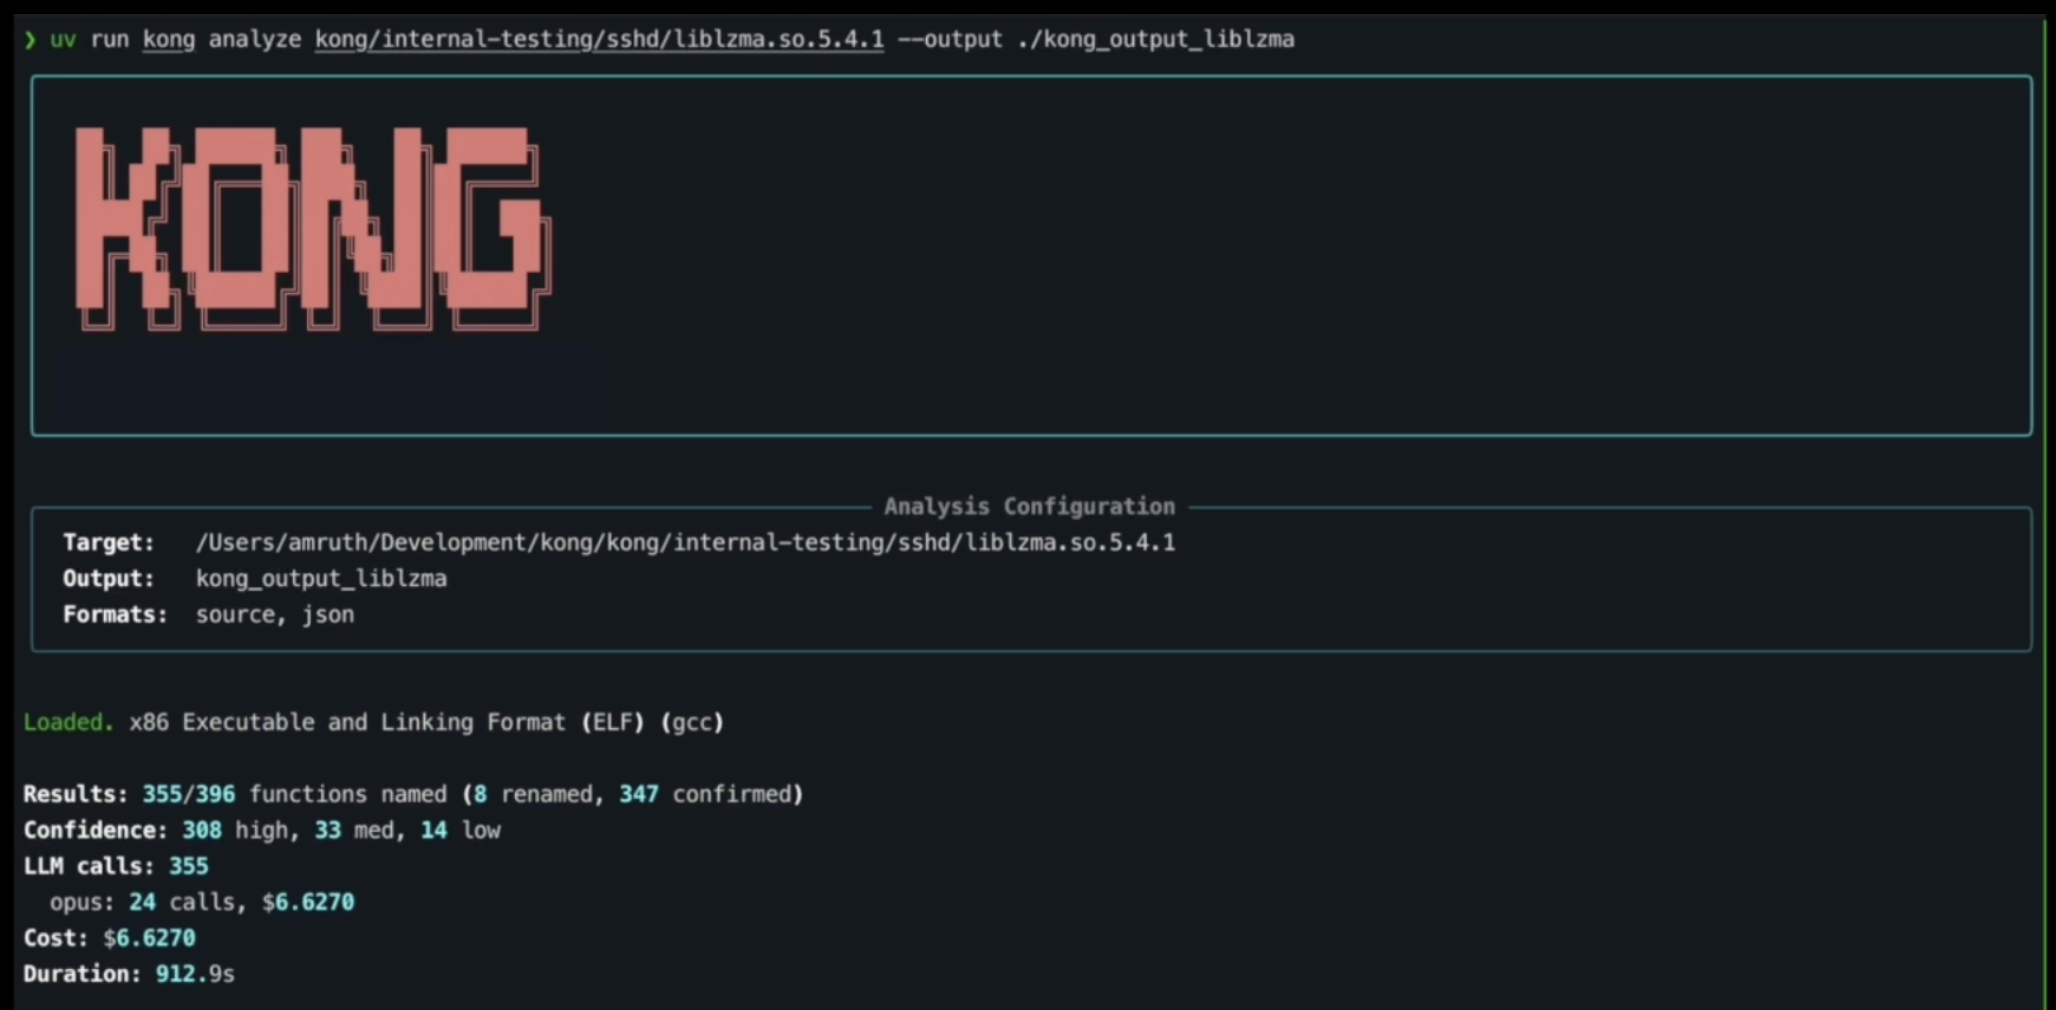
The world's first agentic reverse engineer.

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux

A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.

Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.

Secure, Unified, Powerful and Extensible Rust Android Analyzer

Generate Objective-C headers from Mach-O files.

Penetration testing and auditing toolkit for Android apps.

Python Command-Line Ghidra MCP

A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会

Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…

Extract URLs, paths, secrets, and other interesting bits from JavaScript

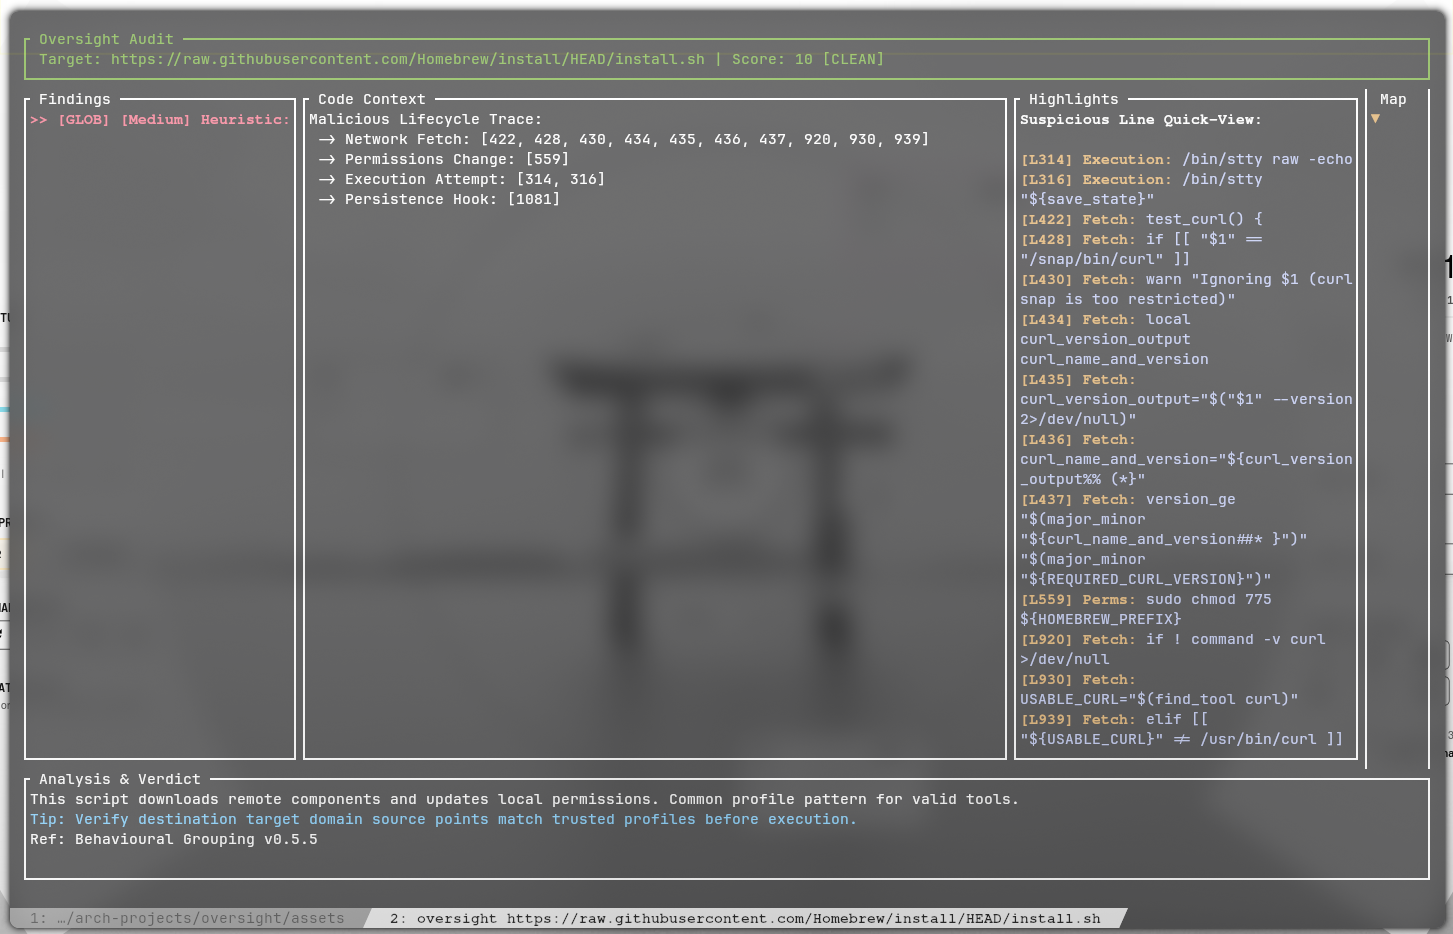
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…

Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.

Kalim backdooe Malware Report

CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.

Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…

Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.