
owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…

The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…

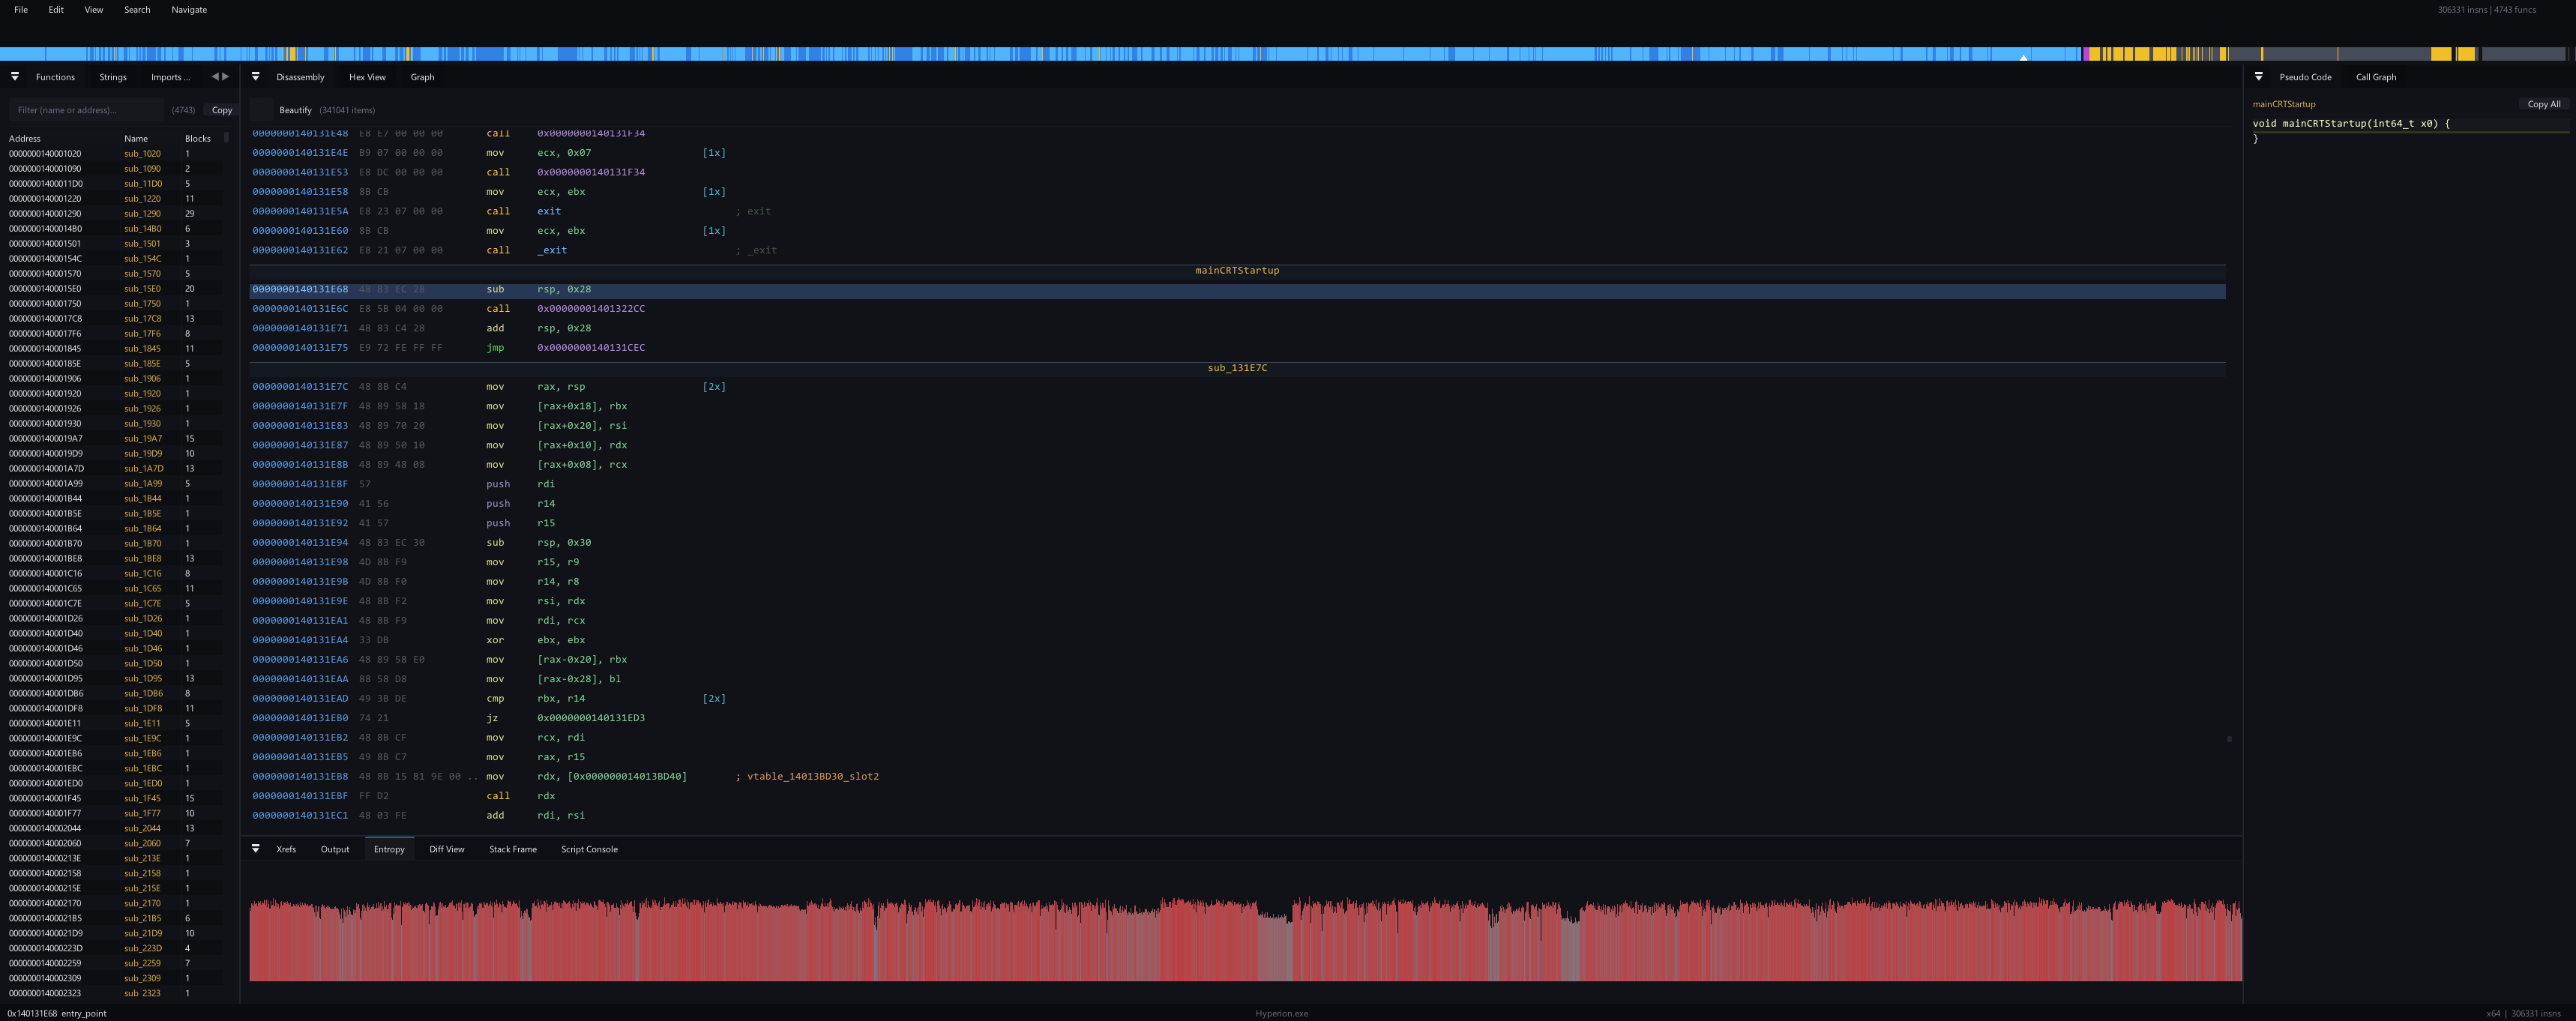
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery

C++ library for detecting cross-site scripting (XSS) vulnerabilities in URLs through pattern analysis, with server modules and command-line tools for…

Java library providing XSS escaping and filtering services (XSSAPI, XSSFilter) to sanitize user-submitted content and prevent cross-site scripting…

Java library for fast, configurable cleansing of untrusted HTML to prevent cross-site scripting (XSS) attacks. Uses policy-driven scanning to…

Static analysis scanner for CVE-2020-11023 XSS vulnerabilities in JavaScript. Detects vulnerable jQuery versions and dangerous DOM manipulation…

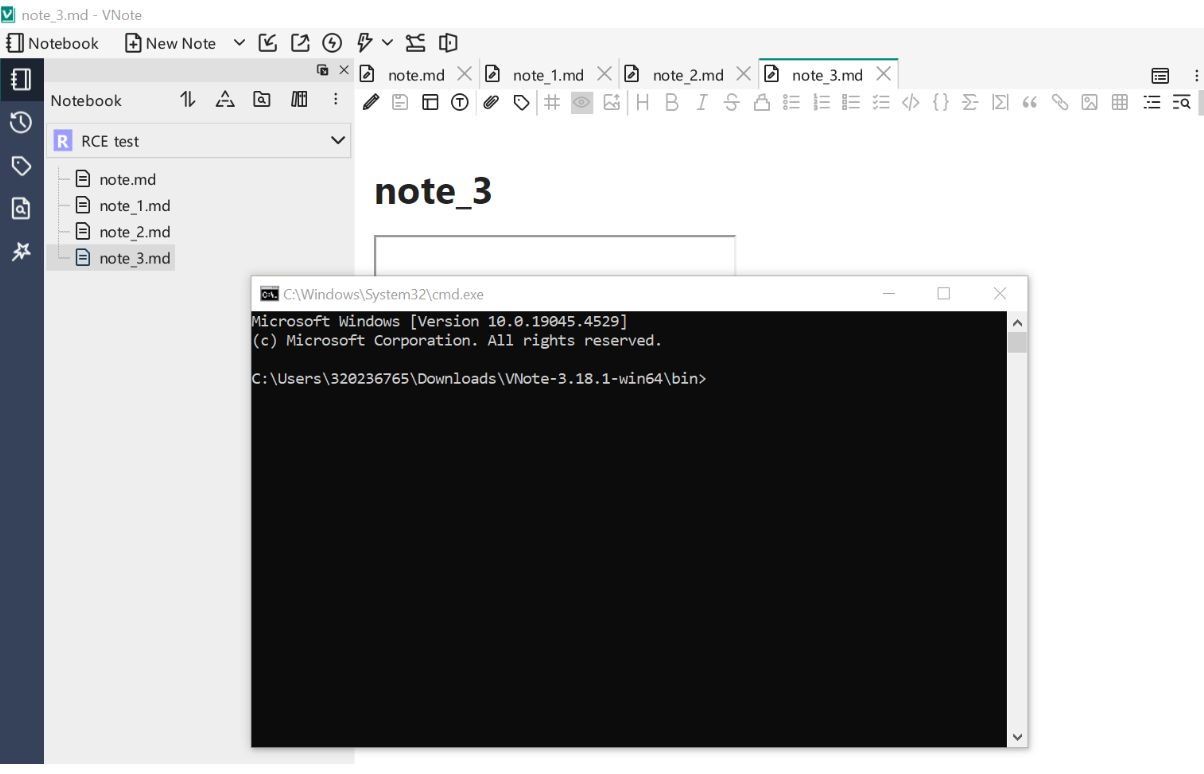
Markdown XSS leads to RCE in VNote version <=3.18.1

Demostracion educativa de mitigacion y deteccion de CVE-2026-32635: XSS en atributos i18n de Angular.

Public disclosure for CVE-2023-31584.

Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.

Regular expression matching for URL's. Maintained, safe, and browser-friendly version of url-regex. Resolves CVE-2020-7661 for Node.js servers.

A powerful Python library and CLI tool for parsing, analyzing, and manipulating YARA rules through Abstract Syntax Tree (AST) representation

Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…