
Archived
anchore-engine
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
cloud-securitycontainer-securitydevsecops+3
1.6k
anchore/anchore-engineA service that analyzes docker images and scans for vulnerabilities
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 ashishb/android-security-awesome
A collection of android security related resources
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
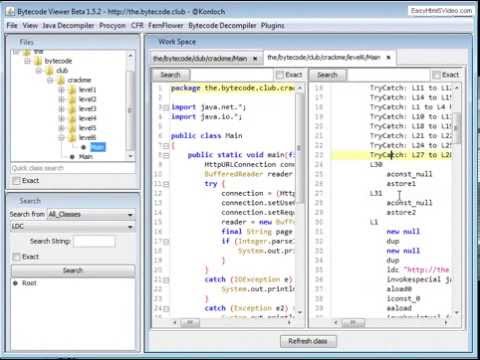 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 androguard/androguard
Reverse engineering and pentesting for Android applications
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 newliver666/apk-reverse
Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 saeidshirazi/awesome-android-security
A curated list of Android Security materials and resources For Pentesters and Bug Hunters
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
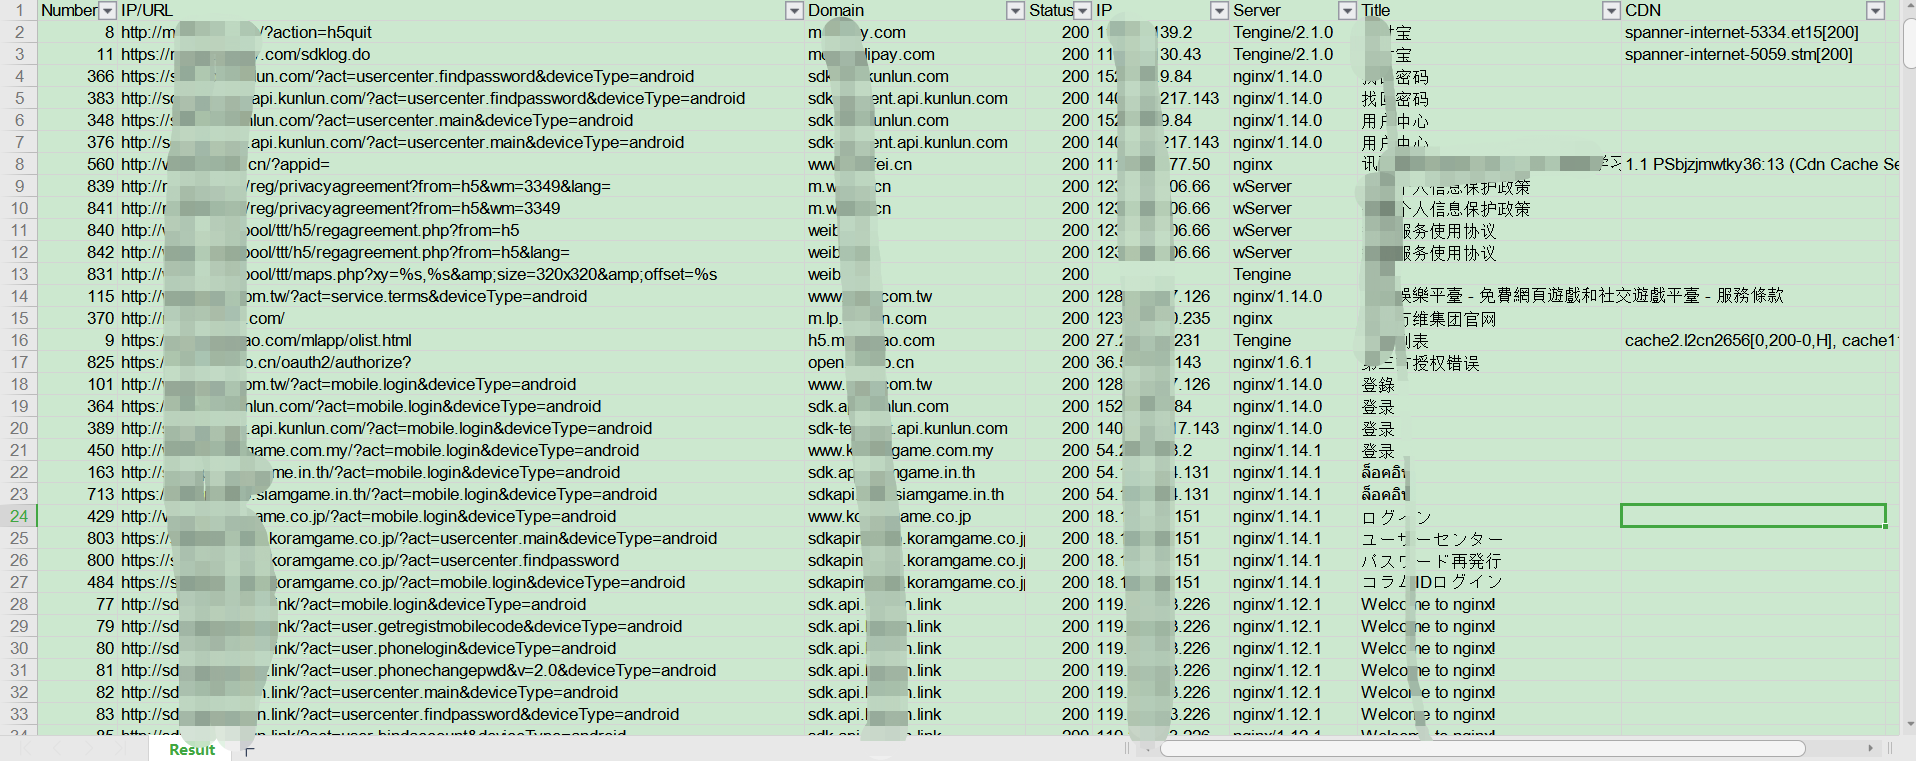 kelvinben/appinfoscanner
一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
 vaib25vicky/awesome-mobile-security
An effort to build a single place for all useful android and iOS security related stuff. All references and tools belong to their respective owners.…
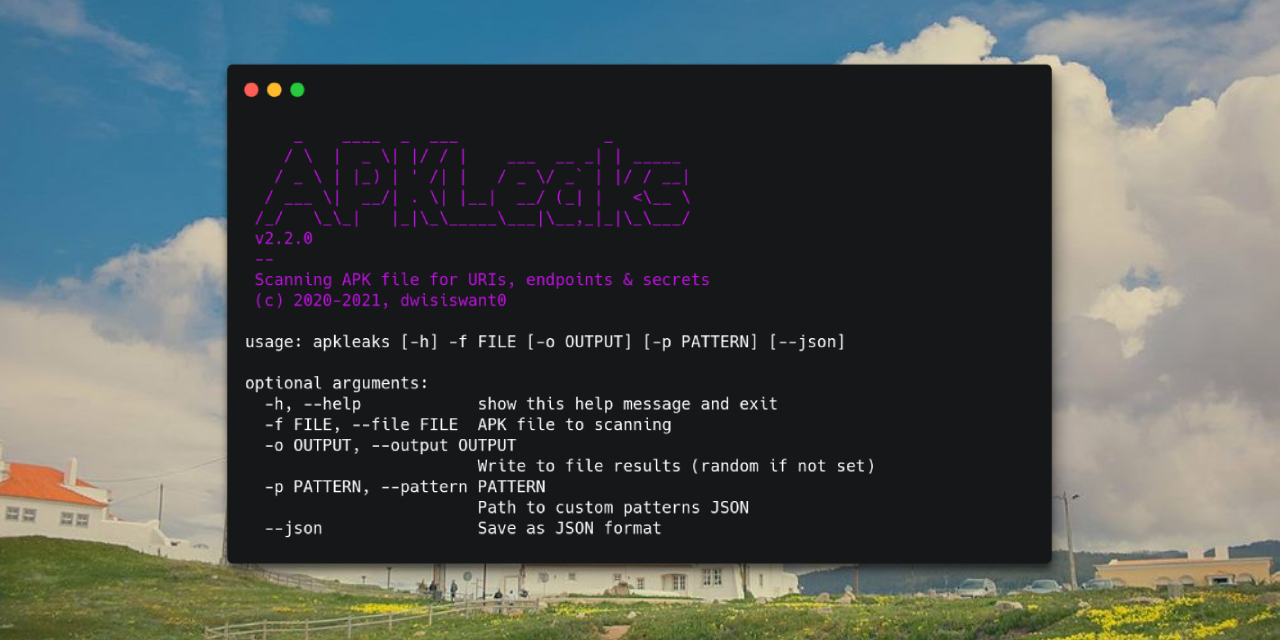 dwisiswant0/apkleaks
Scanning APK file for URIs, endpoints & secrets.