
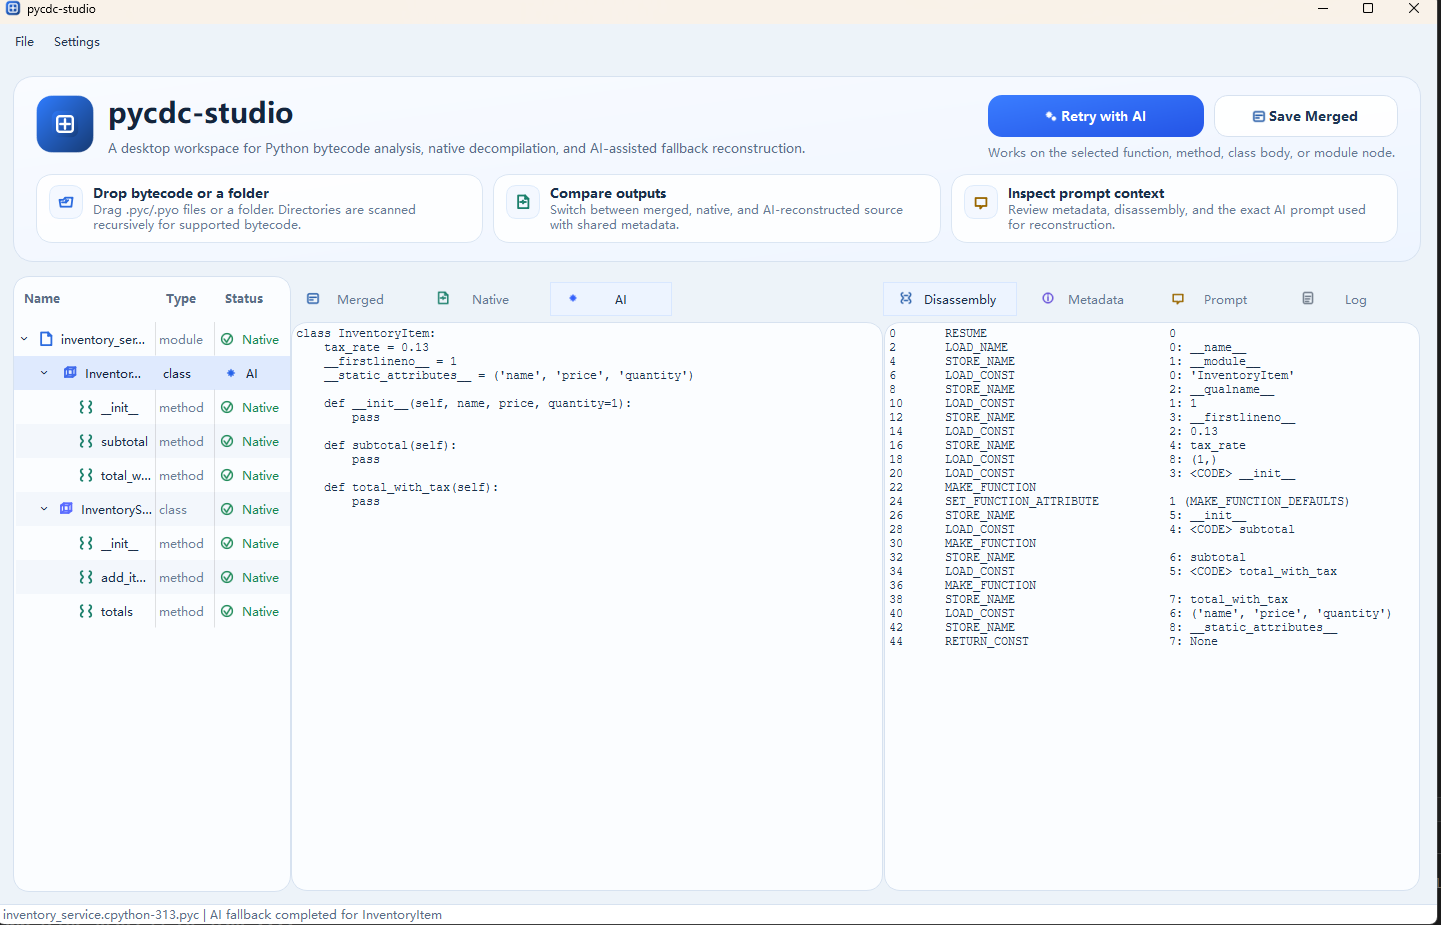
pycdc-studio
 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
ai-assisted-reversingbinary-analysisdebuggers+4
43
ddouworld/pycdc-studioA Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator
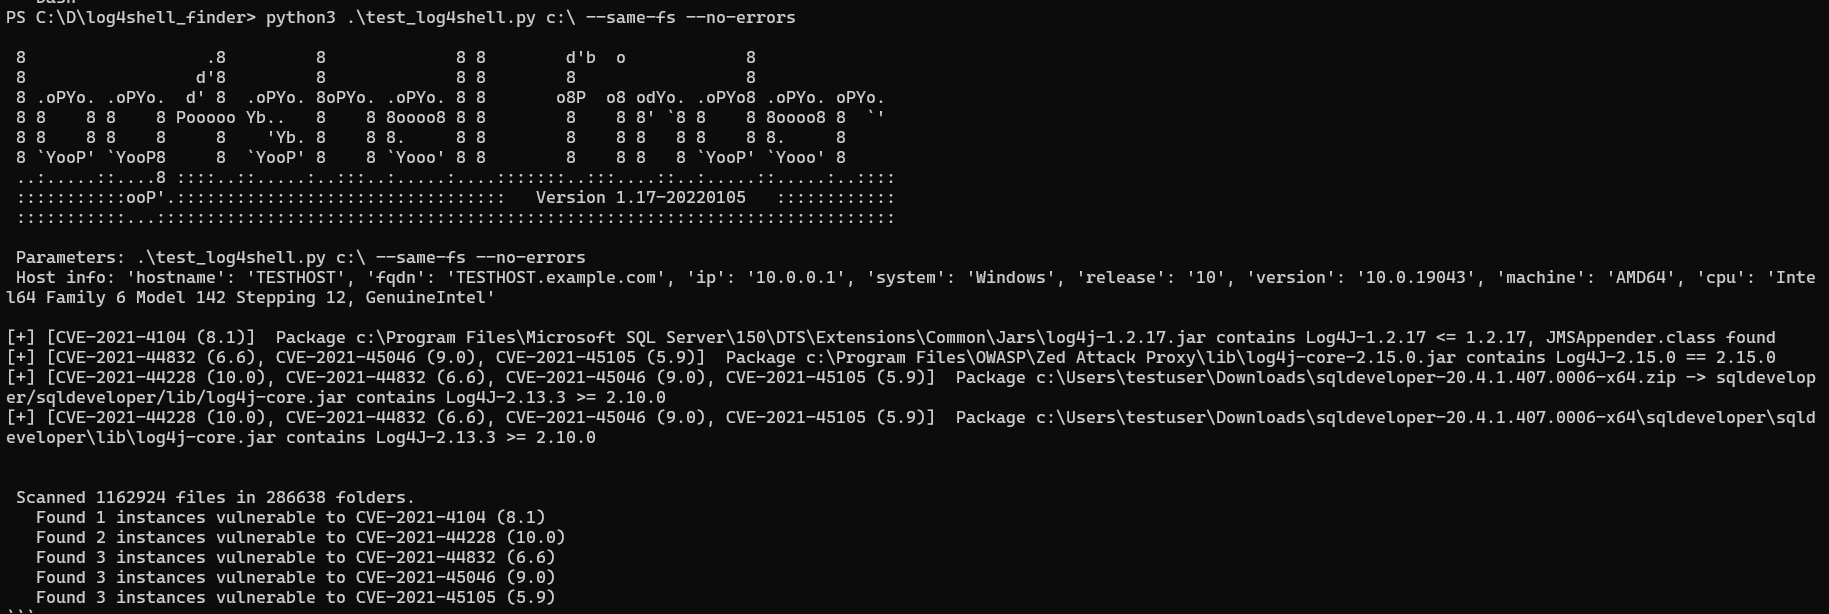 hynekpetrak/log4shell-finder
Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305,…
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
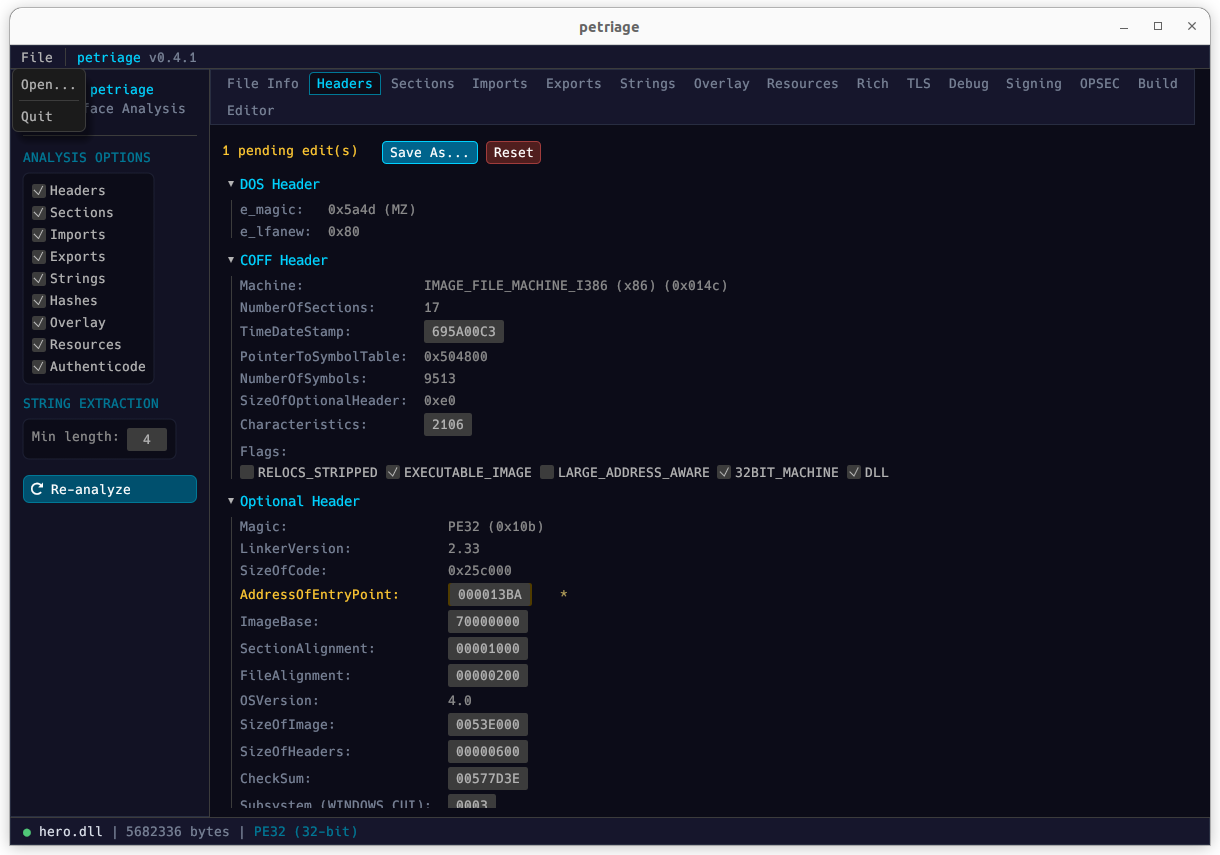 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 gautamvarmadatla/mcpsafetywarden
Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)
 gmh5225/keypatchx
KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 smileostrich/text4shell-scanner
Vulnerability Scanner for CVE-2022-42889 (Text4Shell)
 vivianuba/grandstream-cve-2026-2329-analysis
Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…
 gavmor/x86-cpp-reversing-skill
Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…