

androwarn
 maaaaz/androwarn
Yet another static code analyzer for malicious Android applications
android-securitymalware-analysismobile-security+2
532
maaaaz/androwarnYet another static code analyzer for malicious Android applications
 sh1n0g1/z9
Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.
 monnappa22/limon
Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 xiaoqimikko/thymeleaf-check
Offline checker for Thymeleaf CVE-2026-40477 / CVE-2026-41901 — tells you which of the two CVSS 9.0 SSTI flaws you are exposed to, and whether your…
 github/securitylab
Resources related to GitHub Security Lab
 ga1ois/blackhat-europe-2022
Select Bugs From Binary Where Pattern Like CVE-1337-Days
 proteqtum/interactive-binary-structures
Interactive documentation and visual reference for binary formats and system memory layouts.
 mhaggis/package-inferno
A Public Package Scanner for The Community
 shemesh999/oregami
IDA plugins and scripts for analyzing register usage frame
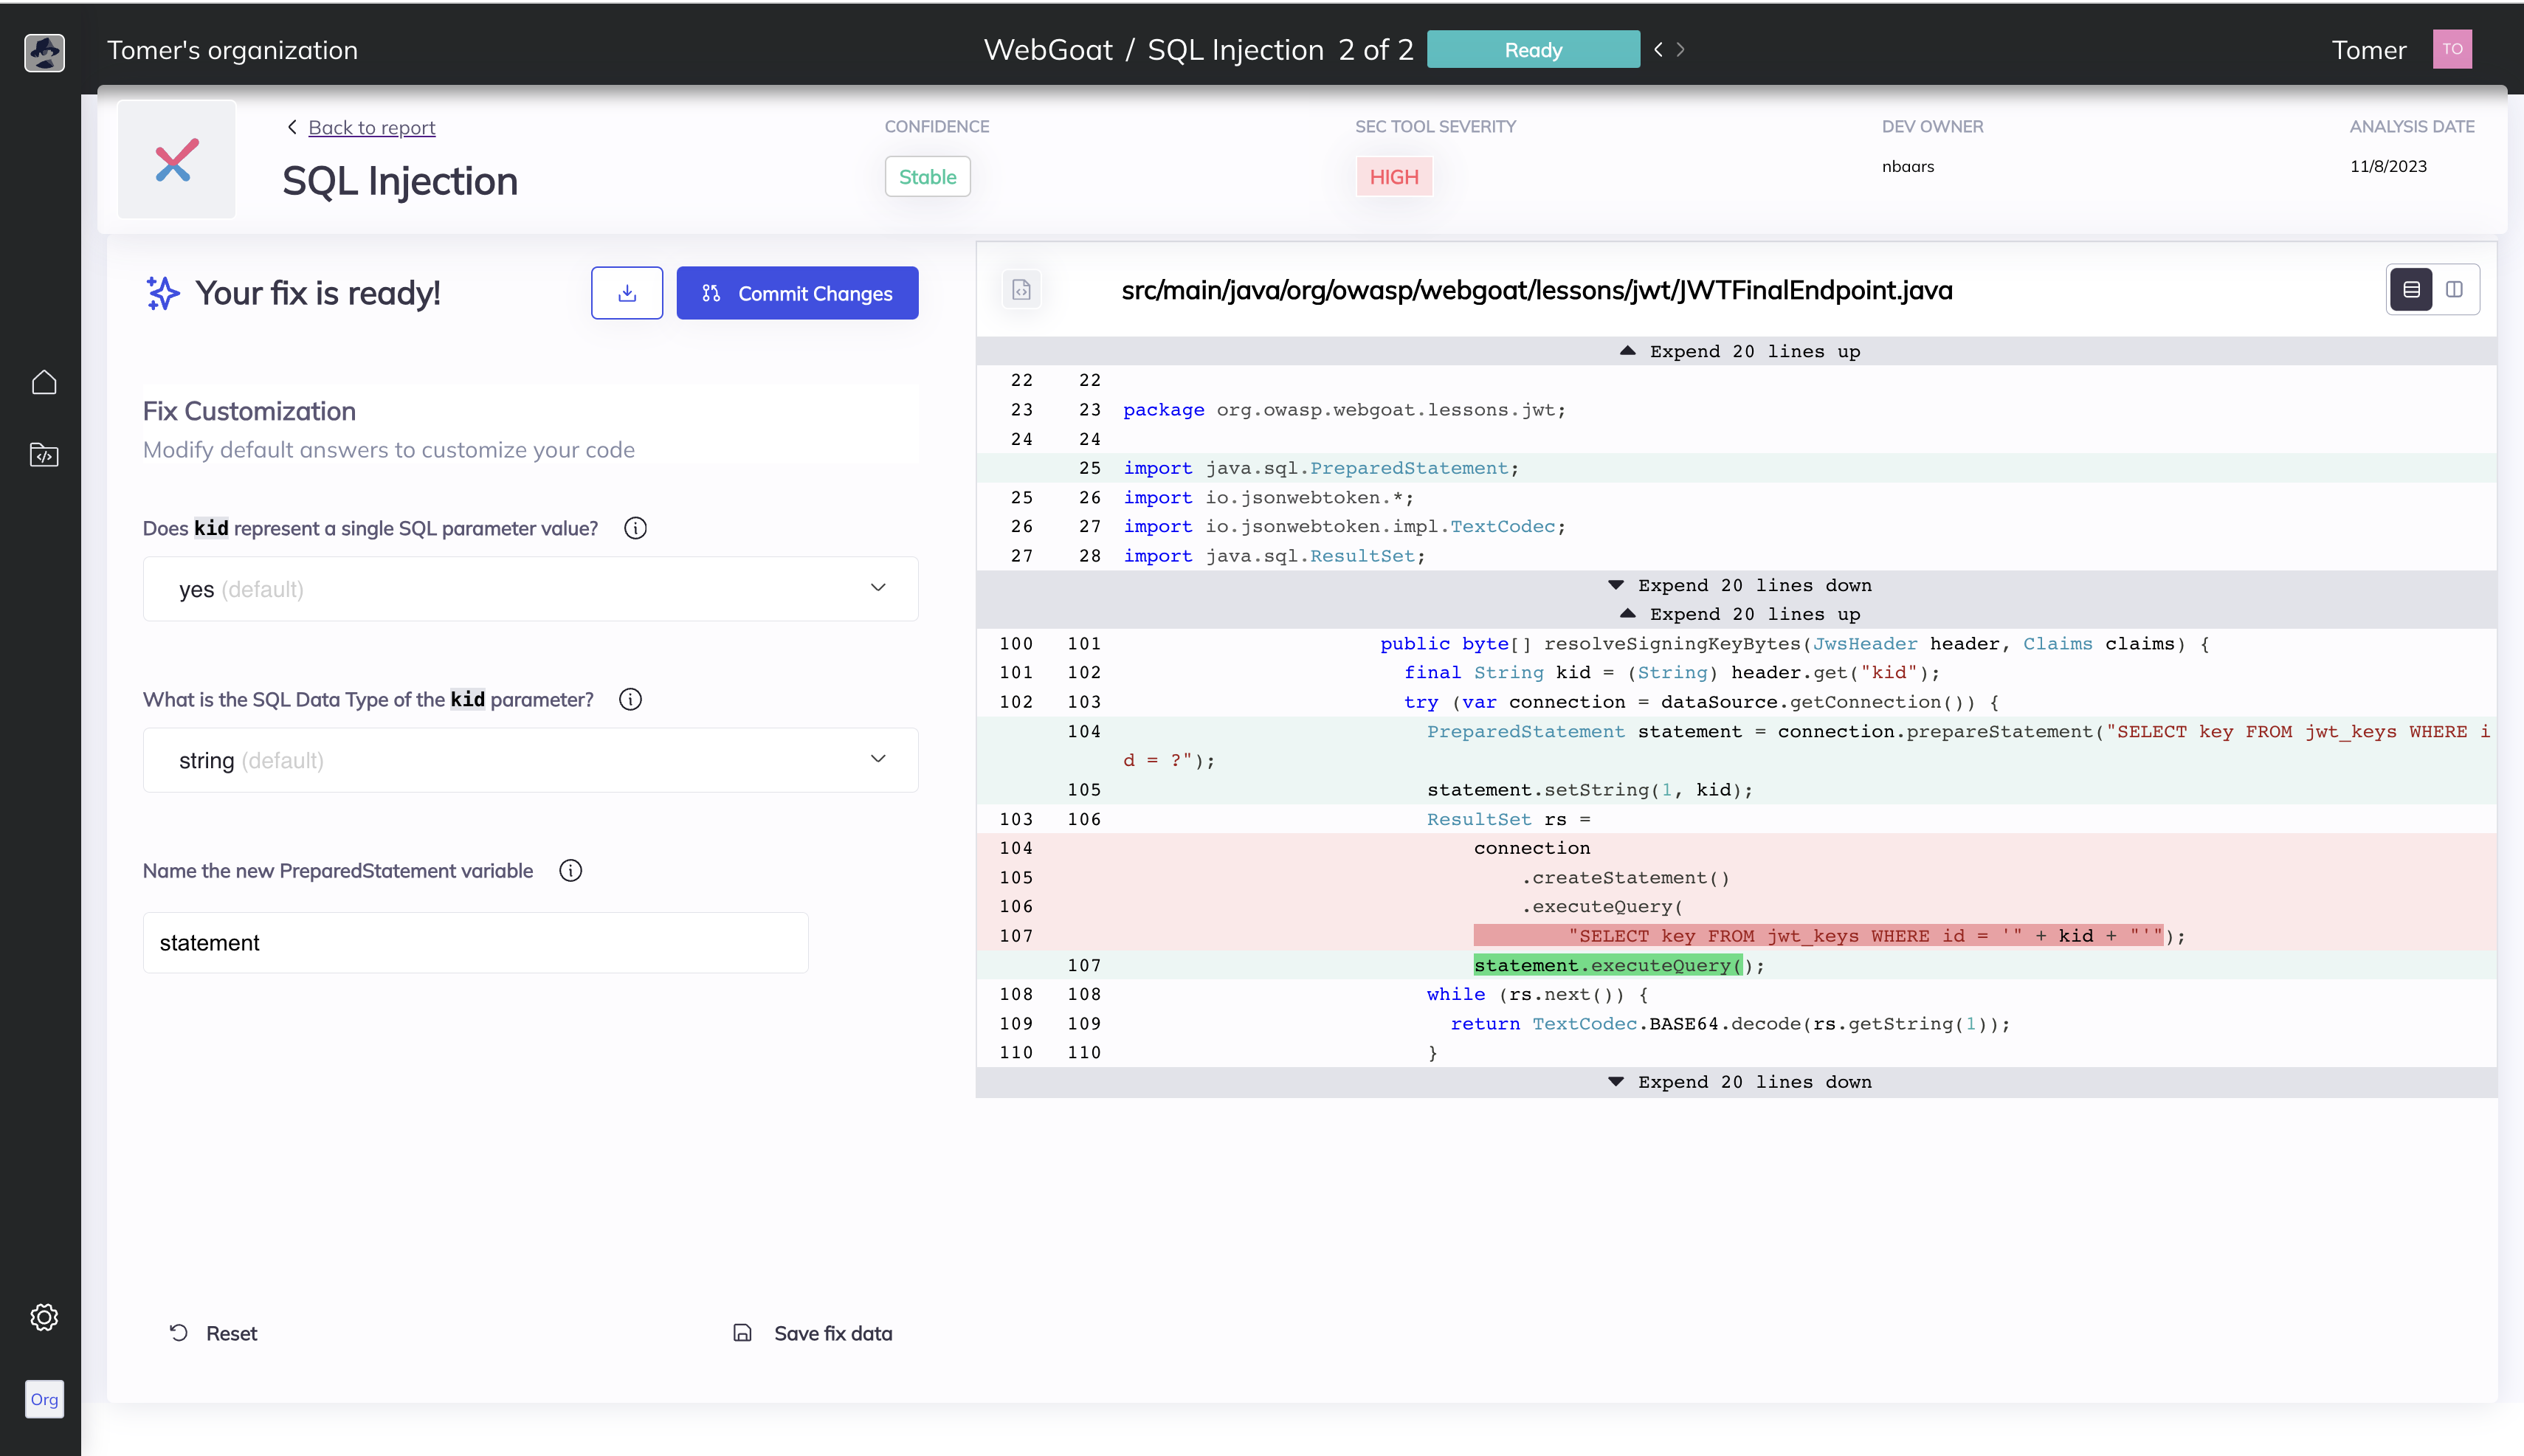 mobb-dev/bugsy
Automatic security vulnerability remediation for your code.
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
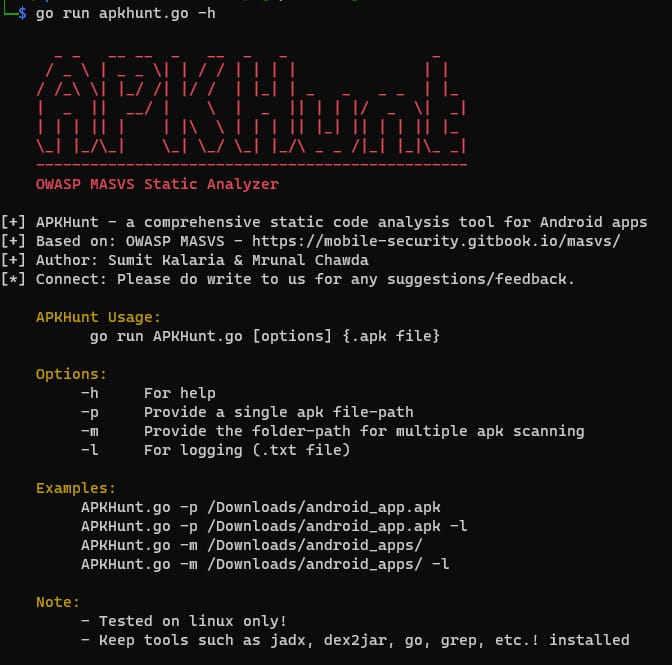 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
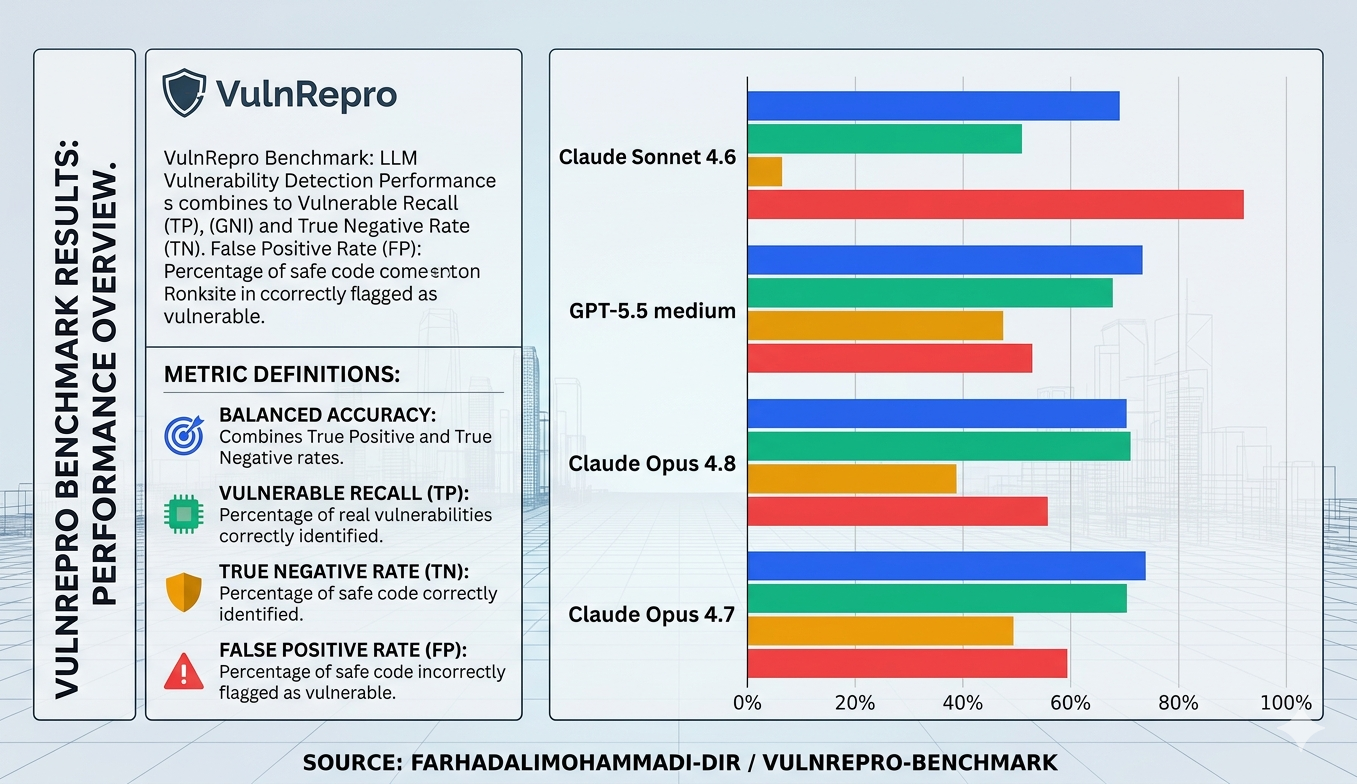 farhadalimohammadi-dir/vulnrepro-benchmark
Benchmark measuring AI models' ability to detect vulnerabilities in source code via real bug bounty cases with balanced recall and false-positive…
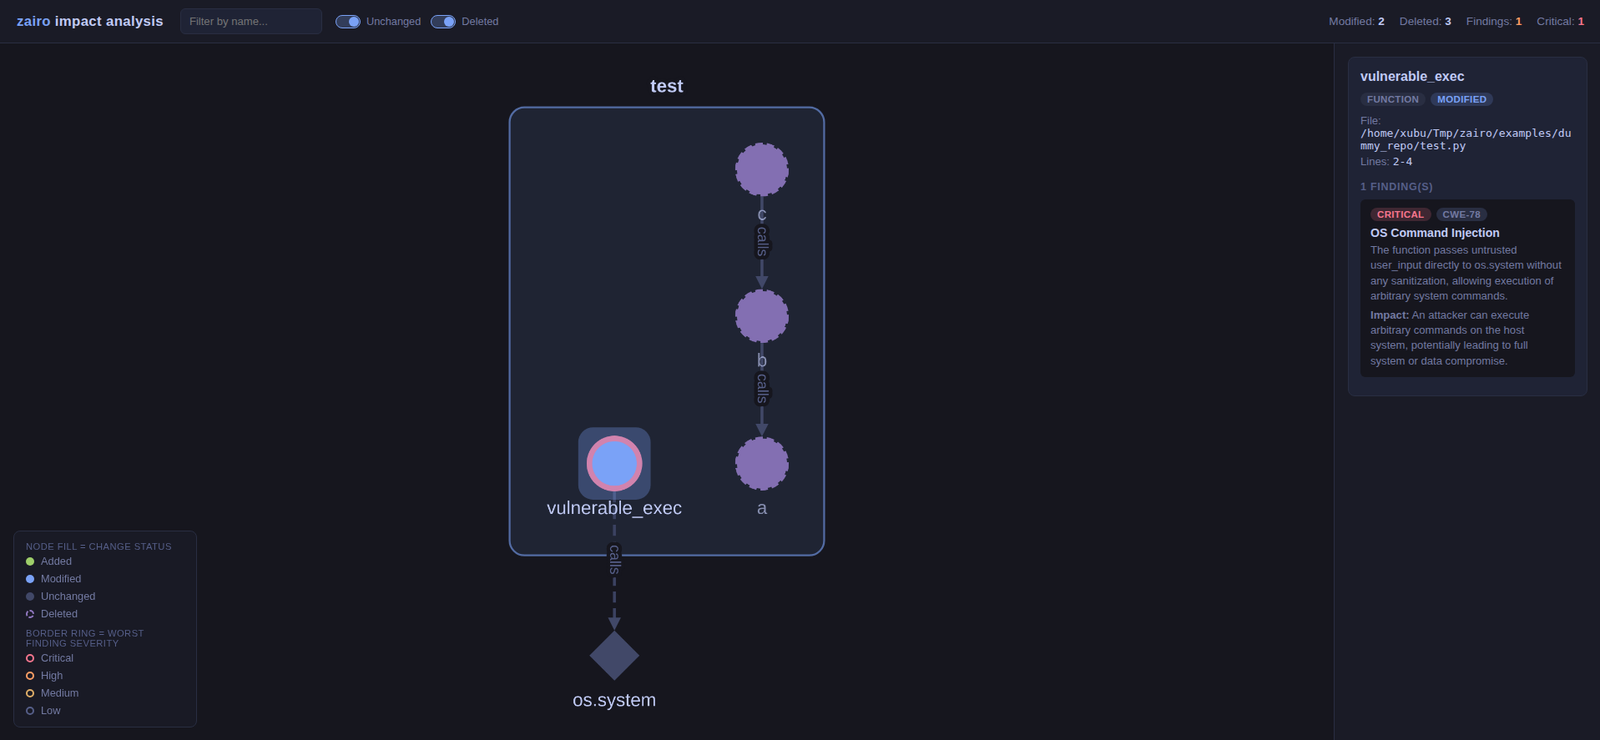 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
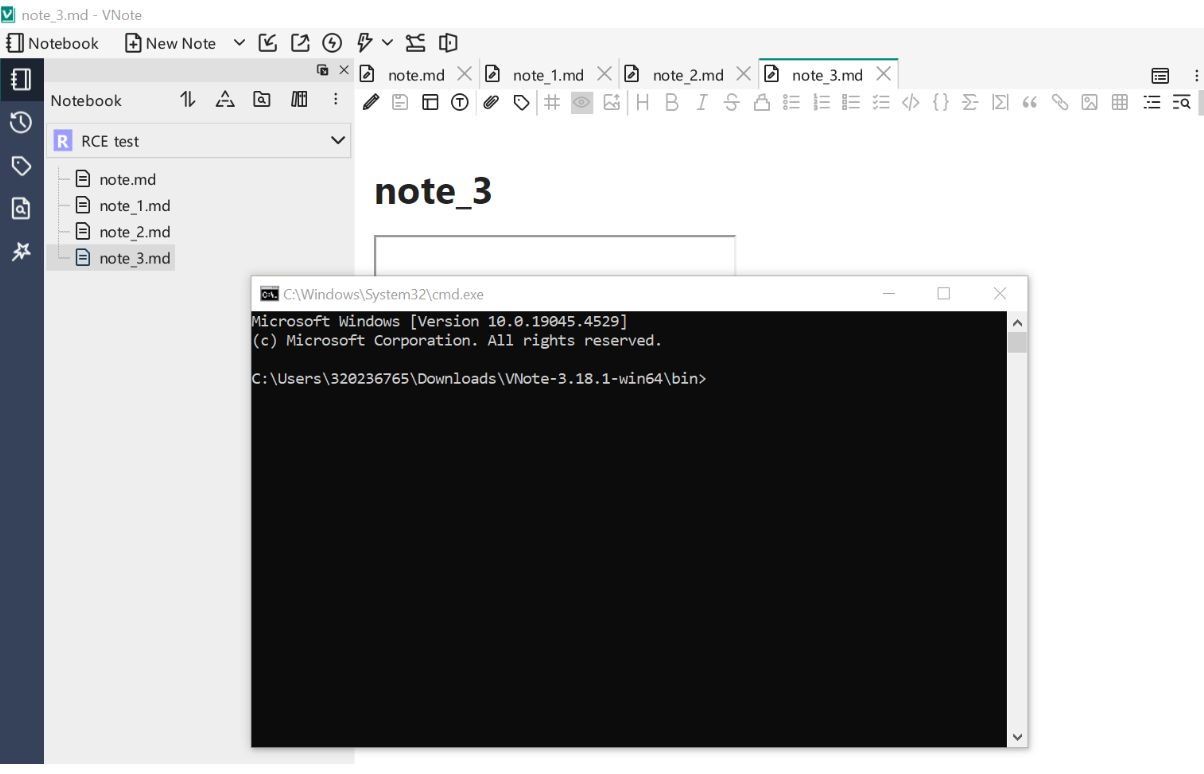 sh3bu/cve-2024-41662
Markdown XSS leads to RCE in VNote version <=3.18.1
 aipeacs/sc3010-computer-security
Using Struts2 and PowerShell to recreate CVE-2017-5638 OGNL Injection vulnerability.
 oitapps/find-vulnerableelectronversion
Scans an executable and determines if it was wrapped in an Electron version vulnerable to the Chromium vulnerability CVE-2023-4863/ CVE-2023-5129