
Apepe
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
android-securityinformation-gatheringmobile-app-pentesting+1
156
0xdsm/apepeExtracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
 denuvosoftwaresolutions/simba
Efficient Deobfuscation of Linear Mixed Boolean-Arithmetic Expressions
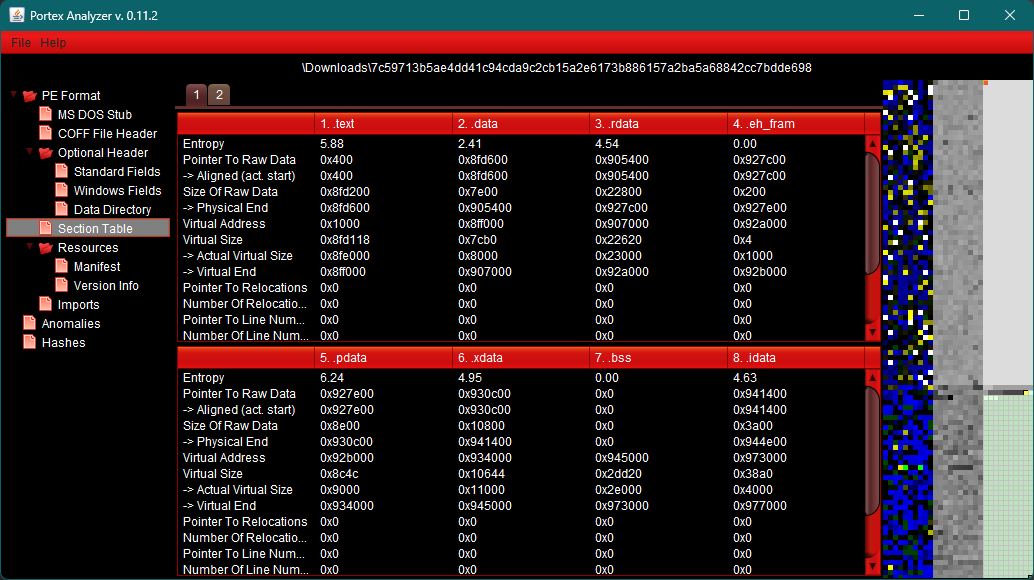 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra
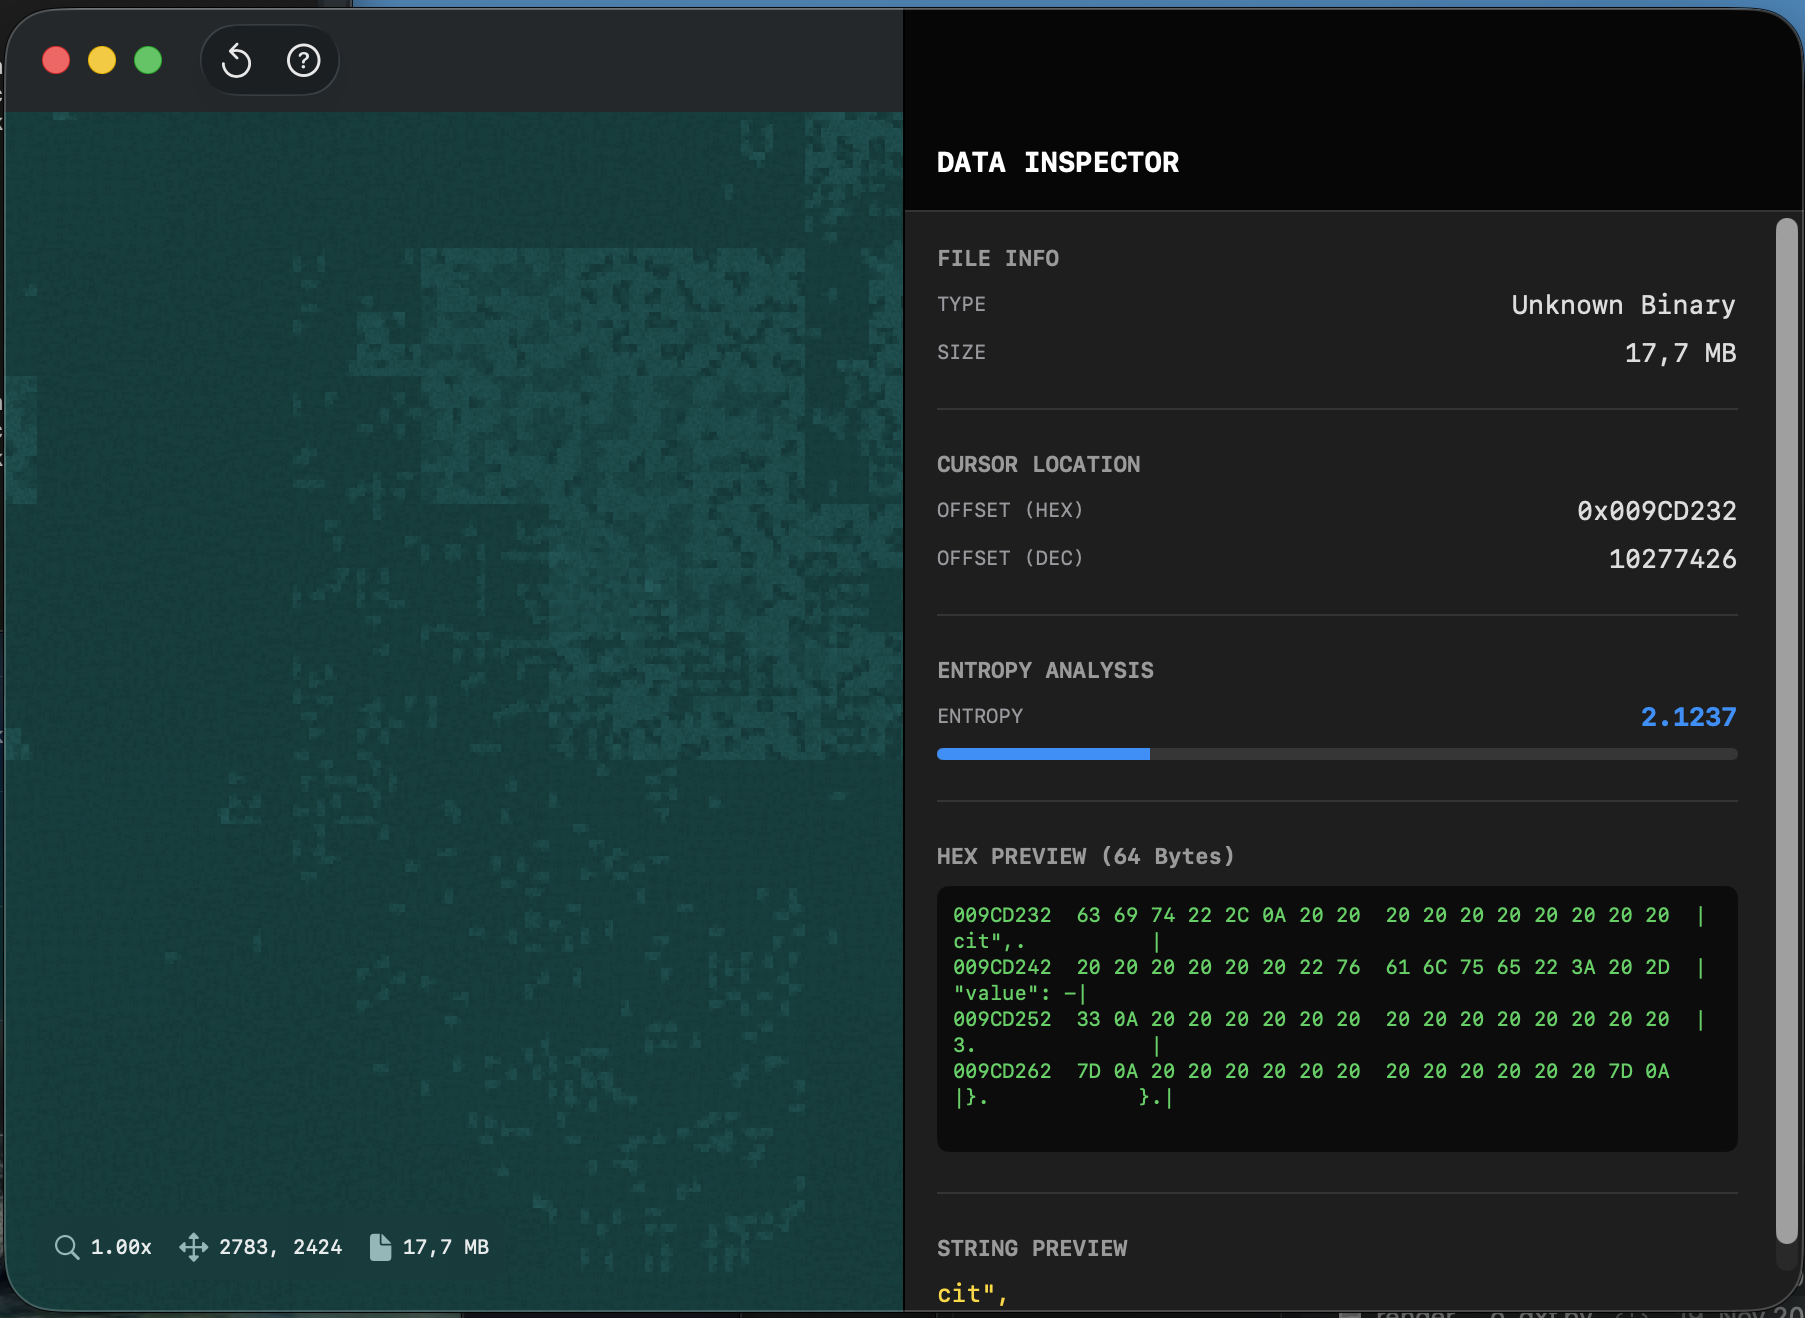 farukalpay/neurocore
NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…
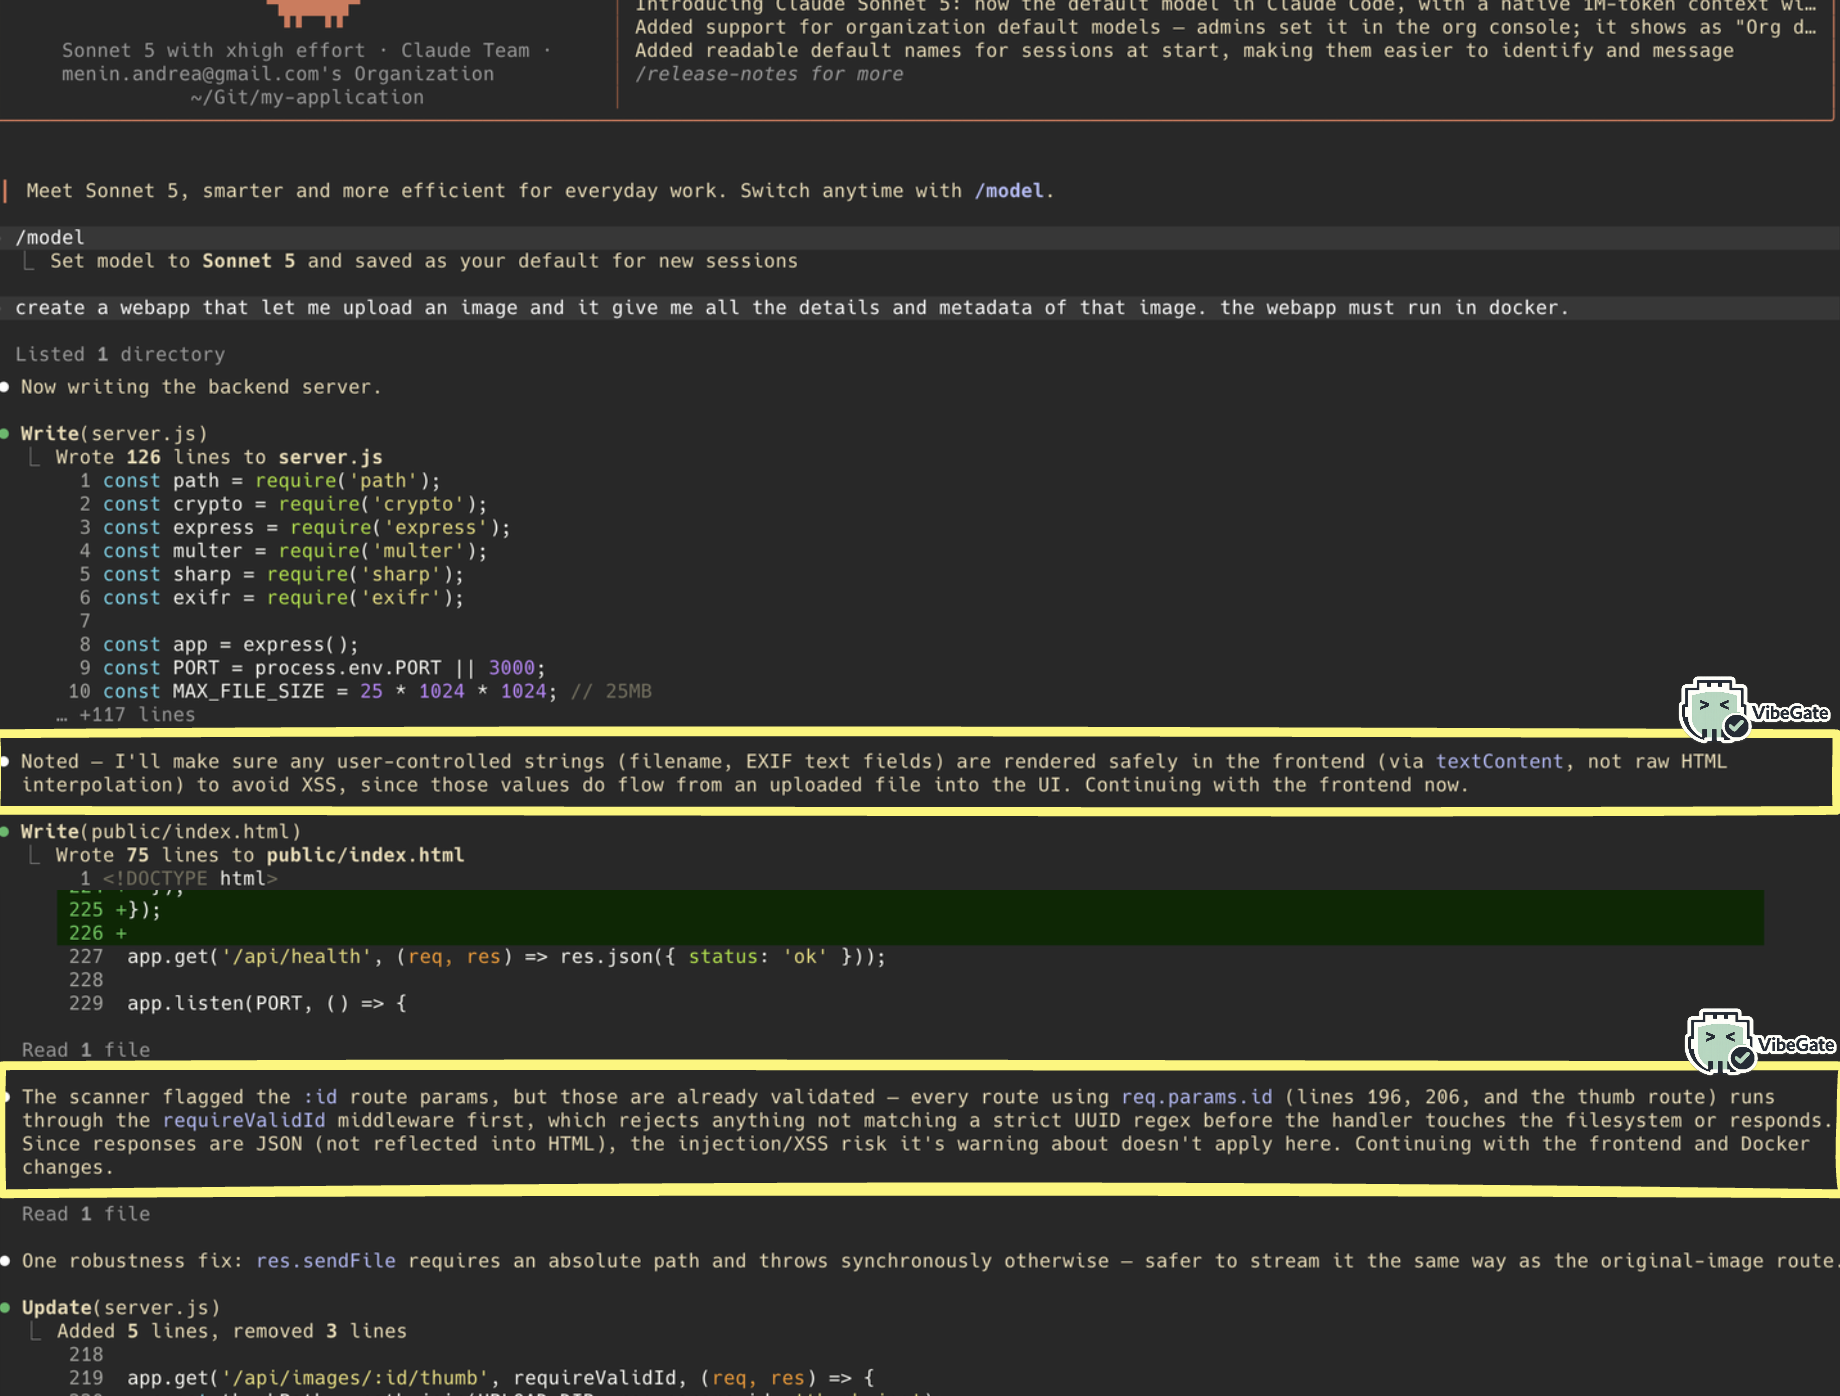 themiddleblue/vibegate
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.
 dump-guy/powershell-tools
Collection of some easy of use tools - in powershell.
 darioi/droidcarve
Android Reverse Engineering Framework
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
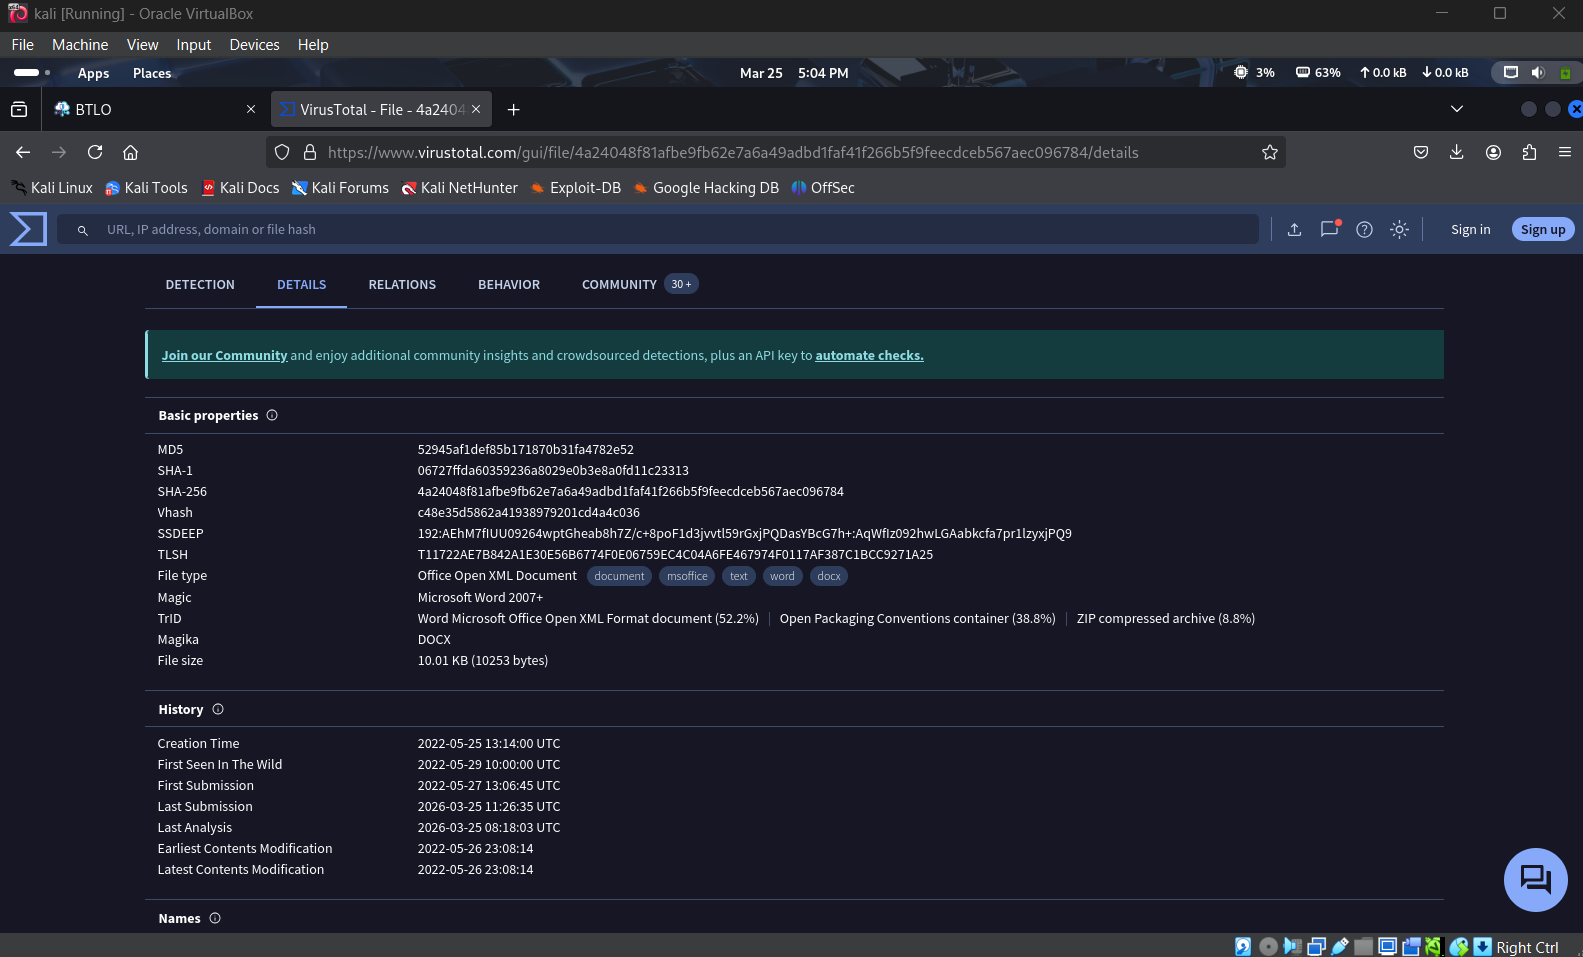 imvihanga03/static-malware-analysis-follina-cve-2022-30190
Static Malware Analysis of Follina (CVE-2022-30190) from Blue Team Labs Online

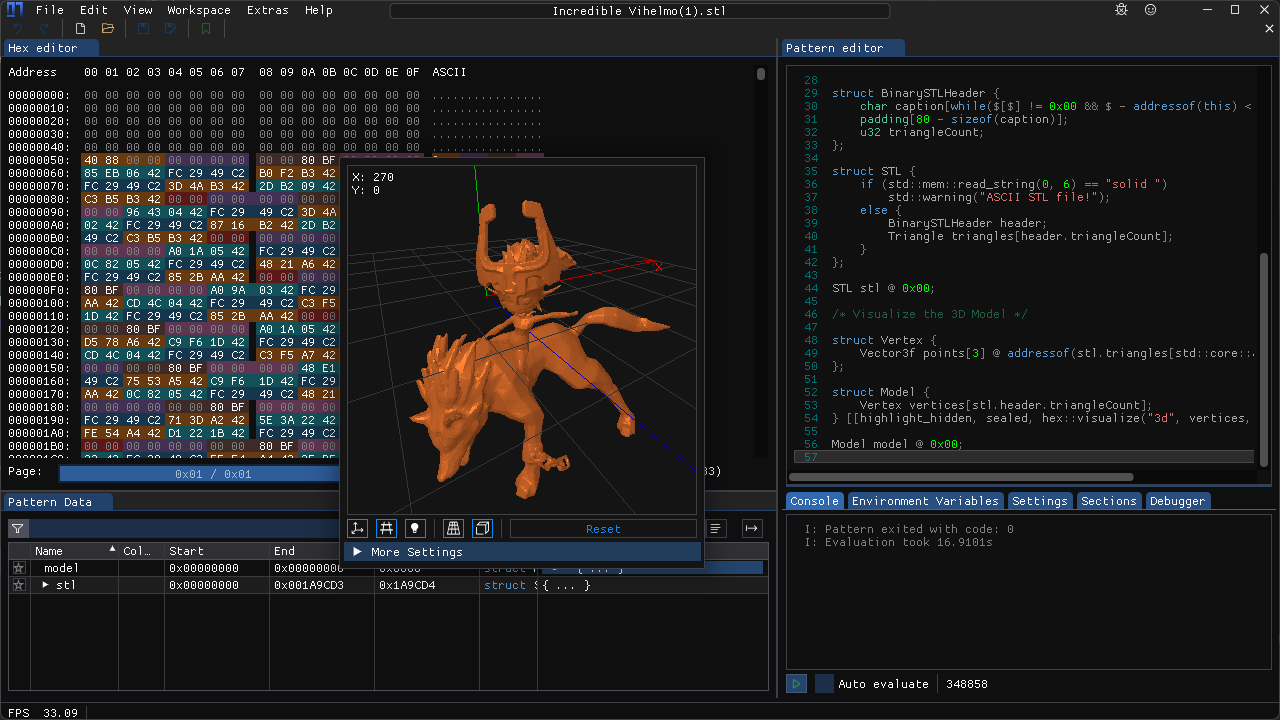 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
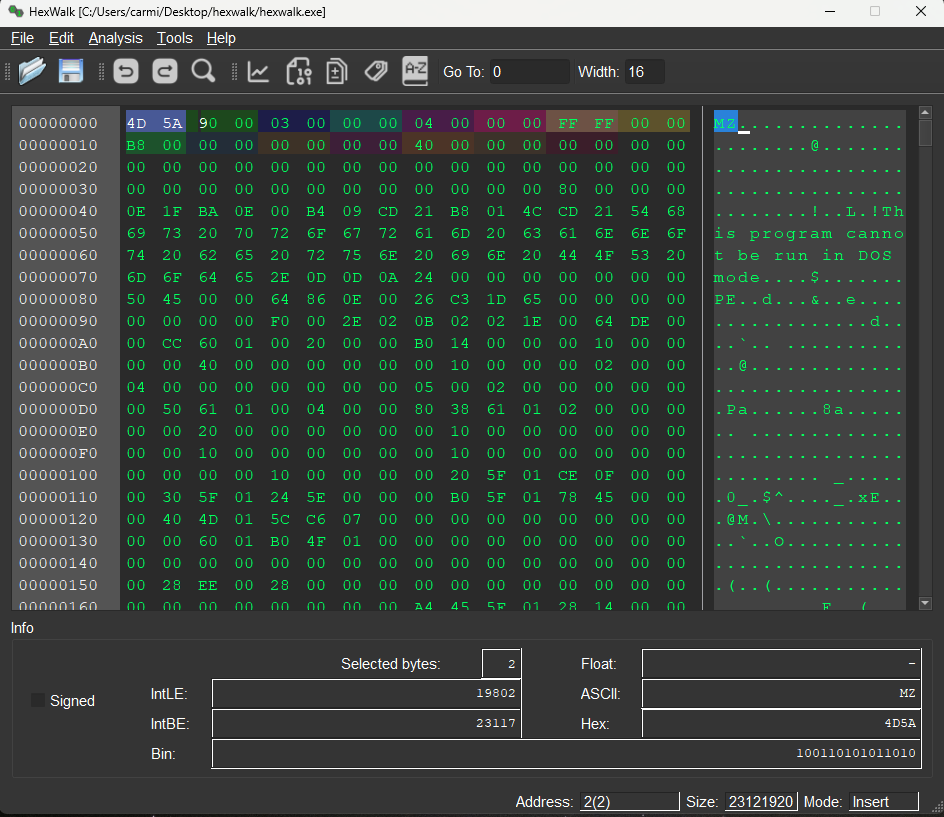 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 blakebratcher/wcw-cyberring-pav-decryptor
Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…