

pefile
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
binary-analysisforensicsmalware-analysis+3
erocarrera/pefilepefile is a Python module to read and work with PE (Portable Executable) files
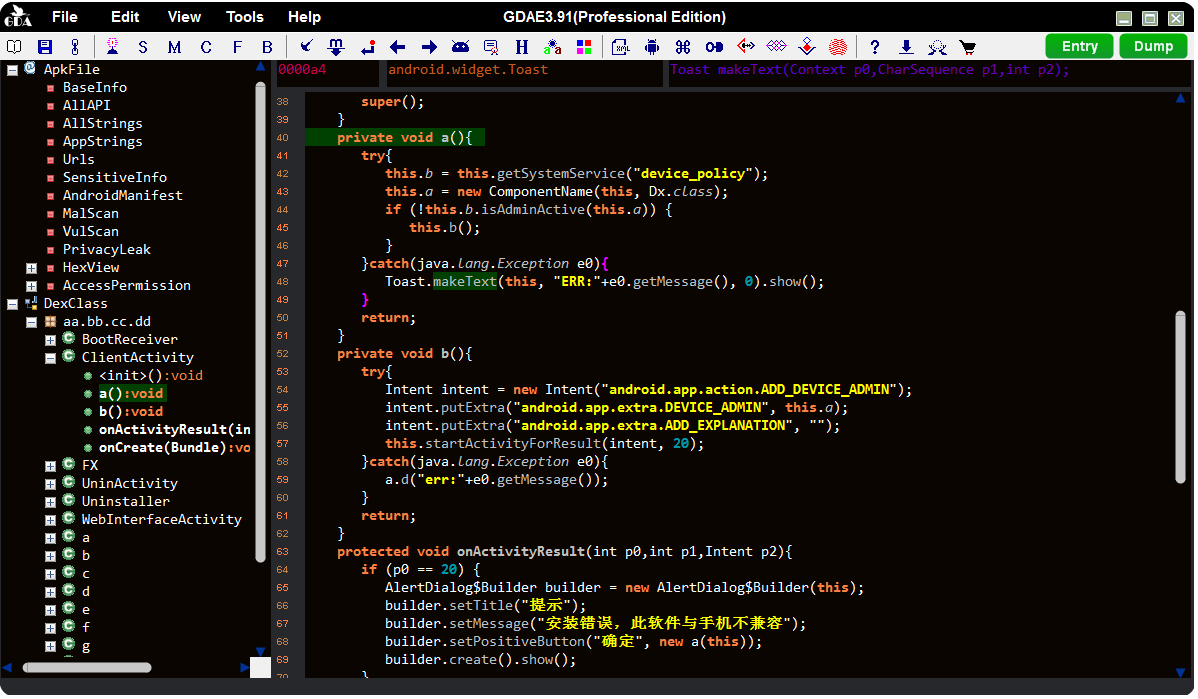 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 huhusmang/awesome-llms-for-vulnerability-detection
The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…
 dryxio/auto-re-agent
Reconstruct and validate C/C++ code from compiled programs with AI.
 betterleaks/betterleaks
Fast, configurable secrets scanner for filesystems, git history, containers, and cloud sources, with Expr-based filtering, credential validation, and…
 yelp/detect-secrets
An enterprise friendly way of detecting and preventing secrets in code.
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 decalage2/oletools
Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
 google/bindiff
Quickly find differences and similarities in disassembled code
 ev-flow/quark-engine
Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…
 user1342/awesome-android-reverse-engineering
A curated list of awesome Android Reverse Engineering training, resources, and tools.
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
 justicerage/manalyze
Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…
 nowsecure/r2frida
Radare2 and Frida better together.
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
 facebook/mariana-trench
A security focused static analysis tool for Android and Java applications.