
vimana-framework
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
api-securityapi-security-testingcrawler+9
66
s4dhulabs/vimana-frameworkVimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 baiduxlab/sgxray
Automated reasoning tool based on the SMACK verifier that detects SGX enclave bugs from trusted boundary violations, including invalid pointer…
 bogdanticu88/threatmap
IaC threat modeler with STRIDE, MITRE ATT&CK, and PASTA frameworks. REST API, GraphQL, and Docker support for Terraform, CloudFormation, and…
 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 n7on/dllspy
Discover input surfaces and security issues in compiled .NET assemblies — without running them.
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
 loadingalias/rscrypto
Rust crypto w/ zero default deps: BLAKE3, Ed25519/X25519, hashes, MACs, KDFs, AEADs, and checksums w/ full SIMD/ASM acceleration
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
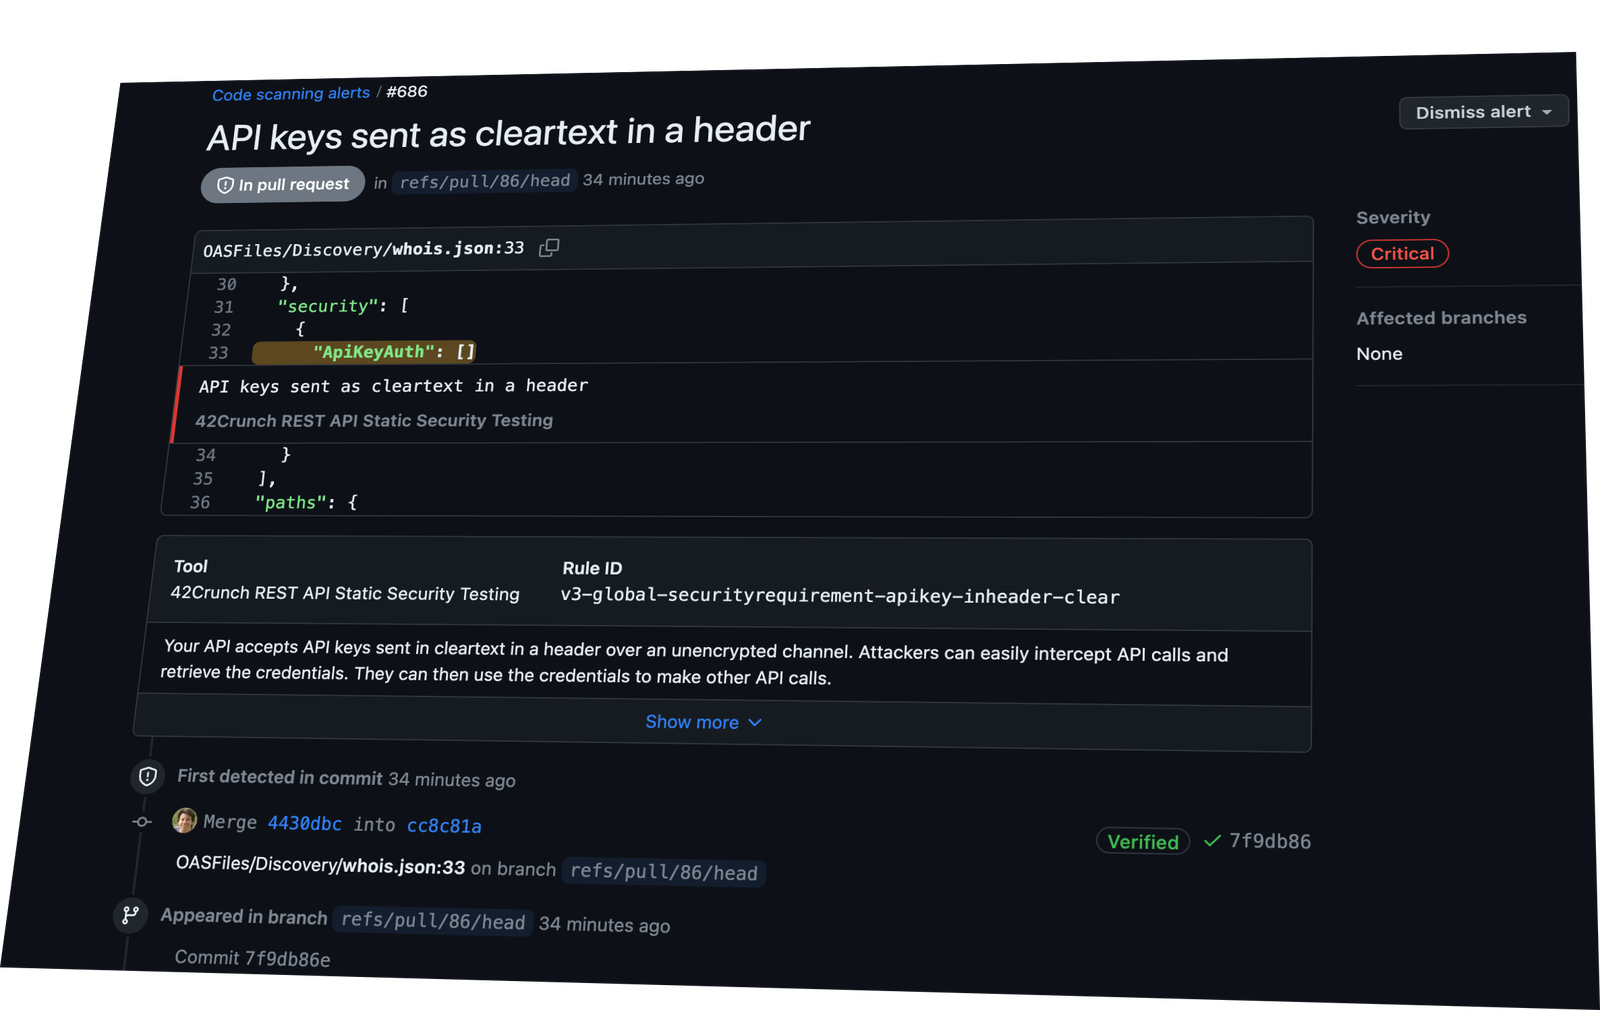 42crunch/api-security-audit-action
Automates static API security auditing of OpenAPI contracts in CI/CD, running 300+ checks for authentication, authorization, and data constraints,…
 saint0x/fzy
a systems programming language prioritizing verifiable correctness, determinism, and performance
 p0pr0ck5/lua-ffi-libinjection
LuaJIT FFI bindings for libinjection, providing SQL injection and XSS detection with context-specific APIs for web application security.
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
 xteardx/diaphora-mcp
MCP server for automated binary diffing.
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.