

Archived
enjarify
 google/enjarify
Translates Dalvik bytecode (DEX/APK) to equivalent Java bytecode, enabling Java analysis tools to process Android applications with high correctness…
android-securitybinary-analysiscode-analysis+3
 rtkwlf/wolf-tools
Scans Windows, Linux, and macOS hosts for Java packages containing JndiLookup.class to detect Log4Shell (CVE-2021-44228, CVE-2021-45046) exposure and…
 1n3/reverseapk
Quickly analyze and reverse engineer Android packages
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 client9/libinjection
SQL / SQLI tokenizer parser analyzer
 muellerberndt/apkx
One-Step APK Decompilation With Multiple Backends
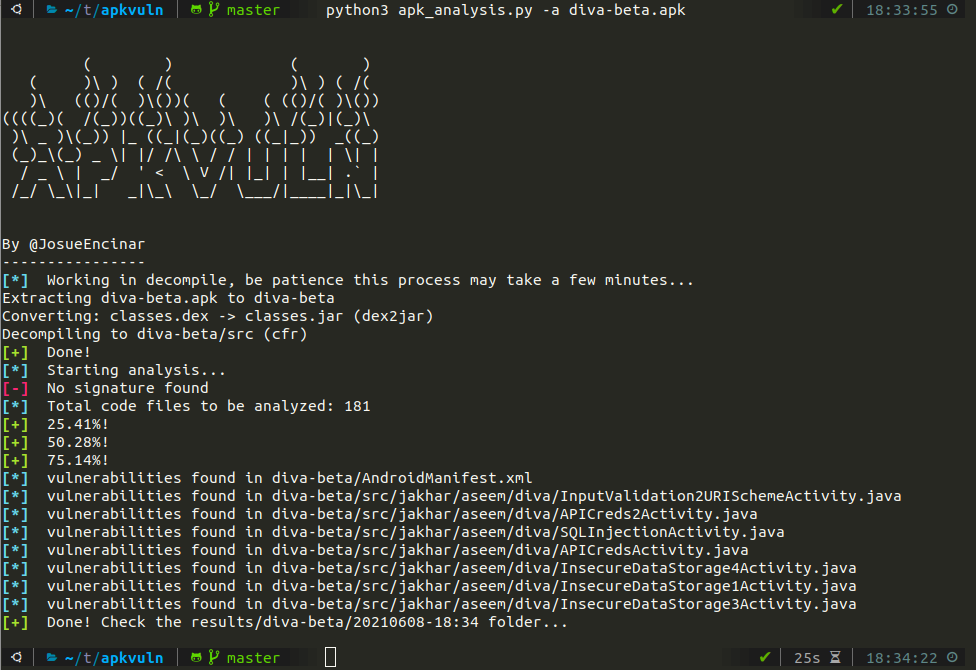 josue87/apkvuln
Static analysis of APKs with regular expressions
 oscerd/cve-2026-40048
Reproducer for CVE-2026-40048: Apache Camel camel-pqc FileBasedKeyLifecycleManager unsafe deserialization (RCE)
 mbadanoiu/cve-2021-46364
CVE-2021-46364: YAML Deserialization in Magnolia CMS
 rashedhasan090/aegisjava
I have created AegisJava, a tool to fix (detect and mitigate) CVE-2025-30749.
 iris-sast/zip4j
CWE-Bench-Java CVE-2018-1002202 versions 1.3.2, 1.3.3
 mario-kart-felix/a-potential-denial-of-service-issue-in-protobuf-java
Detailed analysis of CVE-2021-22569, a high-severity denial-of-service vulnerability in protobuf-java, including affected versions, patched versions,…
 epicosy/vul4j-59
Reproducible CVE-2015-6748 vulnerability example in jsoup HTML parser, demonstrating XSS prevention bypass and DOM-based parsing flaws for security…
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
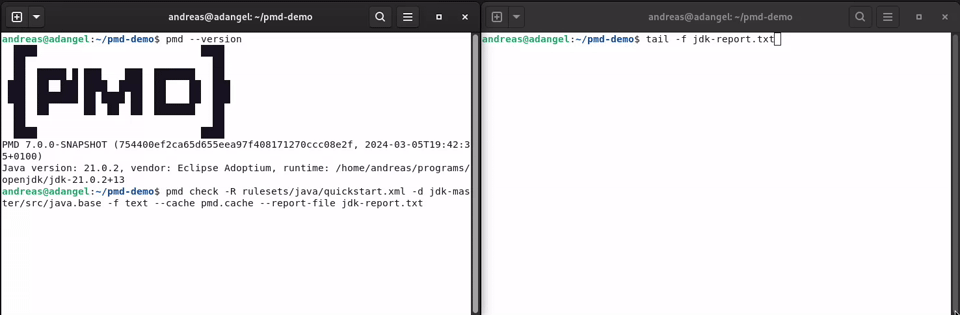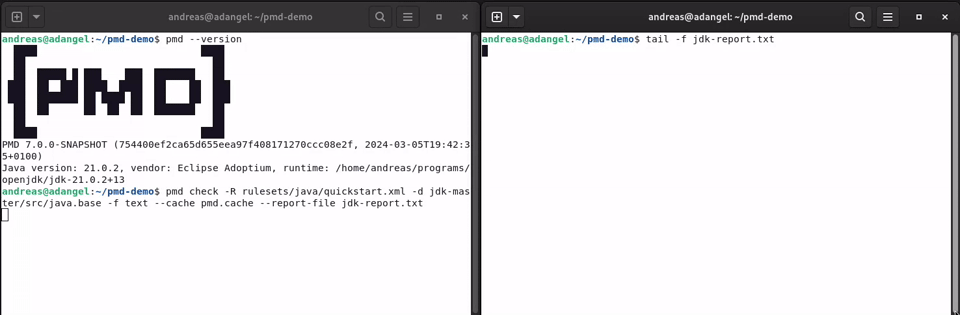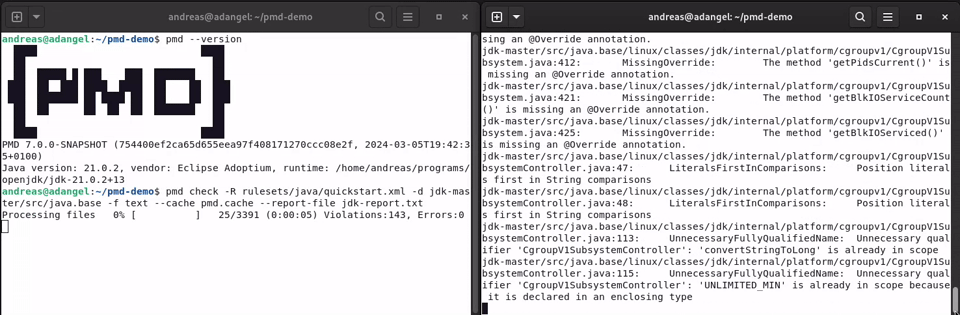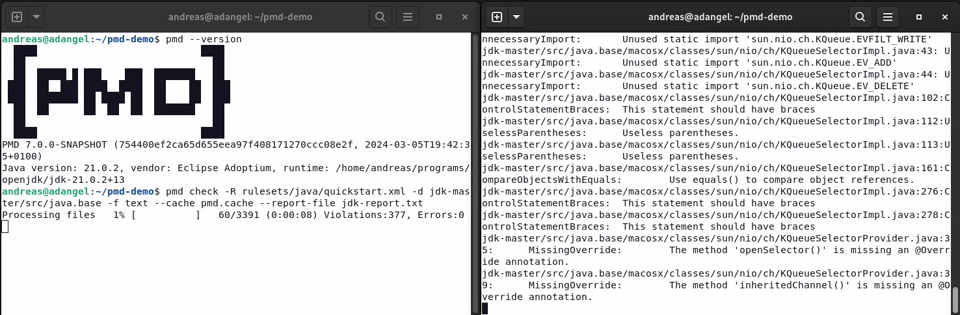 pmd/pmd
An extensible multilanguage static code analyzer.
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
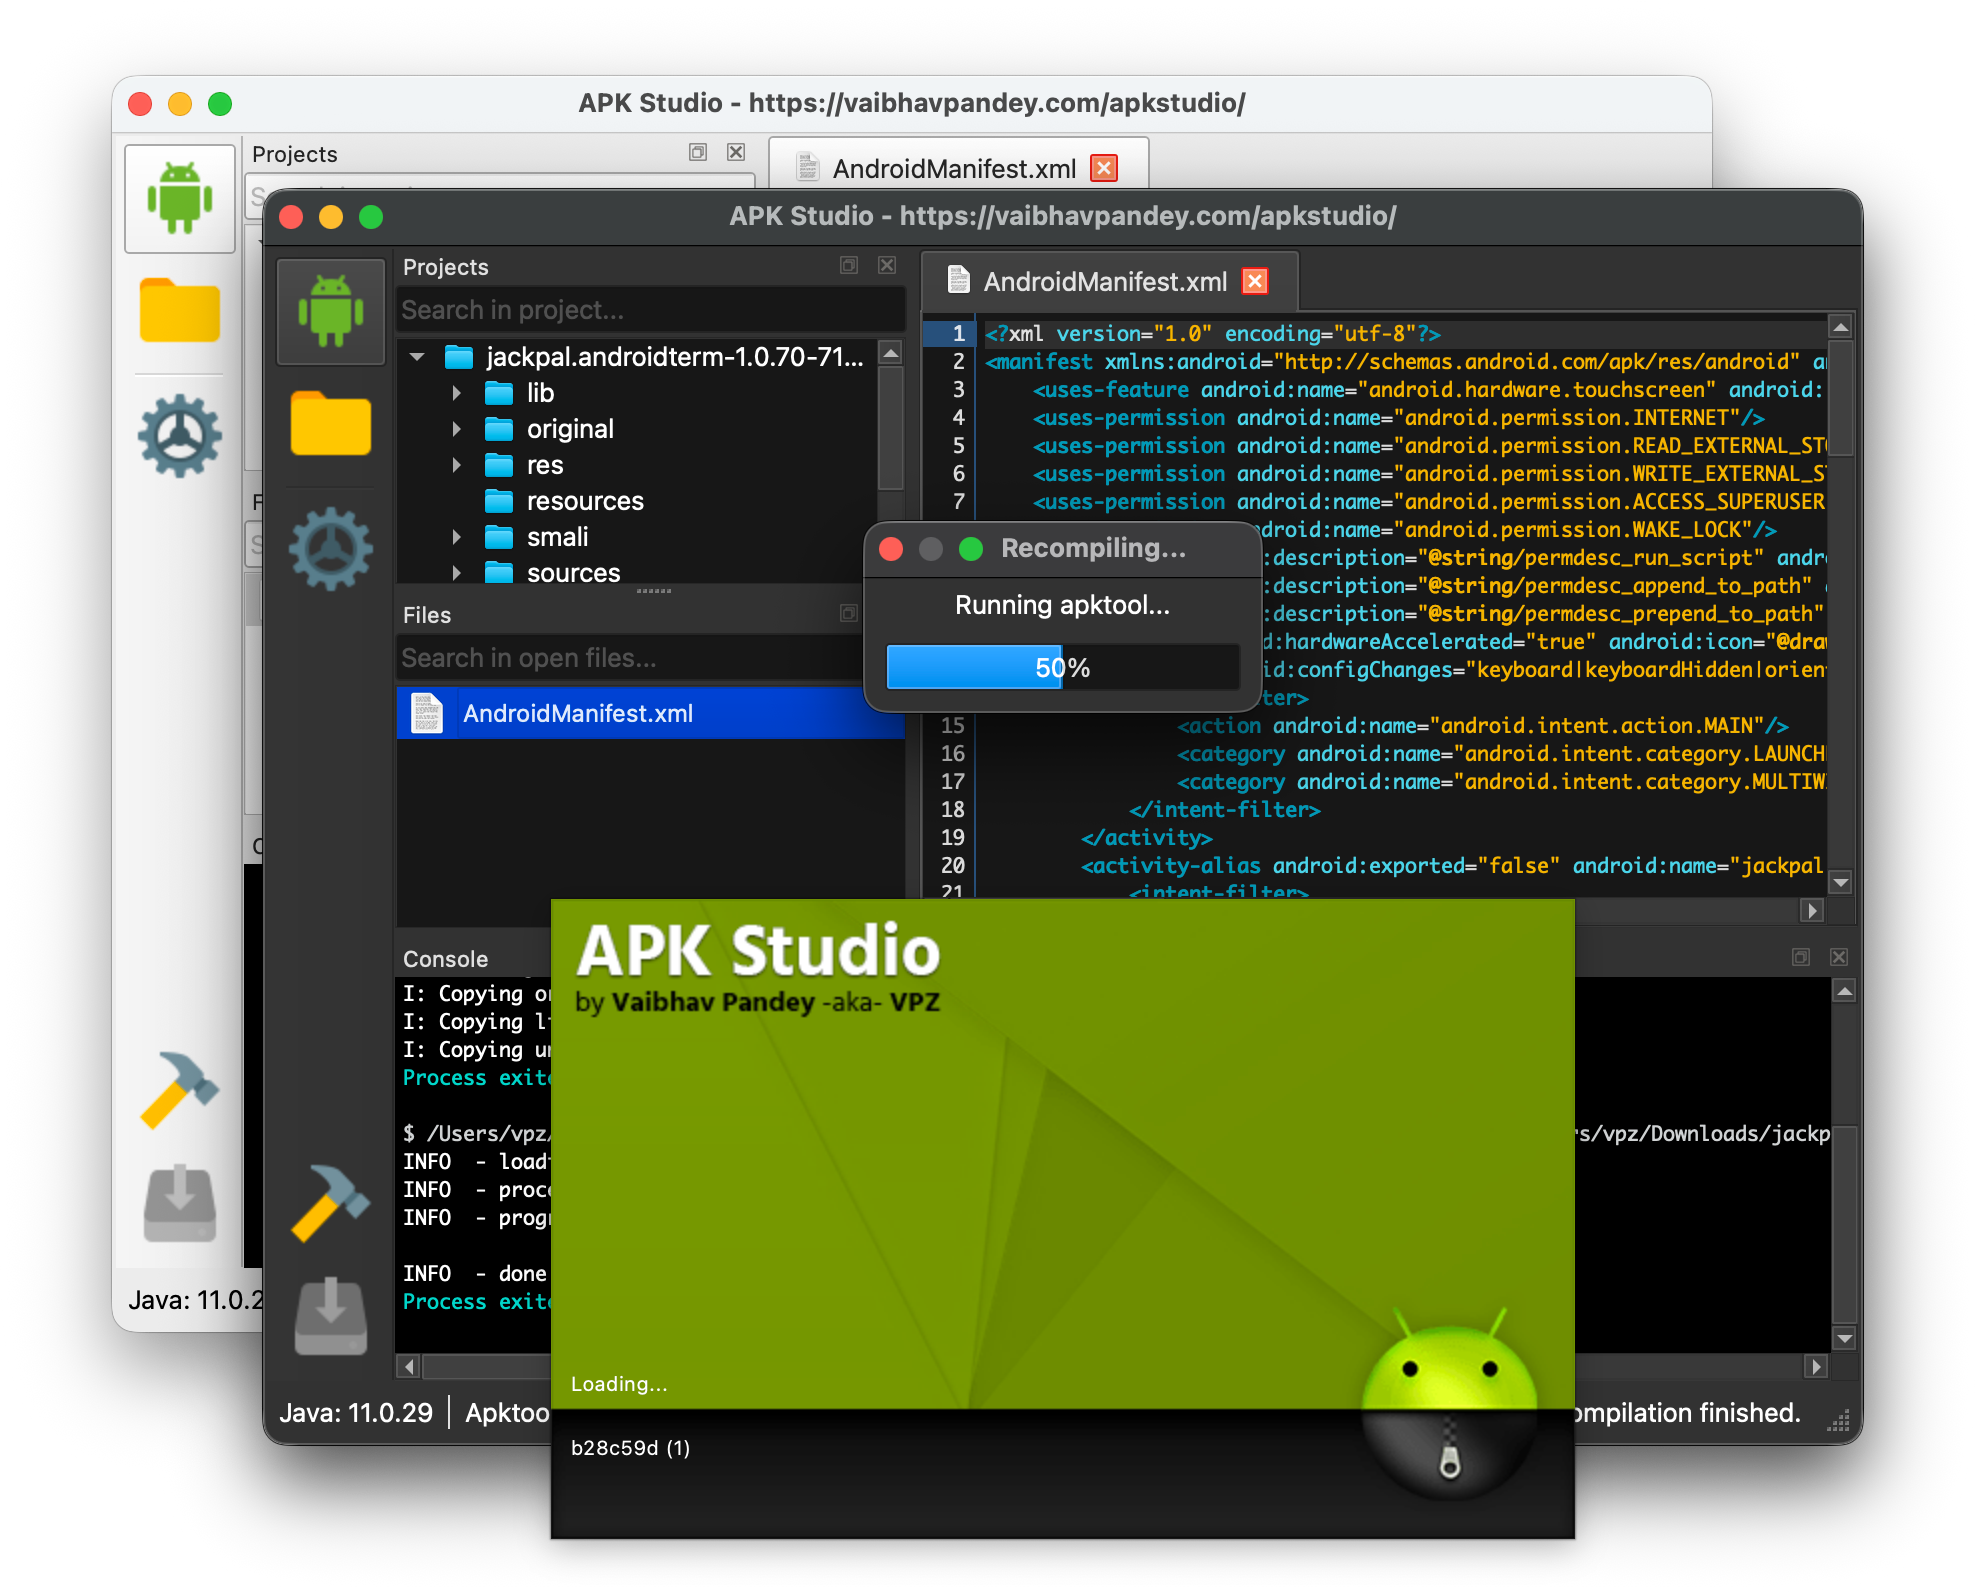 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…