
Dnstracer-1.9-Fix
 j0lama/dnstracer-1.9-fix
Patched version of dnstracer fixing CVE-2017-9430 stack-based buffer overflow via argv[0] length validation. Traces DNS server chains for hostname…
binary-analysisdns-analysisexploitation+2
j0lama/dnstracer-1.9-fixPatched version of dnstracer fixing CVE-2017-9430 stack-based buffer overflow via argv[0] length validation. Traces DNS server chains for hostname…
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
 certcc/cve-2021-44228_scanner
Scanners for Jar files that may be vulnerable to CVE-2021-44228
 felixber/findfunc
IDA Pro plugin for filtering functions by assembly patterns, byte sequences, string/name references, and size constraints, with rule-based search and…
 anteater/anteater
Anteater - CI/CD Gate Check Framework
 pierdipi/unicode-control-characters-action
A GitHub Action to find Unicode control characters using the Red Hat diagnostic tool https://access.redhat.com/security/vulnerabilities/RHSB-2021-007…
 tarantula-team/cve-2019-19203
An issue was discovered in Oniguruma 6.x before 6.9.4_rc2. In the function gb18030_mbc_enc_len in file gb18030.c, a UChar pointer is dereferenced…
 rustynoob-619/100-days-of-yara-2026
The 100 Days of YARA Challenge to write YARA rules consistently
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
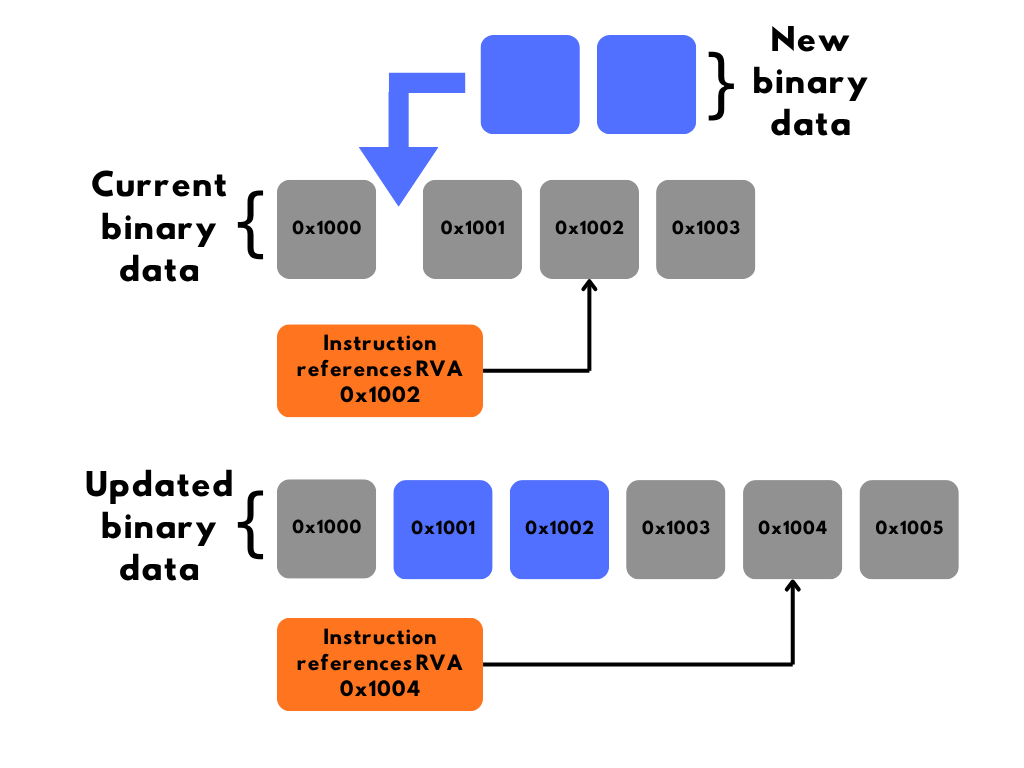 noahware/binprotect
x64 PE bin2bin obfuscator which doesn't add a section to the binary
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 trailofbits/semgrep-rules
Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
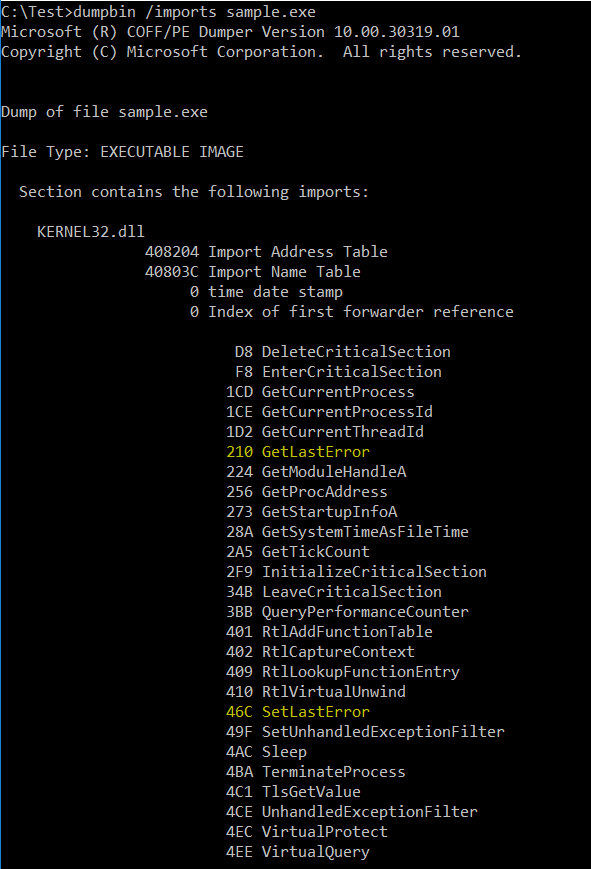 d35ha/callobfuscator
Obfuscate specific windows apis with different apis
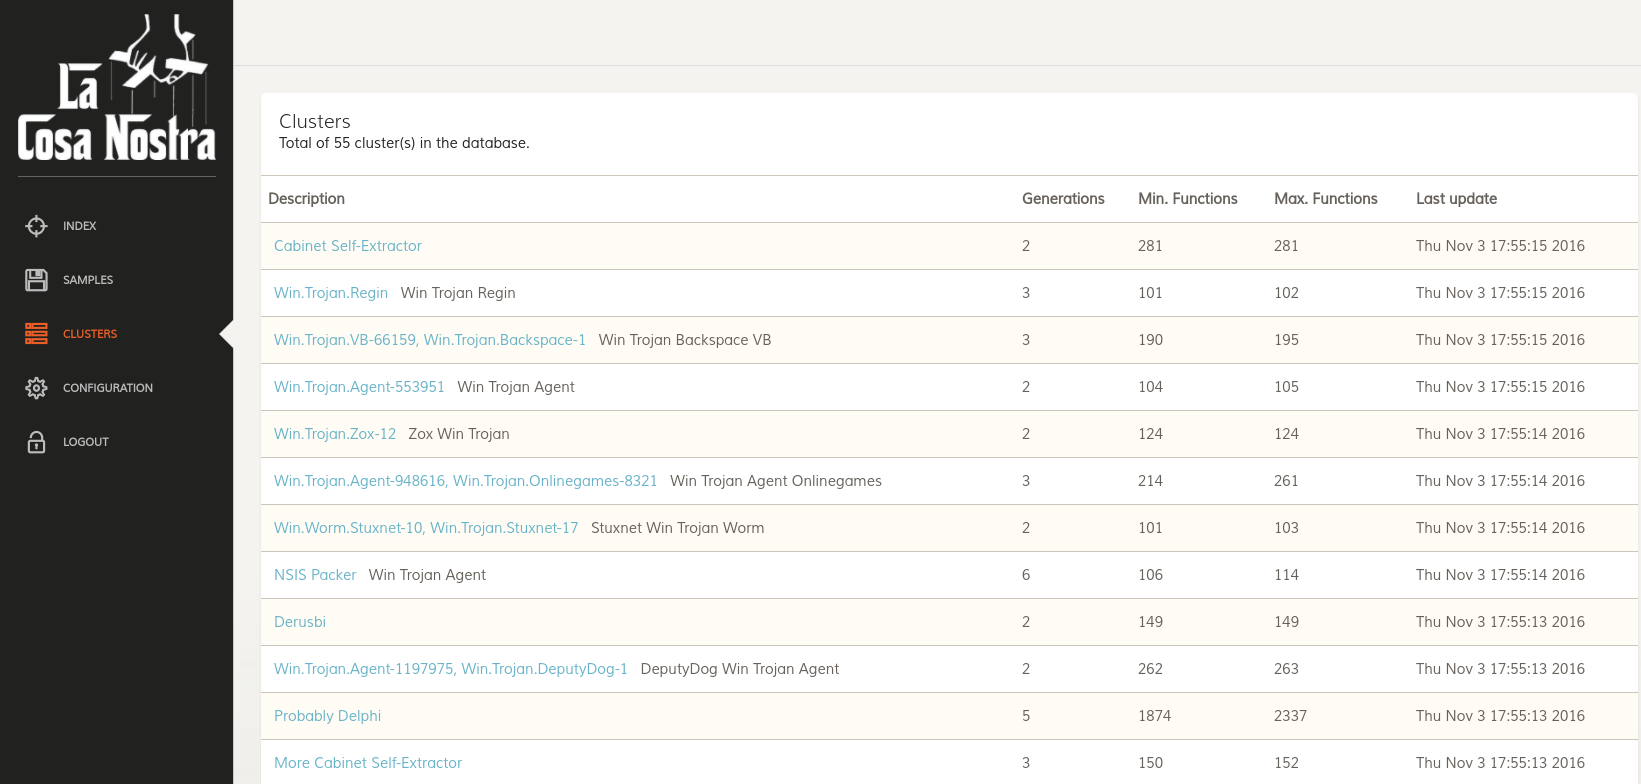 joxeankoret/cosa-nostra
Cosa Nostra, a FOSS graph based malware clusterization toolkit.
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)
 cdong1012/idapython-malware-scripts
Scripts for automating malware analysis and reverse engineering workflows in IDA Pro, covering binary inspection, static analysis, and code…
 killercd/cve-2026-35414
Demonstrates a proof-of-concept for CVE-2026-35414, showing a vulnerable and fixed version of SSH principal matching logic to illustrate the flaw.
 tronciuvlad/cve-2024-26475
An issue in radareorg radare2 v.0.9.7 through v.5.8.6 and fixed in v.5.8.8 allows a local attacker to cause a denial of service via the…