
sqlite-fts5-securedel
 abraxas/sqlite-fts5-securedel
SQLite 3.53.4 - High - Local - Crash - FTS5 secure-delete PutVarint footer overrun
binary-analysisdatabase-securityexploitation+5
abraxas/sqlite-fts5-securedelSQLite 3.53.4 - High - Local - Crash - FTS5 secure-delete PutVarint footer overrun
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 abraxas/sqlite-cte-nest
SQLite 3.53.4 - High - Local - Crash - nested CTEs skip nNestSel view-depth cap
 abraxas/sqlite-collate-depth
SQLite 3.53.4 - High - Local - Crash - COLLATE chain skips SQLITE_LIMIT_EXPR_DEPTH
 iulianvostrut/contexthound
Static analysis CLI that scans codebases for LLM prompt-injection, data-exfiltration, jailbreak, and unsafe agent/tool vulnerabilities. Runs fully…
 shalevo13/se7enslip
A scanner and testter of the CVE-2025-11001 of 7-zip
 bytespulse-oe/wp2shell-hestia-scanner
Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…
 trg-1999/detectpacket-cve-2017-8464
Exploit vulnerabilities and vulnerability prevention implementation
 ilhomjonr/cve-2026-67595
CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.
 xiaoqimikko/netty-resolver-dns-check
Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…
 eqstlab/cve-2026-30951
Sequelize JSON Cast SQL Injection
 bybravehq/ip2
Maintained fork of node-ip with the unpatched SSRF advisory (CVE-2024-29415) fixed
 loic-houchi/django-faille-cve-2025-57833_test
Educational proof-of-concept demonstrating SQL injection via dynamic aliases in Django's annotate() and alias() methods (CVE-2025-57833). Includes…
 j0lama/dnstracer-1.9-fix
Patched version of dnstracer fixing CVE-2017-9430 stack-based buffer overflow via argv[0] length validation. Traces DNS server chains for hostname…
 calusdotai/anticipator
Anticipator is an open-source threat detection platform for multi-agent AI systems.
 bde574786/sequelize-1day-cve-2023-25813
Proof-of-concept and technical analysis of CVE-2023-25813, a SQL injection vulnerability in Sequelize ORM versions prior to 6.19.1, including…
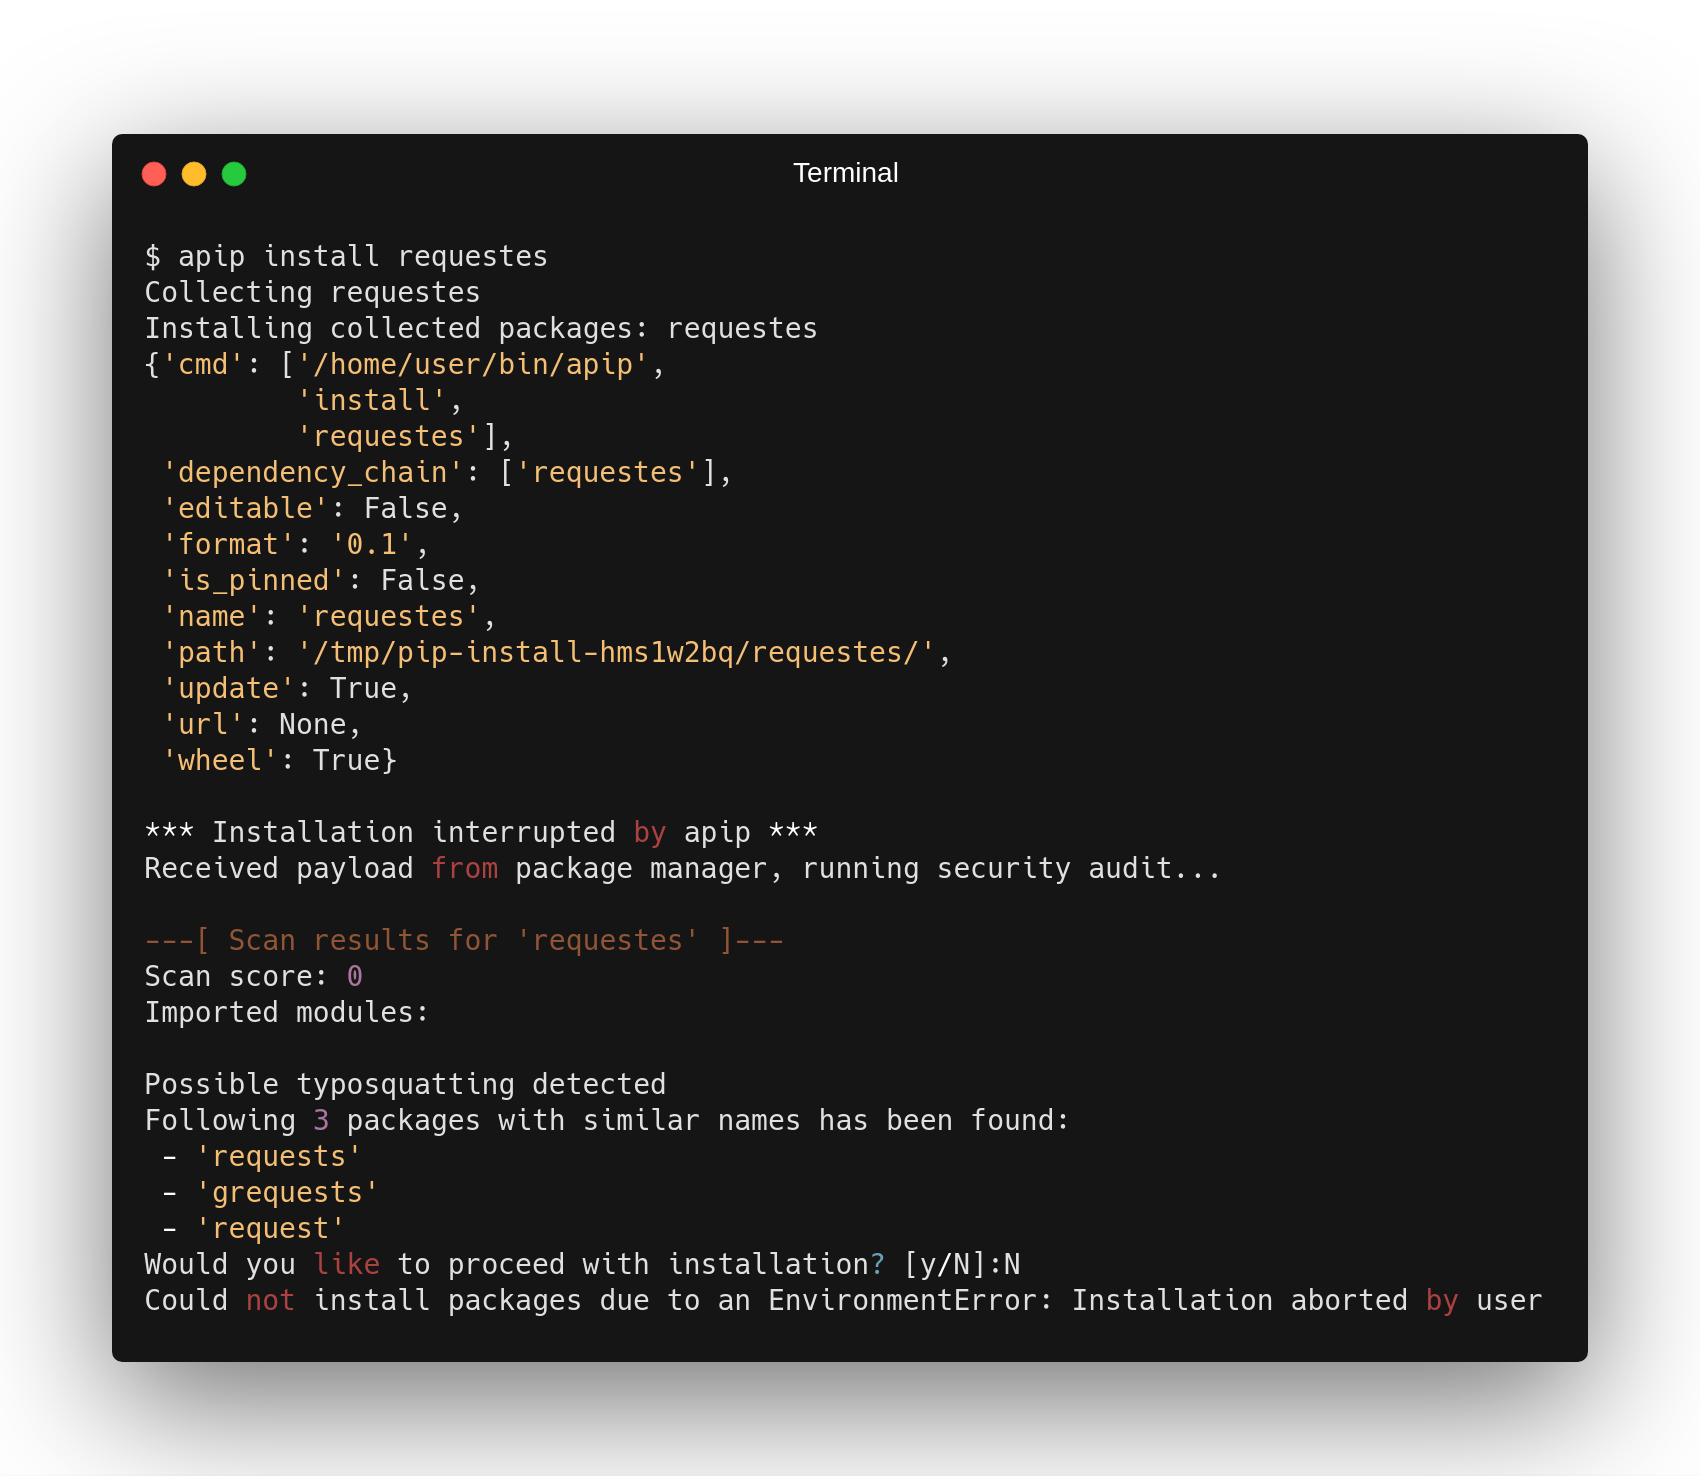 rootlug/aura
Project Aura: Security auditing and code introspection
 msuiche/hotcell
Runtime exploit monitor for Apple document/image pipelines (iOS/macOS) — EXPMON concept: Frida agent + behavioral rules. First target: the…