
Sighthound
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
code-analysisdevsecopsmisconfiguration+4
275
corgea/sighthoundTree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 baiduxlab/sgxray
Automated reasoning tool based on the SMACK verifier that detects SGX enclave bugs from trusted boundary violations, including invalid pointer…
 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
 proteqtum/interactive-binary-structures
Interactive documentation and visual reference for binary formats and system memory layouts.
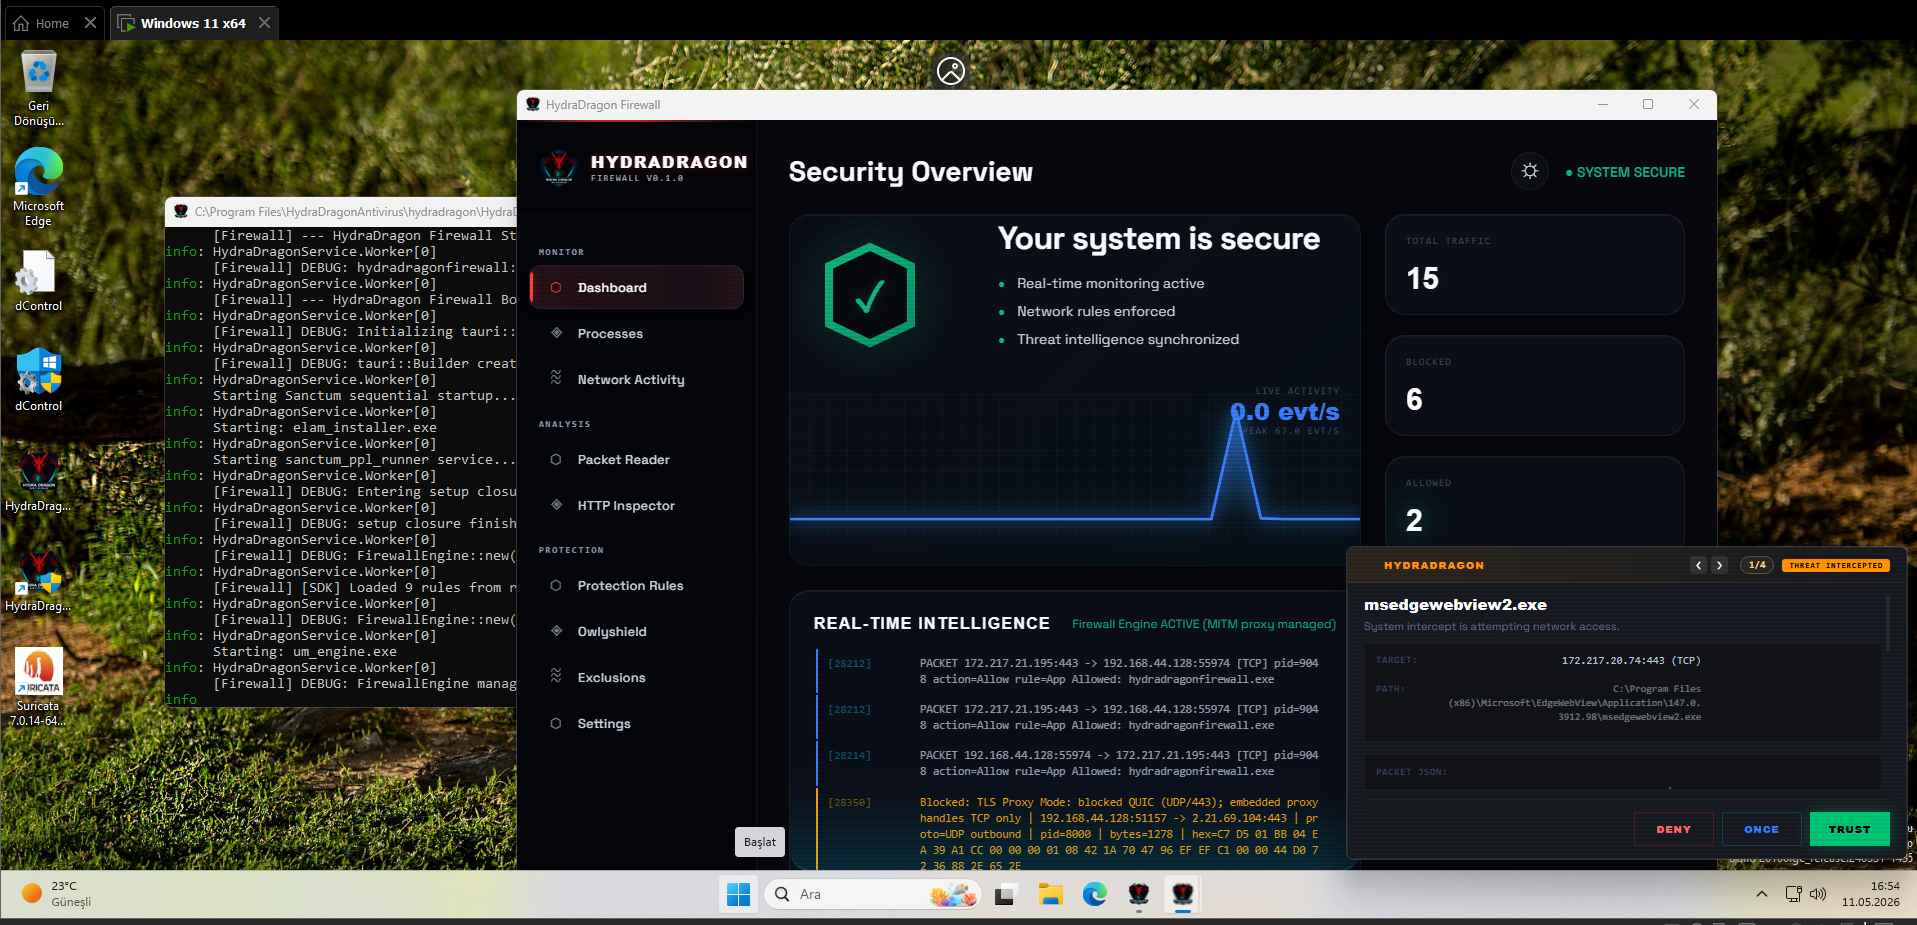 hydradragonantivirus/hydradragonantivirus
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
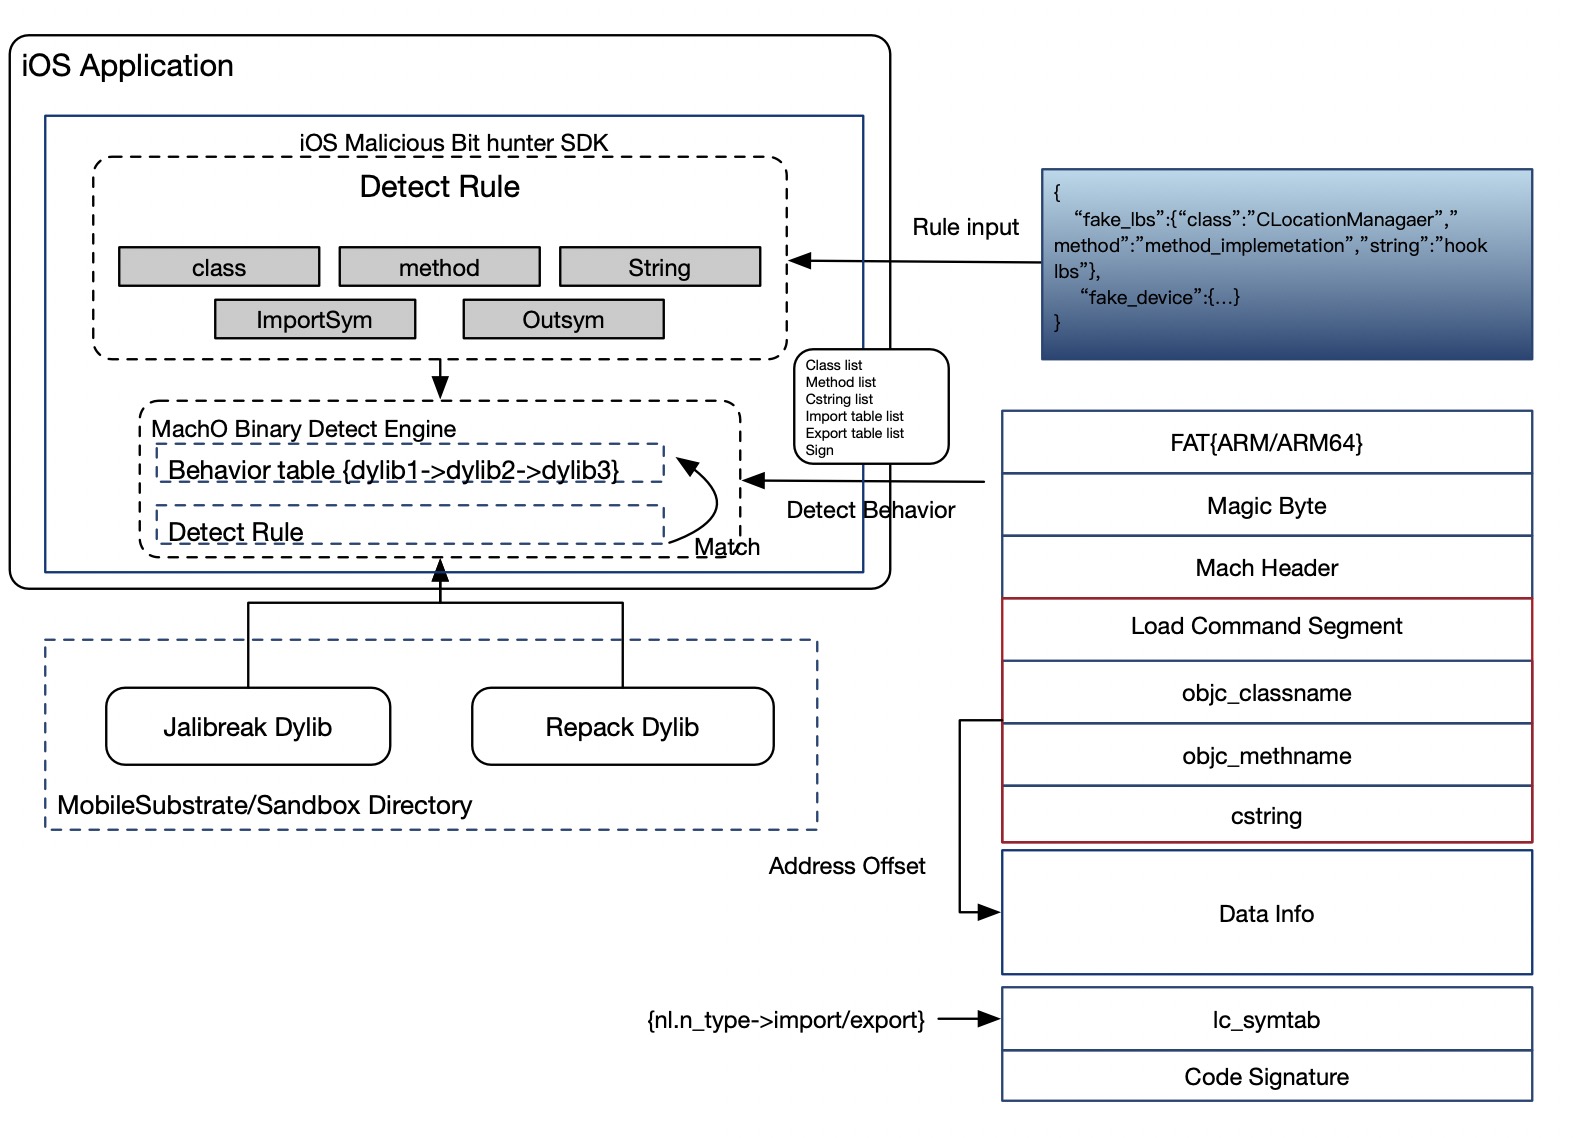 alipay/ios-malicious-bithunter
iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 quarkslab/qsynthesis
Greybox Synthesizer geared for deobfuscation of assembly instructions.
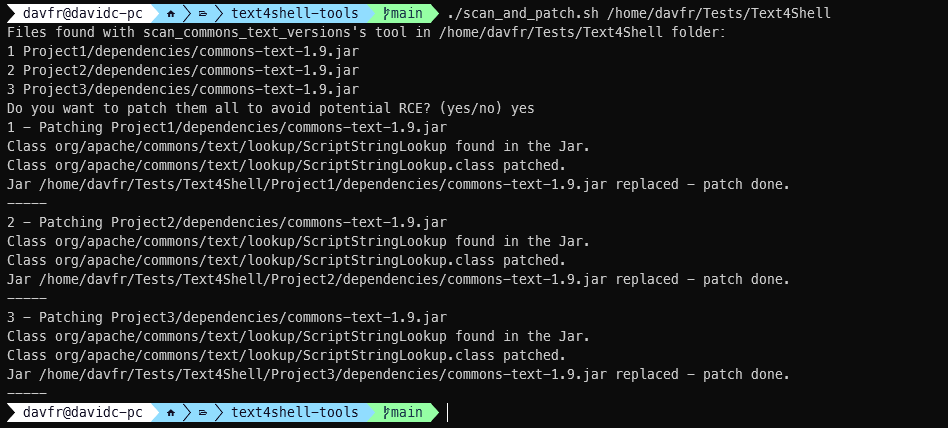 jfrog/text4shell-tools
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…
 vinsontang1/dcvd
The code in "DCVD: Dual-Channel Cross-Modal Fusion for Joint Vulnerability Detection and Localization"
 simota/nginx-rift-scanner
Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
 sexyshoelessgodofwar/cve-2025-47256
Stack overflow in LibXMP
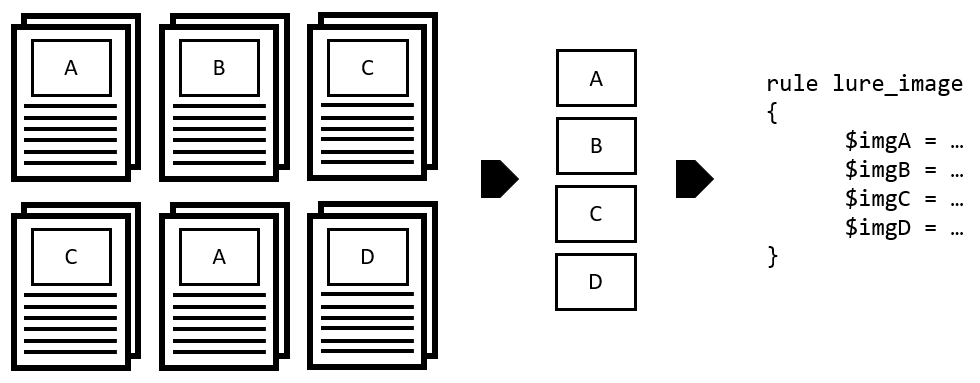 target/halogen
Automatically create YARA rules from malicious documents.
 avast/retdec
RetDec is a retargetable machine-code decompiler based on LLVM.
 colton1skees/dna
LLVM based static binary analysis framework
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing