

log4shelldetect
 1lann/log4shelldetect
Rapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…
code-analysismisconfigurationstatic-analysis+3
45
1lann/log4shelldetectRapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…
 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 paveg/rails-activestorage-vips-audit
Agent skill that audits a Rails codebase for CVE-2026-66066 (KindaRails2Shell) — Active Storage + libvips arbitrary file read / RCE, checking Rails…
 cahyod/react2shell
Alat ini mendeteksi potensi kerentanan React2Shell (CVE-2025-55182) dalam proyek React dengan memeriksa: - File `package.json` dan file lock untuk…
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
 haxatron/cve-2022-0219
Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
 mhaggis/package-inferno
A Public Package Scanner for The Community
 mitre/multiscanner
Modular file scanning/analysis framework
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
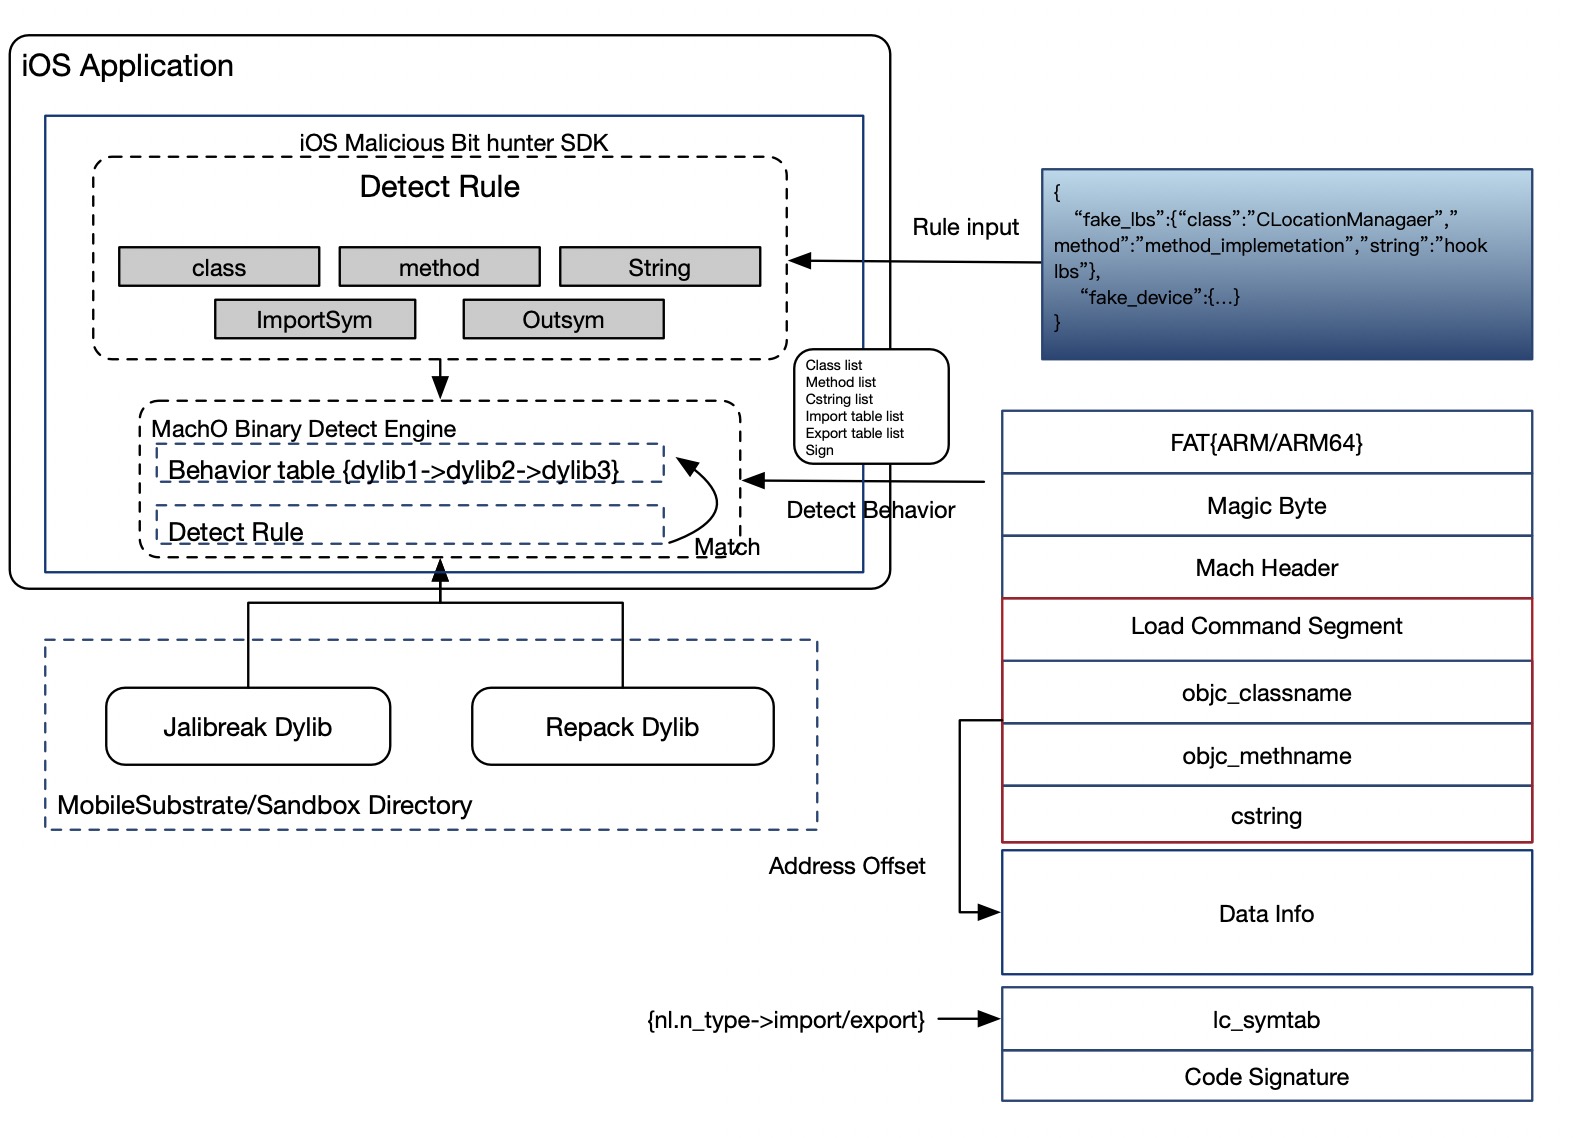 alipay/ios-malicious-bithunter
iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…
 redyank/cve-2026-29780
Demonstrates a path traversal vulnerability in an official eml-parser example script, allowing arbitrary file write via crafted attachment filenames,…
 arsalanraja987/java-cve-2021-29425-tika-xxe
Proof-of-concept exploit for CVE-2021-29425, an XML External Entity (XXE) vulnerability in Apache Tika, demonstrating file disclosure and SSRF via…
 tigr78/cve-2025-53964
Proof-of-concept exploit for CVE-2025-53964: remote file read/write via malicious XDXF dictionary in GoldenDict 1.5.0/1.5.1, leveraging unsanitized…
 jaycelation/cve-2026-25645
Insecure Temp File Reuse in extract_zipped_paths()