

gef
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
ai-assisted-reversingbinary-analysisbinary-exploitation+10
8.4k
hugsy/gefGEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
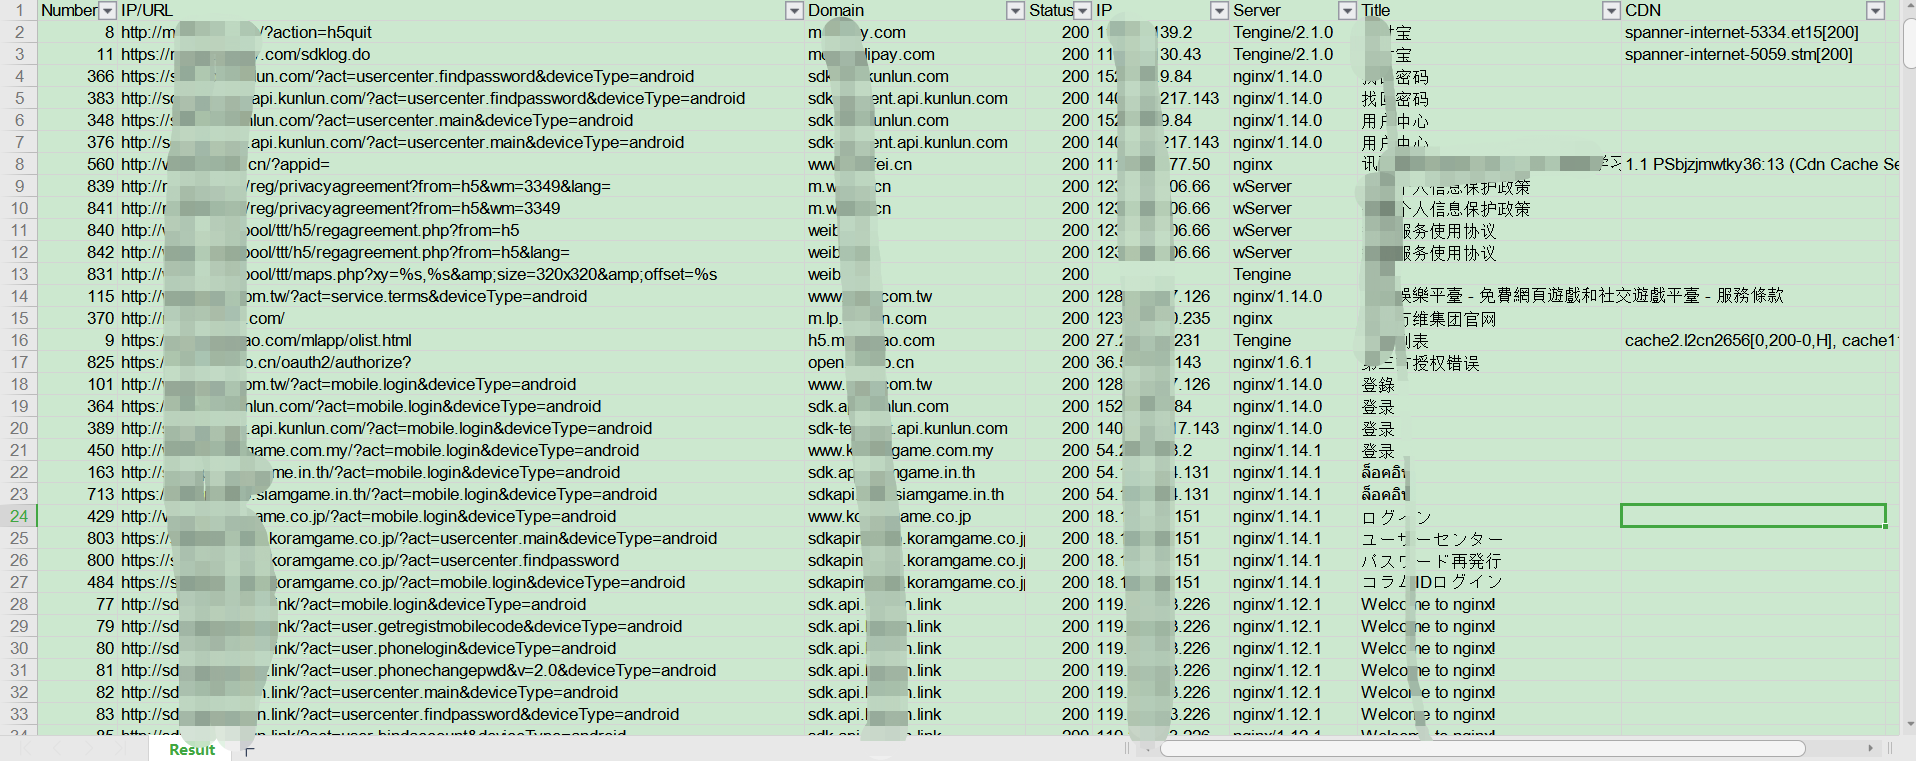 kelvinben/appinfoscanner
一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.

 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 user1342/awesome-android-reverse-engineering
A curated list of awesome Android Reverse Engineering training, resources, and tools.
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android

 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
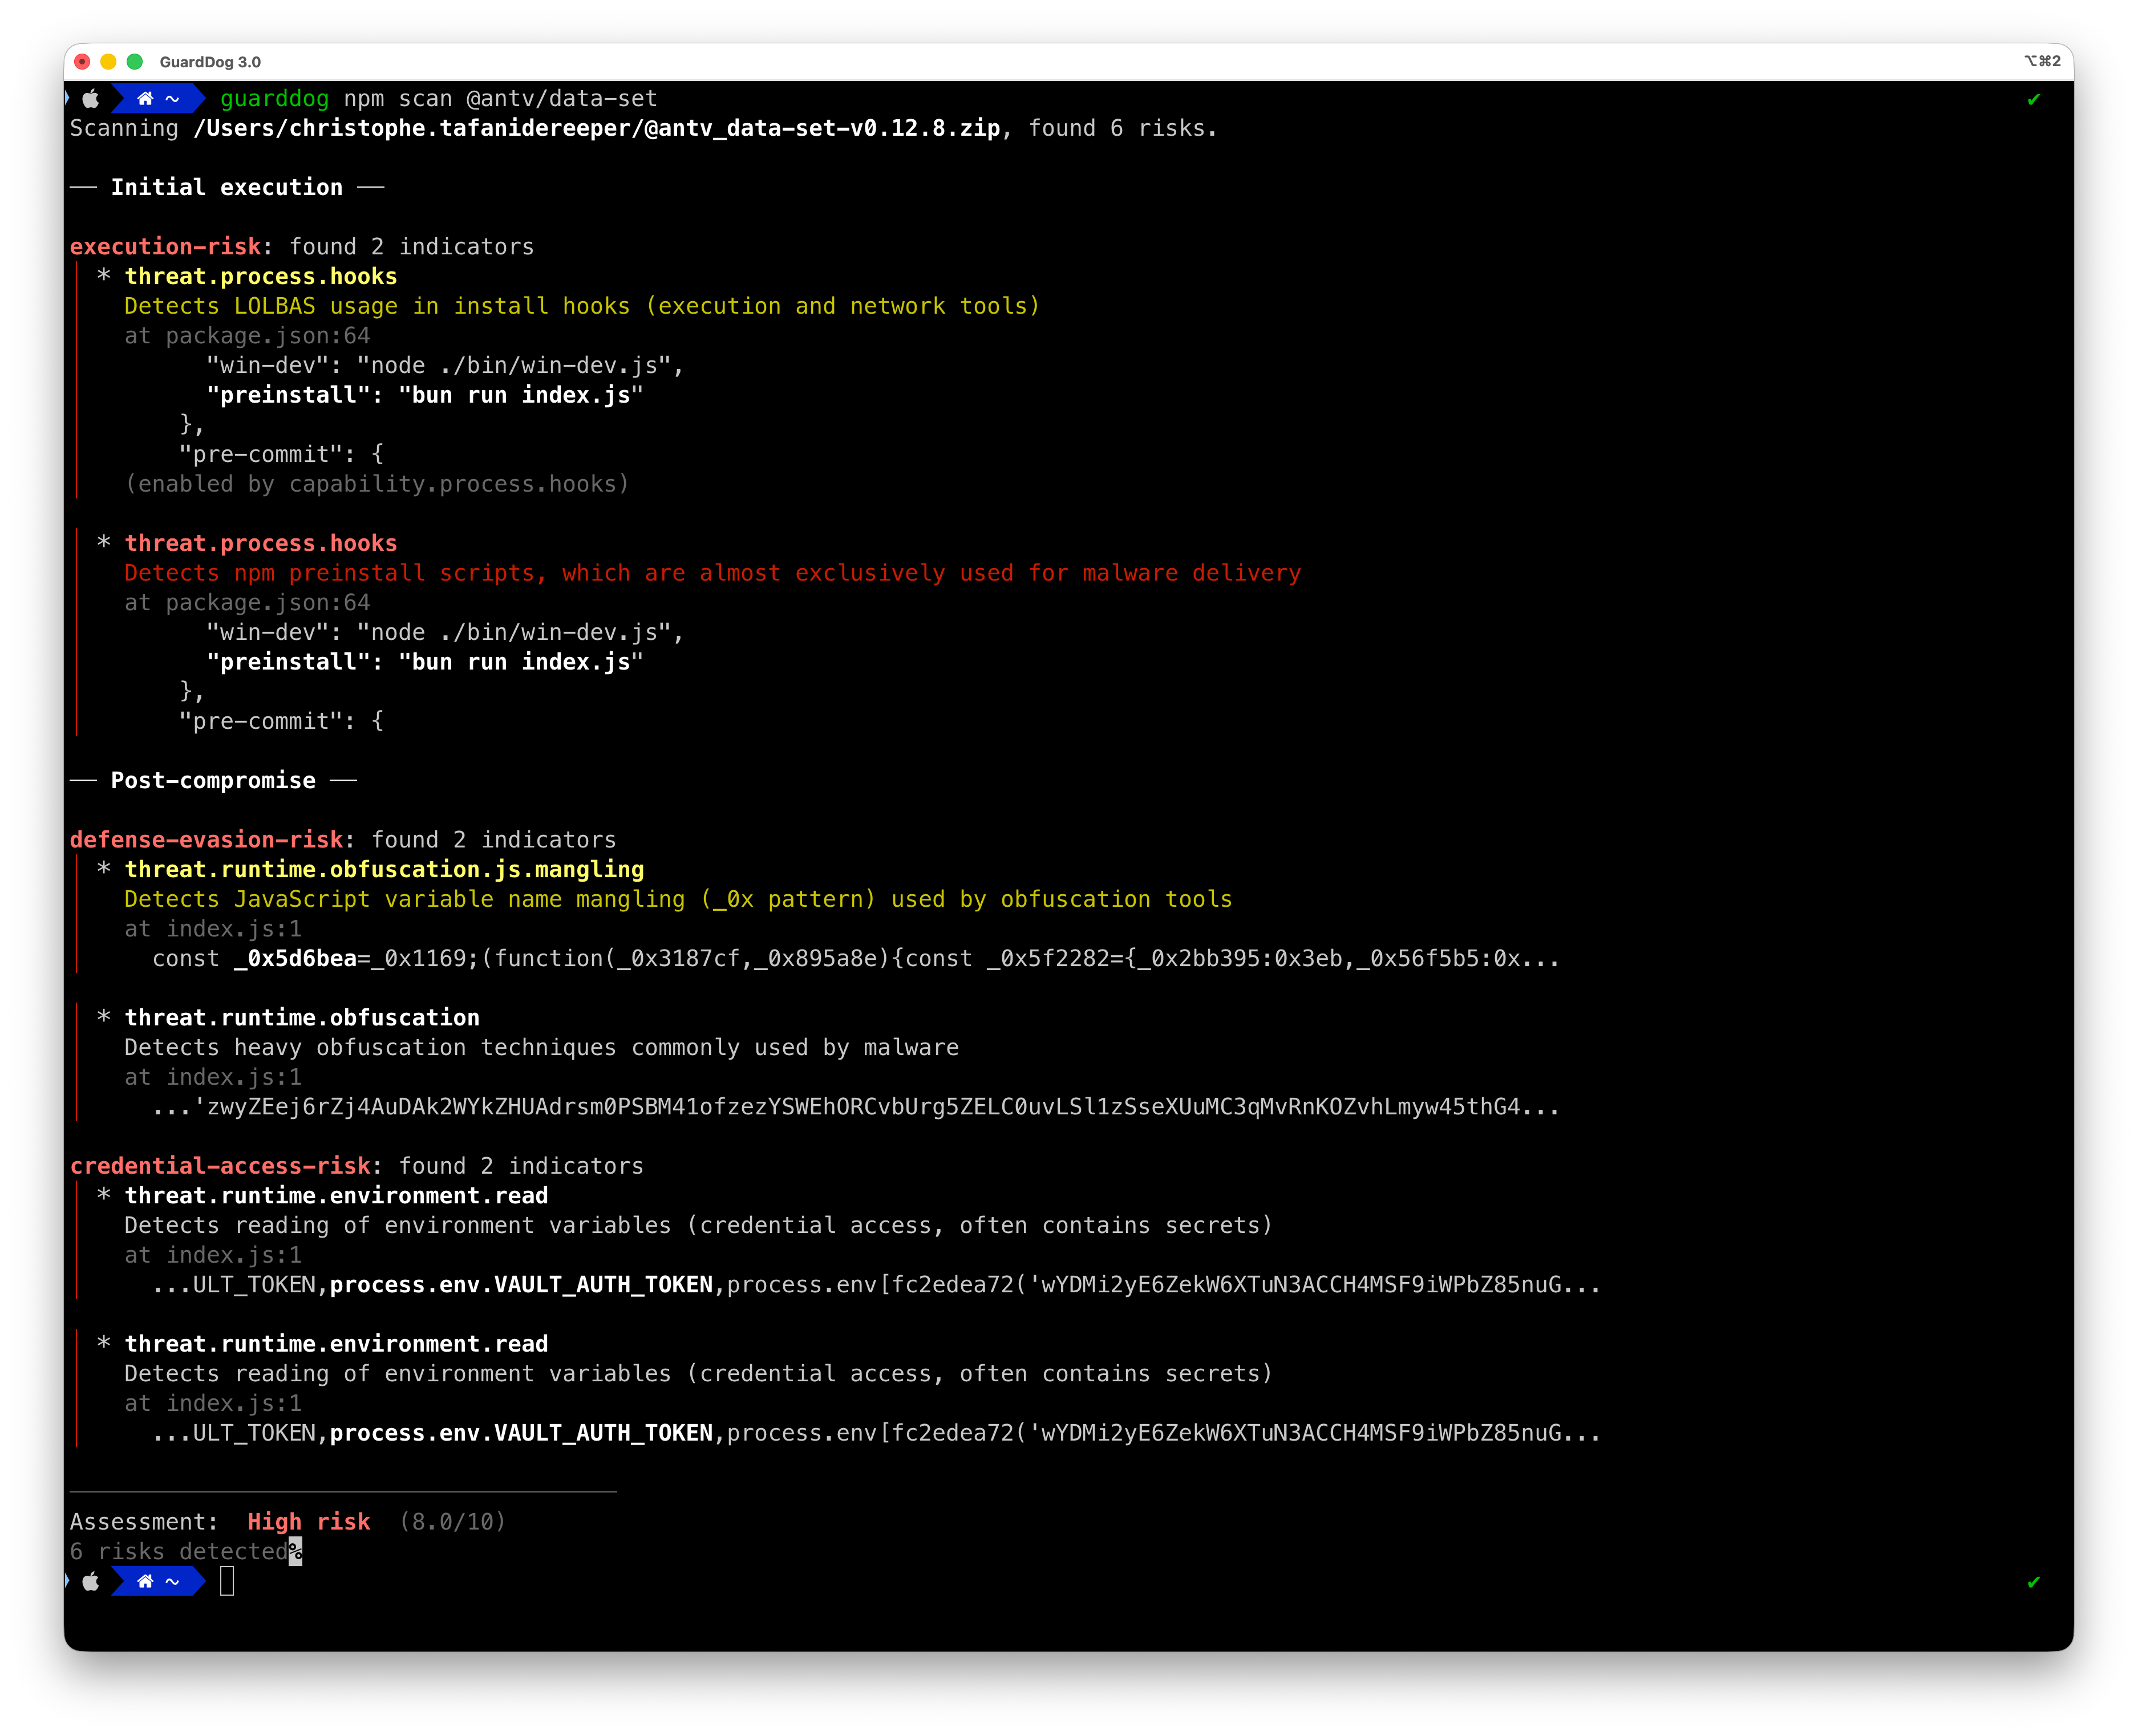 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering