

AgentTesla-Config-Extractor
 embee-research/agenttesla-config-extractor
Config extractor for AgentTesla - Discord/Telegram Variant
binary-analysiscommand-and-controlioc-management+4
3
embee-research/agenttesla-config-extractorConfig extractor for AgentTesla - Discord/Telegram Variant
 keensecuritylab/binabsinspector
Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…
 tylabs/qs_old
Command line tool for scanning streams within office documents plus xor db attack
 peterlinccl/vulnerability-dlink-cve-2025-14659
Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…
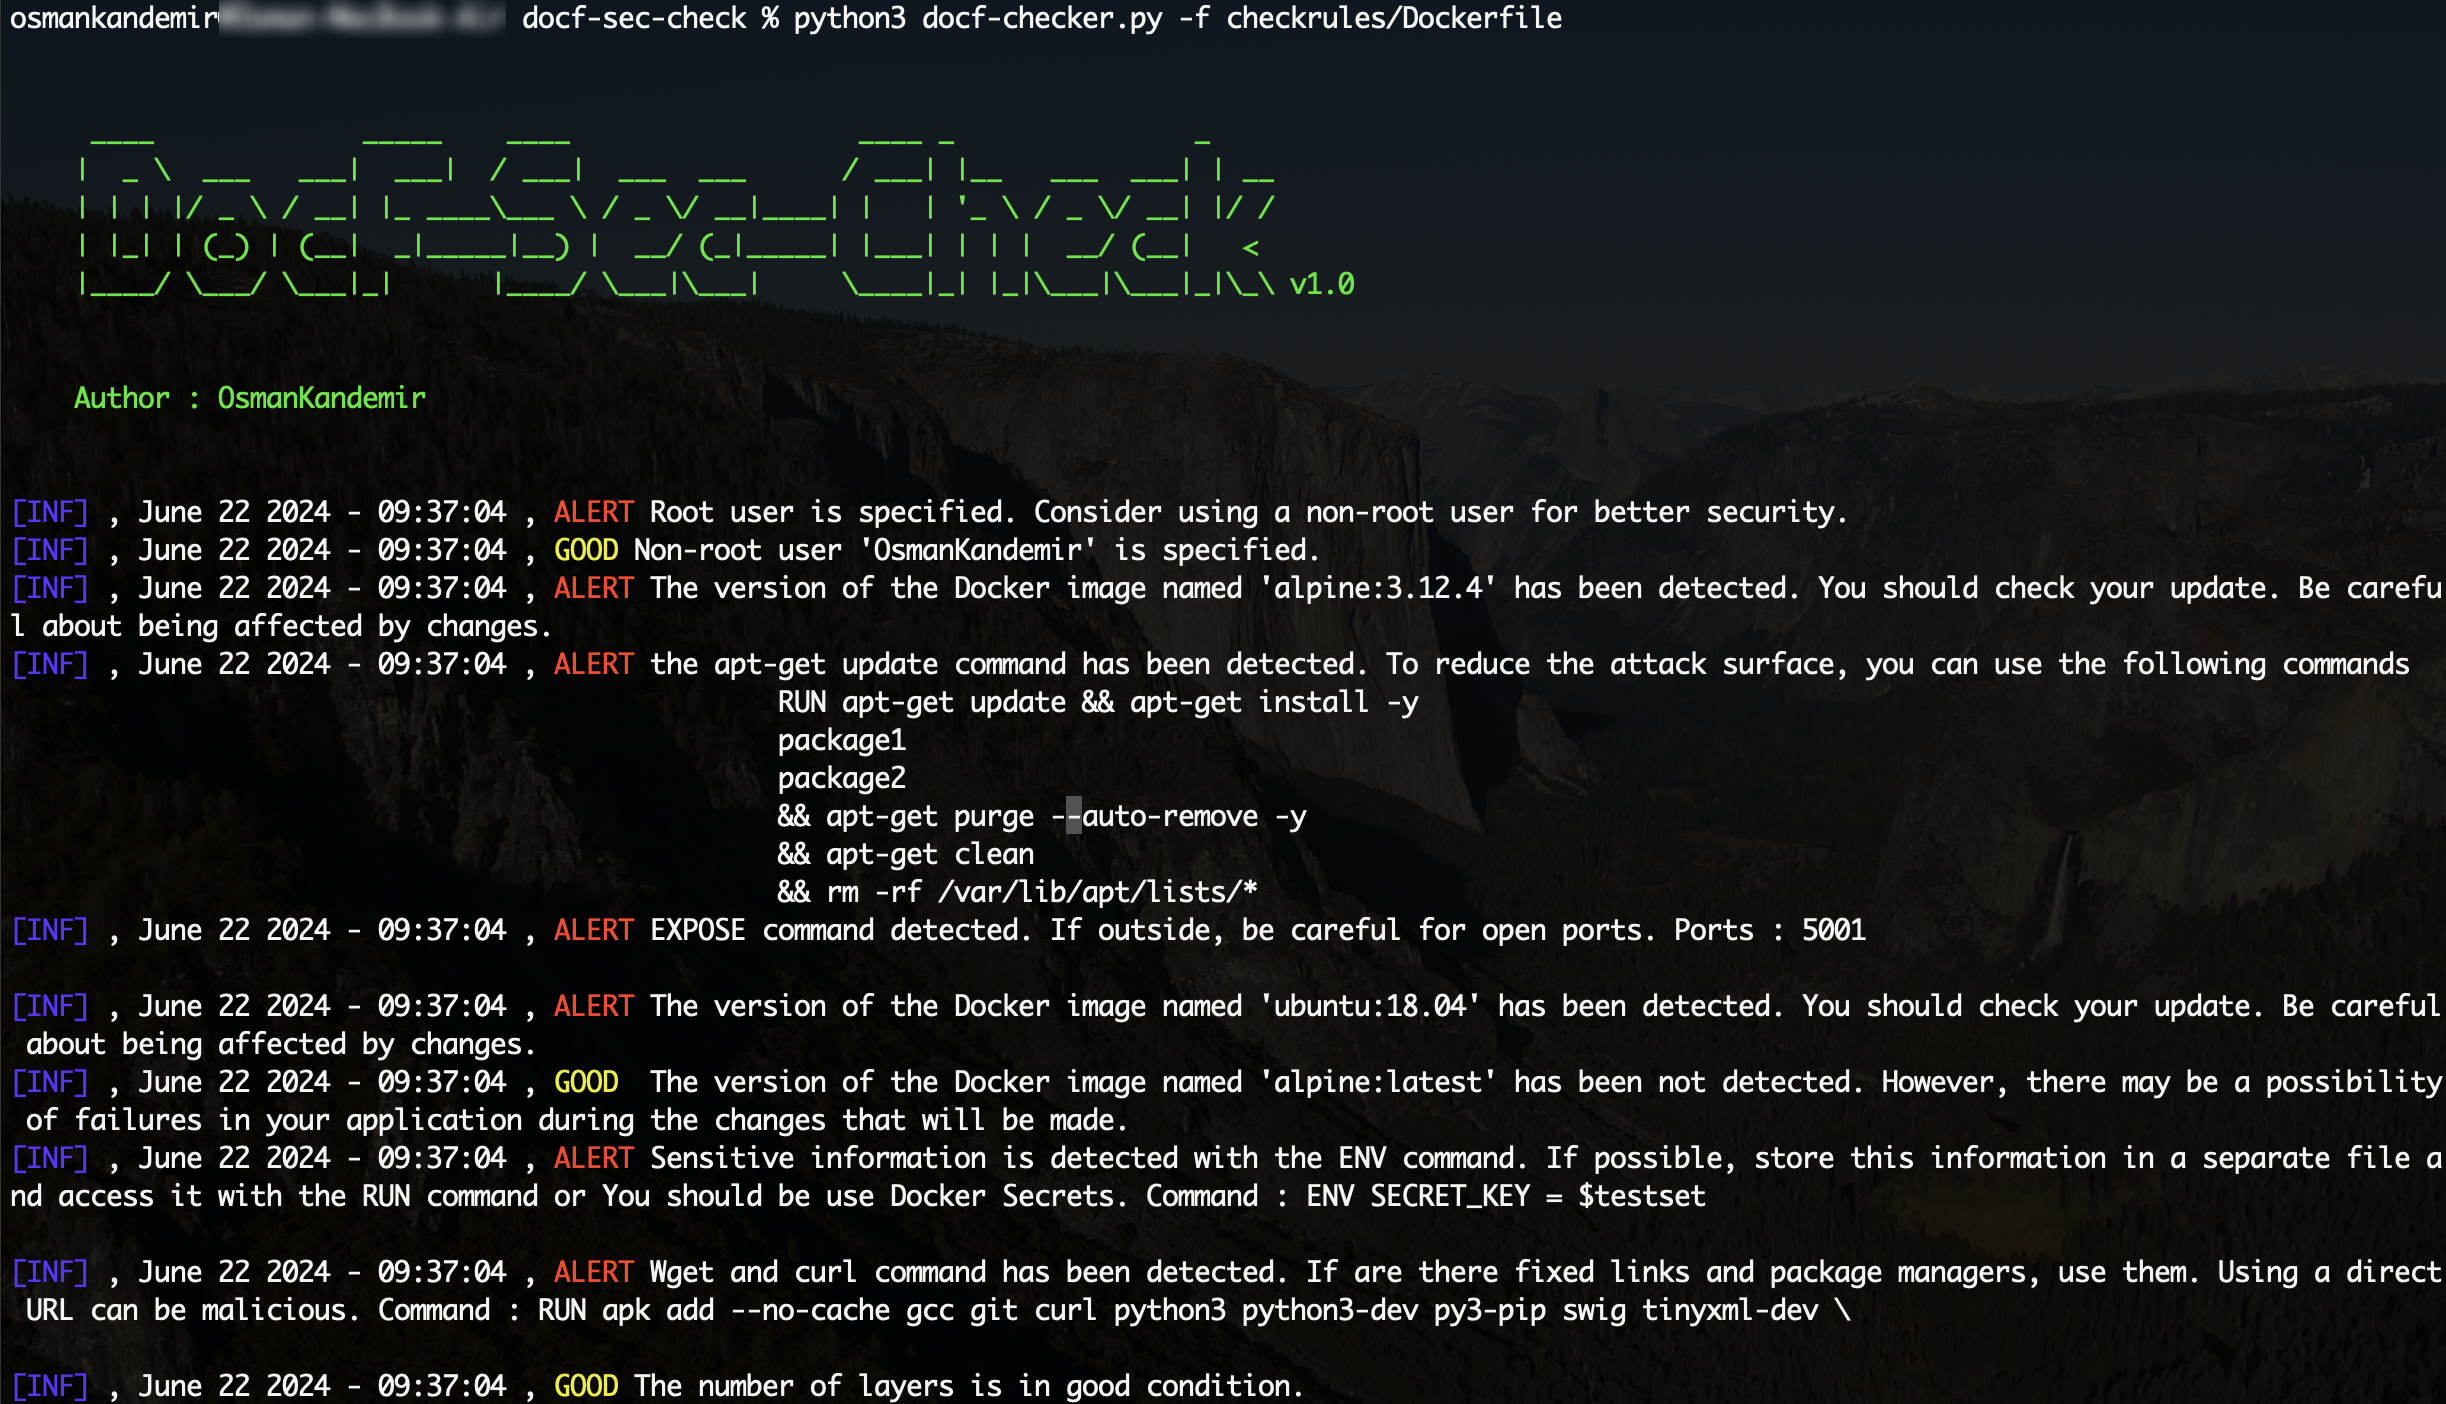 osmankandemir/docf-sec-check
Static analysis tool that scans Dockerfiles for insecure commands and configuration issues, providing actionable security notifications to harden…
 abdozkaya/rsc-security-auditor
🛡️ Audit your Next.js & React Server Components stack for critical vulnerabilities (CVE-2025-66478, CVE-2025-55184). Detects risks & generates fix…
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
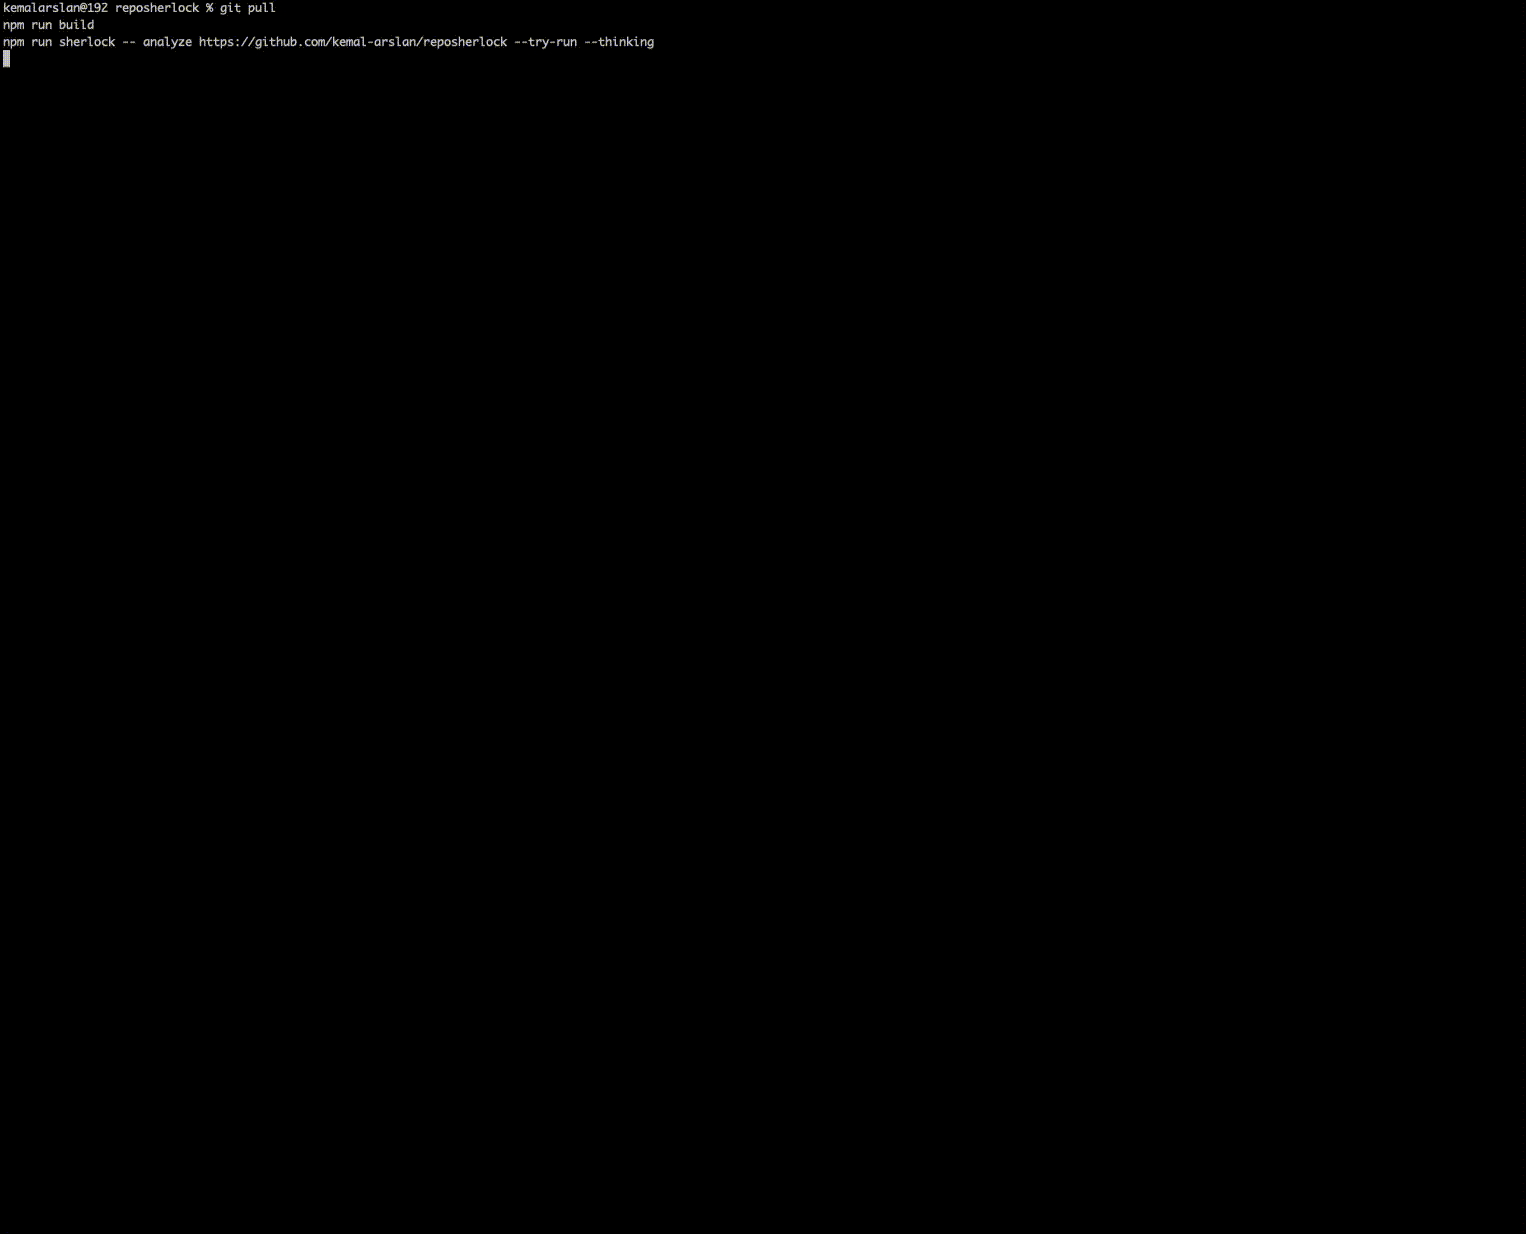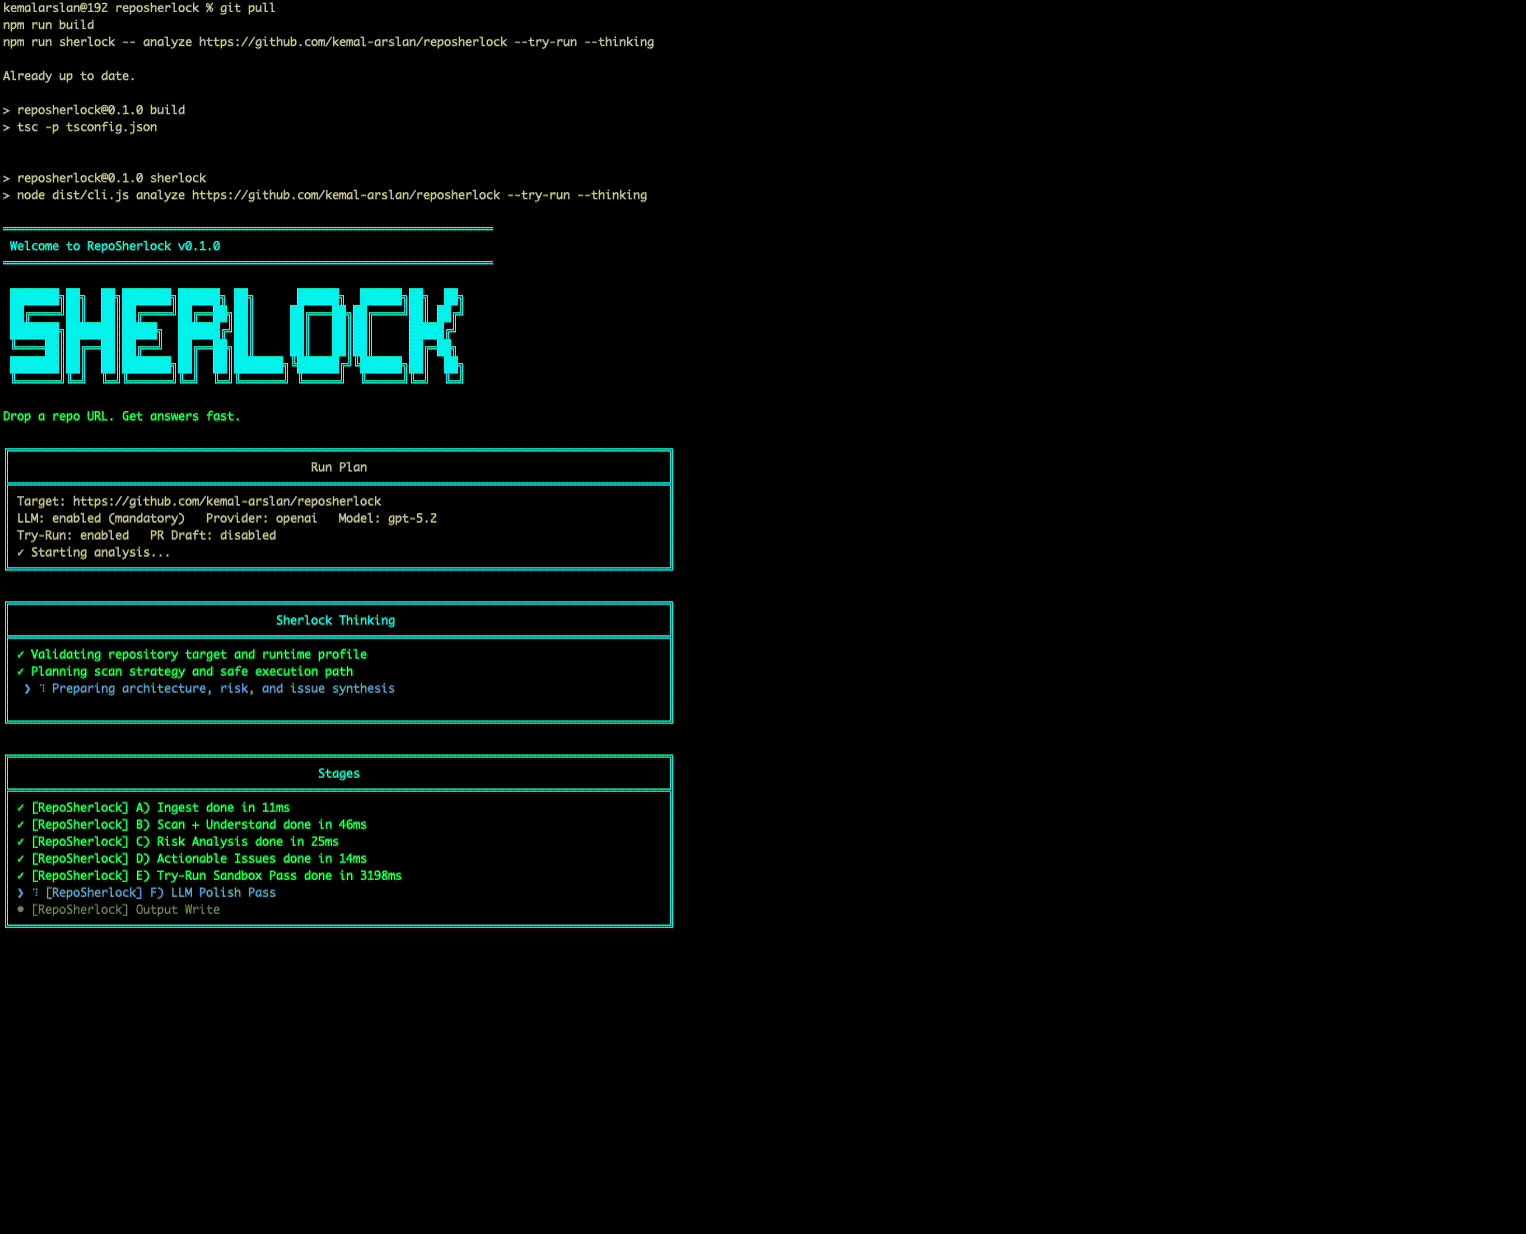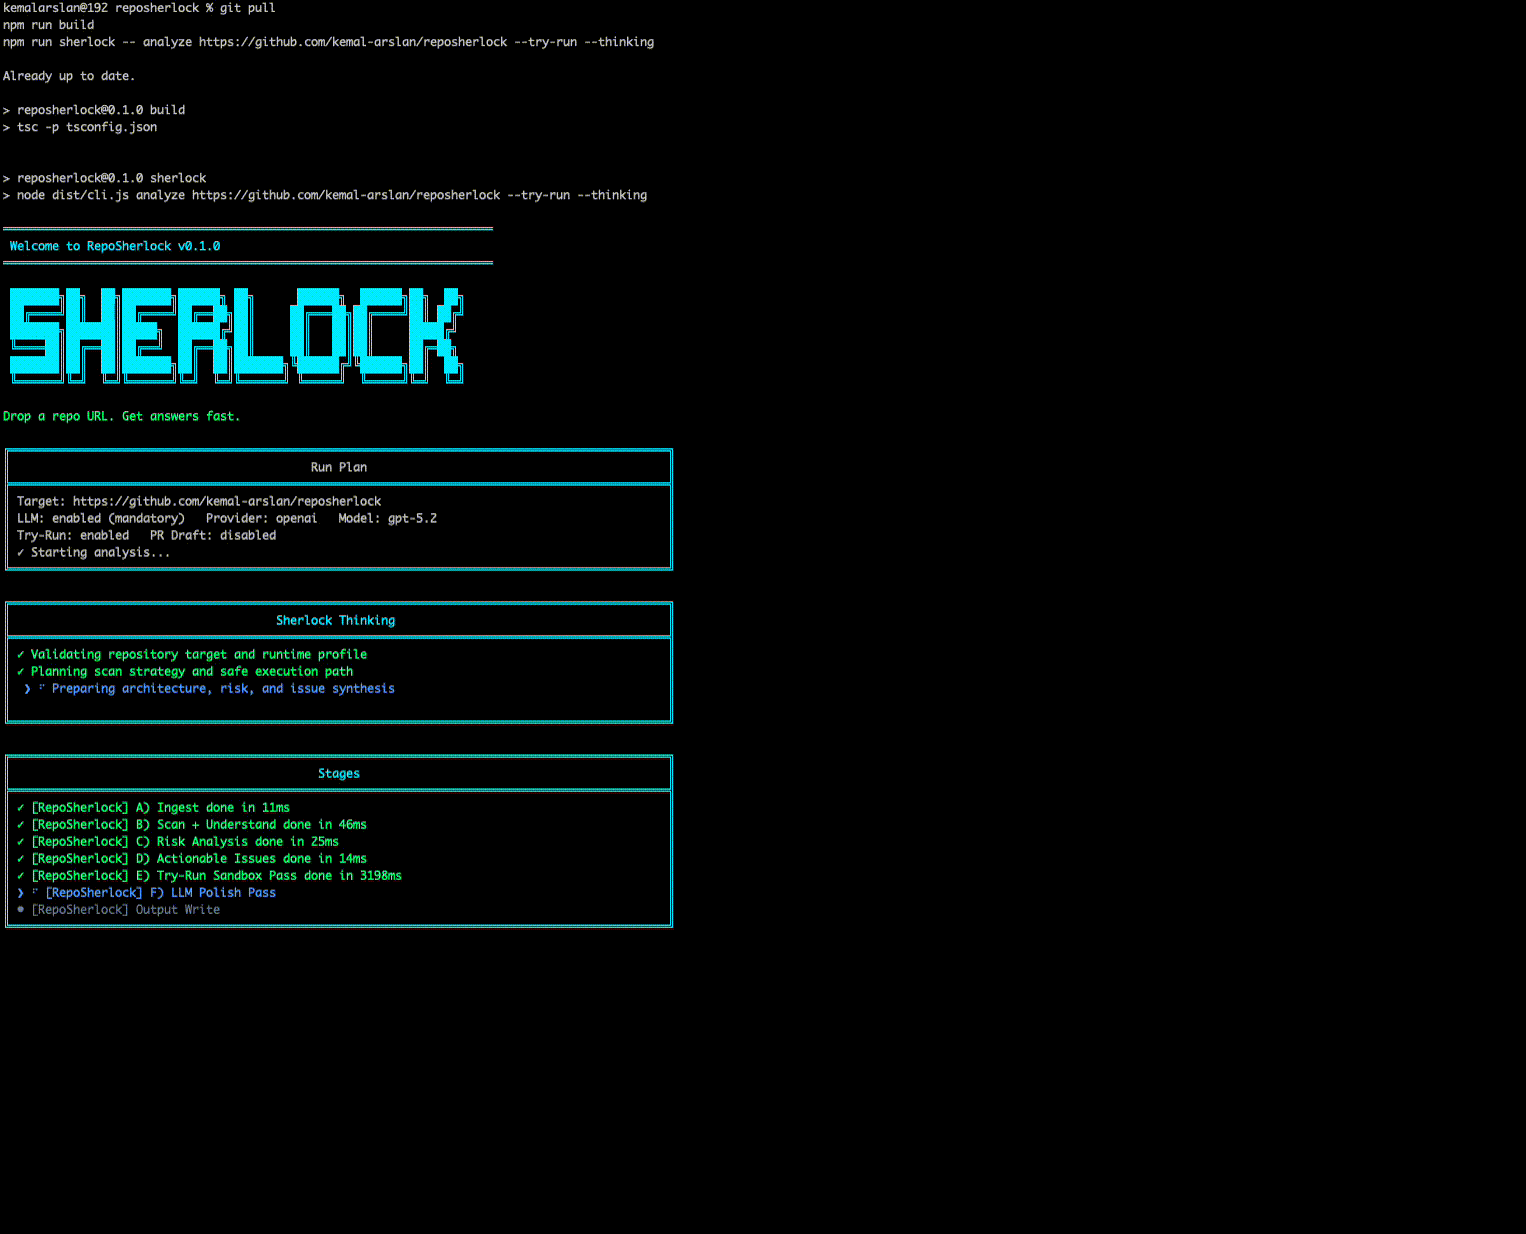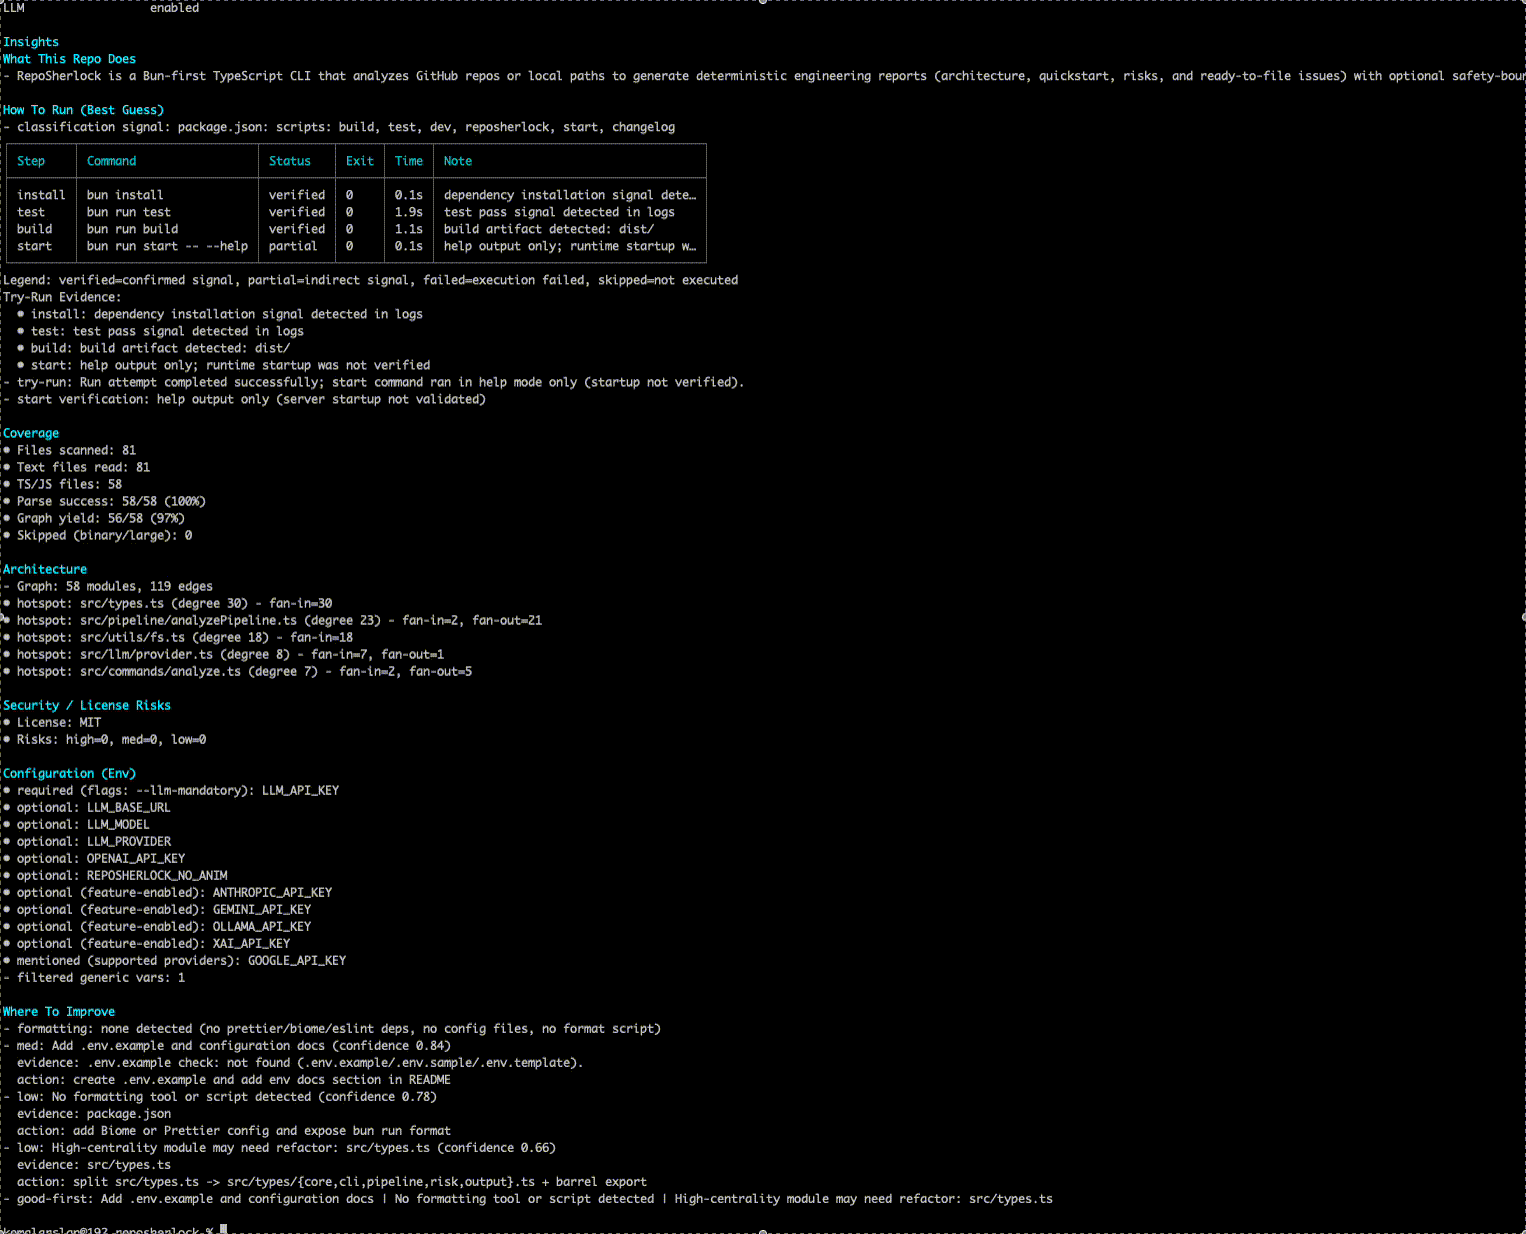 kemal-arslan/reposherlock
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
 shoucheng3/whitesource__curekit_cve-2022-23082_1-1-3
Java security library providing contextual encoders and sanitizers to automatically remediate vulnerabilities like XSS, path traversal, and command…
 jftierno/-cve-2018-6574
Exploit for CVE-2018-6574, a Go command injection vulnerability. Provides a targeted payload for testing and validating the flaw in affected systems.
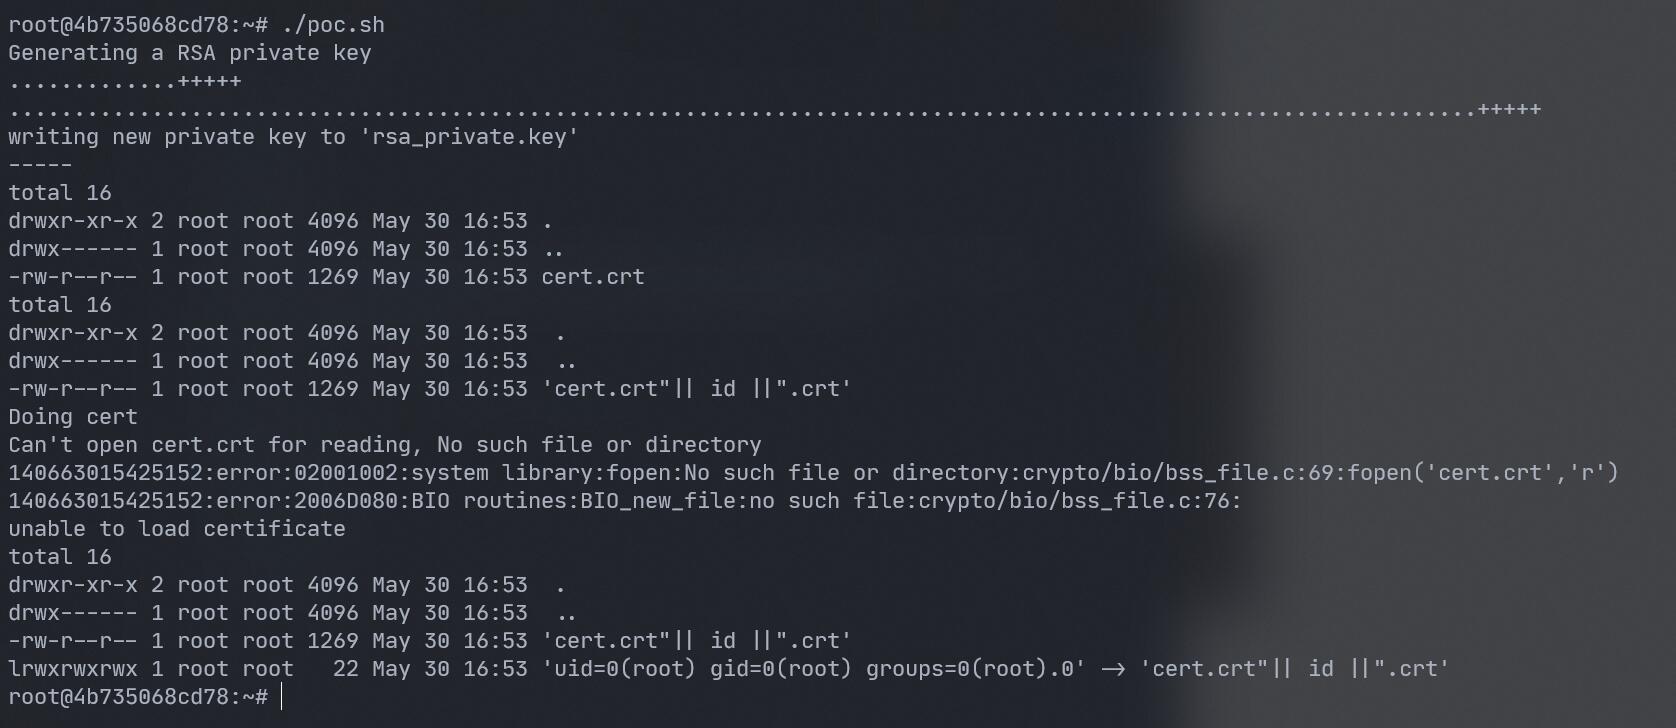 rama291041610/cve-2022-1292
CVE-2022-1292 OpenSSL c_rehash Vulnerability
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 nowsecure/r2frida
Radare2 and Frida better together.
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
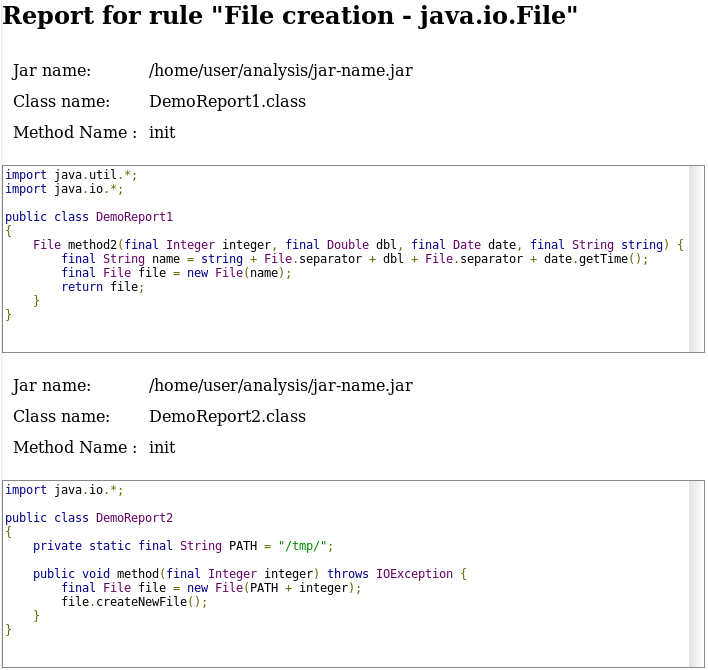 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules
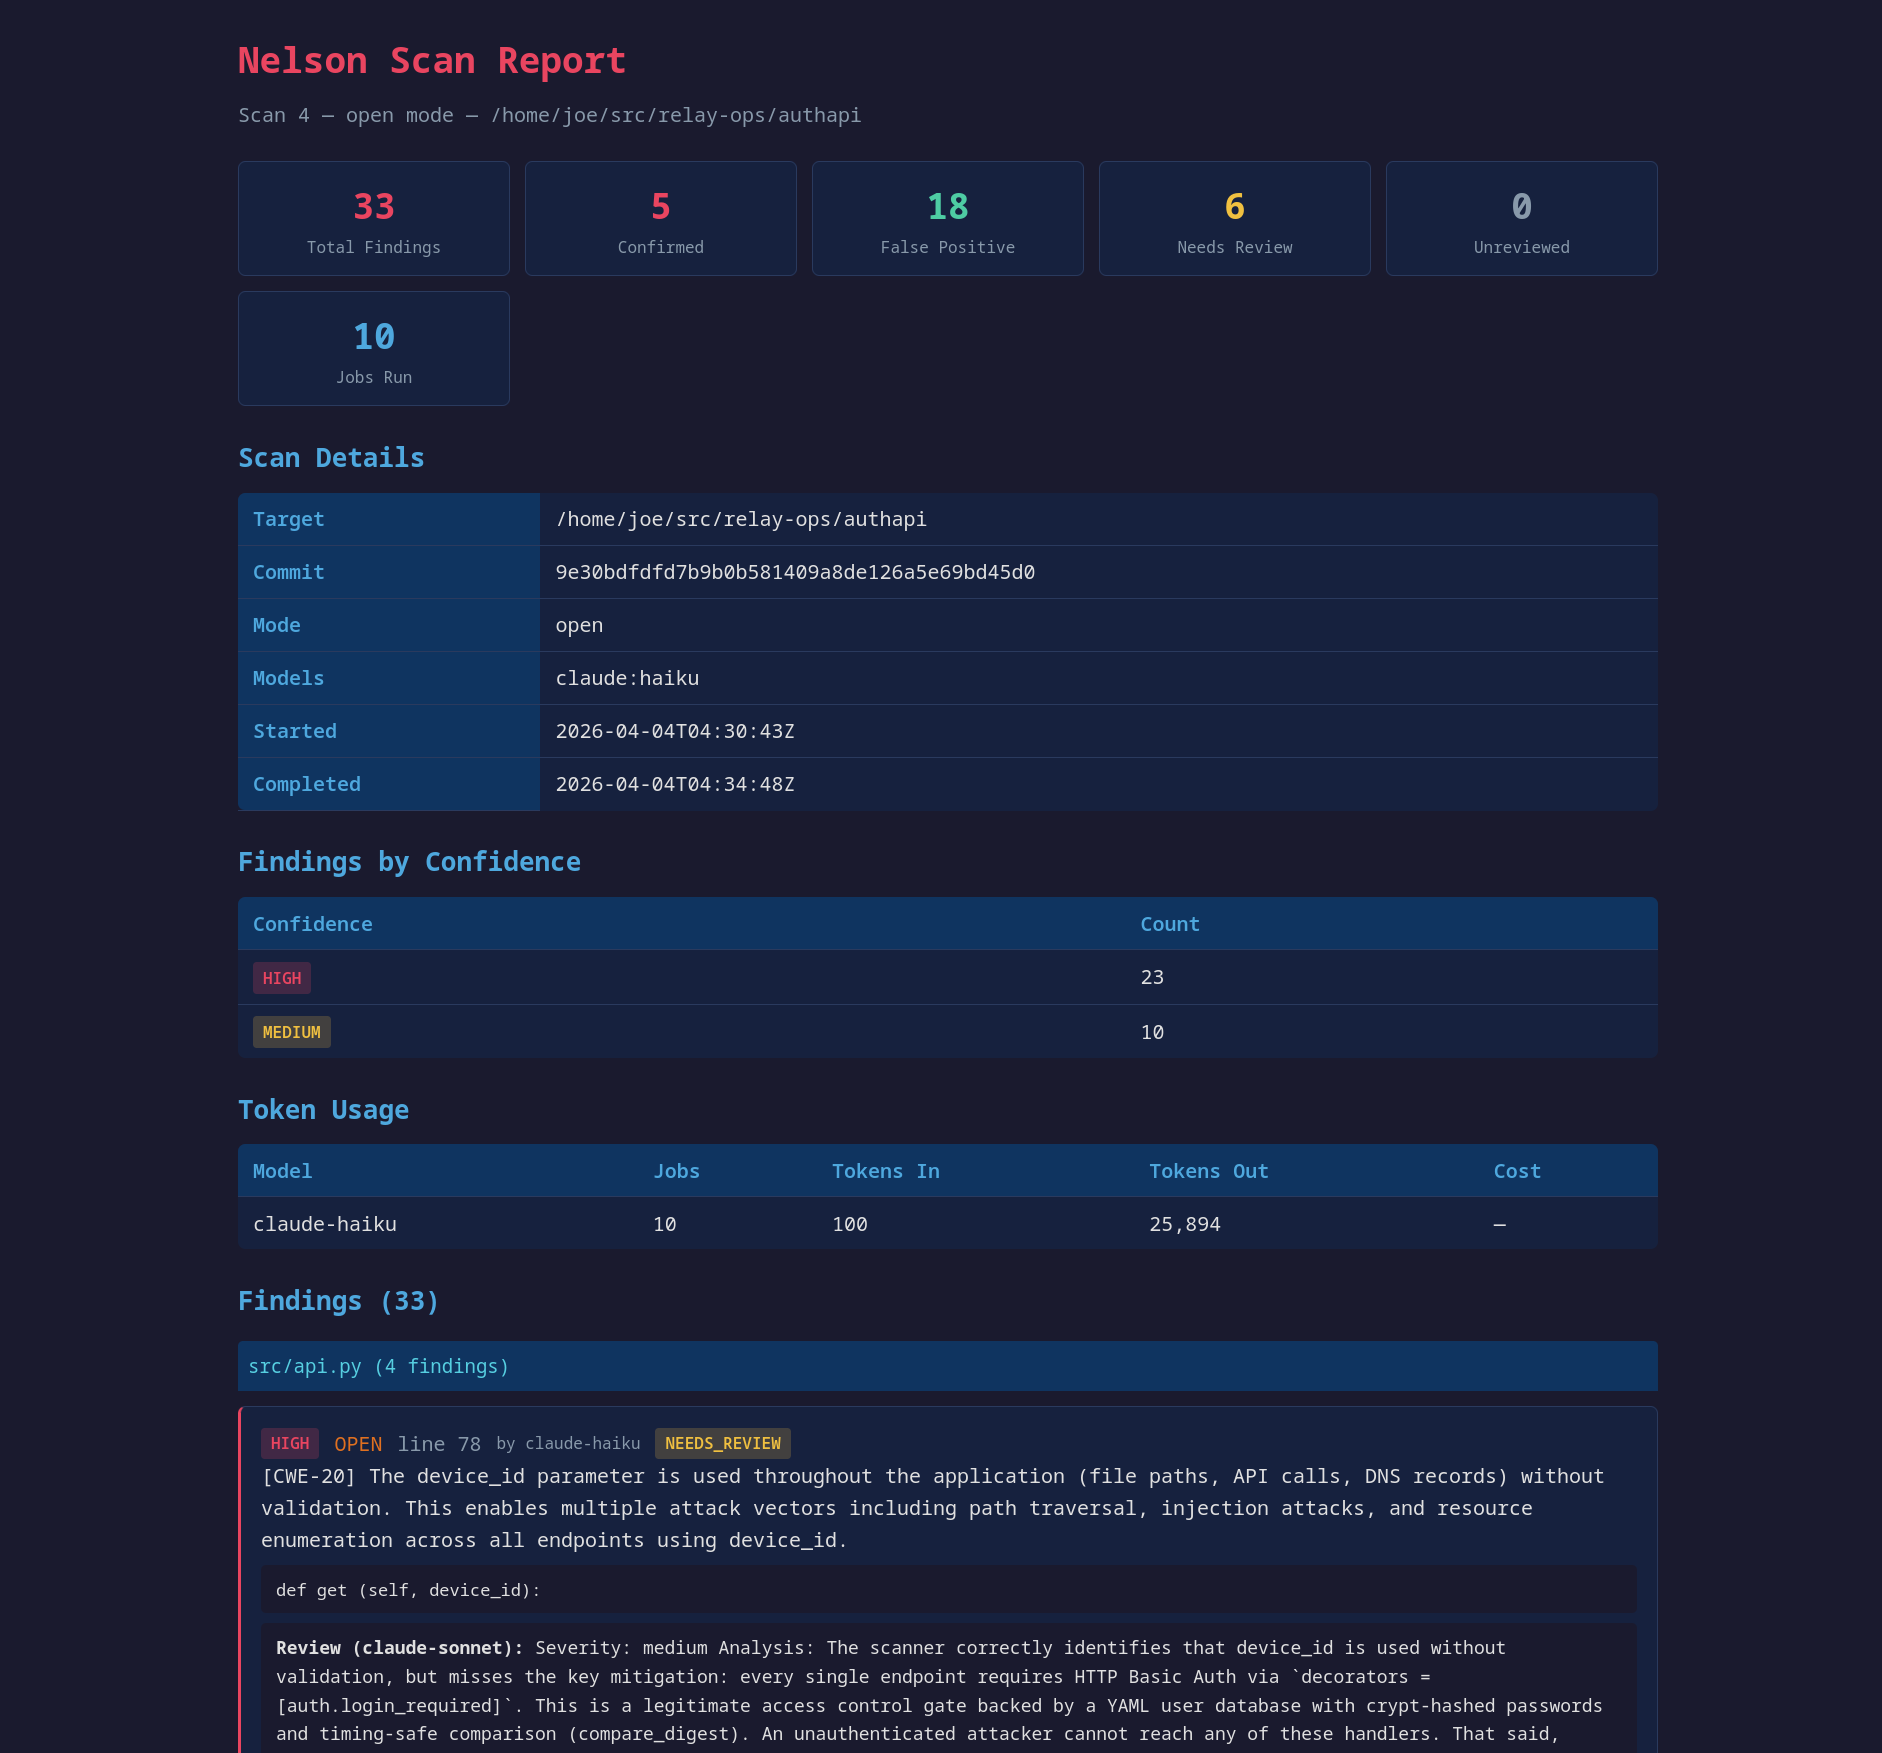 swelljoe/nelson
Finding vulnerabilities through dumb brute force
 mattijsmoens/intentshield
Pre-execution intent verification for AI agents. Audits what your AI is about to do, not what it says. Zero dependencies, deterministic, hash-sealed.