
http-desync-guardian
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
api-security-testingstatic-analysisvulnerability-analysis+1
274
aws/http-desync-guardianAnalyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
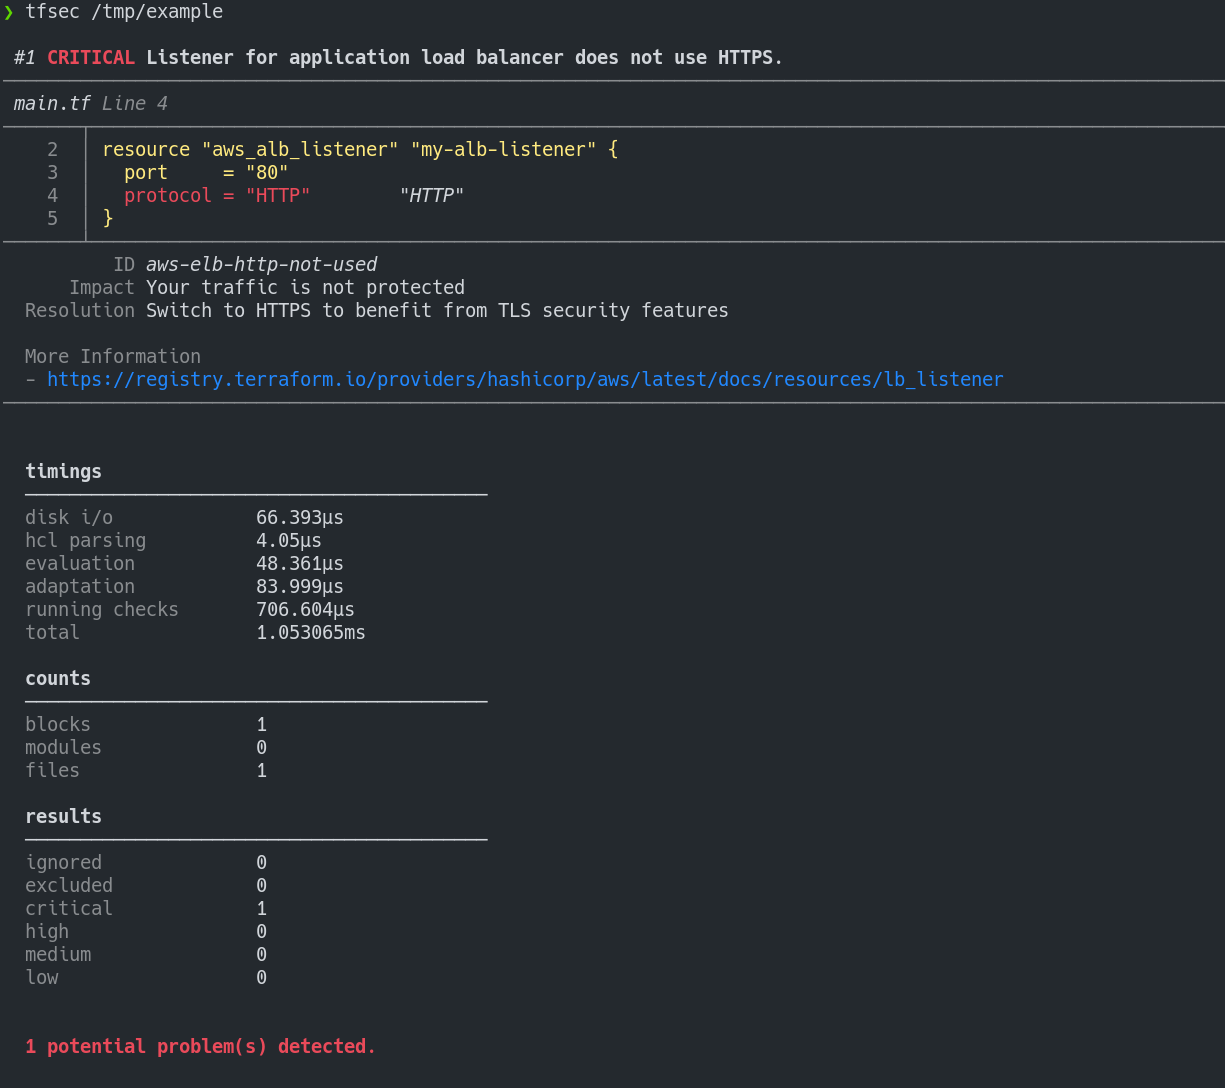
 appvia/krane
Kubernetes RBAC static analysis & visualisation tool
 arsbr/veritensor
The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 arzaan789/keyguard
Scan codebases and GCP projects for exposed API credentials
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
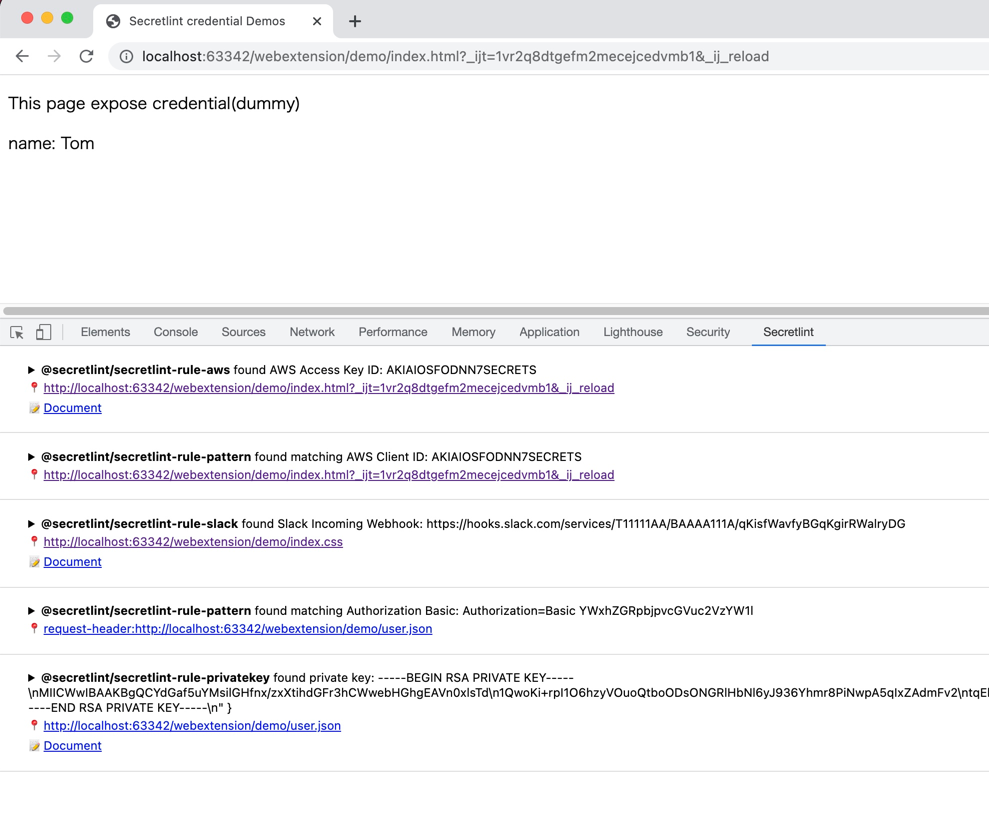 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 pq-code-package/mlkem-native
Secure, fast, and portable C90 implementation of ML-KEM / FIPS 203
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing
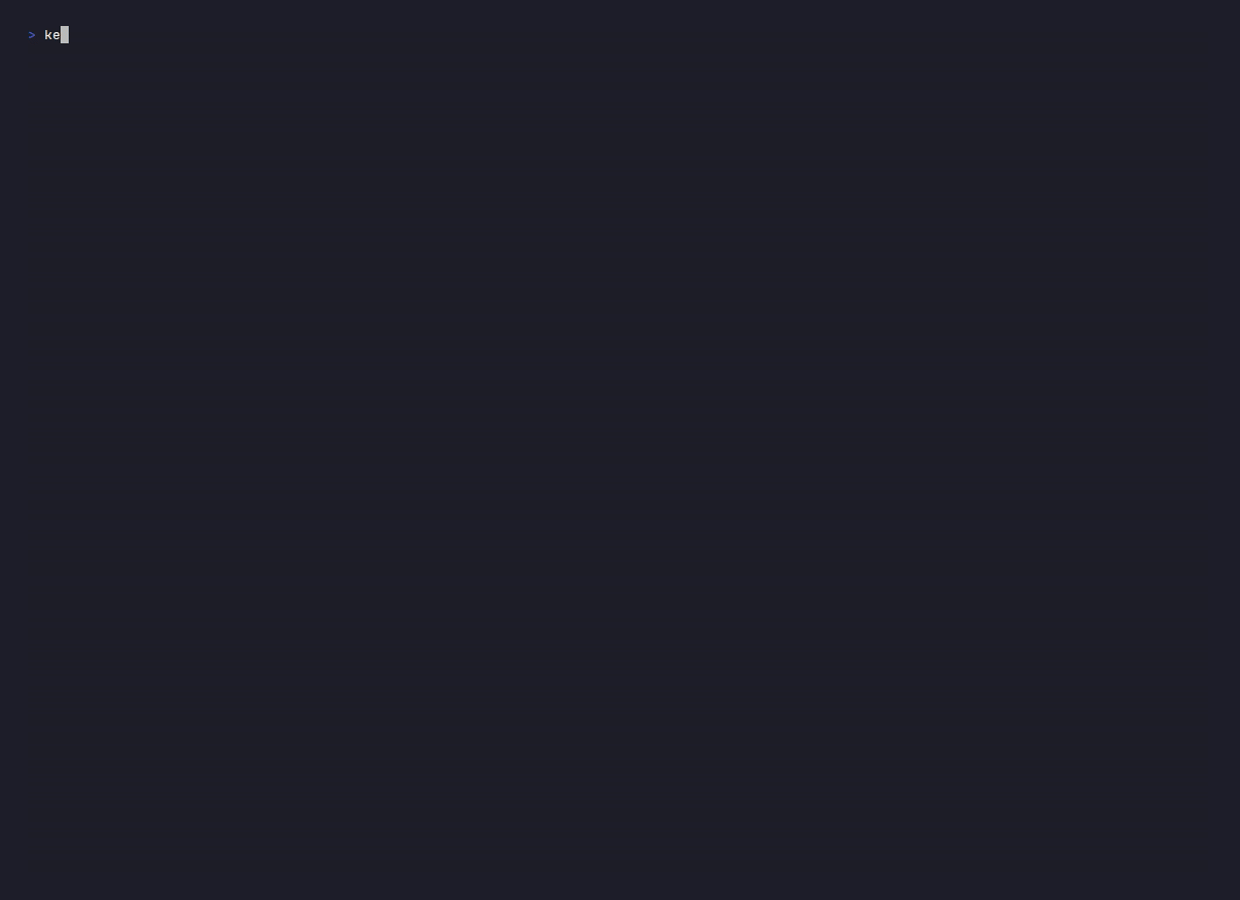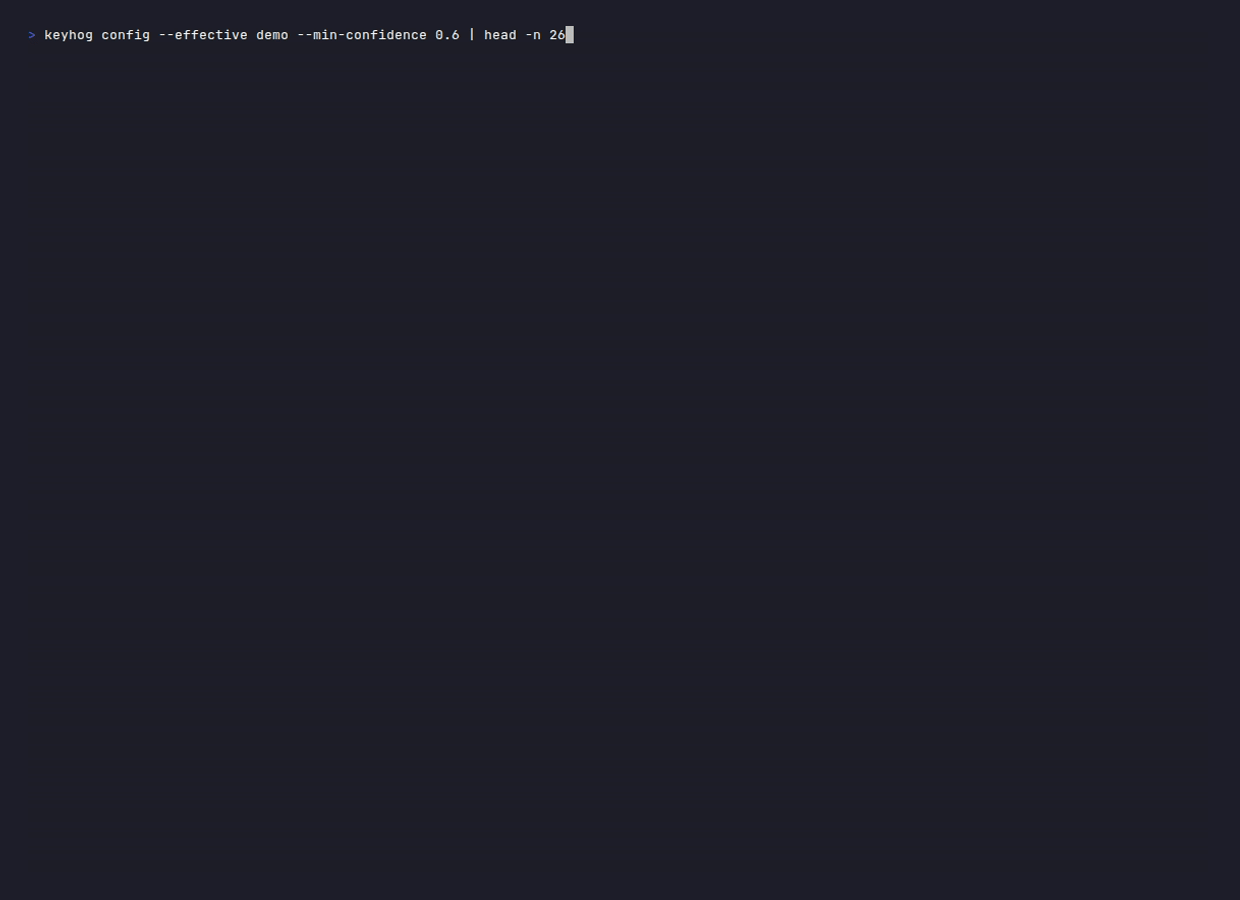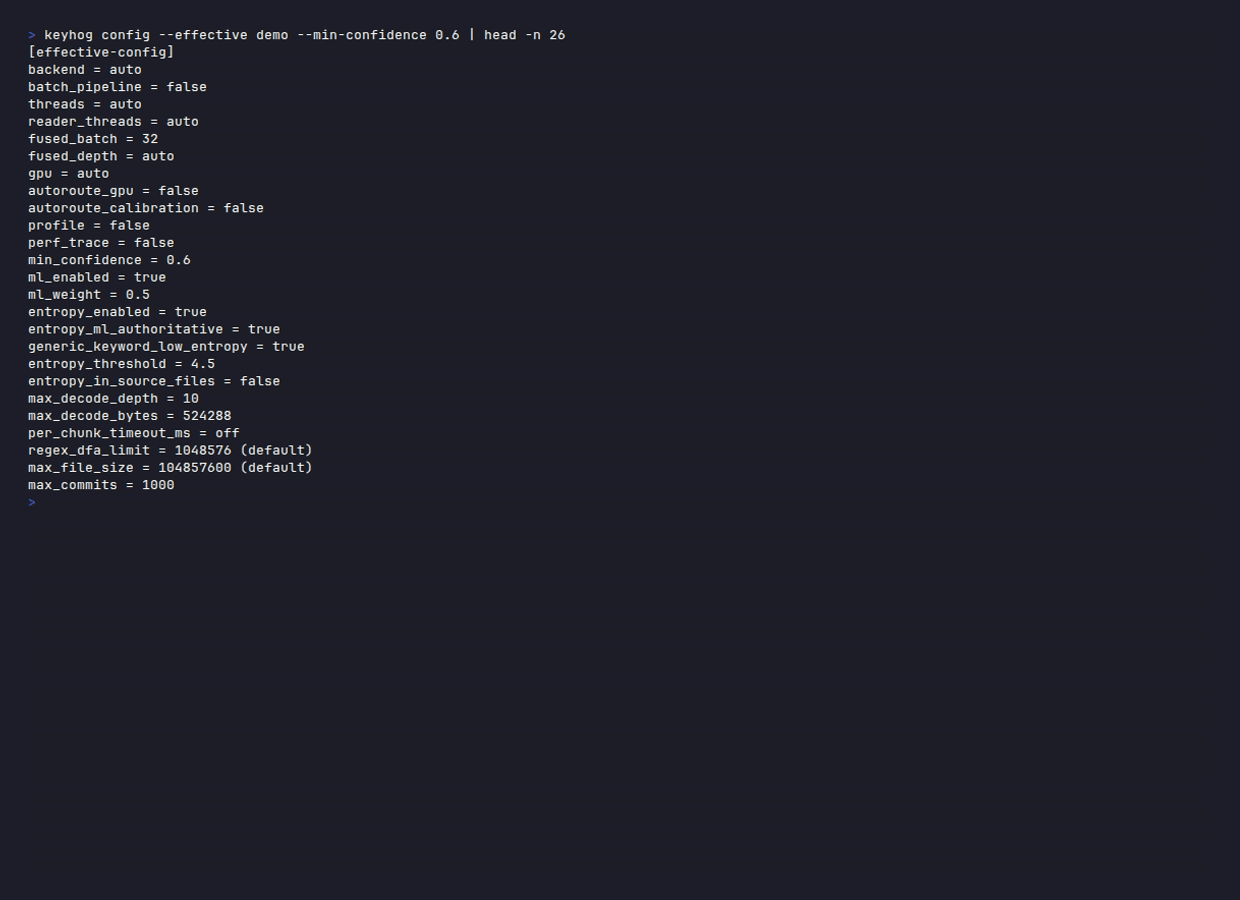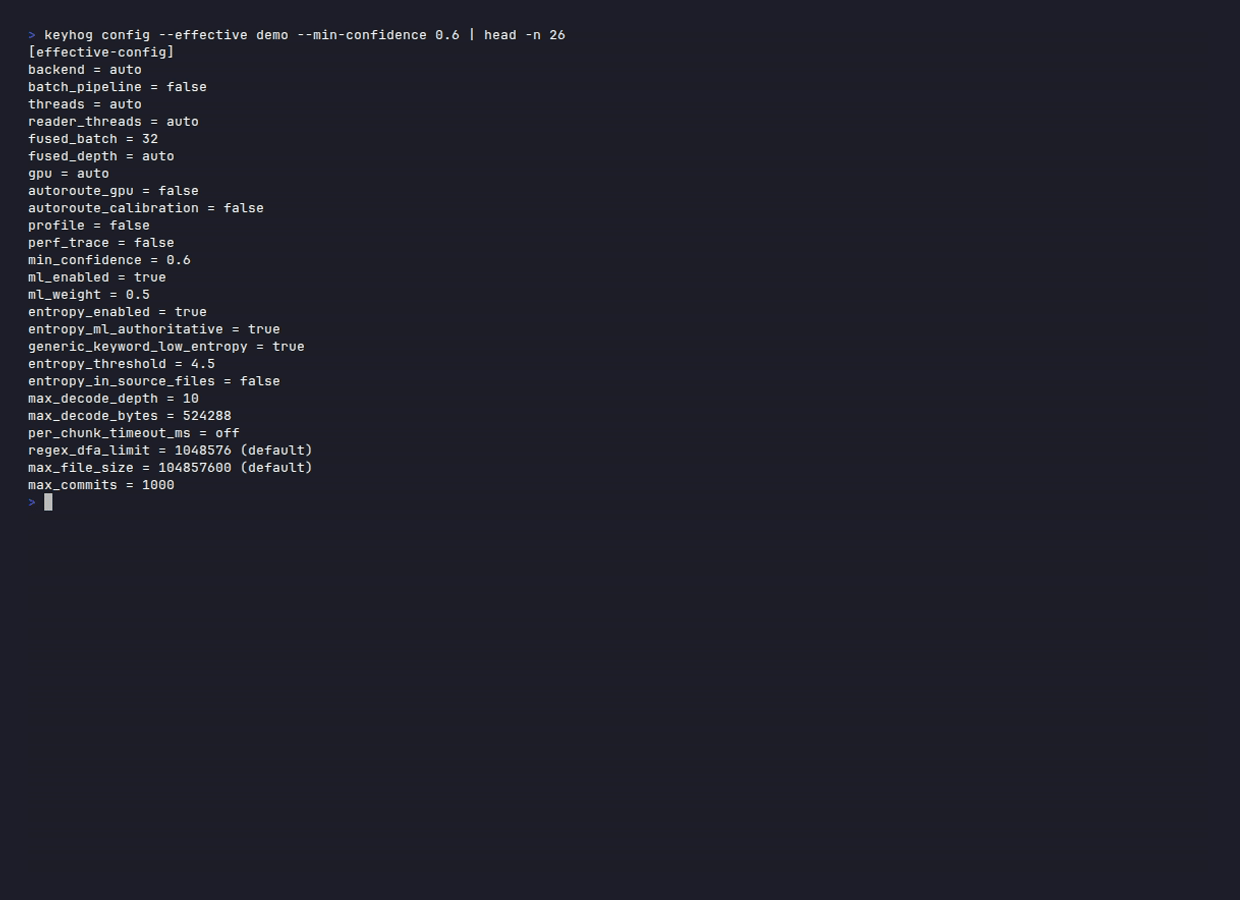 santhreal/keyhog
Open-source secret scanner in Rust
 bogdanticu88/threatmap
IaC threat modeler with STRIDE, MITRE ATT&CK, and PASTA frameworks. REST API, GraphQL, and Docker support for Terraform, CloudFormation, and…
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…