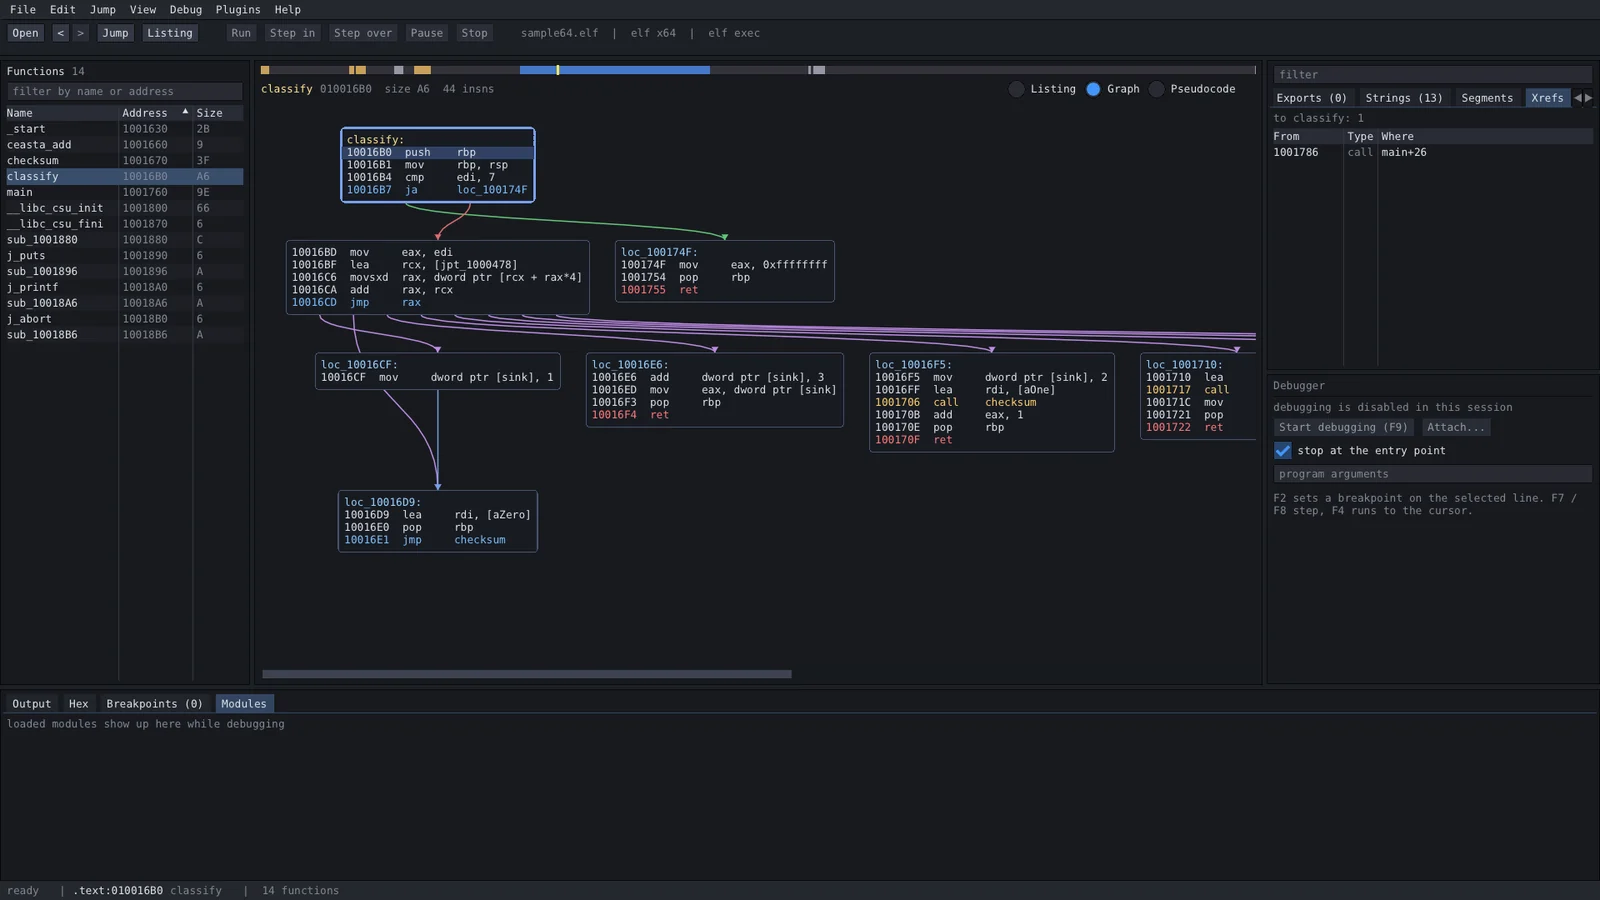
ceasta
 ngwg/ceasta
reverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
25
ngwg/ceastareverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…
 githubsecuritylab/seclab-taskflows-fuzzing
An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
 google/enjarify
Translates Dalvik bytecode (DEX/APK) to equivalent Java bytecode, enabling Java analysis tools to process Android applications with high correctness…
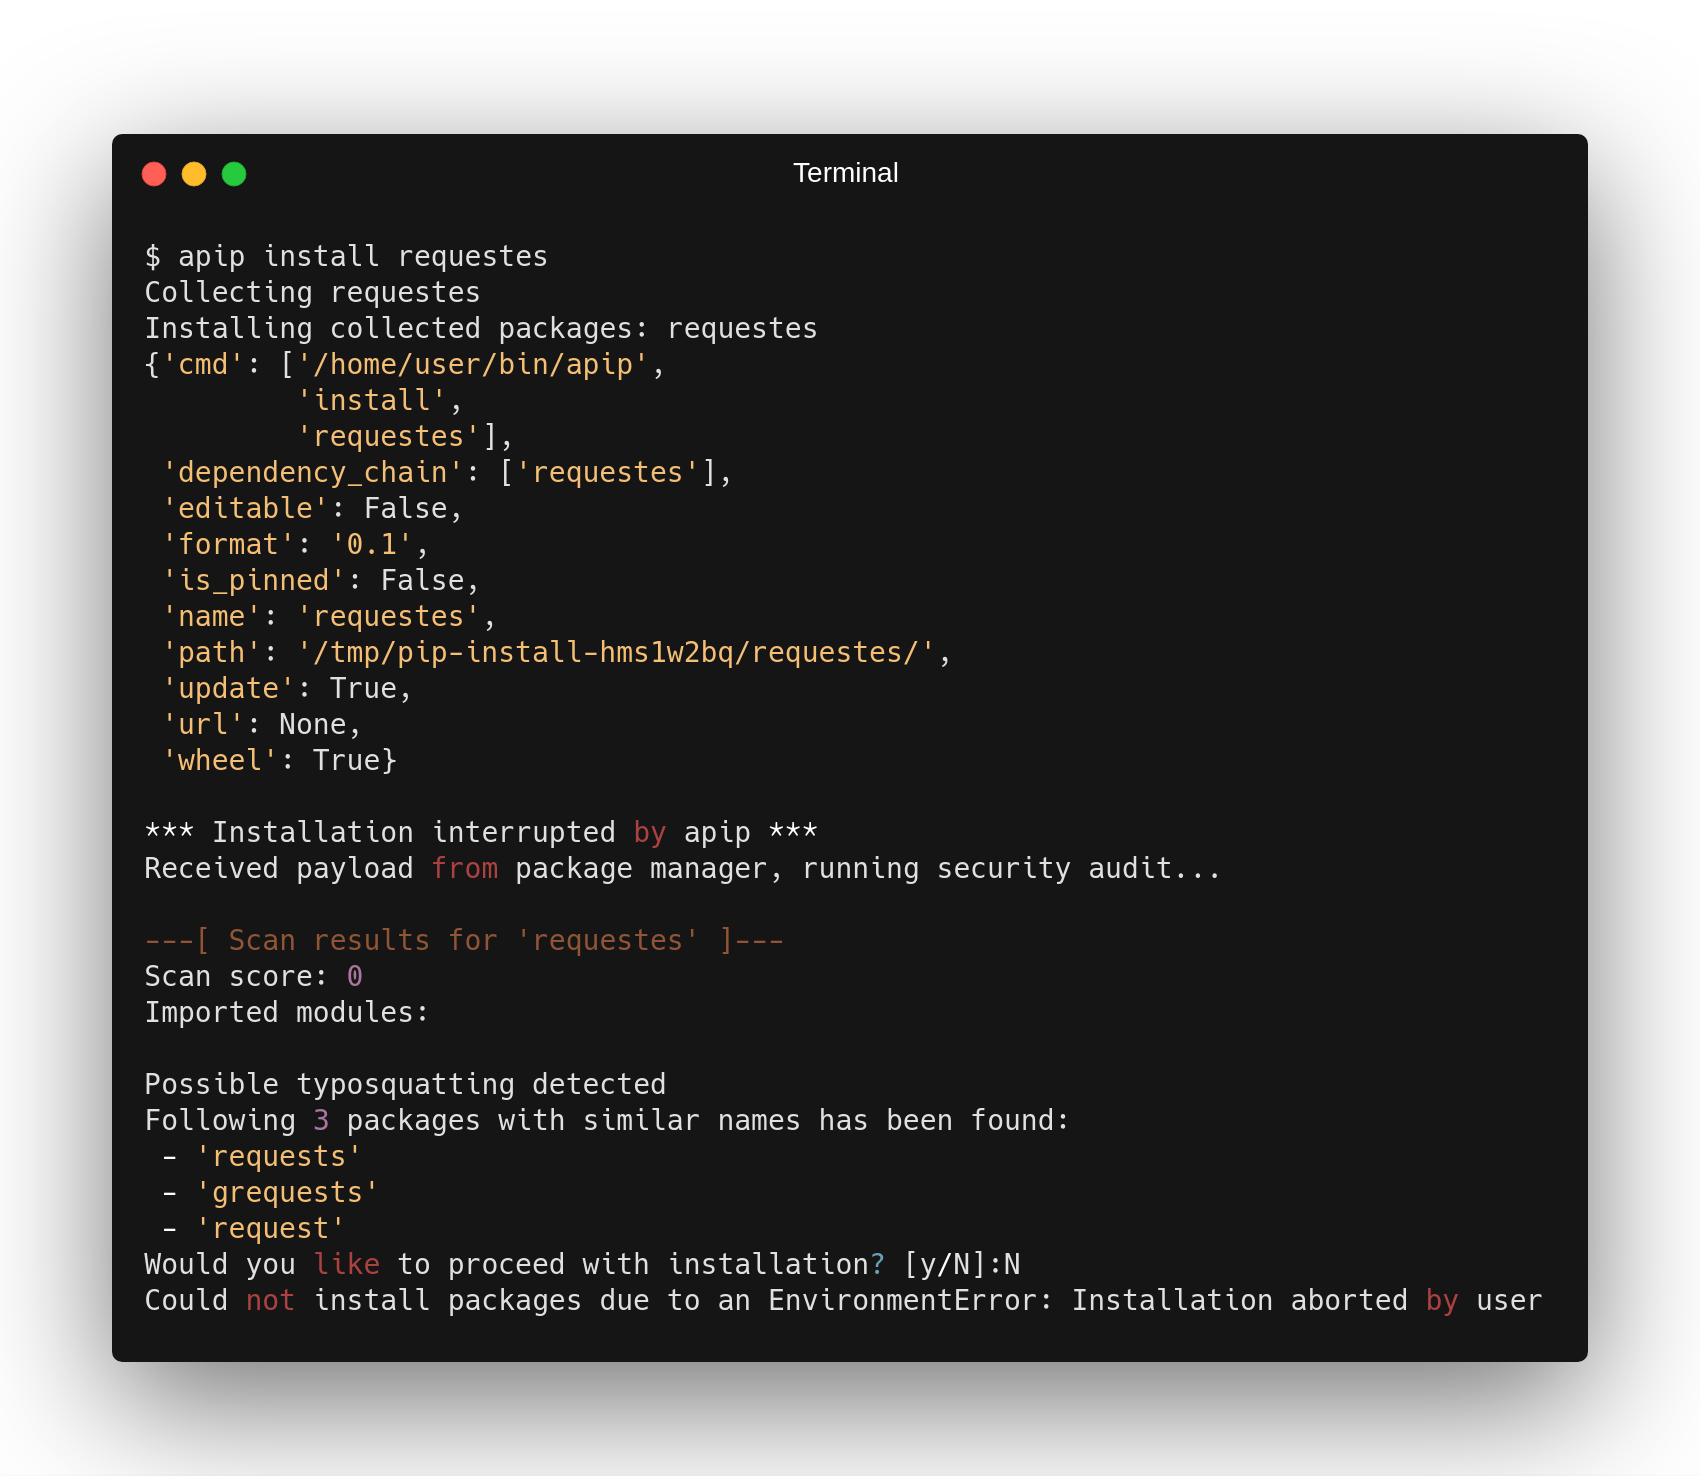 rootlug/aura
Project Aura: Security auditing and code introspection
 superandroidanalyzer/super
Secure, Unified, Powerful and Extensible Rust Android Analyzer
 androbugs/androbugs_framework
AndroBugs Framework is an efficient Android vulnerability scanner that helps developers or hackers find potential security vulnerabilities in Android…
 newliver666/apk-reverse
Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…
 gmh5225/ghidra_svr_bridge
Binary Ninja plugin that syncs analysis bidirectionally with a Ghidra Server repository, via a Java bridge subprocess.
 mandiant/flashmingo
Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
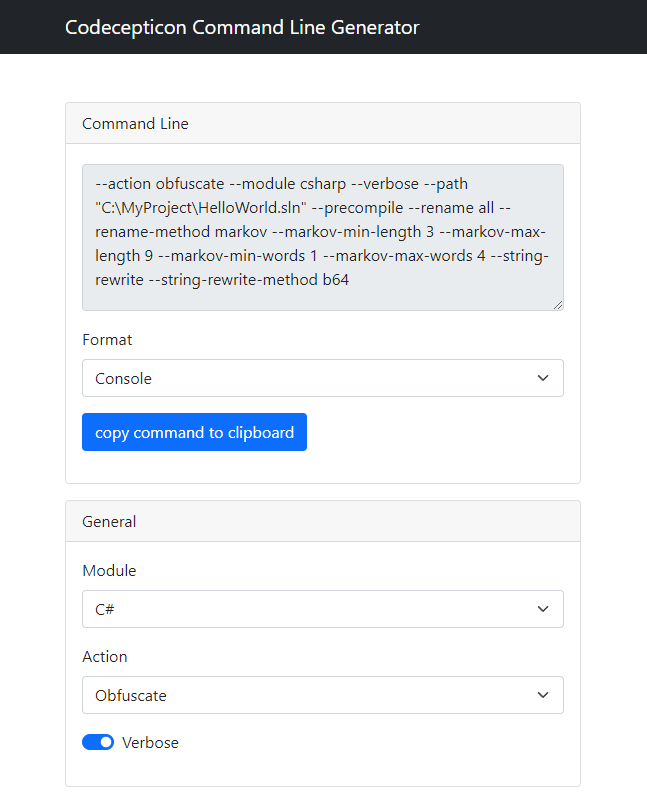 accenture/codecepticon
.NET/PowerShell/VBA Offensive Security Obfuscator
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator
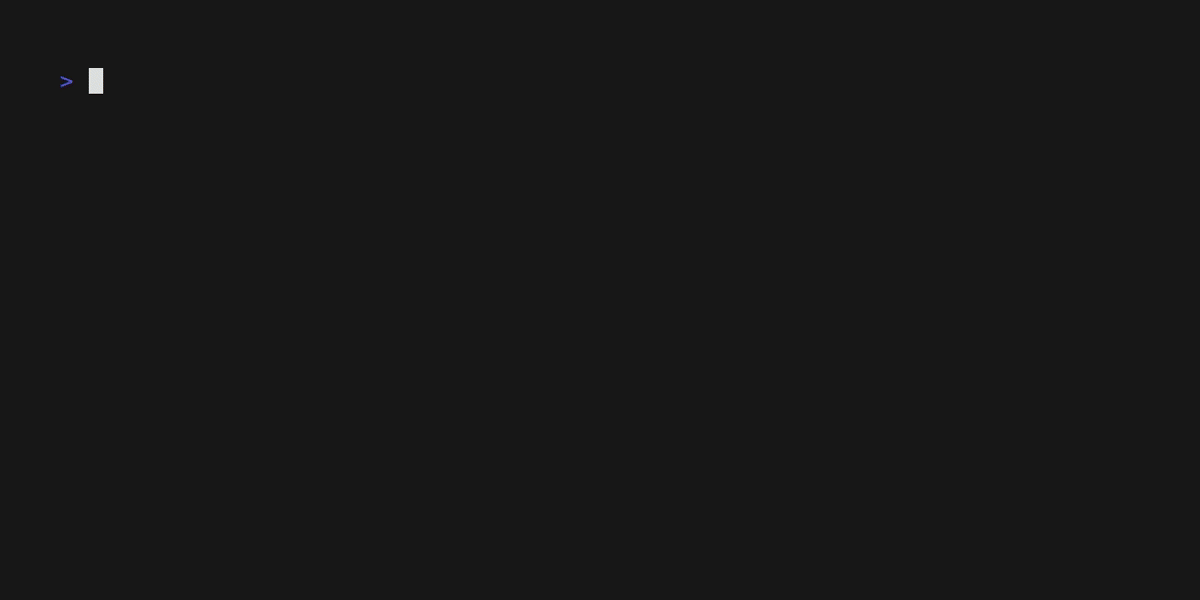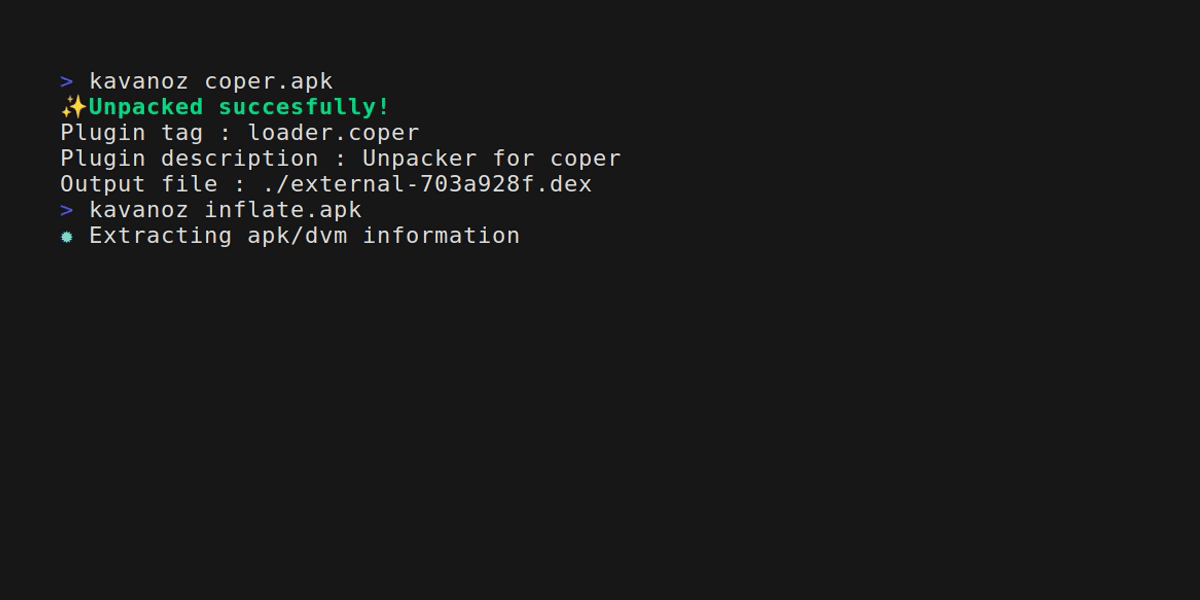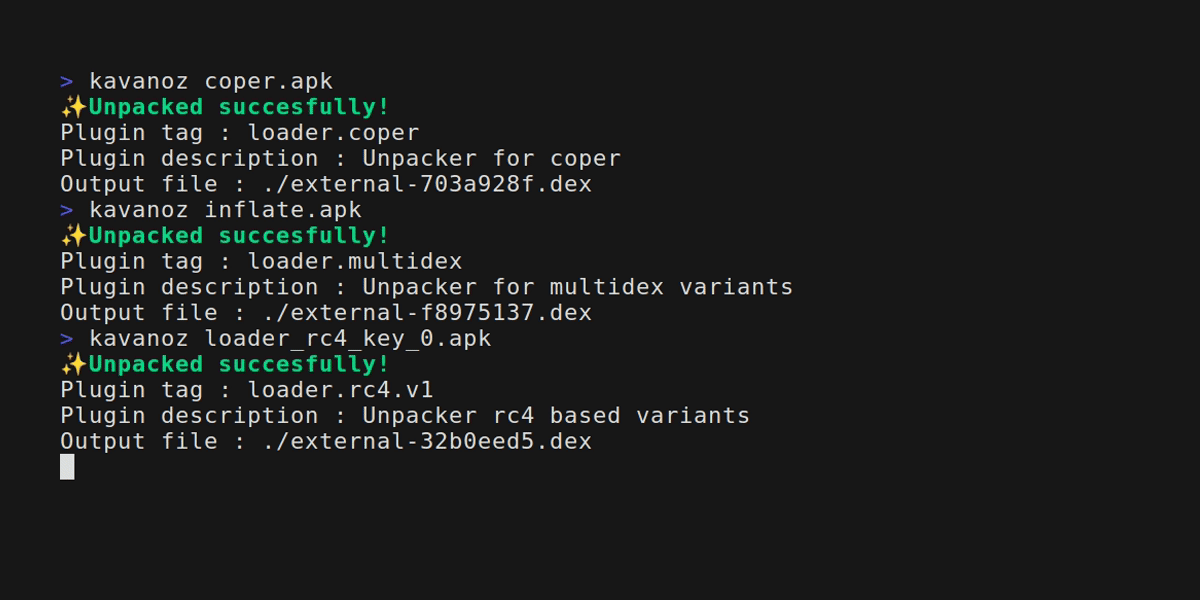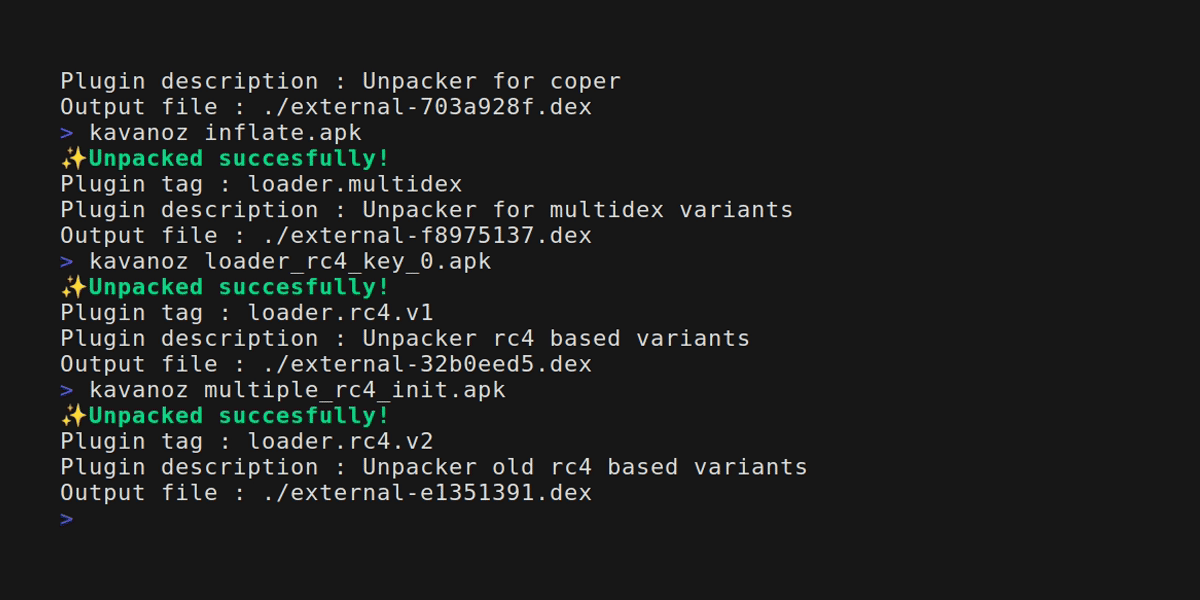 eybisi/kavanoz
Statically unpacking common android banker malware.
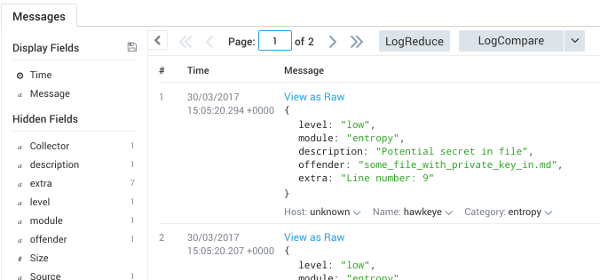 hawkeyesec/scanner-cli
A project security/vulnerability/risk scanning tool
 google/paranoid_crypto
Paranoid's library contains implementations of checks for well known weaknesses on cryptographic artifacts.
 certcc/cve-2021-44228_scanner
Scanners for Jar files that may be vulnerable to CVE-2021-44228