
Open-Source-Seal-Security
 ronmadar/open-source-seal-security
Fix open source package uses tough-cookie 2.5.0 - CVE-2023-26136,
code-analysiseducationstatic-analysis+2
ronmadar/open-source-seal-securityFix open source package uses tough-cookie 2.5.0 - CVE-2023-26136,

 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 de4dot/de4dot
.NET deobfuscator and unpacker.
 ejfkdev/ddc
DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI
 beardypig/ghidra-emotionengine
Ghidra Processor for the Play Station 2's Emotion Engine MIPS based CPU
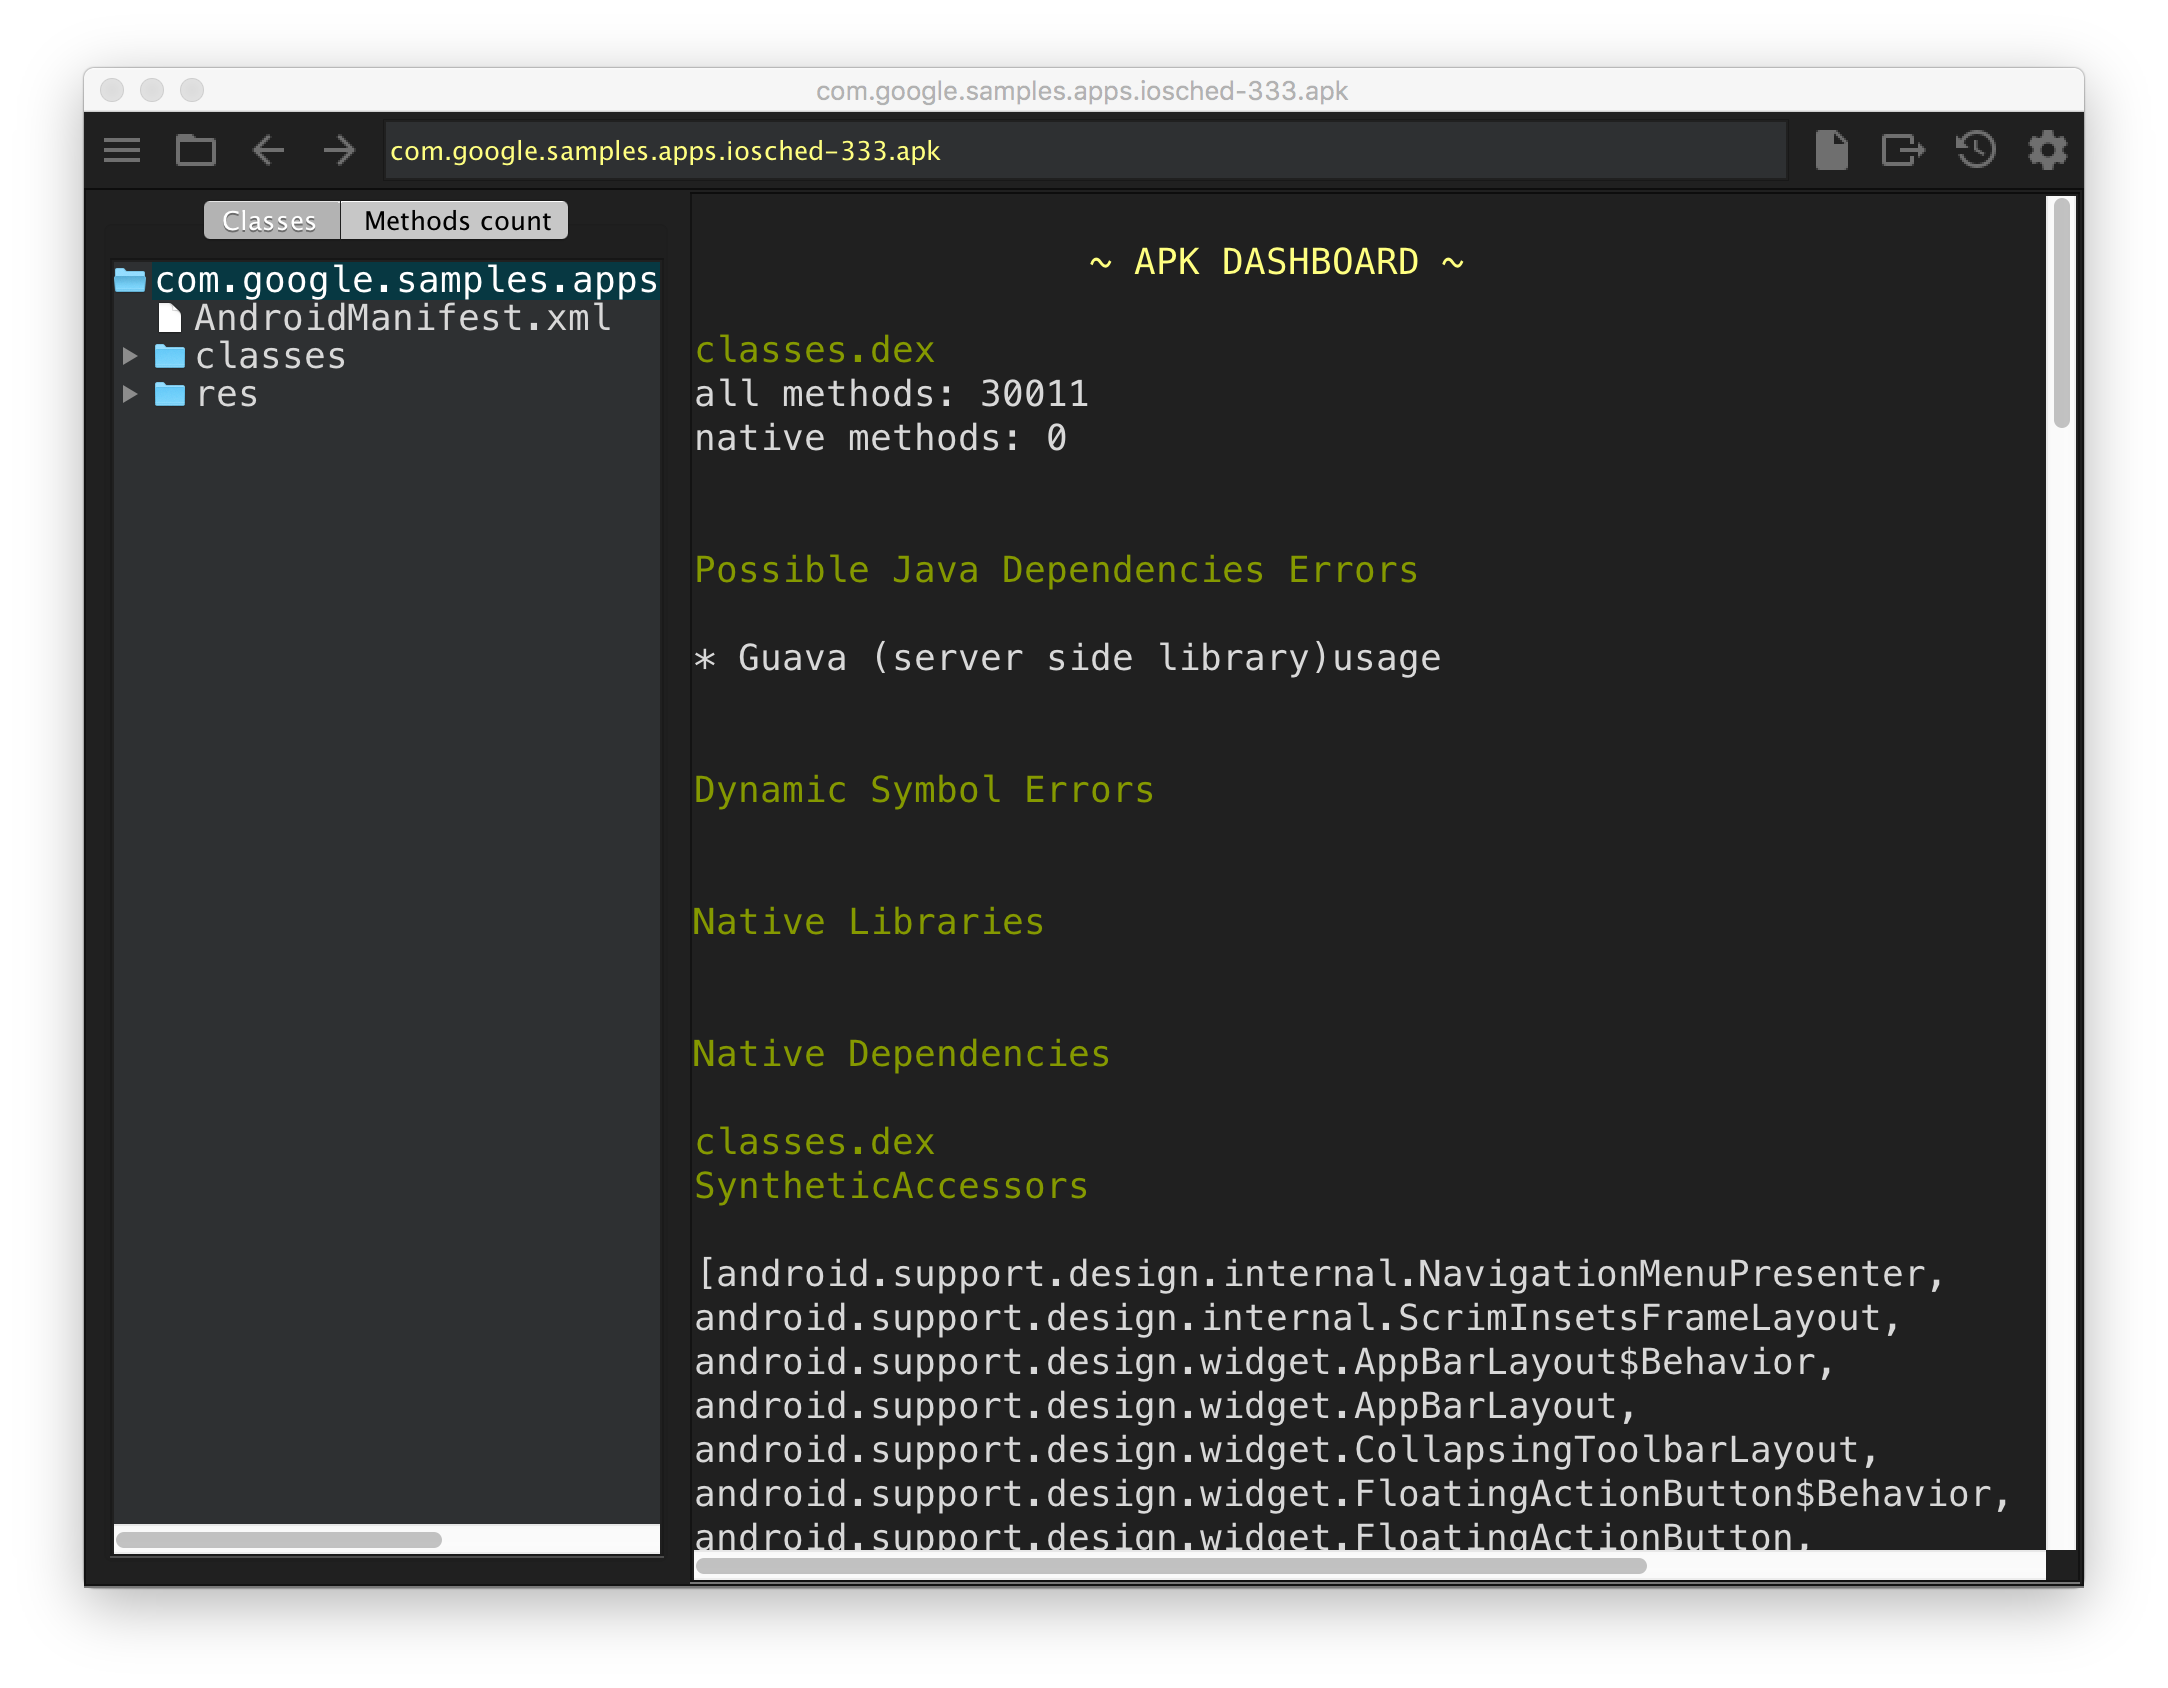 google/android-classyshark
Android and Java bytecode viewer
 mozilla/bleach
Bleach is an allowed-list-based HTML sanitizing library that escapes or strips markup and attributes
 certcc/trommel
TROMMEL: Sift Through Embedded Device Files to Identify Potential Vulnerable Indicators
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 ssh-pur66/cve-replay
Independent offline regression of CVE-2026-44431 across pinned urllib3 releases, with original reporter attribution.
 soulghost/iblessing
iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis. It can…
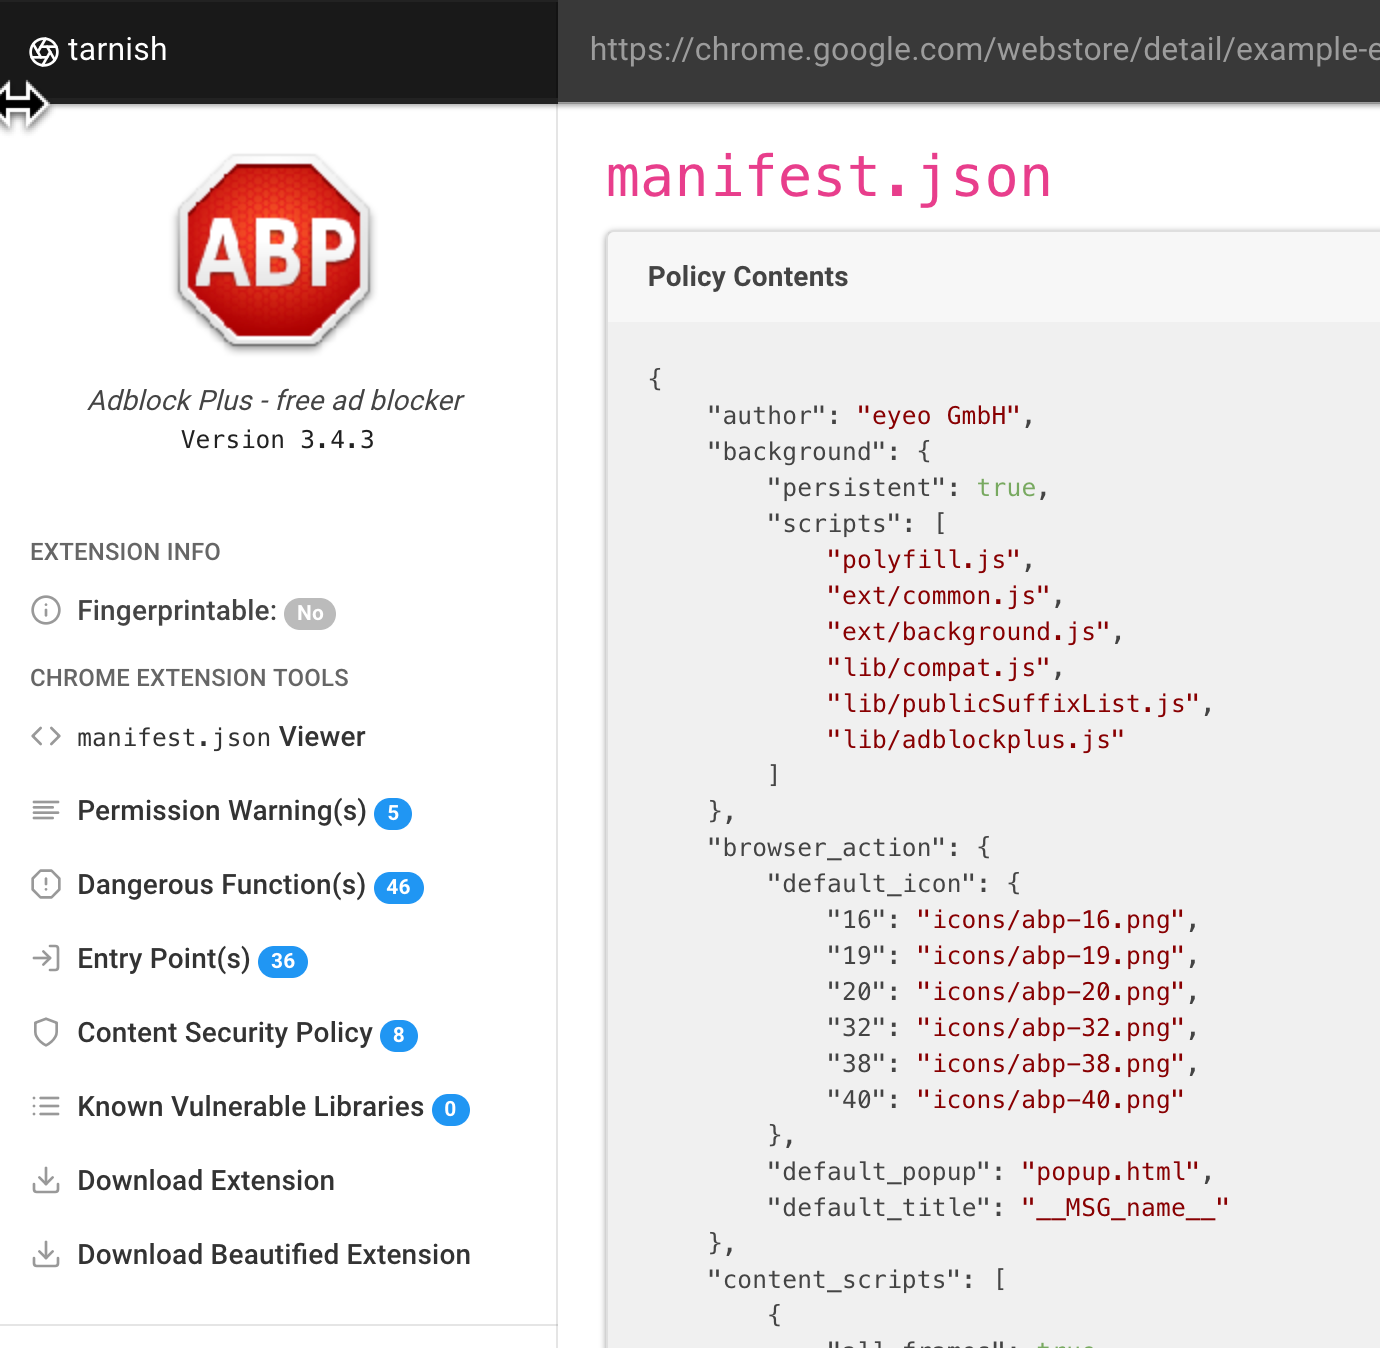 mandatoryprogrammer/tarnish
A Chrome extension static analysis tool to help aide in security reviews.
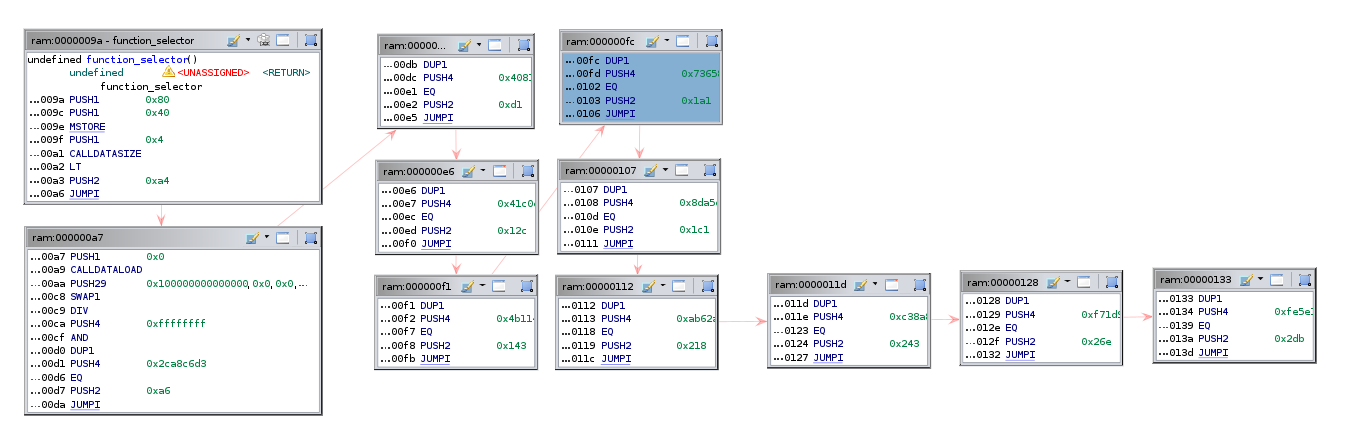 adelapie/ghidra-evm
Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
 emicoecommerce/magento-apsb22-48-security-patches
This repository contains potential security patches for the Magento APSB22-48 and CVE-2022-35698 security vulnerability
 elevenpaths/pesto
Extracts and analyzes PE file security characteristics (ASLR, DEP, CFG, NO_SEH) from DLLs and EXEs across directories, storing results in a SQLite…