
AppInfoScanner
 kelvinben/appinfoscanner
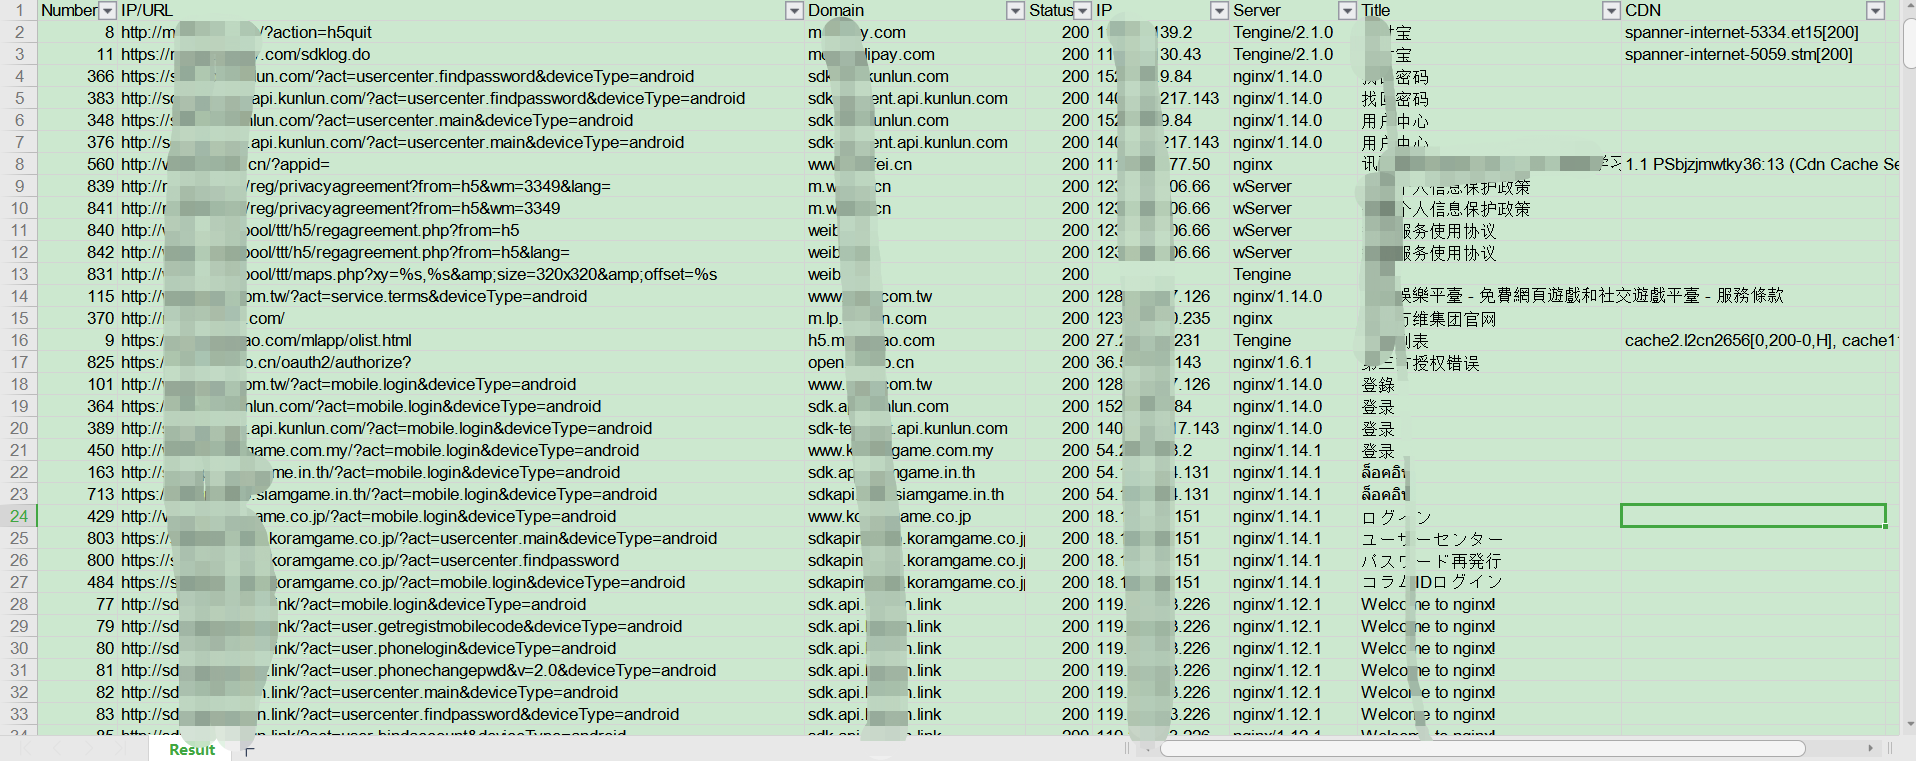
一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
android-securityinformation-gatheringios-security+6
3.6k
kelvinben/appinfoscanner一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
 xiaoqimikko/pac4j-check
Offline scanner for CVE-2026-29000 (CVSS 10.0) in org.pac4j:pac4j-jwt. Inspects jars/fat-jars directly, so it works where mvn dependency:tree cannot.…
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 bekwiner/cve-2026-47777
Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 shalevo13/se7enslip
A scanner and testter of the CVE-2025-11001 of 7-zip
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-23457_2-2-3-1
Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…