
pki-toolbox
 youkyi/pki-toolbox
Client-side PKI toolbox that decodes X.509, CSR, chain, CRL, PKCS#7 and PKCS#12 artifacts, views ASN.1, converts formats, and generates self-signed…
cryptographydefensive-toolsencryption-decryption-tools+4
6
youkyi/pki-toolboxClient-side PKI toolbox that decodes X.509, CSR, chain, CRL, PKCS#7 and PKCS#12 artifacts, views ASN.1, converts formats, and generates self-signed…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 anchore/grype
A vulnerability scanner for container images and filesystems
 vulnex/bytesrevealer
Online Reverse Enginerring viewer
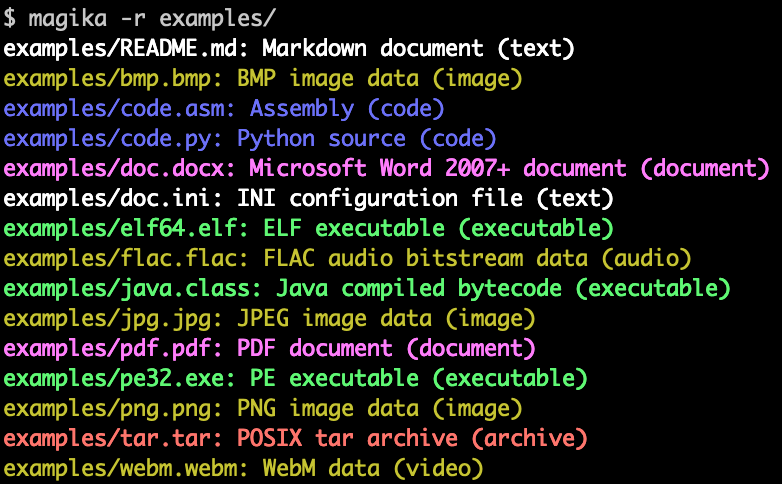 google/magika
Fast and accurate AI powered file content types detection
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 skyscanner/cfripper
Library and CLI tool for analysing CloudFormation templates and check them for security compliance.
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.

 loadingalias/rscrypto
Rust cryptography w/ zero required deps: hashes, checksums, MACs, KDFs, password hashing, AEADs, signatures, RSA, key exchange, ML-KEM, and ML-DSA.…
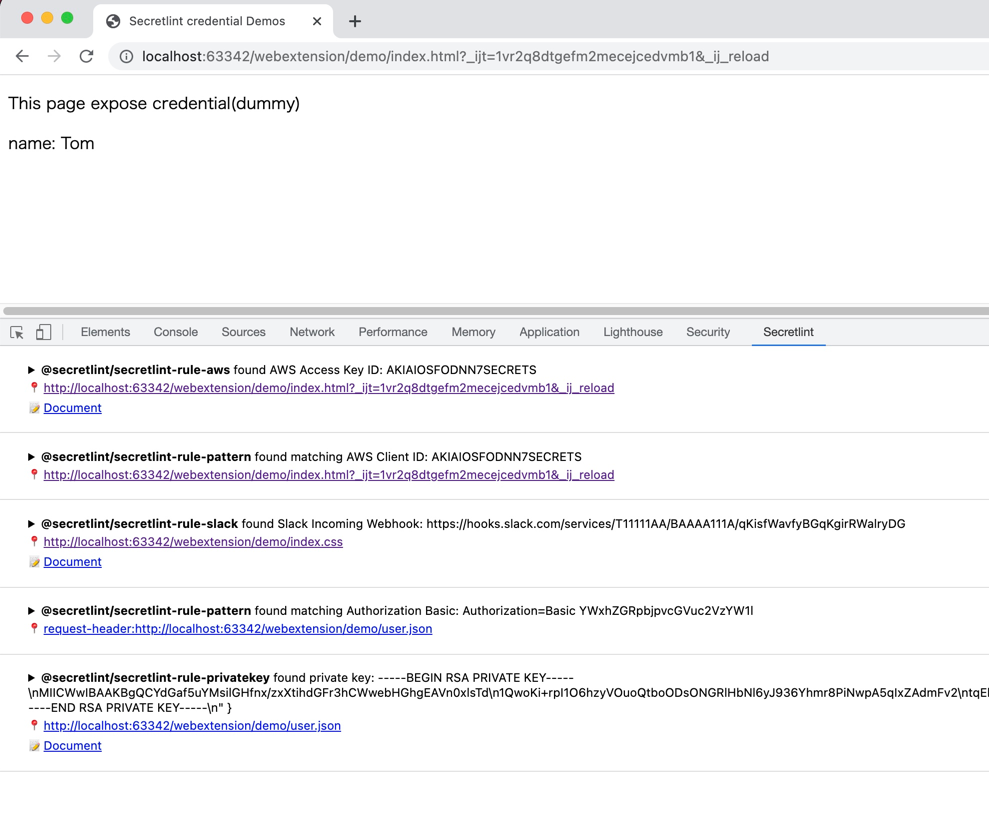 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 jsonpath-plus/jsonpath
A fork of JSONPath from http://goessner.net/articles/JsonPath/
 gautamvarmadatla/mcpsafetywarden
Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 spamscanner/spamscanner
Spam Scanner is a Node.js anti-spam, email filtering, and phishing prevention tool and service. Built for @ladjs, @forwardemail, @cabinjs, @breejs,…
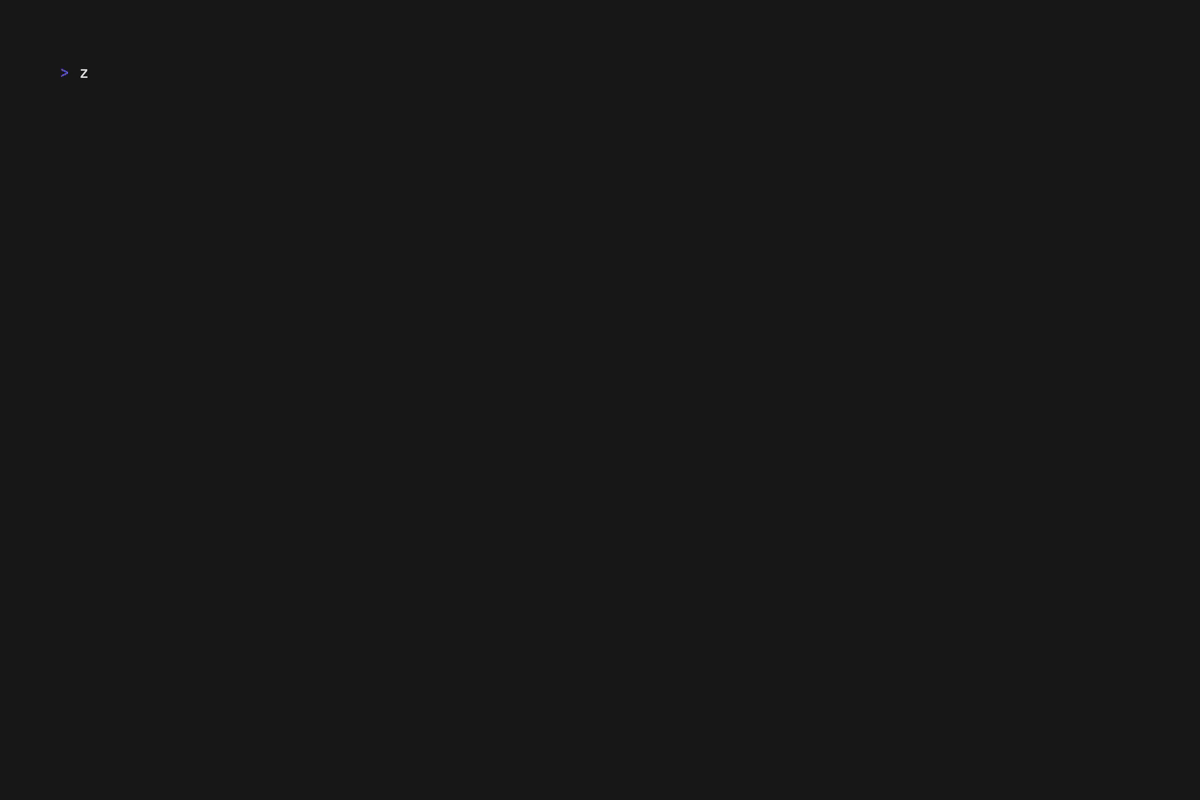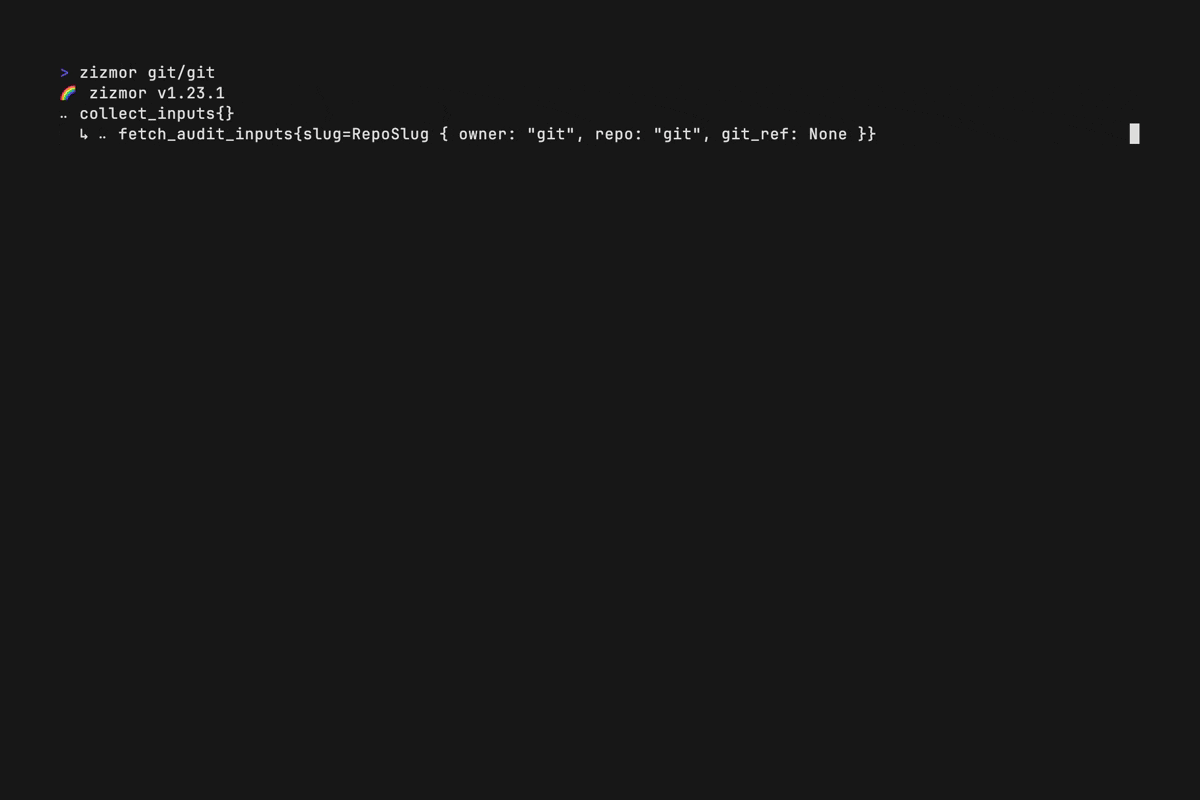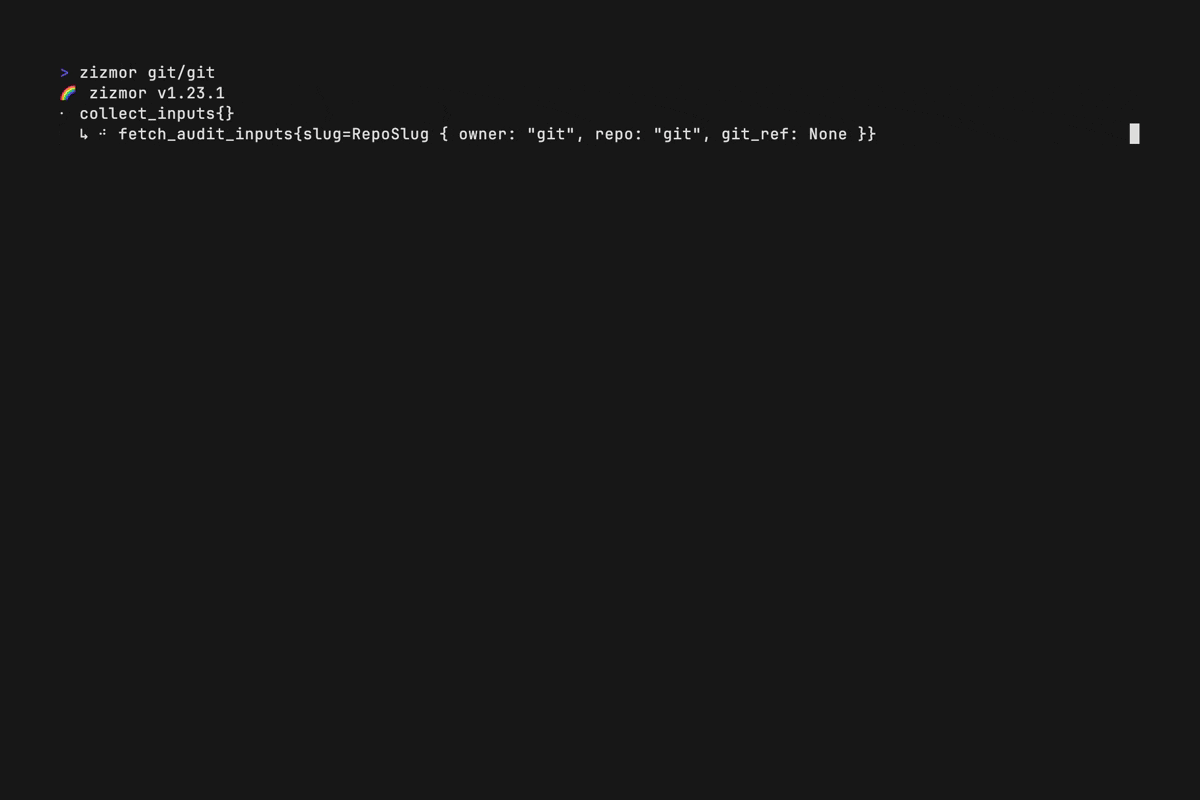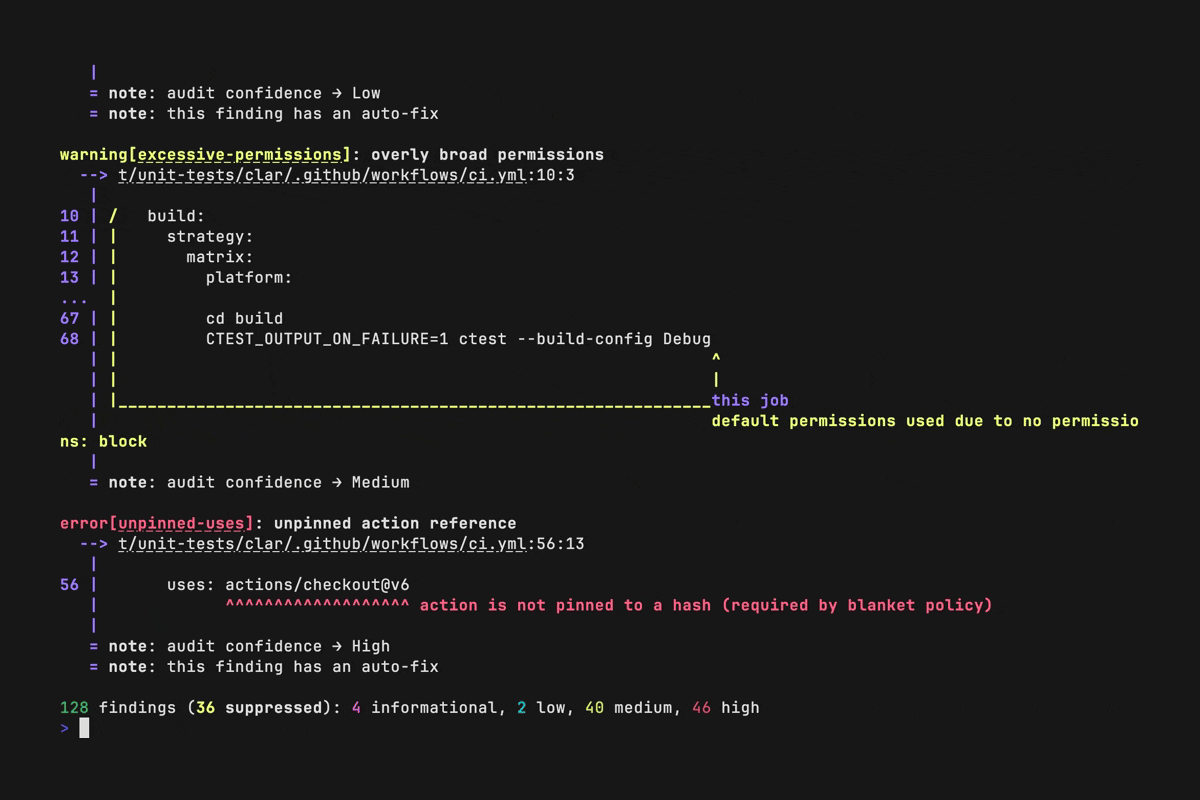 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…