

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
53 results
Capsulith preview

Capsulith

GitHubnazeeh111/capsulith

Run preserved ARM64 code in Node or a browser; inspect decoded image pixels and initialized memory.

binary-analysisbinary-exploitationdebuggers+5
1 day ago
rea-rust preview

rea-rust

GitHubnanashili/rea-rust

Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker

ai-assisted-reversingbinary-analysisdebuggers+7
632 days ago
pycdc preview

pycdc

GitHubejfkdev/pycdc

Decompile and disassemble Python bytecode (.pyc/.pyo) back to readable source. Supports Python 2.0 - 3.15 (CPython, PyPy and other implementations).…

binary-analysiscode-analysisdebuggers+4
85 days ago
ceasta preview

ceasta

GitHubngwg/ceasta

Disassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…

ai-assisted-reversingbinary-analysisbinary-exploitation+6
1781 month ago
idamcp preview

idamcp

GitHubidamcp/idamcp

MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…

ai-assisted-reversingbinary-analysisdebuggers+3
12513h 36m ago
AIDebug preview

AIDebug

GitHubanpa1200/aidebug

Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
ai-securitybinary-analysisdebuggers+7
1519 days ago
not-slithering-anywhere preview

not-slithering-anywhere

GitHubtrailofbits/not-slithering-anywhere

The Python Version of our Not Go-ing Anywhere Vulnerable Application
dynamic-analysis-sandboxingeducationlabs-practice+3
113 years ago
xed preview

xed

GitHubintelxed/xed

Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
binary-analysiscode-analysisdebuggers+3
1.6k2 months ago
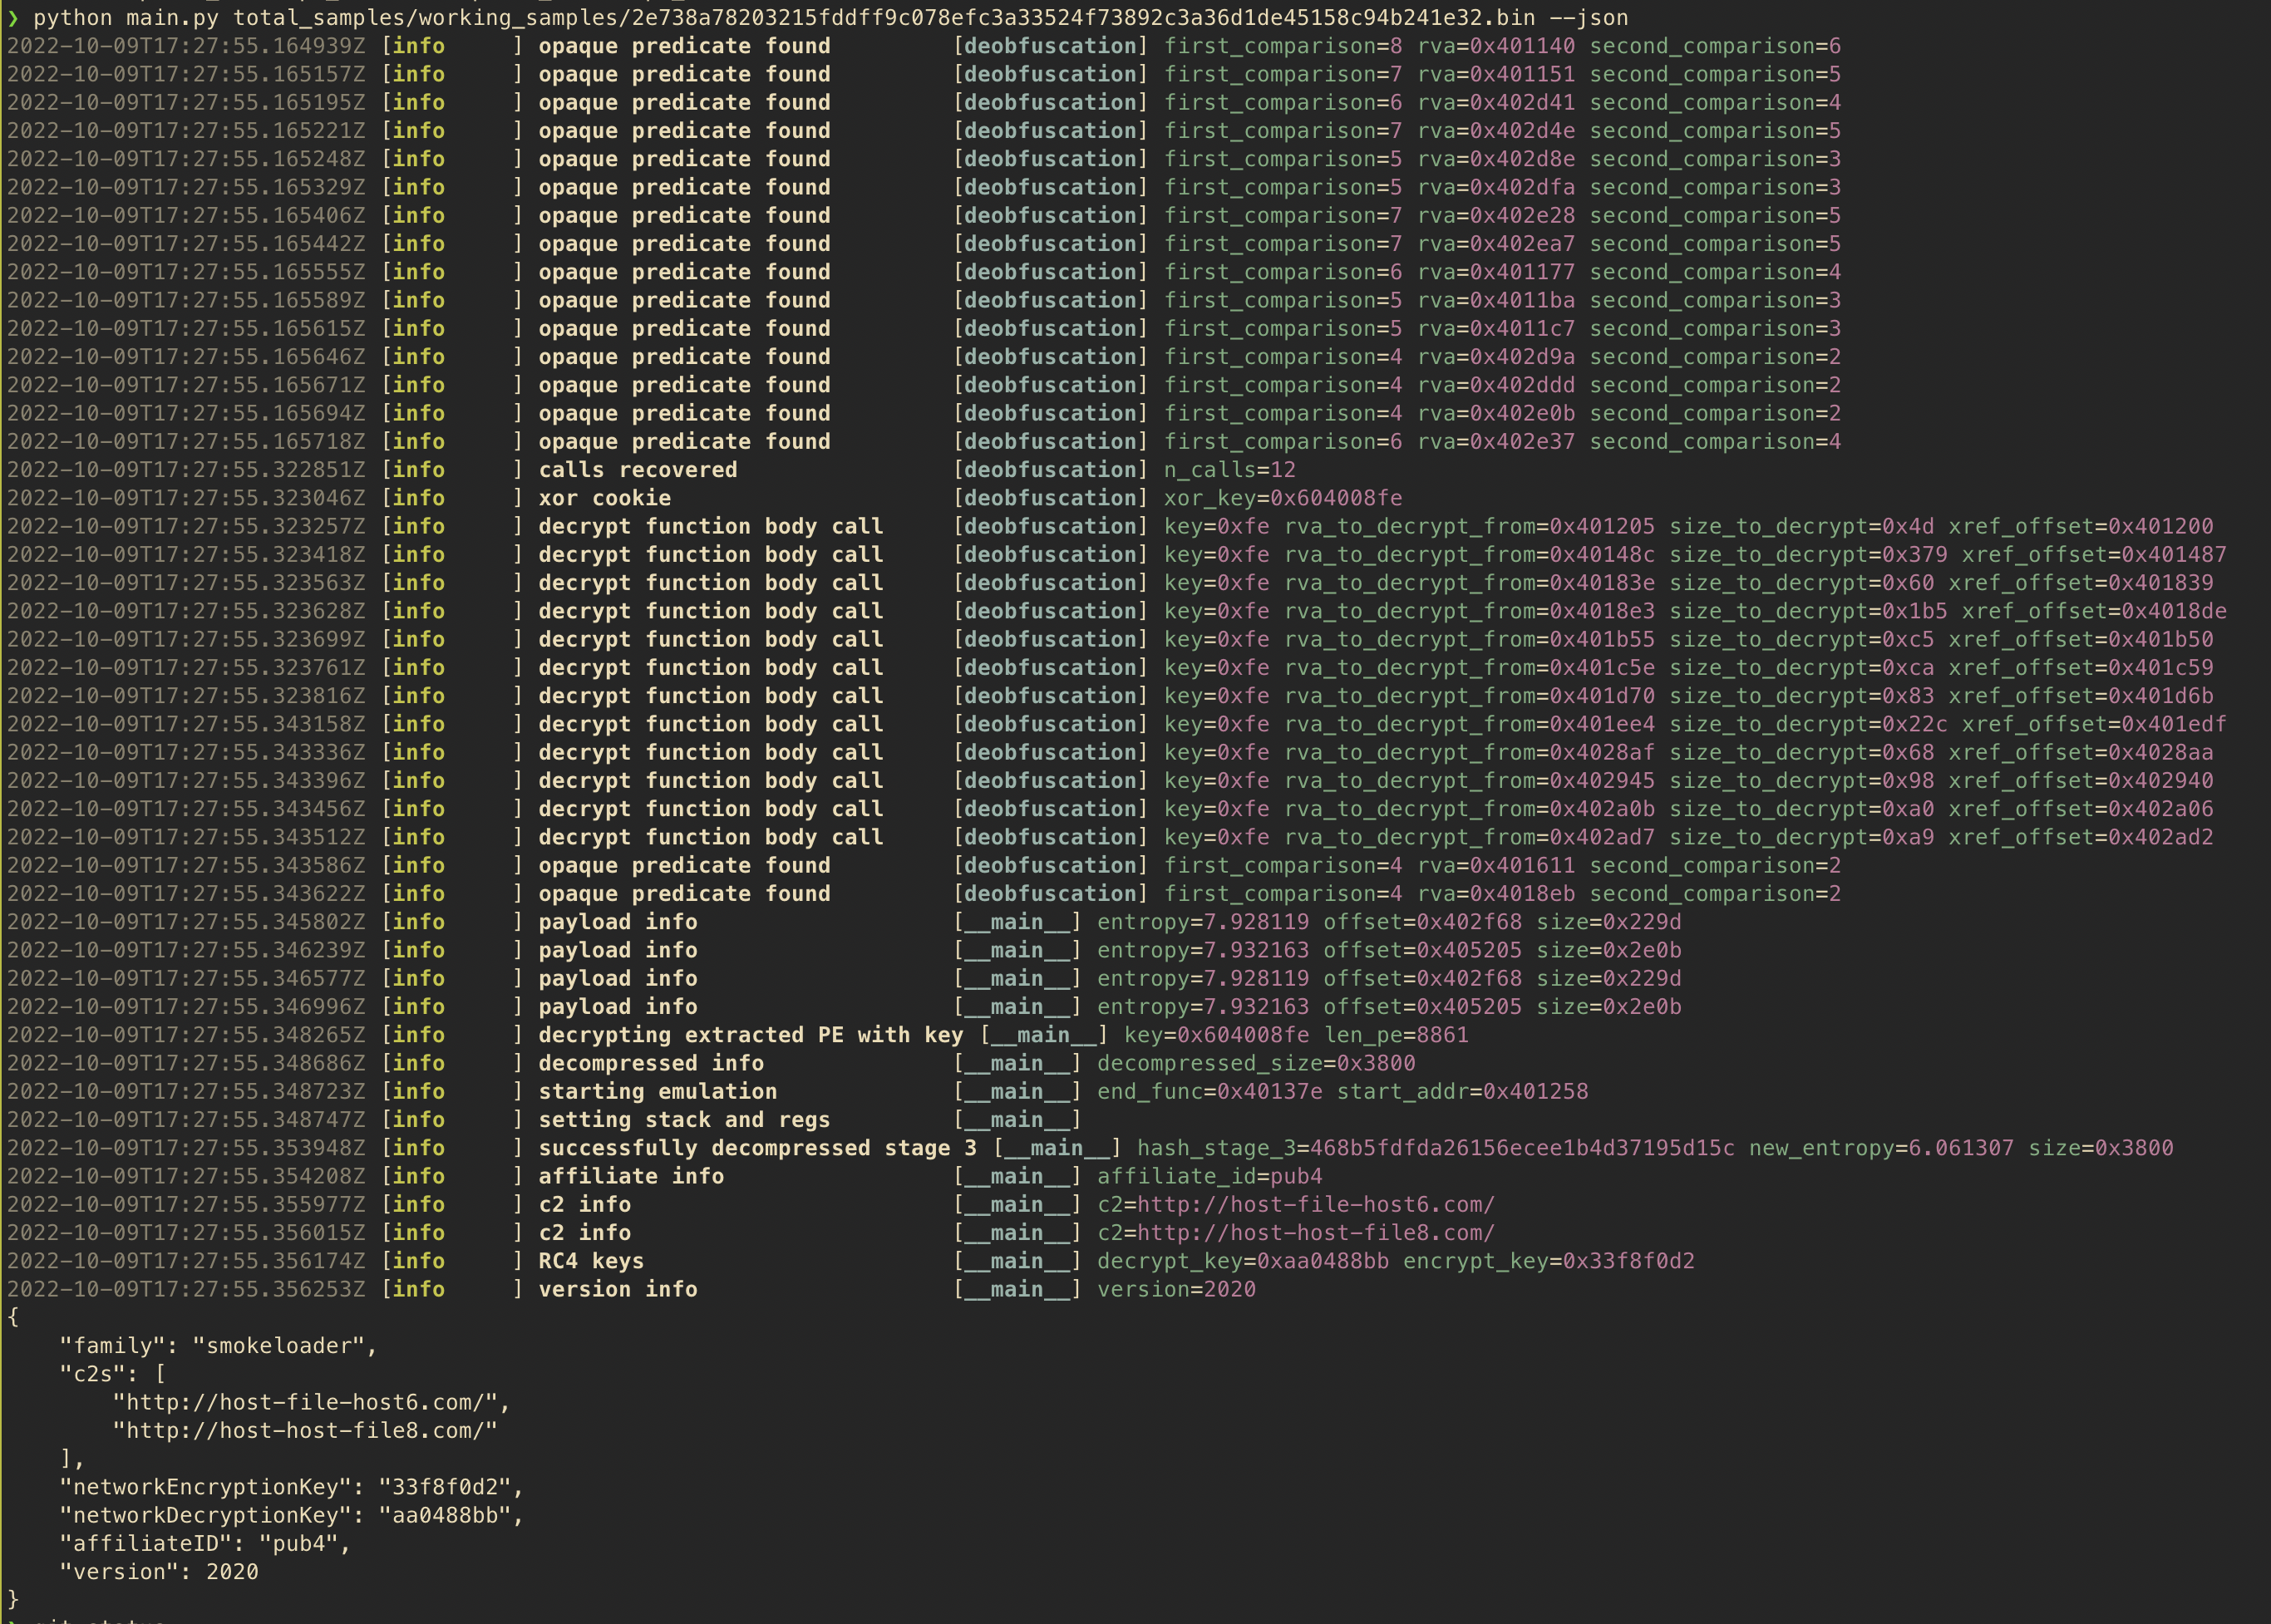
smoke_conf_extract preview

smoke_conf_extract

GitHubmyrtus0x0/smoke_conf_extract

Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.
binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
133 years ago
fastjson-jsontype-rce-lab preview

fastjson-jsontype-rce-lab

GitHubdinosn/fastjson-jsontype-rce-lab

Docker labs + defensive scanner for fastjson remote-class-load RCE. fastjson 1.2.66-1.2.83: @JSONType resource probe (CVE-2026-16723). fastjson2…
dynamic-analysis-sandboxingeducationexploitation+5
2073 months ago
svg_phishing_tools preview

svg_phishing_tools

GitHubhackinglz/svg_phishing_tools

SVG Analysis and generation tools for commonly seen SVG attachment phishing
dynamic-analysis-sandboxinginformation-gatheringmalware-analysis+5
571 year ago
paimei preview

paimei

GitHubopenrce/paimei

A reverse engineering framework written in Python.
binary-analysiscode-analysisdebuggers+6
50814 years ago
LitterBox preview

LitterBox

GitHubblacksnufkin/litterbox

A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end…

ai-securitydynamic-analysis-sandboxingmalware-analysis+4
1.6k5 months ago
RATDecoders preview

RATDecoders

GitHubkevthehermit/ratdecoders

Python Decoders for Common Remote Access Trojans
dynamic-analysis-sandboxingforensicsincident-response+6
1.1k5 years ago
Kaspersky_CVE-2024-3094 preview

Kaspersky_CVE-2024-3094

GitHubvesjolyjd/kaspersky_cve-2024-3094

Security review of CVE-2024-3094 (XZ Utils backdoor) including threat modeling, static/dynamic code analysis, fuzzing with AFL++, and a…
code-analysisdynamic-analysis-sandboxingeducation+7
6 months ago
hyperion-disassembler preview

hyperion-disassembler

GitHubsidenai/hyperion-disassembler

Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery

binary-analysisdebuggerseducation+5
2304 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubfkshield/cve-2025-5548

End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
binary-exploitationdynamic-analysis-sandboxingeducation+9
3 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubalberto-galindo/cve-2025-5548

Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…

binary-exploitationdebuggerseducation+8
7 months ago
Previous123Next