

wolf-tools
 rtkwlf/wolf-tools
Scans Windows, Linux, and macOS hosts for Java packages containing JndiLookup.class to detect Log4Shell (CVE-2021-44228, CVE-2021-45046) exposure and…
configuration-auditingdefensive-toolsincident-response+4
87
rtkwlf/wolf-toolsScans Windows, Linux, and macOS hosts for Java packages containing JndiLookup.class to detect Log4Shell (CVE-2021-44228, CVE-2021-45046) exposure and…
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 suhanmen/sew
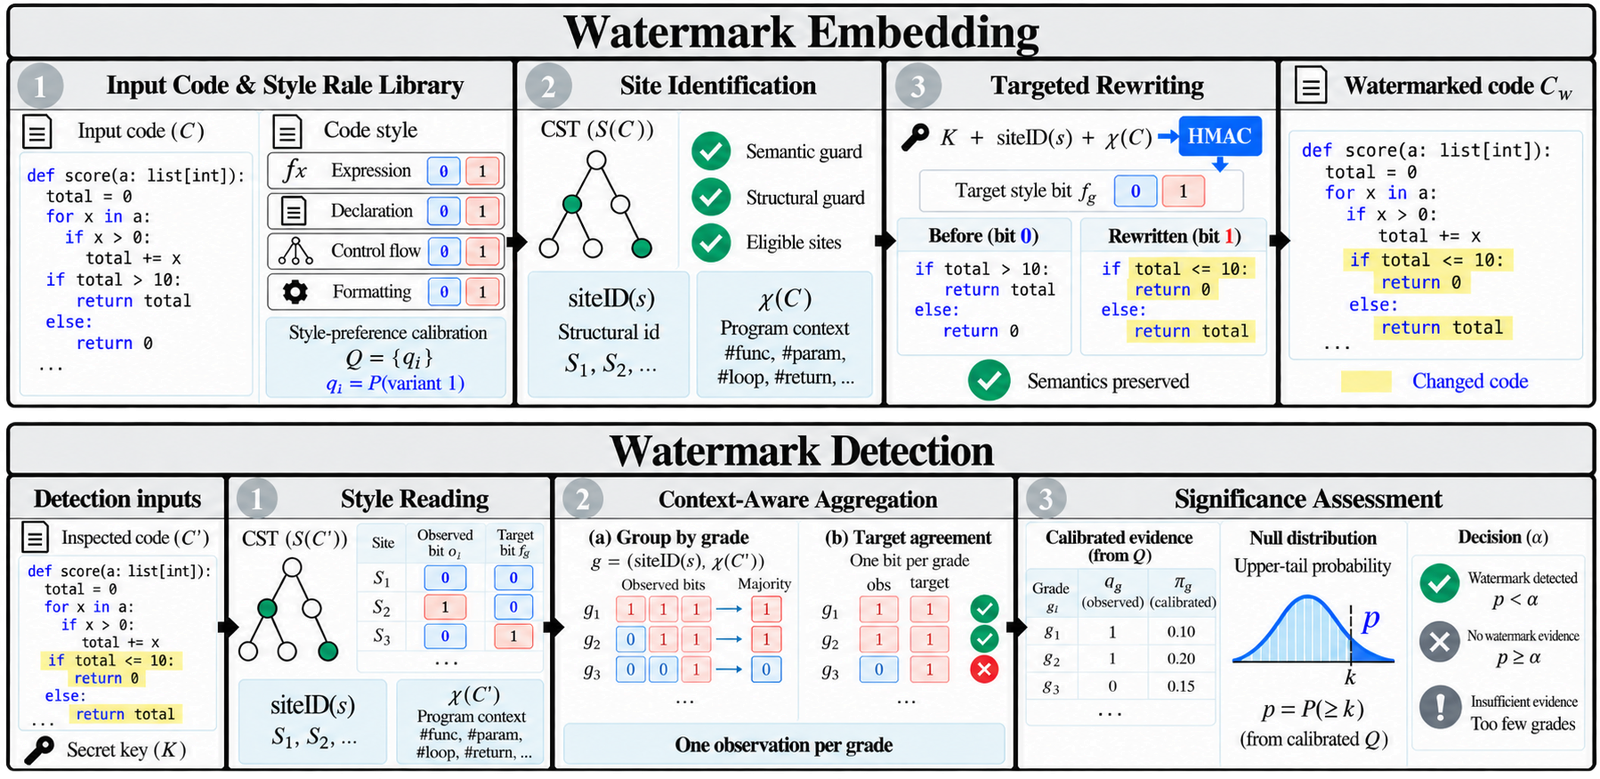
Embeds and detects keyed, style-based watermarks in LLM-generated Python, Java, and C++ code via CST rewriting, preserving functional correctness and…
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator
 gmh5225/ghidra_svr_bridge
Binary Ninja plugin that syncs analysis bidirectionally with a Ghidra Server repository, via a Java bridge subprocess.
 xiaoqimikko/async-http-client-check
Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…
 xiaoqimikko/netty-resolver-dns-check
Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 xiaoqimikko/thymeleaf-check
Offline checker for Thymeleaf CVE-2026-40477 / CVE-2026-41901 — tells you which of the two CVSS 9.0 SSTI flaws you are exposed to, and whether your…
 wadingporque/apkprobe
APK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…
 pelock/jobfuscator
Obfuscates Java source code to protect against reverse engineering, decompilation, and IP theft. Renames variables/methods, encrypts strings, and…
 mario-kart-felix/a-potential-denial-of-service-issue-in-protobuf-java
Detailed analysis of CVE-2021-22569, a high-severity denial-of-service vulnerability in protobuf-java, including affected versions, patched versions,…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 xiaoqimikko/shiro-check
扫出你实际装的 Apache Shiro 模块与版本,逐条判定官方 26 条 CVE 里哪些真的落在你身上。按「CVE × 模块」判定,零依赖单 jar。 CVE-2026-49268
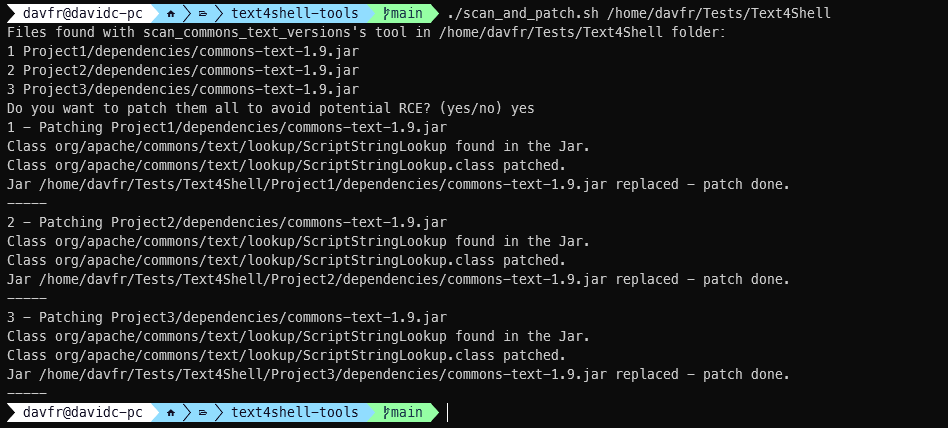 jfrog/text4shell-tools
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…
 xiaoqimikko/scc-check
Offline checker for Spring Cloud Config CVE-2026-40982 — tells you whether your version line has an OSS fix at all (3.1.x/4.1.x/4.2.x: it does not)