

wolf-tools
 rtkwlf/wolf-tools
Scans Windows, Linux, and macOS hosts for Java packages containing JndiLookup.class to detect Log4Shell (CVE-2021-44228, CVE-2021-45046) exposure and…
configuration-auditingdefensive-toolsincident-response+4
87
rtkwlf/wolf-toolsScans Windows, Linux, and macOS hosts for Java packages containing JndiLookup.class to detect Log4Shell (CVE-2021-44228, CVE-2021-45046) exposure and…
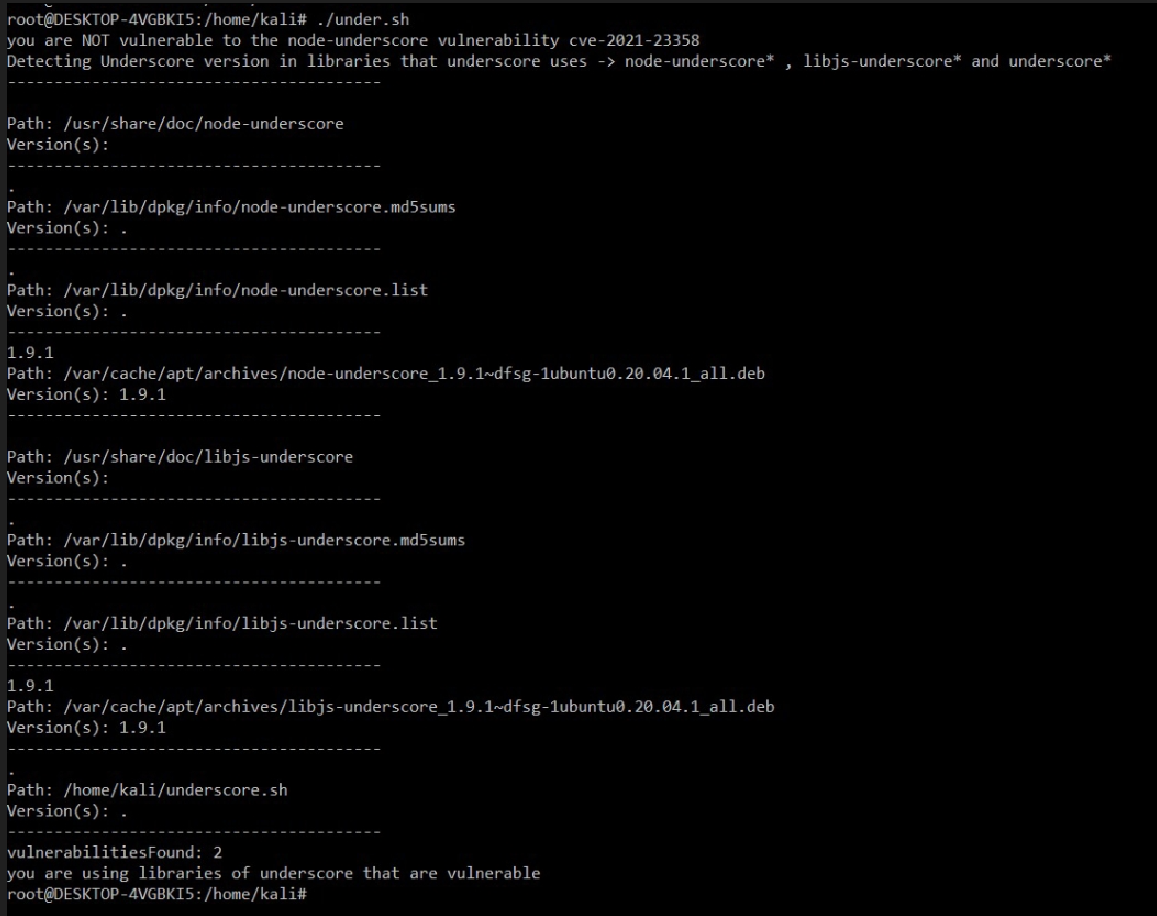 ekamsinghwalia/detection-script-for-cve-2021-23358
Detection script for cve-2021-23358
 saharnooby/log4j-vulnerability-patcher-agent
Fixes CVE-2021-44228 in log4j by patching JndiLookup class
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 name/log4j-scanner
Discover Log4Shell vulnerability [CVE-2021-44832]
 occamsec/log4j-checker
Bash and PowerShell scripts to scan a local filesystem for Log4j .jar files which could be vulnerable to CVE-2021-44228 aka Log4Shell.
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)
 pcmkuit/cve-2021-44228---log4shell-analysis
Technical deep dive into Apache Log4j2 JNDI injection vulnerability. Features static code analysis, patch comparison, attack vectors (LDAP/RMI/DNS),…
 rvermeulen/codeql-workshop-cve-2021-21380
A CodeQL workshop covering CVE-2021-21380
 inettgmbh/checkmk-log4j-scanner
Checkmk extension that scans JAR, WAR, EAR, and AAR files for Log4j versions vulnerable to CVE-2021-44228 by inspecting META-INF pom.properties…
 hozyx/log4shell
Applications that are vulnerable to the log4j CVE-2021-44228/45046 issue may be detectable by scanning jar, war, ear, zip files to search for the…
 george-petrakis/log4j-scanner-cve-2021-44228
Simple tool for scanning entire directories for attempts of CVE-2021-44228
 frenzymadness/cve-2021-3572
Minimal test repository for CVE-2021-3572, demonstrating a pip dependency confusion vulnerability and its fix across vulnerable and patched versions.
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
 dn9uy3n/check-cve-2021-23383
Check the conditions for exploiting CVE-2021-23383 through the handlebars library version assessment.
 dbzoo/log4j_scanner
Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…
 k271266/cve-2021-42694
Static analysis tool to detect homoglyph substitution attacks in source code, scanning Python identifiers for visually similar Unicode characters to…
 alexpena5635/cve-2021-44228_scanner-main-modified-
Scans jar, war, and ear files for the presence of JndiLookup.class to detect applications vulnerable to CVE-2021-44228 (Log4Shell).