

work1-secure-api
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
api-securityauthentication-authorizationdevsecops+7
ght657/work1-secure-apiHDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 shalevo13/se7enslip
A scanner and testter of the CVE-2025-11001 of 7-zip
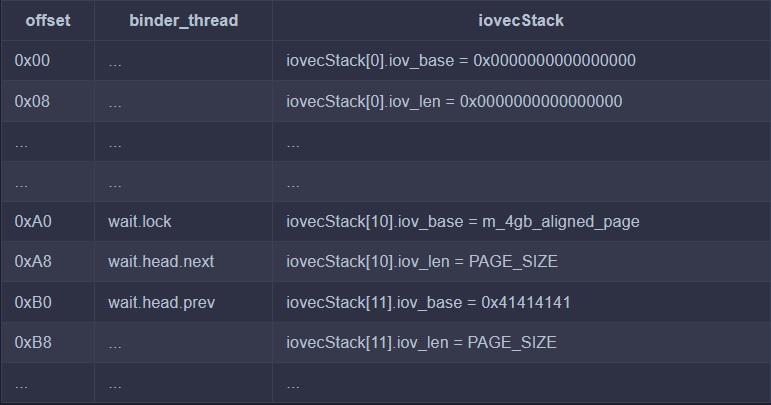 sharif-dev/androidkernelvulnerability
Triggering and Analyzing Android Kernel Vulnerability CVE-2019-2215
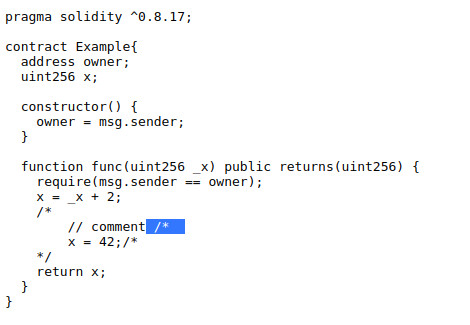 tin-z/solidity_cve-2021-42574-poc
POC of CVE-2021-42574 for solidity and solc compiler
 uriyahav/tough-cookie-2.5.0-cve-2023-26136-fix
ecurity patch for CVE-2023-26136 in tough-cookie 2.5.0 - Prototype pollution vulnerability fix with backward compatibility
 ricedu/struts1-patch
struts1 CVE-2014-0114 classLoader manipulation vulnerability patch
 rgielen/struts1filter
A request parameter filter solution for Struts 1 CVE-2014-0114 based on the work of Alvaro Munoz and the HP Fortify team
 shoucheng3/srikanth-lingala__zip4j_cve-2018-1002202_1-3-2
Decompiled source code of zip4j library versions 1.3.2 (vulnerable) and 1.3.3 (fixed) for CVE-2018-1002202 path traversal analysis, part of the…
 yihtserns/spring-web-without-remoting
Spring Web 5.x with `org.springframework.remoting` package removed, to fix CVE-2016-1000027.
 nicpenning/rtf-cleaner
RTF de-obfuscator for CVE-2017-0199 documents to find URLs statically.
 u-maxx/magento-swf-patched-cve-2011-2461
Patched version of the uploader.swf and uploaderSingle.swf to fix CVE-2011-2461
 oitapps/find-vulnerableelectronversion
Scans an executable and determines if it was wrapped in an Electron version vulnerable to the Chromium vulnerability CVE-2023-4863/ CVE-2023-5129
 rootd4ddy/cve-2023-31584
Public disclosure for CVE-2023-31584.
 tiran/cve-2018-8970
Demo for https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-8970
 quandqn/cve-2018-14667
Proof-of-concept exploit for CVE-2018-14667, demonstrating Java deserialization combined with EL injection to achieve remote code execution in…
 samaujs/cve-2011-1475
Check with Maven on CVE-2011-1475
 murphysecurity/libwebp-checker
A tool for finding vulnerable libwebp(CVE-2023-4863)
 bde574786/sequelize-1day-cve-2023-25813
Proof-of-concept and technical analysis of CVE-2023-25813, a SQL injection vulnerability in Sequelize ORM versions prior to 6.19.1, including…