
TrueVerdict
 prox0959/trueverdict
Zero-dependency Windows PE provenance and false-positive reduction engine (Embedded Authenticode + OS Security Catalogs, Rich Header ROL32…
binary-analysisdefensive-toolsdigital-forensics+6
1
prox0959/trueverdictZero-dependency Windows PE provenance and false-positive reduction engine (Embedded Authenticode + OS Security Catalogs, Rich Header ROL32…
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
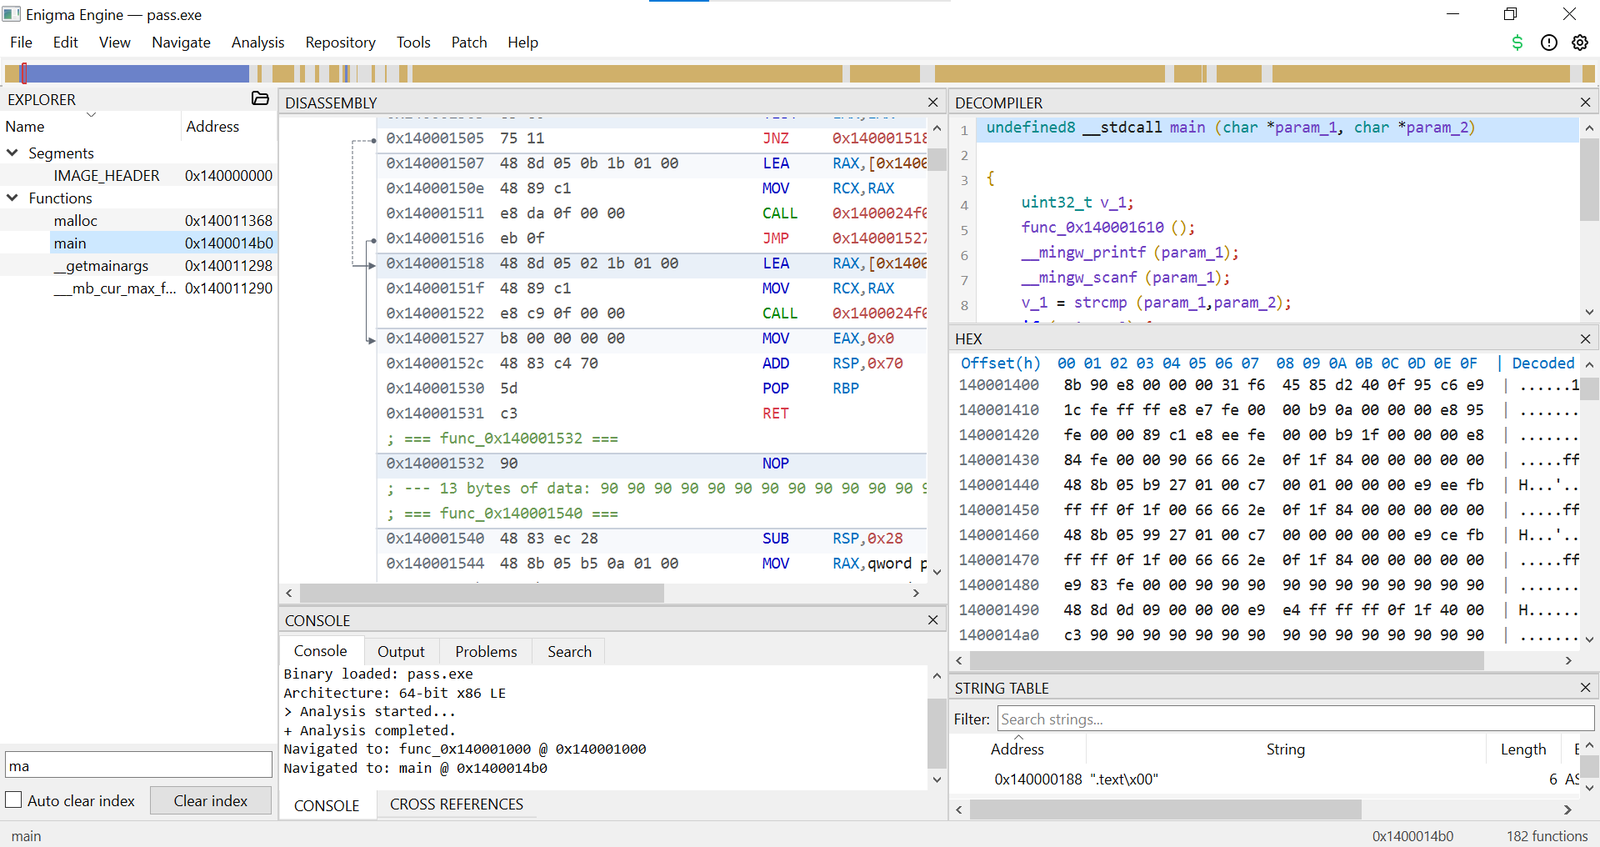 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 hydradragonantivirus/hydradragonav-mobile
Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware
 abusech/yaraify
Open YARA scan- and search engine
 califio/ngxray
ngxray — nginx config security scanner
 shoucheng3/jenkinsci__workflow-cps-plugin_cve-2022-25173_2646-v6ed3b5b01ff1
Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
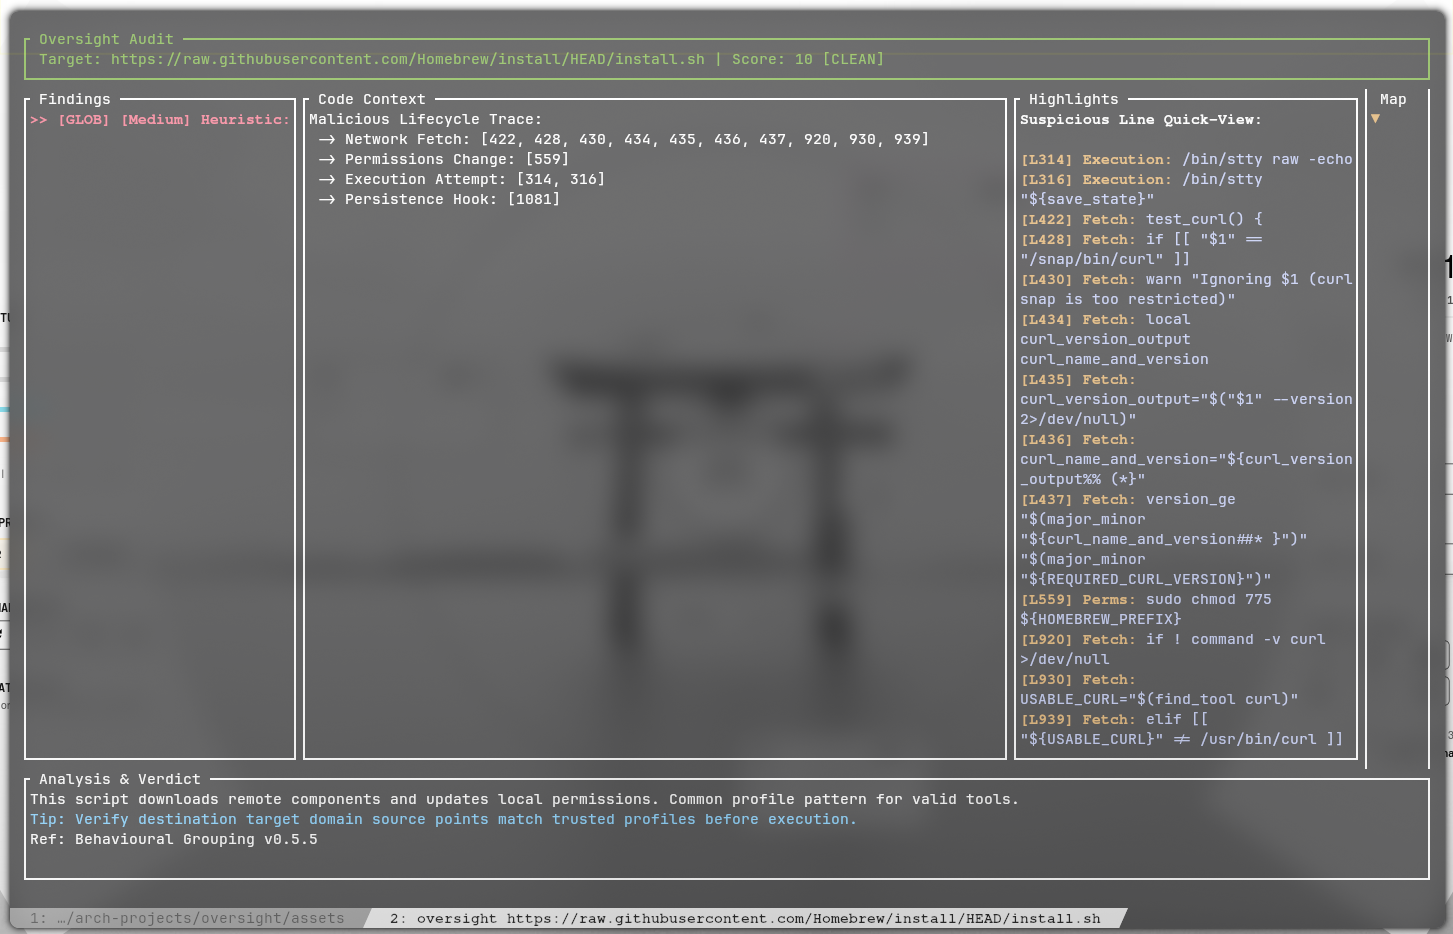 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
 satheesh575555/external_v8_aosp10_r33_cve-2021-0396
Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
 runreveal/sigmalite
Go library for parsing and executing Sigma detection rules against log entries, supporting field modifiers, CIDR matching, and custom field resolvers…
 noah4ever/sshconfig-lint
Rule-based linter for OpenSSH client config files that detects duplicate hosts, missing identity files, weak algorithms, wildcard ordering issues,…