
htmlpurifier
 ezyang/htmlpurifier
Standards compliant HTML filter written in PHP
code-analysisdefensive-toolsstatic-analysis+3
ezyang/htmlpurifierStandards compliant HTML filter written in PHP
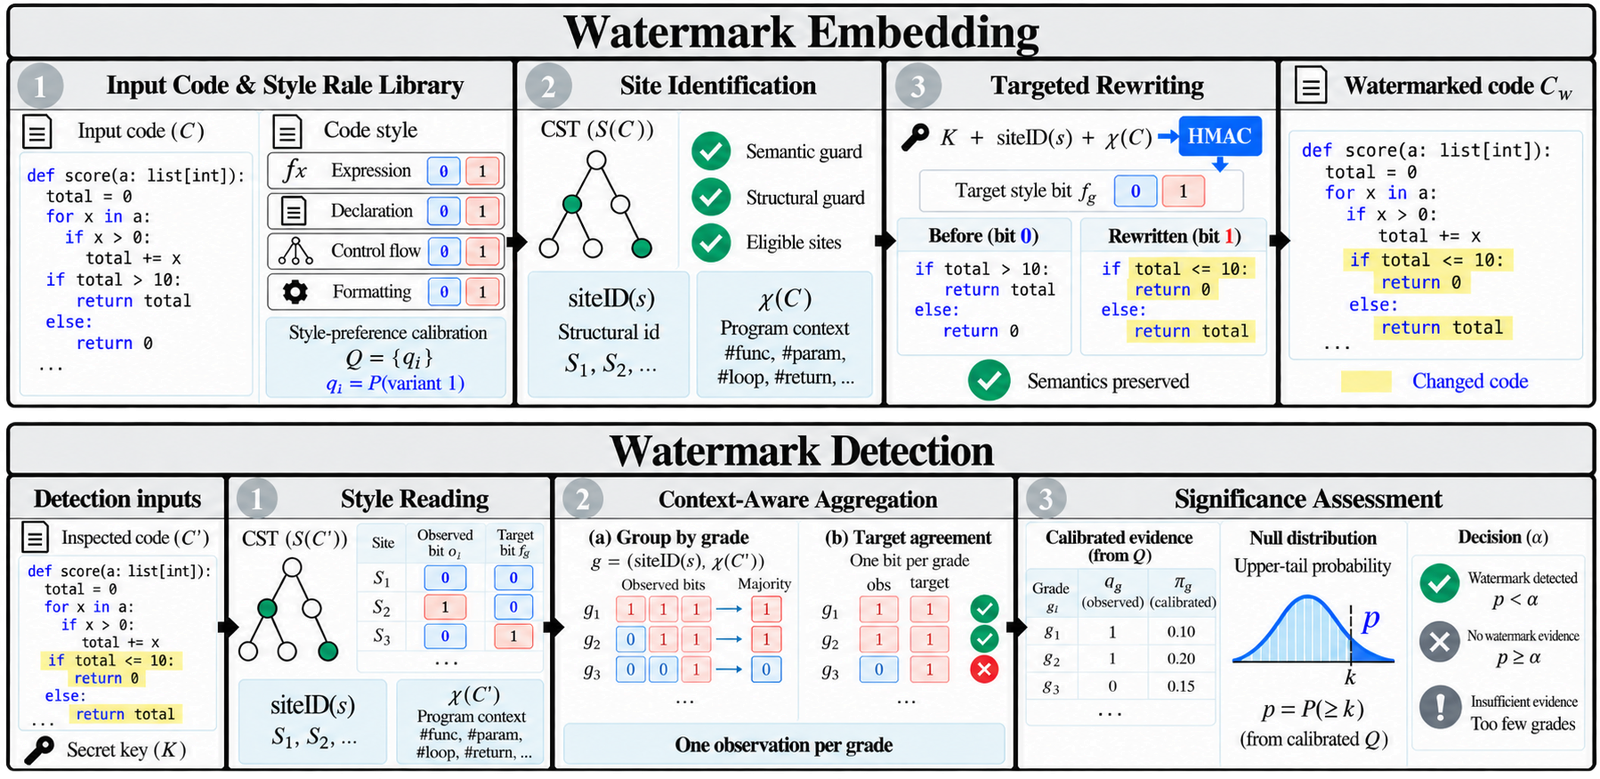 suhanmen/sew
Embeds and detects keyed, style-based watermarks in LLM-generated Python, Java, and C++ code via CST rewriting, preserving functional correctness and…
 protectai/modelscan
Protection against Model Serialization Attacks
 ossillate-inc/packj
Static and dynamic analysis tool that audits open-source packages for malicious, vulnerable, and risky attributes, with sandboxed installation to…
 mdshoaibuddinchanda/zombieguard
ML-based detection of Zombie ZIP archive header evasion attacks (CVE-2026-0866)
 c2sp/wycheproof
Project Wycheproof tests crypto libraries against known attacks.
 aniketkarne/aco-prompt-shield
Stop prompt injection attacks before they reach your LLM — zero API costs, runs entirely locally, integrates in 2 minutes. Prompt injection is the…
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 brennhill/sloppy-joe
Shields against supply-chain, slopsquatting, and typosquatting attacks from dependencies and code.
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
 digi4care/shai-scan
Zero-dependency CLI scanner for npm/PyPI supply chain compromises. Detects compromised packages in lockfiles and system-level IOCs from attacks like…
 maweil/bidi_char_detector
Checks your files for existence of Unicode BIDI characters which can be misused for supply chain attacks. See CVE-2021-42574
 pierdipi/unicode-control-characters-action
A GitHub Action to find Unicode control characters using the Red Hat diagnostic tool https://access.redhat.com/security/vulnerabilities/RHSB-2021-007…
 calusdotai/anticipator
Anticipator is an open-source threat detection platform for multi-agent AI systems.
 k271266/cve-2021-42694
Static analysis tool to detect homoglyph substitution attacks in source code, scanning Python identifiers for visually similar Unicode characters to…
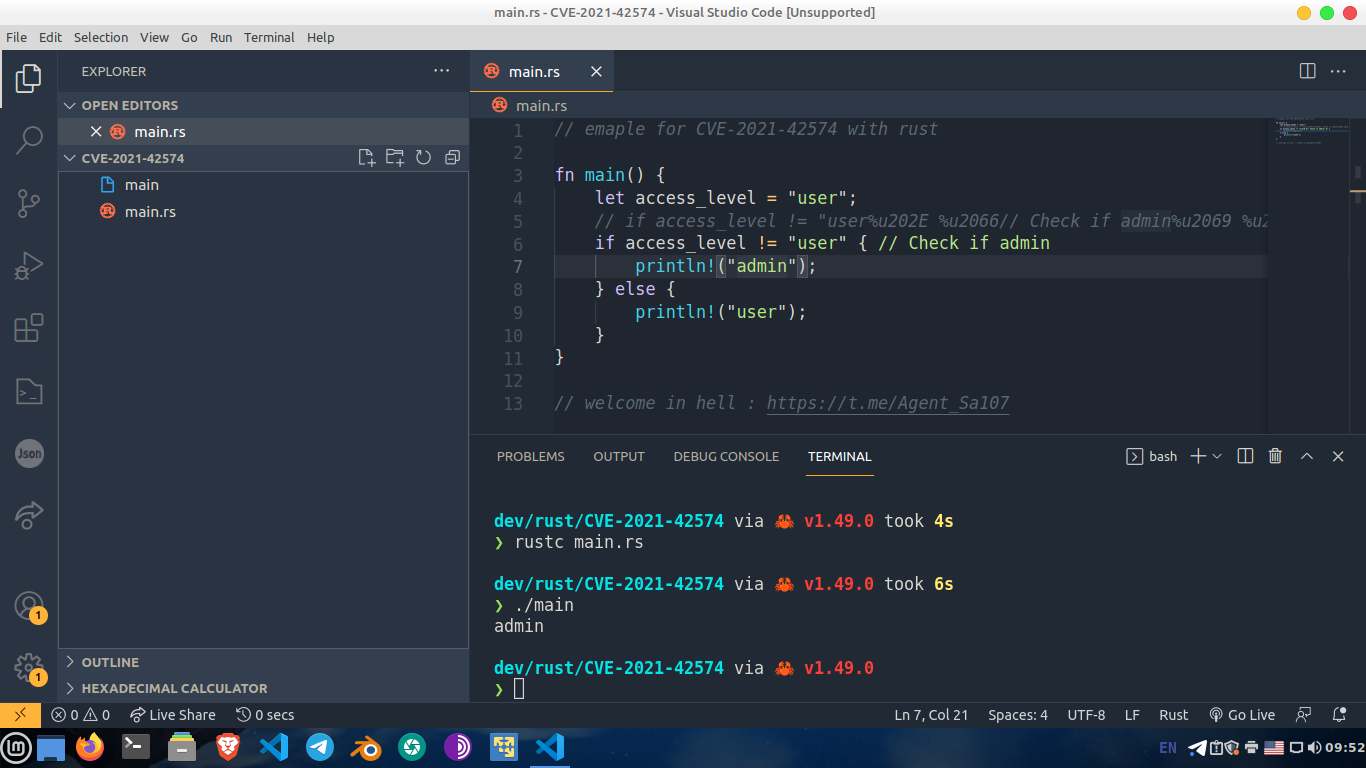 waseeld/cve-2021-42574
Demonstrates the Trojan Source vulnerability (CVE-2021-42574) by generating source code with invisible Unicode control characters that alter compiler…
 shoucheng3/nahsra__antisamy_cve-2022-29577_1-6-6-1
Java library for fast, configurable cleansing of untrusted HTML to prevent cross-site scripting (XSS) attacks. Uses policy-driven scanning to…
 mbadanoiu/cve-2021-46364
CVE-2021-46364: YAML Deserialization in Magnolia CMS