
CVE-2024-30956
 leocottret/cve-2024-30956
(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.
exploitationphishing-toolssocial-engineering+2
leocottret/cve-2024-30956(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.
 s1lkys/cve-2021-24884
If an authenticated user who is able to edit Wordpress PHP code in any kind, clicks a malicious link, PHP code can be edited through XSS in…
 d419h/iconjector
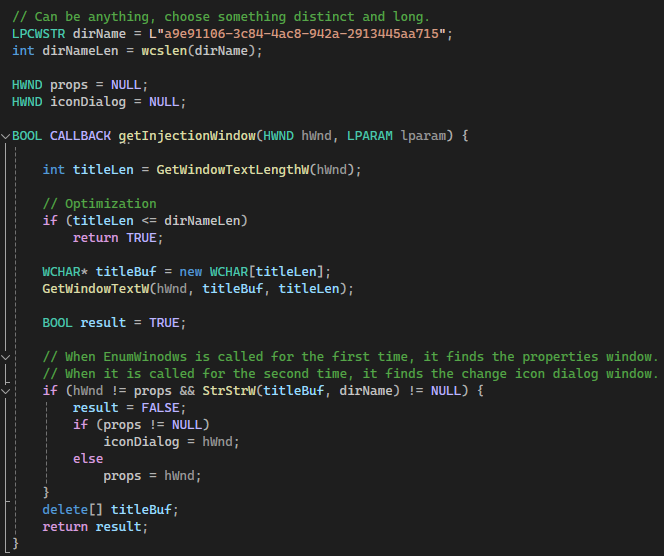
Inject DLLs into the explorer process using icons