
ImgBackdoor
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
command-and-controlexploitationpayload-development+3
tsuyoken/imgbackdoorHide your payload into .jpg file
 err0r-ica/whatspayloadrce
Whatsapp Automatic Payload Generator [CVE-2019-11932]
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 keepwannabe/whatsrce
This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)
 jasonjerry/whatsrce
This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)
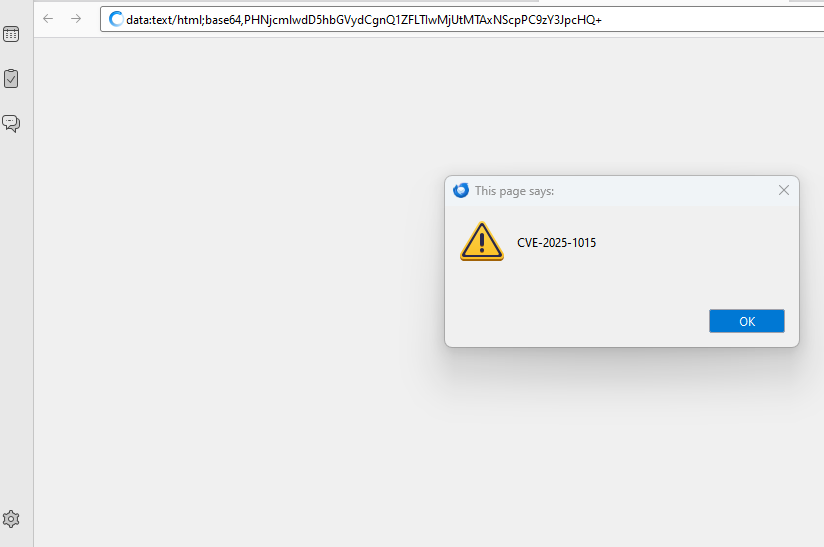 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
 r00t-3xp10it/backdoorppt
transform your payload.exe into one fake word doc (.ppt)
 thegeekht/loki.rat
Loki.Rat is a fork of the Ares RAT, it integrates new modules, like recording , lockscreen , and locate options. Loki.Rat is a Python Remote Access…
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
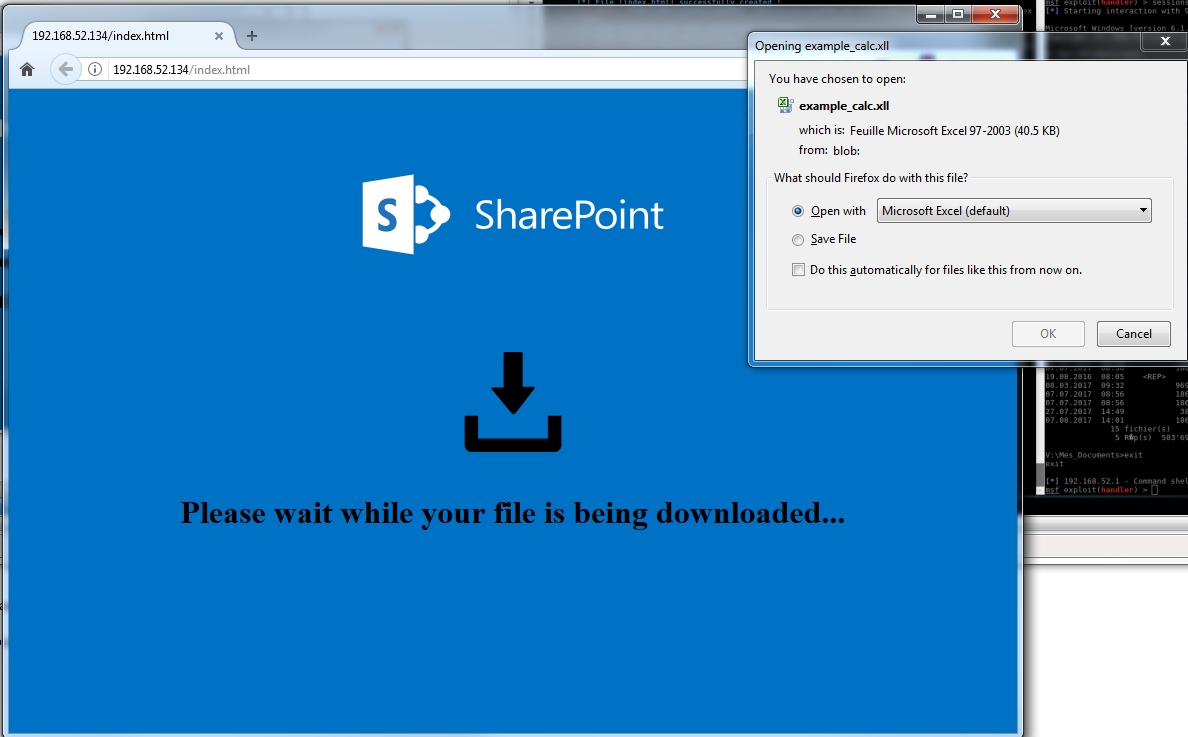 arno0x/embedinhtml
Embed and hide any file in an HTML file
 khr0x40sh/macroshop
Collection of scripts to aid in delivering payloads via Office Macros. Most are python. See http://khr0x40sh.wordpress.com for details.
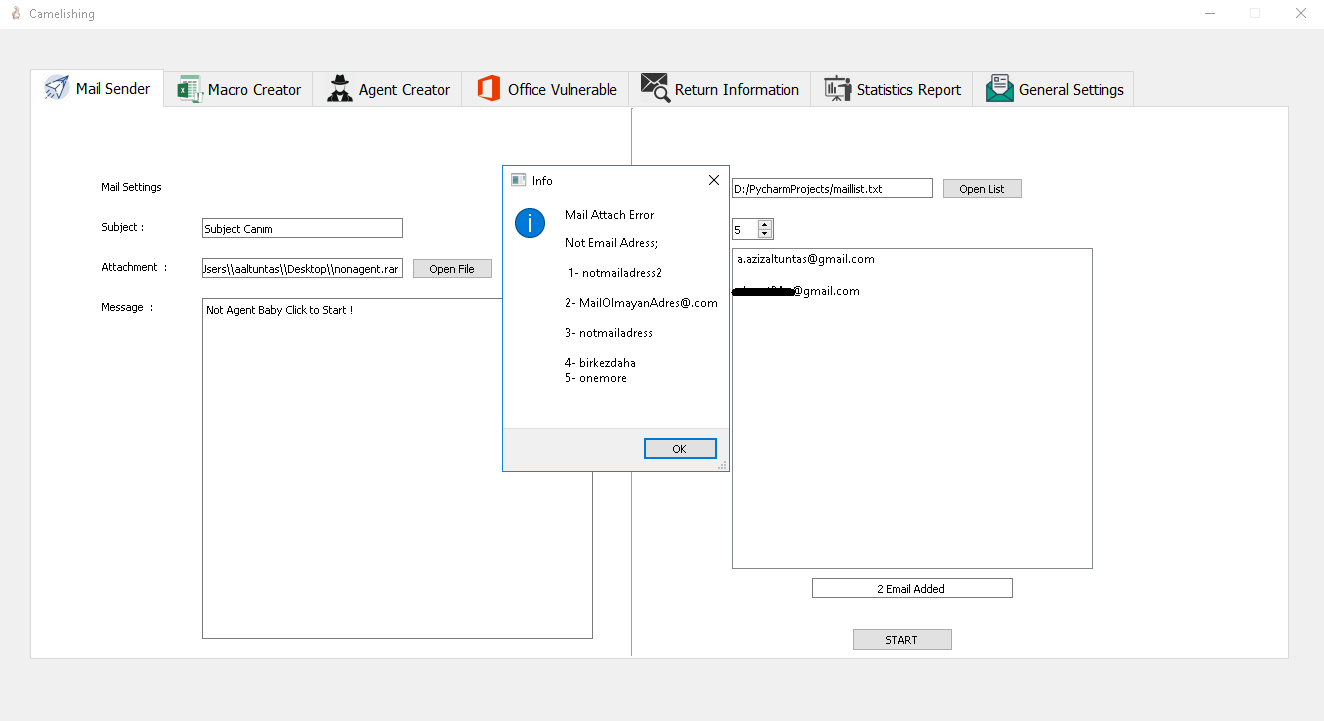 azizaltuntas/camelishing
Social Engineering Tool
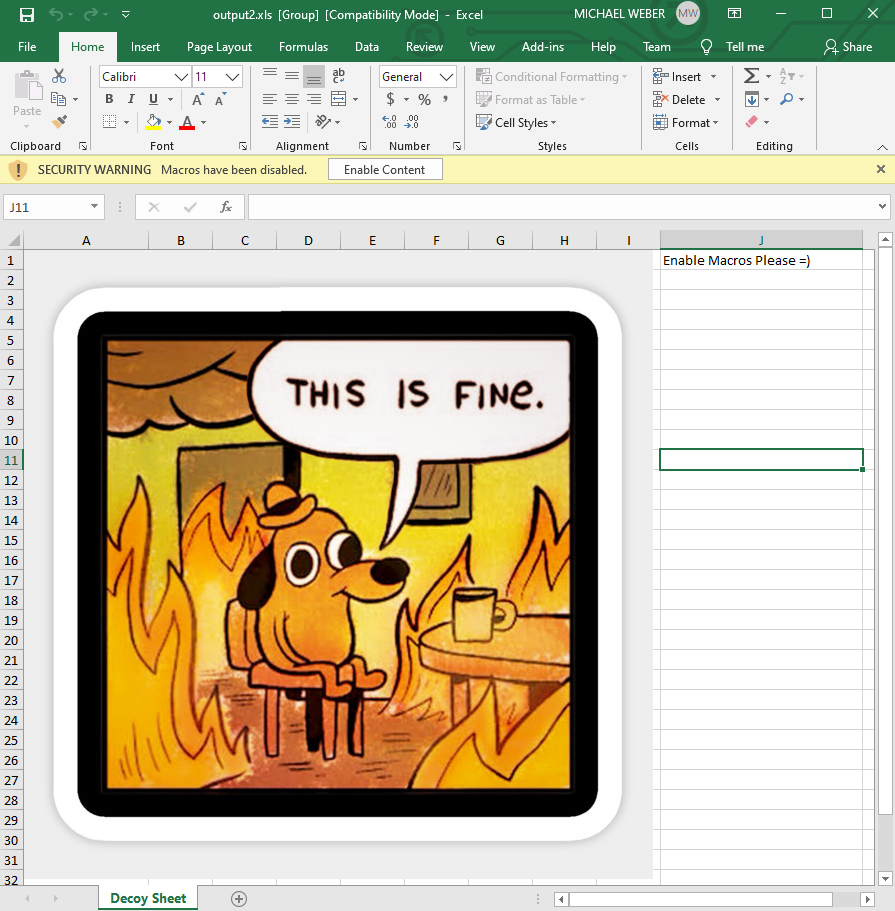 michaelweber/macrome
Excel Macro Document Reader/Writer for Red Teamers & Analysts
 d419h/iconjector
Inject DLLs into the explorer process using icons
 stmcyber/boobsnail
Generate obfuscated Excel 4.0 XLM macros for red team operations and blue team analysis, with support for multiple infection techniques, formula…