
RP_RecordClip_DLL_Hijack
 edubr2020/rp_recordclip_dll_hijack
Remote DLL hijack exploit for Real Player (CVE-2022-32291) using malicious DLLs from WebDAV/SMB shares to achieve code execution.
binary-exploitationexploitationsocial-engineering
2
edubr2020/rp_recordclip_dll_hijackRemote DLL hijack exploit for Real Player (CVE-2022-32291) using malicious DLLs from WebDAV/SMB shares to achieve code execution.
 sakurasamuraii/ez-irz
Exploit for CVE-2022-27226
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 paulpierre/informer
A Telegram Mass Surveillance Bot in Python
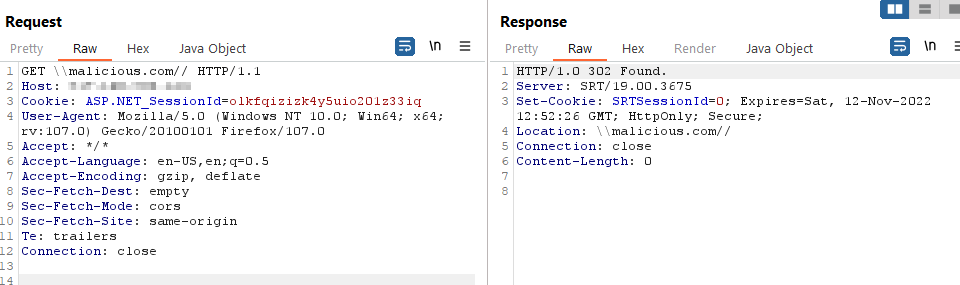 jbalanza/cve-2022-44215
Public disclosure of TitanFTP 19.X Open Redirection vulnerability
 shndnth/cve-2022-30190
Educational Proof-of-Concept for the CVE-2022-30190 (Follina) vulnerability.
 polling-repo-continua/cve-2022-25257
Proof-of-concept exploit for CVE-2022-25257: CSRF parameter injection in SAS Logon 9.4 enabling warning-message spoofing for phishing attacks.